







Multiple U.S. Army internet subdomains were defaced in a 404 hijacking campaign, CyberScoop has confirmed.
As of Monday morning, error pages on two U.S. Army websites – oil.army.mil and ai2c.army.mil – displayed defacement messages visible to users. The messages denigrated President Donald Trump and United States Ambassador to Türkiye Tom Barrack, called to “FREE KURDISTAN,” And included another line reading “Kurdish sr was here.”
One of the websites, oil.army.mil, belongs to the Army’s Open Innovation Lab, a test bed for software and cyber capabilities established in 2020. The other belongs to the Artificial Intelligence Integration Center, established in 2019 to integrate AI technologies into the Army and train personnel on emerging technologies.
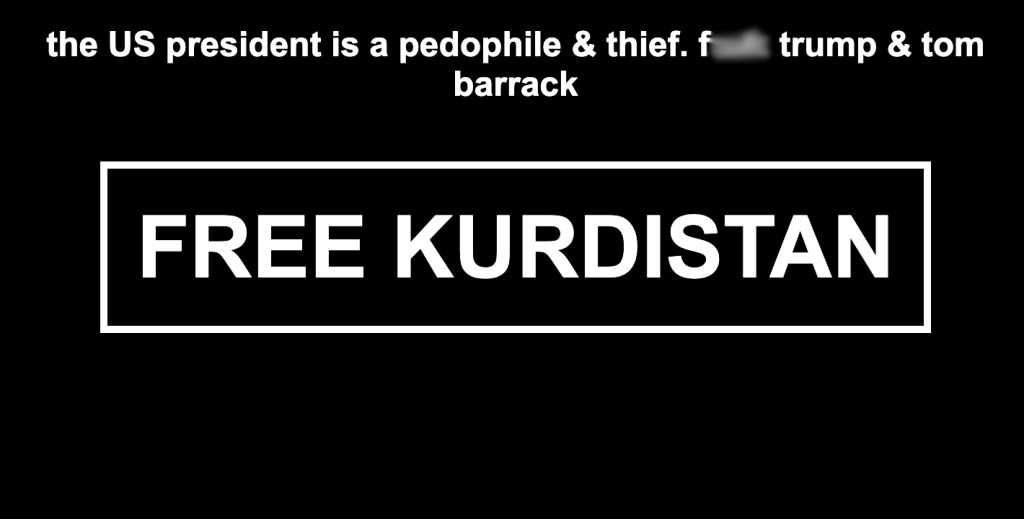
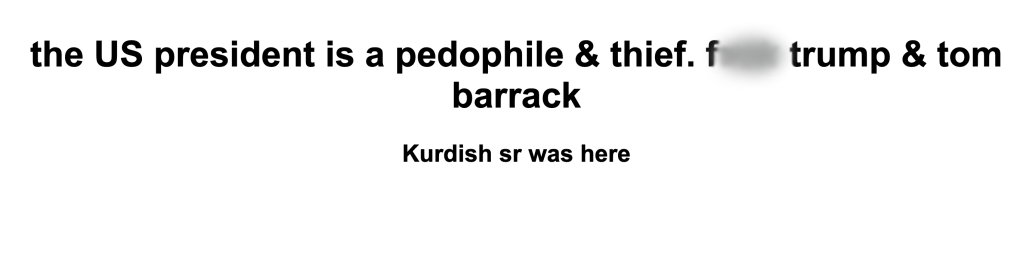
The defacements were initially discovered by independent cybersecurity researcher Ronald Lovelace, who notified U.S. Army officials and CyberScoop.
404 hijacking exploits a website’s error-handling system — often by compromising a plugin, content management system, or server configuration — to control what content gets displayed when a page isn’t found, rather than breaching the site’s core pages directly. This lets malicious users insert defacement messages, malicious redirects, or other unauthorized content that visitors see specifically on error pages, sometimes making the compromise harder to detect since the rest of the site appears untouched.
Lovelace said the affected sites run on WordPress and Microsoft cloud infrastructure. It’s not clear how long the subdomains have been compromised or whether other subdomains are affected.
“It raises the severity a decent amount because it shows it’s a bit deeper than just one single path” that’s being corrupted, Lovelace said.
However, while the defacement’s presence across multiple subdomains suggests the potential for “broad reach,” it doesn’t appear to affect all Army websites, with many still showing normal 404 error pages.
Also unclear at this time is how the hackers gained the ability to edit error pages for those websites, whether the breach originated internally if it was due to an internal or through a third party breach, and whether the intrusion extends beyond limited website defacement.
The websites were taken offline after CyberScoop reached out to the Army for comment. An Army spokesperson told CyberScoop that the pages were hosted on a legacy third-party platform that is not connected to the Army’s enterprise network and have since been removed.
The spokesperson said incident response by Army cyber investigators remains ongoing, and that it’s too early to say whether the third-party platform will be patched or discontinued.
“We are aware of unauthorized defacements on the error pages of oil.army.mil and ai2c.army.mil, which are hosted on a legacy, non-authoritative platform,” said Army spokesperson Maj. Sean Minton in a statement. “Technical teams took immediate action to mitigate the issue, and the affected pages have been secured. The Army takes all cyber incidents seriously and is actively investigating this matter to enforce our strict cyber defense and network security standards.”
It’s not clear who is behind the defacement beyond the references to Kurdistan— a geographic region spanning parts of Turkey, Iraq, Iran and Syria that is home to more than 30 million Kurdish people. The Kurdish separatist movement has fought for decades to establish an independent nation, and defacing government websites has long been a popular tactic among Kurdish hacktivists.
Trump and Barrack drew the ire of Kurdish proponents earlier this year for seeming to back a Syrian government military campaign to reestablish federal control over Kurdish-majority lands.
It’s not the first time that Army websites have been seemingly compromised by foreign hackers. In 2015, Army officials had to temporarily shut down major websites, including the Army main home page and the Department of Defense’s U.S. Strategic Command, after hackers from the Syrian Electronic Army defaced them.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。