



惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

F
Fortinet All Blogs
爱范儿
爱范儿
P
Proofpoint News Feed
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
T
Tailwind CSS Blog
J
Java Code Geeks
宝玉的分享
宝玉的分享
Jina AI
Jina AI
B
Blog
N
Netflix TechBlog - Medium
Recent Announcements
aimingoo的专栏
aimingoo的专栏
腾讯CDC
C
Check Point Blog
The Cloudflare Blog
阮一峰的网络日志
阮一峰的网络日志
博客园 - Franky
罗磊的独立博客
B
Blog RSS Feed
WordPress大学
WordPress大学
小众软件
小众软件
博客园 - 叶小钗
M
MIT News - Artificial intelligence
GbyAI
GbyAI

Blog

Imperva Customers Protected Against StyleSmuggler (CVE-2026-75650) in Adobe Commerce and Magento Open Source | Imperva SSL Integration Center: BYO CA & DigiCert TLM | Imperva OWASP LLM Top 10: What Comes Next for AI Security | Imperva Imperva API Security Token & Authentication Risk Report: Nearly 40% of APIs Face Multiple Authentication Risks | Imperva Imperva API Security Token & Authentication Risk Report: Nearly 40% of APIs Face Multiple Authentication Risks | Imperva www.imperva.com Imperva Customers Protected Against XSS2Shell (CVE-2026-64638) in WordPress Core | Imperva What SecureIQLab Cloud WAAP 5.0 means for your application security | Imperva Generative AI Security: Why AI Needs New Defenses | Imperva ShadowAI-Watch: Bringing AI Agent Activity Out of the Shadows | Imperva Imperva Customers Protected Against Novel HTTP Desync Attacks | Imperva Agentic AI Security: The Chatbot Era Is Over | Imperva MCP Server Security: Risks, Attacks & Controls | Imperva Google Australia Customers Now Benefit From Imperva Cloud-Native WAAP Security | Imperva Closing the Sovereignty Gap: Bringing Active API Protection to Self-Managed Environments | Imperva Imperva Customers Protected Against CVE-2026-16723: Critical FastJson 1.x Zero-Day RCE | Imperva Imperva Customers Protected Against "wp2shell" Pre-Authentication RCE in WordPress Core | Imperva Code Injection in Perforce Helix Core (CVE-2026-6902) | Imperva AI Bot Traffic: Which Bots to Allow or Block | Imperva API Security Tools: What Each One Protects | Imperva CVE-2025-54068 Laravel Livewire Credential Theft Campaign: 6,000+ Applications Compromised | Imperva On-Premises API Security on Kubernetes | Imperva AI Security Assistant for Faster Investigations | Imperva Best WAAP Solutions 2026: Enterprise Buyer Guide | Imperva Compromise OpenClaw with Prompt Injections in Message Objects The Clock Is Already Ticking: Why Post-Quantum Cryptography Can’t Wait Imperva Customers Protected Against CVE-2026-45247 in Mirasvit Full Page Cache Warmer for Magento Real-Time Webhook Notifications: No More Lost Security Alerts Imperva Customers Protected Against CVE-2026-9082 in Drupal Core Dify: When Your AI Platform Becomes the Attack Surface
Imperva Customers Protected Against CVE-2026-49975 (HTTP/...
Bar Menachem, Muly Levy · 2026-06-04 · via Blog

Imperva Customers Protected Against CVE-2026-49975 (HTTP/2 Bomb) DoS

TL;DR: CVE-2026-49975, dubbed the “HTTP/2 Bomb,” is a critical remote Denial-of-Service (DoS) vulnerability affecting default HTTP/2 configurations of major web servers including NGINX, Apache HTTPD, Microsoft IIS, Envoy, and Cloudflare Pingora. Discovered by security firm Calif using OpenAI’s Codex, the attack combines a unique HPACK compression bomb variant with a Slowloris-style flow-control window hold to cause immediate server outages and memory exhaustion. NGINX and Apache have rolled out fixes, while others remain exposed. Imperva customers are fully protected against exploitation attempts associated with this vulnerability.

About CVE-2026-49975

On June 3, 2026, California-based cybersecurity firm Calif disclosed a novel, highly disruptive remote denial-of-service attack chain tracked as CVE-2026-49975. The exploit targets structural similarities across default HTTP/2 protocol implementations, potentially threatening over 880,000 websites operating on default stack configurations.

Remarkably, the vulnerability chain was identified using OpenAI’s Codex. The AI model parsed multiple public codebases, recognizing that two distinct techniques, (each public or partially resolved for nearly a decade), could be seamlessly chained together to cripple enterprise web servers.

The exploit functions by combining two distinct phases:

  1. The Bookkeeping Compression Bomb (HPACK): Unlike traditional compression bombs that expand huge, stuffed data strings to trigger decoded-size limits, this variant relies on an optimized, nearly empty header payload. Instead of triggering maximum header restrictions, it forces the server to spend immense memory allocations purely on the internal per-entry bookkeeping and structural tables of the HTTP/2 HPACK scheme.
  2. The Flow-Control Slowloris Hold: Once the massive internal memory overhead is forced, the attack client advertises a zero-byte flow-control window. This effectively forces the server to hang, preventing it from sending a response while concurrently resetting the send timeouts. The connection stays active, trapping the allocated server memory indefinitely.

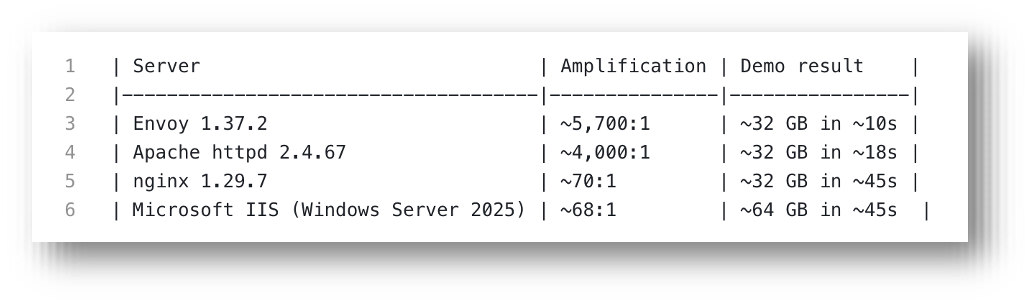
Because the attack vectors utilize standard, valid HTTP/2 frame properties, an unauthenticated attacker using a basic home computer over a 100 Mbps connection can exhaust up to 32GB of server memory within 20 seconds, knocking targeted infrastructure offline almost instantly.
CVE 2026 49975 blog

What We’ve Seen

Following the public disclosure, Imperva Threat Research has been actively tracking reconnaissance and proof-of-concept (PoC) validation activity corresponding to the newly released guidelines.

Because the exploit relies on native HTTP/2 frame manipulations, specifically targeting HPACK table modifications combined with restrictive WINDOW_UPDATE flow mechanics, initial traffic patterns show distinct automated probing behavior rather than standard application-layer payloads. Attackers are running specialized tools designed to map out whether target servers handle aggressive, dense bursts of small header blocks under restricted windows without terminating the connection. Given that HTTP/2 is almost universally adopted across modern web infrastructure, any unpatched asset running default configurations of the affected servers remains a viable target for these generic probes.

Mitigation and Protection

Organizations are advised to audit their web server footprints and apply vendor updates immediately:

  • NGINX: Upstream fixes were quietly addressed in version 1.29.8+ and supported branches in April.
  • Apache HTTPD: Fixes addressing the specific chaining behaviors have been integrated into late-May releases.
  • Microsoft IIS, Envoy, and Cloudflare Pingora: Default configurations remain exposed at the time of writing; organizations using these platforms should closely monitor infrastructure memory thresholds or consider temporarily disabling HTTP/2 on unpatched public endpoints if downstream mitigations are not in place.

Imperva Protection

Imperva customers with Cloud WAF deployments are protected against exploitation attempts associated with CVE-2026-49975. Cloud WAF automatically inspects and manages anomalous stream and frame structures at the edge, mitigating malicious HPACK anomalies before they reach backend services.

For organizations utilizing Imperva WAF-GW protecting environments where HTTP/2 is enabled, administrators should take immediate action to verify that HTTP/2 Header Restrictions are actively applied and enforced within their security policies. Ensuring these granular protocol constraints are enabled provides a critical layer of defense, blocking the dense, high-frequency header bookkeeping manipulation characteristic of the HTTP/2 Bomb exploit before it can consume backend server resources. For detailed configuration steps, please refer to the following KB article.

Bottom Line

CVE-2026-49975 represents a significant shift in threat discovery, showing how agentic AI capabilities can systematically bridge known, siloed software behaviors into destructive new exploit chains. Because the “HTTP/2 Bomb” requires minimal bandwidth to trigger complete memory exhaustion across major web servers in their default states, patching and perimeter mitigation are urgent priorities.

Imperva customers remain protected. Imperva Cloud WAF and WAF Gateway inspect and drop malicious stream and frame structures, ensuring that anomalous HPACK table definitions and malicious flow-control holds are neutralized at the edge before they can induce memory stress on backend enterprise systems.

Try Imperva for Free

Protect your business for 30 days on Imperva.

Start Now