



惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

F
Fortinet All Blogs
爱范儿
爱范儿
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
B
Blog
WordPress大学
WordPress大学
Jina AI
Jina AI
GbyAI
GbyAI
aimingoo的专栏
aimingoo的专栏
N
Netflix TechBlog - Medium
腾讯CDC
Cyber Security Advisories - MS-ISAC
阮一峰的网络日志
阮一峰的网络日志
The GitHub Blog
The GitHub Blog
V
Visual Studio Blog
Google DeepMind News
月光博客
月光博客
博客园 - Franky
Y
Y Combinator Blog
MyScale Blog
MyScale Blog
大猫的无限游戏
大猫的无限游戏
Martin Fowler
Martin Fowler
雷峰网
雷峰网
小众软件
小众软件
H
Hackread – Cybersecurity News, Data Breaches, AI and More

Security Affairs

Copy Fail: New Linux bug enables Root via page‑cache corruption Agent’s claims on WhatsApp access spark security concerns Meta accused of violating DSA by failing to safeguard minors Large-scale Roblox hacking operation shut down by Ukrainian authorities CVE-2026-42208: LiteLLM bug exploited 36 hours after its disclosure Internet censorship index reveals Russia’s lead and widespread content blocking All supported cPanel versions hit by critical auth bug, now patched U.S. CISA adds Microsoft Windows Shell and ConnectWise ScreenConnect flaws to its Known Exploited Vulnerabilities catalog ShinyHunters exploit Anodot incident to target Vimeo CVE-2026-3854 GitHub flaw enables remote code execution Signal Phishing Campaign Targets German Officials in Suspected Russian Operation Microsoft fixes Entra ID flaw enabling privilege escalation New Android spyware Morpheus linked to Italian surveillance firm NCSC launches SilentGlass, a plug-in device to secure HDMI and DisplayPort links Medtronic discloses security incident after ShinyHunters claimed theft of 9M+ records Chinese spy posed as researcher in spear-phishing campaign targeting NASA to steal defense software LINKEDIN BROWSERGATE Firefox bug CVE-2026-6770 enabled cross-site tracking and Tor fingerprinting Fast16: Pre-Stuxnet malware that targeted precision engineering software Italy moves to extradite Chinese national to the U.S. over hacking charges U.S. utility giant Itron discloses a security breach Critical bug in CrowdStrike LogScale let attackers access files GopherWhisper: new China-linked APT targets Mongolia with Go-based malware SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 94 Trigona ransomware adopts custom tool to steal data and evade detection Security Affairs newsletter Round 574 by Pierluigi Paganini – INTERNATIONAL EDITION U.S. CISA adds SimpleHelp, Samsung, and D-Link flaws to its Known Exploited Vulnerabilities catalog Over 400,000 sites at risk as hackers exploit Breeze Cache plugin flaw (CVE-2026-3844) CISA reports persistent FIRESTARTER backdoor on Cisco ASA device in federal network 12-year-old Pack2TheRoot bug lets Linux users gain root privileges
Bitcoin Depot hack leads to $3.6M Bitcoin theft via stole...
2026-04-10 · via Security Affairs

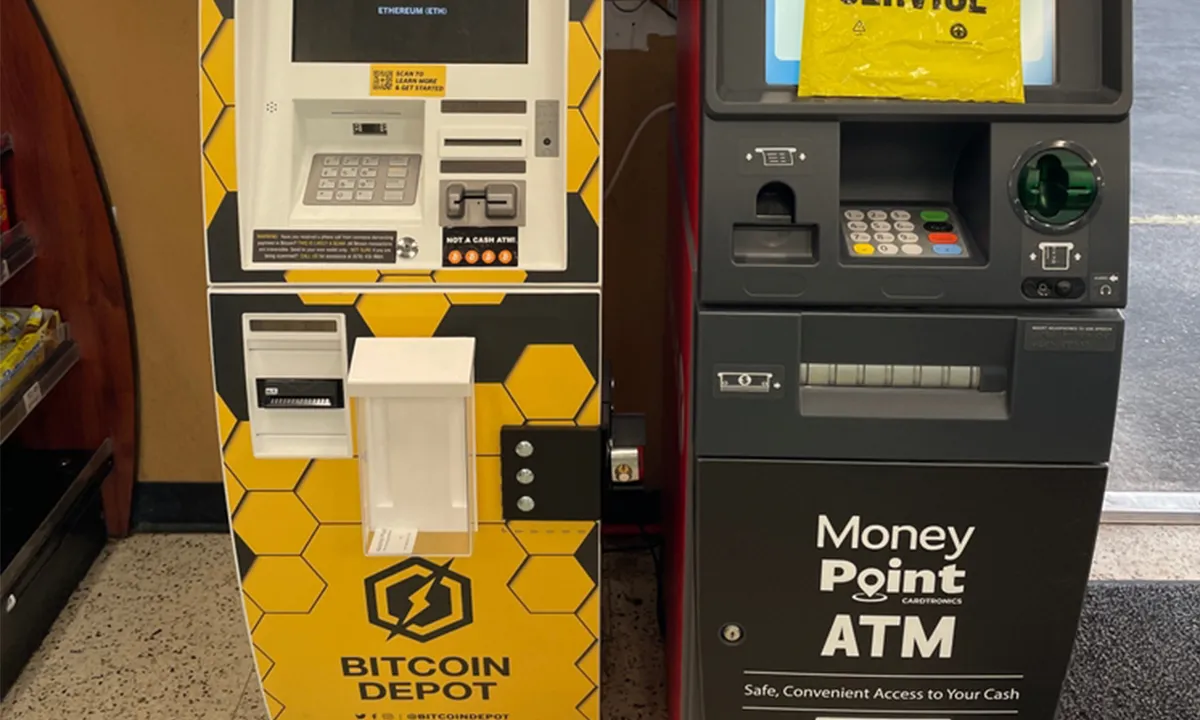
Hackers breached Bitcoin Depot, stole credentials, and took about 50 BTC worth $3.6M from its wallets after a March 23 intrusion.

Hackers breached the largest US Bitcoin ATM operator, Bitcoin Depot, on March 23, stole login credentials, and drained about 50.9 BTC worth $3.6M from company wallets.

Bitcoin Depot told the SEC that a hacker accessed its systems and stole credentials linked to its digital asset settlement accounts, gaining control and enabling unauthorized activity.

“On March 23, 2026, Bitcoin Depot Inc. (the “Company”) discovered that an unauthorized party gained access to certain of its information technology systems. Upon detection, the Company promptly activated its incident response protocols, engaged external cybersecurity experts, and notified law enforcement. Based on the Company’s investigation to date, the unauthorized actor gained access to certain systems and obtained control of credentials associated with the Company’s digital asset settlement accounts.” reads the FORM 8-K filed with the SEC. “As a result, the unauthorized actor transferred approximately 50.903 Bitcoin from Company-controlled wallets, valued at approximately $3.665 million as of the date of this report, without authorization. The Company further believes that the incident was contained to the Company’s corporate environment and did not affect the Company’s customer platforms, divisions, systems, data or environments.”

The company continues to investigate the security breach with the help of external cybersecurity experts and works to strengthen its systems to prevent future attacks. It has not found evidence of stolen customer personal data, but the investigation is still ongoing.

The incident has not disrupted operations, but the company now considers it material due to possible legal, reputational, and response costs. It estimates a $3.665 million loss from unauthorized Bitcoin transfers, though the final impact may change. Insurance may cover part of the damage, but recovery is not guaranteed.

“The Company has recorded a preliminary estimate of loss of approximately $3.665 million, representing the fair value of the Bitcoin transferred without authorization as of the date of the incident. The ultimate impact may differ from this estimate as the investigation continues.” continues the FORM 8-K. “The Company maintains insurance coverage that may cover certain losses associated with cybersecurity incidents, but there can be no assurance that such coverage will be sufficient to recover any or all losses incurred as a result of this incident.”

This isn’t the first incident suffered by the company. In July 2025, Bitcoin Depot notified over 26,000 people about a data breach that happened in 2024. Attackers accessed company systems and stole files containing personal data.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Bitcoin Depot)