





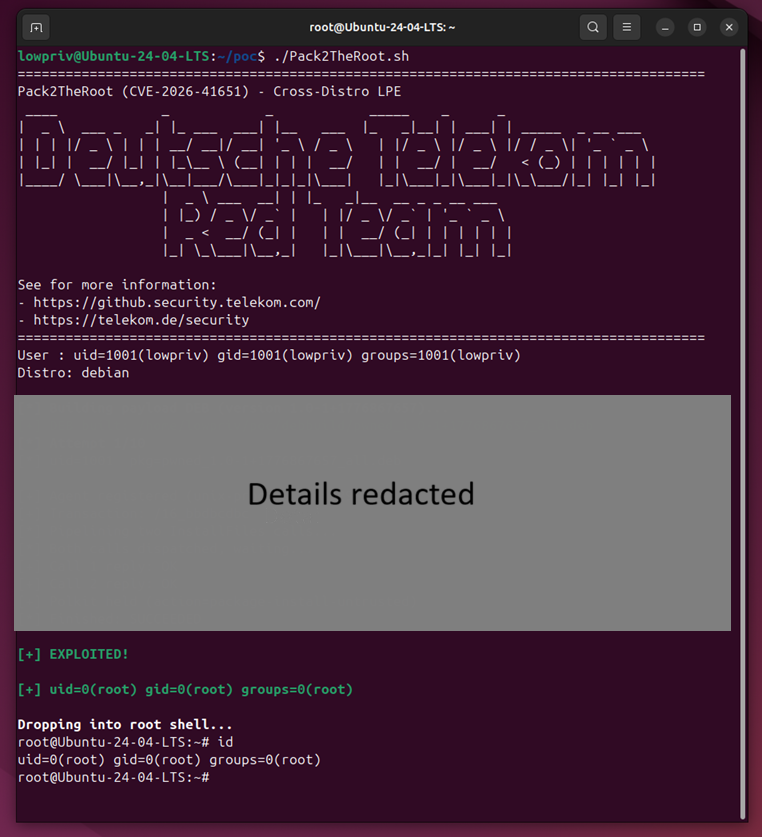
The Pack2TheRoot flaw, tracked as CVE-2026-41651, lets unprivileged users install or remove system packages without authorization, potentially gaining full root access.
The vulnerability is rated high severity, CVSS score of 8.8, and has existed for nearly 12 years.
Discovered by Deutsche Telekom’s Red Team, it stems from PackageKit allowing commands like “pkcon install” to run without a password on some systems. Researchers used AI (Claude Opus) to explore the issue, confirmed it manually, and responsibly disclosed it to maintainers, who validated the flaw.
“Today we publicly disclose a high-severity vulnerability (CVSS 3.1: 8.8) – in coordination with distro maintainers – that affects multiple Linux distributions in their default installations. The Pack2TheRoot vulnerability can be exploited by any local unprivileged user to obtain root access on a vulnerable system.” reads the advisory published by Deutsche Telekom. “The vulnerability lies in the PackageKit daemon, a cross-distro package management abstraction layer.
Details of the Pack2TheRoot flaw were disclosed alongside a fix in PackageKit 1.3.5, though exploit code was withheld to allow patching. Deutsche Telekom researchers found that PackageKit could run commands like “pkcon install” without authentication in some cases on Fedora, enabling package installation. The researchers used the Claude Opus AI tool to explore this behavior further and identified the vulnerability as CVE-2026-41651.
All PackageKit versions from 1.0.2 to 1.3.4 are vulnerable, affecting many Linux distributions for over 12 years. Tested systems include Ubuntu, Debian, Fedora, and Rocky Linux, and others using PackageKit may also be at risk, including servers with Cockpit. The issue is fixed in version 1.3.5, with patches released on April 22, 2026.
Technical details of the vulnerability are not yet disclosed and will be shared later. Researchers have developed a reliable proof-of-concept that allows an unprivileged local user to gain root code execution on default Linux systems. However, the PoC code has not been released publicly to prevent abuse while patches are being deployed.

To check if you’re vulnerable, verify if PackageKit is installed using dpkg or rpm, as it may run on demand via D-Bus. Then check if the service is active with systemctl or monitoring tools like pkmon/pkgcli. If active and unpatched, your system may be at risk. Although fixed in version 1.3.5, many distributions have released patched versions separately, so updating via your distro is essential.
You can use the following commands to check whether a vulnerable version of PackageKit is installed on your system:
dpkg -l | grep -i packagekitrpm -qa | grep -i packagekit
To verify if the PackageKit daemon is active, run systemctl status packagekit or pkmon. If the service is loaded or running, your system may be at risk if it has not been patched.
Researchers released Indicators of compromise (IOCs) for this flaw.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Pack2TheRoot)
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。