



The enterprise technology landscape is undergoing a radical transformation, and at its core is the modern data center. Virtual machines (VMs) and agile Kubernetes-based environments have long served as the foundation of this infrastructure. However, as companies deploy artificial intelligence in daily business operations, they must aggressively expand their AI ecosystems to handle highly resource-intensive AI workloads. Ultimately, this shift is redefining what is possible in IT infrastructure and driving unprecedented growth across the enterprise.
This rapid expansion comes with a dark side: the same frontier AI that is accelerating business operations is being weaponized by adversaries. Attackers are increasingly deploying these models to intelligently find vulnerabilities, generate exploit code, correlate across targets, and execute chained attack paths at machine speed. The impact is staggering. As documented in recent M-Trends reporting, AI-discovered vulnerabilities have collapsed the median time to exploit (TTE) from 771 days in 2018 to sub-hourly windows today.
This explosive growth creates a sprawling attack surface that is notoriously difficult to secure consistently and efficiently. Furthermore, when facing threats that move at sub-hourly speeds, defenders can no longer rely on traditional playbooks. They must operate continuously, cost-effectively, and at that exact same machine speed. To effectively defend this modern ecosystem, organizations need robust lateral security that scales with the immense demands of high-performance workloads while enforcing consistent protection across highly distributed VM and Kubernetes clusters.
Purpose-built to address these challenges for the VMware Cloud Foundation (VCF) private cloud, VMware vDefend offers a multi-layered defense approach to protect east-west traffic against ransomware and advanced threats. vDefend includes an Intrusion Detection and Prevention System (IDPS), which inspects all traffic entering or leaving the network, detecting and preventing known threats from gaining access to the network, critical systems, and data.
Let’s look at how vDefend IDPS addresses these critical needs.
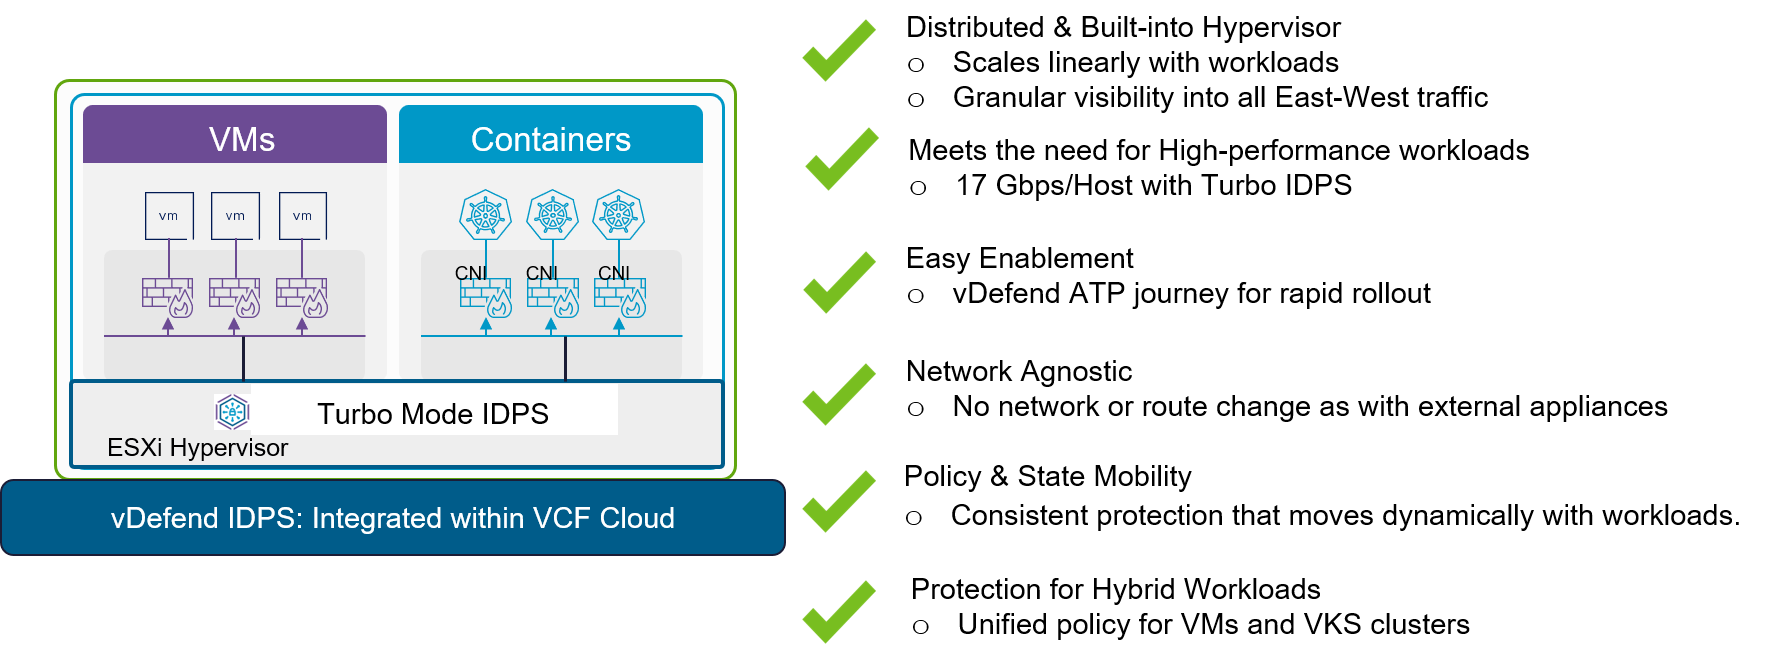
To protect modern, distributed workloads without sacrificing speed, security must be built-in, not bolted on. By leveraging a hypervisor-native architecture, vDefend distributed IDPS provides seamless, plug-and-play zero-trust lateral protection. Furthermore, because policies are distributed and automated, protection scales effortlessly, applying instantly as workloads are created or migrated across your environment.
vDefend introduces High-Performance Lateral Threat Prevention via an optimized Turbo IDPS architecture. By boosting throughput from 9 Gbps to 17 Gbps per host (17 Tbps per VCF instance), an 88% increase, Turbo IDPS ensures that every internal flow is inspected for malicious activity at line-rate speeds. Now you can seamlessly protect your East-West traffic while meeting the immense demands of high-performance AI workloads.
In a Zero Trust architecture, deep packet inspection is vital, but applying it blindly to all traffic is computationally inefficient. While vDefend distributed IDPS offers a robust 17 Gbps of throughput per host, securing high-capacity workloads optimally requires intelligent bypassing.
The “EXEMPT” rule action enables this strategy by allowing security operators to easily identify specific trusted flows (data backups, database replications, etc.) and exclude them from the IDPS scanning engine.
Key benefits for vDefend customers:
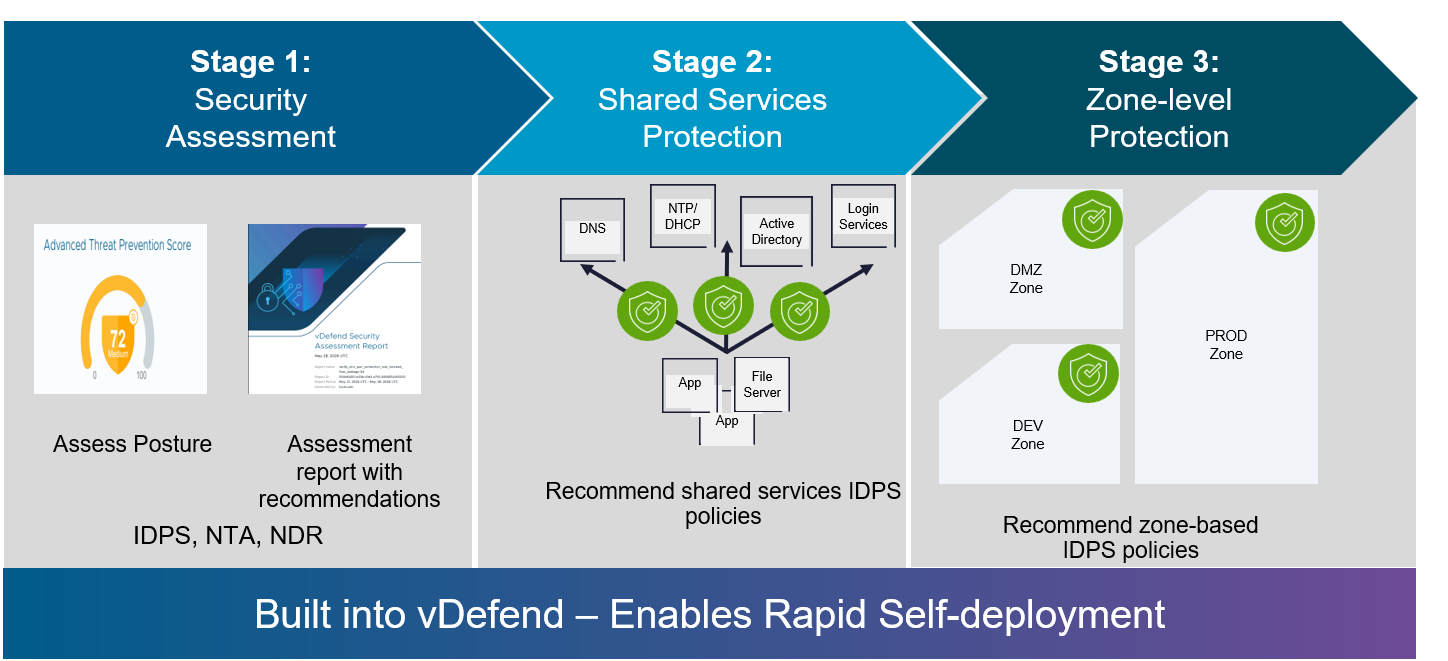
vDefend ATP Journey (ATP 1-2-3) streamlines comprehensive IDPS deployment by transforming the complex path to Zero Trust into an intuitive, data-driven Security Journey. This methodology assesses an organization’s current security posture. It provides a structured workflow that smoothly guides users through sequential segmentation stages—from securing critical infrastructure services to fully locking down inter-environment traffic.
Key User Benefits:
Frontier AI models have armed attackers with the ability to find previously unknown zero-day vulnerabilities across software and at machine speed. Attacks can now propagate in hours. Given the speed of AI-driven threats, it’s imperative to have a solution that can proactively address them and effectively maintain a defensive posture.
vDefend IDPS acts as a shield, proactively blocking potential exploits for newly detected vulnerabilities until official patches can be applied. It uses frequently updated signatures to protect against the latest global threats and supports custom signatures—imported or developed in-house—allowing customers to quickly and virtually patch their applications.
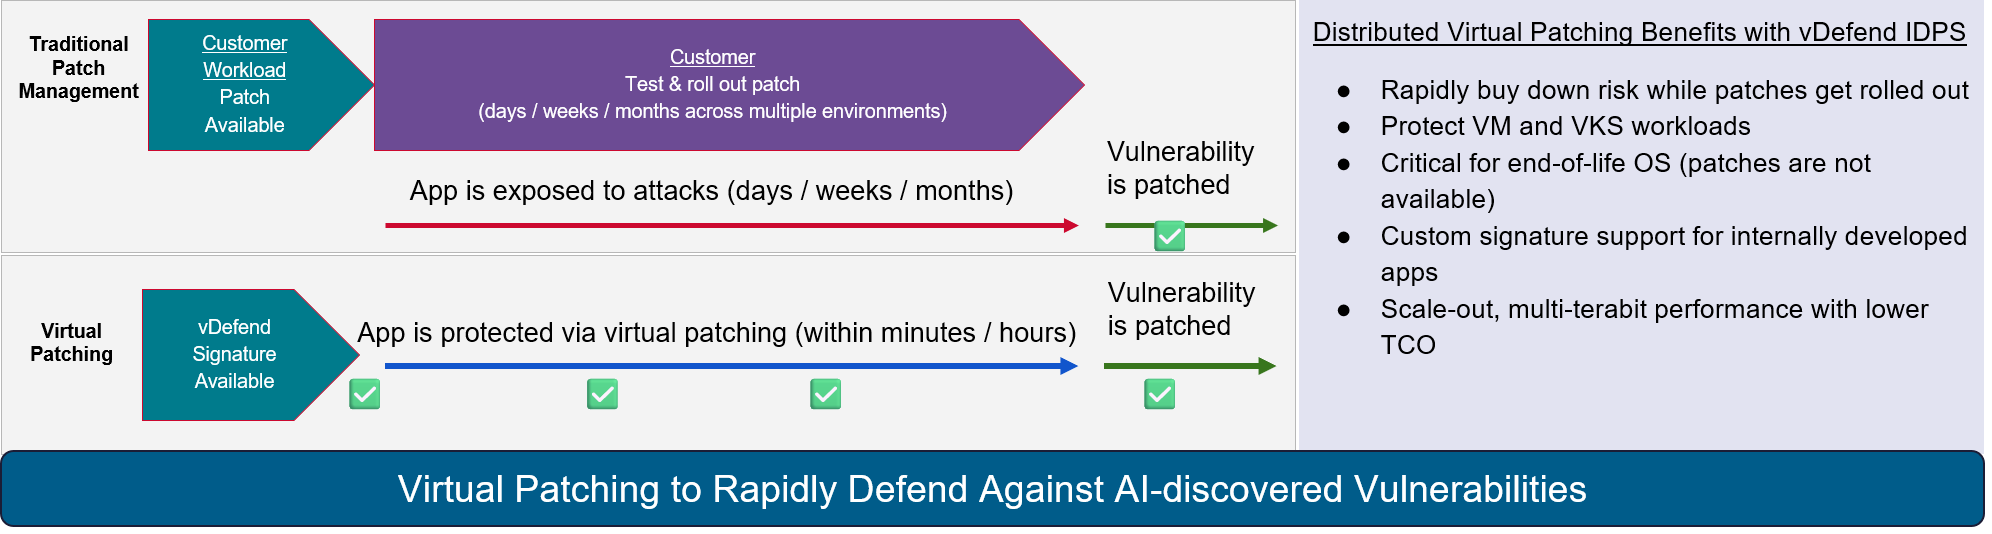
This video, vDefend Virtual Patching, demonstrates how distributed IDPS can be applied to protect against these threats.
Learn more about vDefend Virtual Patching here.
Deploying vDefend IDPS in a detect-only mode transforms network monitoring into a high-visibility threat intelligence tool. By generating high-fidelity alerts mapped directly to the MITRE ATT&CK framework, the system illuminates exactly how an attacker breaches the network and moves laterally. This detailed mapping of the attack kill chain provides SOC teams with the essential, deep context required to quickly investigate, understand, and respond to complex security events before they escalate.
vDefend IDPS provides:
Learn more about the vDefend ATP solution here.
Achieving compliance with stringent frameworks doesn’t have to be a resource-intensive challenge. vDefend IDPS transforms complex regulatory mandates into a streamlined, automated process.
Core Benefits
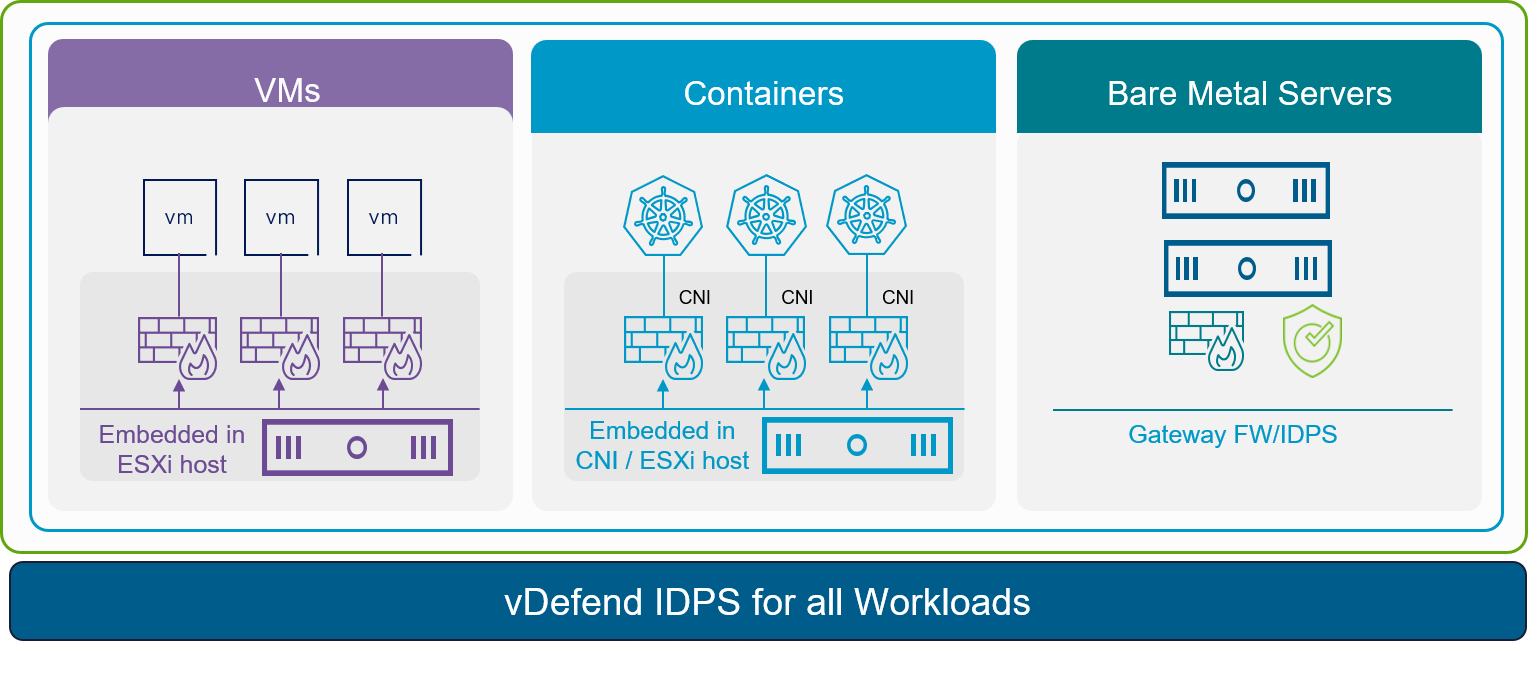
In addition to protecting VM workloads, vDefend IDPS extends deep packet inspection directly to container nodes and bare-metal servers. Analyzing this highly dynamic container traffic provides granular visibility into lateral East-West traffic. This allows organizations to scale cloud-native architectures without compromising their underlying security posture.
Key benefits for vDefend customers:
vDefend distributed IDPS protects a diverse range of modern workloads—from VMs and containers. By leveraging Advanced Threat prevention on the gateway firewall, these detection capabilities extend directly to bare-metal servers. Additionally, full support for air-gapped environments ensures your infrastructure meets all regulatory compliance requirements.
The rapid expansion of AI workloads is radically reshaping the modern enterprise data center. Simultaneously, adversaries are weaponizing frontier AI models to launch high-speed, sophisticated cyberattacks. To navigate this, organizations must make vDefend IDPS an integral, foundational part of their security journey. By embedding security into the hypervisor, vDefend seamlessly delivers true zero-trust protection. The platform addresses a vast breadth of critical use cases, from virtual patching to securing modern containers. Furthermore, with recent high-performance architectural enhancements such as Turbo IDPS, vDefend powers advanced threat prevention without introducing network bottlenecks. Ultimately, vDefend IDPS ensures your infrastructure remains agile, scalable, and decisively protected against AI-driven threats.
Learn more:
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。