






In the past, data center security mostly relied on perimeter protection—”building walls” to keep bad actors out. Today, safeguarding the data center’s “east-west” or lateral traffic traversing within applications and data is just as critical. Threat actors are leveraging “Frontier AI” security models to automate and accelerate attacks against private cloud workloads.
To help enterprises achieve best-of-breed protection with significantly reduced complexity, we are excited to announce new VMware vDefend blueprints to speed up lateral security roll-out across VCF private cloud workloads and help organizations quickly buy down risk. The “Lateral Security for VMware Cloud Foundation with VMware vDefend” VVS is now integrated into core VCF 9.1 design documentation as “Lateral Security with vDefend” Blueprints. The blueprints for Securing the Management and Workload domains are now included with the core VCF 9.1 design documentation.
Here is a closer look at what this change means, what these blueprints cover, and how you can start using them to modernize your private cloud security and protect against both conventional and AI attacks.
A blueprint is a prescriptive, end-to-end architecture designed to accelerate your time-to-value when building and operating a VMware Cloud Foundation (VCF) private cloud platform. It provides predefined deployment models that conform to specific profiles. A blueprint also includes a set of planning, implementation, and design elements (requirements and recommendations) tailored to the selected deployment model. You can streamline your VCF private cloud provisioning by using them as a template, swapping out models to match your unique infrastructure layout.
The Lateral Security with vDefend Blueprints describes the architectural components and design selections required to provide unified, enterprise-grade security services for a VMware Cloud Foundation platform using VMware vDefend security solutions.
The design consists of three individual blueprints that cover pre-defined models to address network and application security corners of your platform:
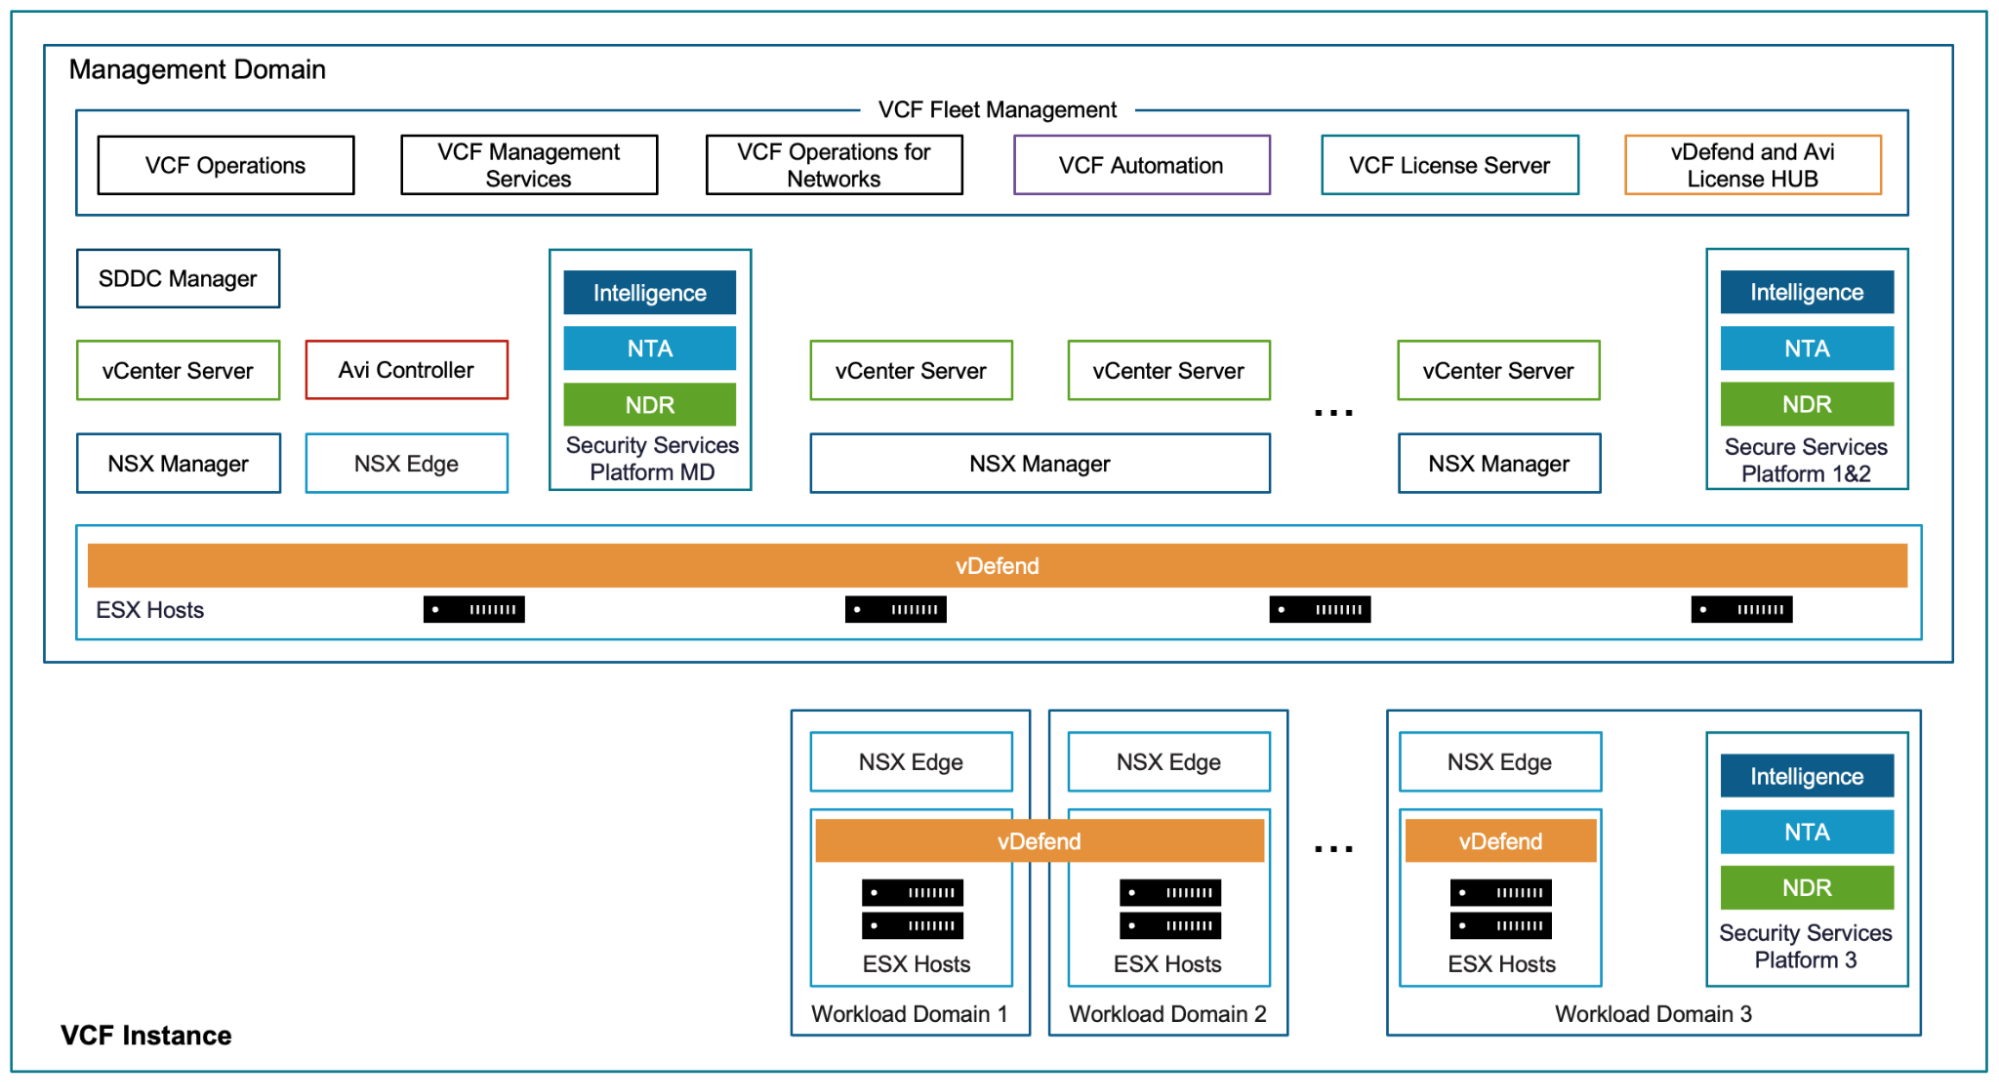
Ready to eliminate blind spots and lock down your east-west traffic? Check out the new Lateral Security with vDefend design blueprints today and take your private cloud security to the next level.
By integrating VMware Validated Solutions into the core VCF 9.1 design documents, Broadcom aims to streamline documentation and provide straightforward guidance for building a robust, secure private cloud.
The Lateral Security with vDefend Blueprints equips you with verified configurations and guidelines to streamline setup, reduce guesswork, and accelerate the path to a cyber-resilient private cloud. Whether you’re new to security or an experienced professional, these blueprints make it easier than ever to transform your security plans into a practical security strategy.
Deployment and Design Resources:
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。