




惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

WordPress大学
WordPress大学
大猫的无限游戏
大猫的无限游戏
酷 壳 – CoolShell
酷 壳 – CoolShell
博客园 - 叶小钗
月光博客
月光博客
Last Week in AI
Last Week in AI
让小产品的独立变现更简单 - ezindie.com
人人都是产品经理
人人都是产品经理
阮一峰的网络日志
阮一峰的网络日志
罗磊的独立博客
IT之家
IT之家
美团技术团队
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
Hugging Face - Blog
Hugging Face - Blog
博客园_首页
S
SegmentFault 最新的问题
宝玉的分享
宝玉的分享
博客园 - Franky
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
Jina AI
Jina AI
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
The Cloudflare Blog
博客园 - 司徒正美
爱范儿
爱范儿

Palo Alto Networks Blog

Palo Alto Networks Named a Leader in the 2026 Gartner® Magic Quadrant™ for Hybrid Mesh Firewall Secure AI Coding: Governing every agent, artifact, and identity Building Securely From Day One: Palo Alto Networks Partners with the Zendesk Startup Program Making the Most of the Cloud Marketplace Opportunity Celebrating excellence: Palo Alto Networks announces the 2026 North America Partner of the Year Awards Unit 42 Defends Organizations Against Next-Gen Frontier AI Risks with Anthropic’s Mythos 5 Putting OpenAI Cyber Models to Work for Defenders Palo Alto Networks Recognized as the Only Vendor to be Named a 4X Leader in SASE and SSE Gartner Magic Quadrant Reports Strengthening Security of AI Coding: Prisma AIRS API Integration with OpenAI Codex Bridging the Gap: An Unprecedented Approach to Browser and Endpoint Security Prisma AIRS - Unified Data Protection for Claude Redefining Network Security for the Frontier AI Era Introducing Unit 42 Threat Intelligence: Know What Matters, Understand the Adversary, and Act Faster Palo Alto Networks Achieves Global CBPR and PRP Certifications Announcing the General Availability of Prisma AIRS AI Gateway Palo Alto Networks and AT&T - Delivering Quantum-Resilient SASE Fabric What It Takes to Secure Claude Cowork Across the AI Enterprise It Might Feel Like We’ve Been Here Before, But We Haven’t A Defining Moment in Identity Security New Executive Order Accelerates Post-Quantum Readiness Amid the Cryptographic Reset Built to Last: What Stonehenge Teaches us About IT Architecture & Cyber Resilience Expanding Our Footprint: Local Cloud Availability for Prisma AIRS in Japan The Invisible CEO of Crisis: Breaking the Cycle of CISO Burnout Securing the Agentic AI Frontier: Palo Alto Networks and Databricks Deliver a New Standard for AI Security Securing Canada’s Digital Future: Why PBMM Matters Beyond Government Beyond Human Oversight: Adapting to the Frontier AI Era Shifting from Data Hoarding to Active Defense: Navigating the New Era of OMB M-26-14 European Digital Sovereignty Starts With Trust How AI and Evasion Demand a Radical Shift in Network Threat Prevention Reinventing Security for the Agentic NVIDIA AI Factory
FedRAMP Moderate Authorization for Palo Alto Networks’ Qu...
Matt Marsden · 2026-09-15 · via Palo Alto Networks Blog

Palo Alto Networks has achieved FedRAMP Moderate authorization for Quantum-Safe Security (QSS), a turnkey Automated Cryptography Discovery and Inventory (ACDI) solution. With this certification, federal agencies can deploy QSS immediately.  The authorization demonstrates that QSS meets stringent security requirements, enabling federal agencies to adopt cutting-edge technologies while safeguarding sensitive, unclassified data. QSS removes operational roadblocks by making cryptographic discovery, risk assessment and transition both continuous and actionable.
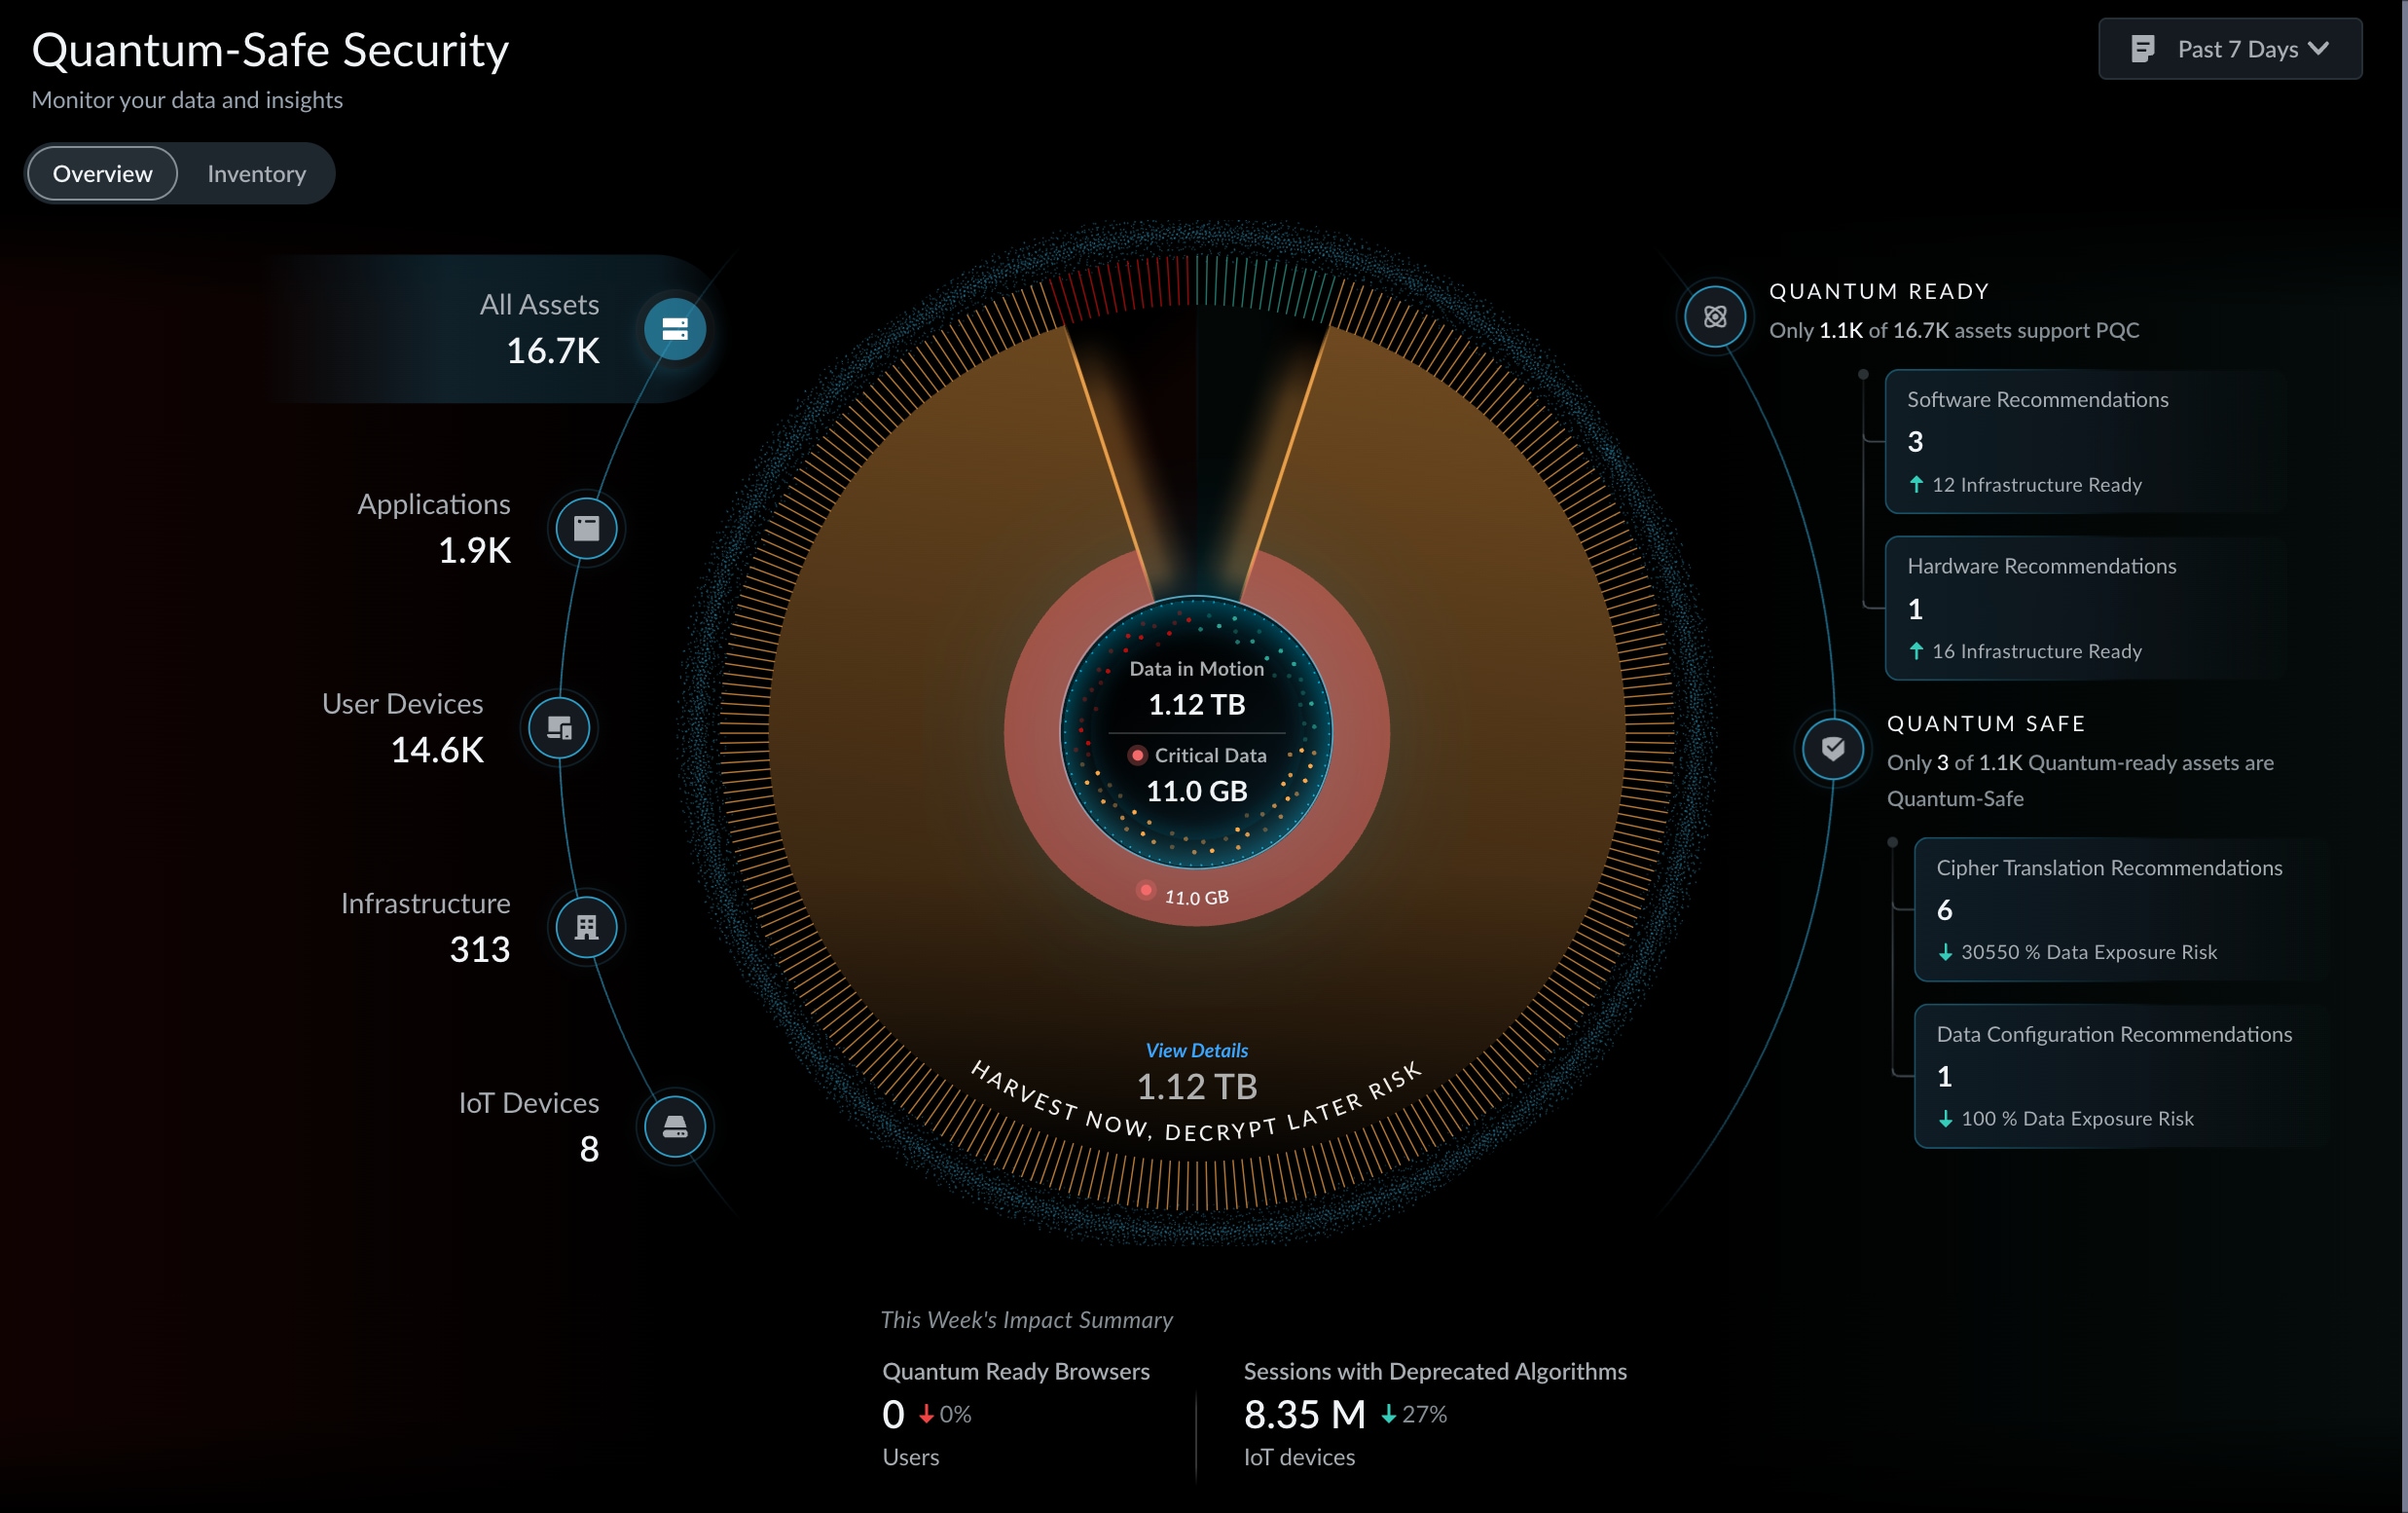
Palo Alto Networks Quantum-Safe Security dashboard

Accelerating Mandates for PQC Transition

Executive Order 14412 and OMB Memorandum M-26-15 have moved federal transition milestones well ahead of the original 2035 target. Federal agencies must now transition High Value Assets (HVA) and  high  impact  systems to post-quantum cryptography (PQC) for:

  • Key establishment: By December 31, 2030
  • Digital signatures: By December 31, 2031

Meeting these compressed timelines demands upgrading from static, manual inventory methods to continuous, automated cryptographic visibility. Traditional, annual spreadsheet audits are point-in-time snapshots that become obsolete the moment they are completed.

As the largest standalone cybersecurity provider, Palo Alto Networks leverages existing federal firewalls as distributed sensors within an integrated platform turns the network into an automated, real-time cryptographic control point. Agencies using the QSS solution will achieve high-fidelity visibility into their network-wide cryptographic posture and active algorithms immediately on Day 0, without introducing operational friction or deployment delays. By utilizing the native cryptographic discovery capabilities built into already deployed firewalls, agencies can activate their PQC migration plans without demanding a net-new, capital-intensive hardware acquisition. This makes Palo Alto Networks’ solution a fiscally responsible and rapid path to PQC migration execution. 

Technical Architecture: Discovery to Remediation

QSS operationalizes the full PQC migration lifecycle through a unified control plane built on three technical pillars:
  • Agentless Discovery: QSS transforms the existing Palo Alto Networks security fabric into a distributed sensor network, providing comprehensive  visibility into encrypted sessions, certificates, and tunnels. This approach identifies hidden cryptographic debt across diverse vendor ecosystems and IoT without forcing new agent rollouts or secondary hardware deployments.
  • Prioritized Risk Intelligence: The platform fuses automated cryptographic discovery with rich enterprise context, correlating the mathematical strength of ciphers and certificates against asset criticality and data sensitivity categorization. This multidimensional risk engine enables teams to move beyond raw technical alerts and focus resources on protecting long-lived, high-value data against Harvest Now, Decrypt Later (HNDL) attacks and cryptographic debt.
  • Active Inline Remediation: QSS moves beyond reporting to active risk reduction. For most legacy systems that cannot natively support PQC, Cipher Translation allows the firewall to translate weak classical encryption into quantum-safe standards at the network edge, shielding unpatchable assets without requiring application code changes.

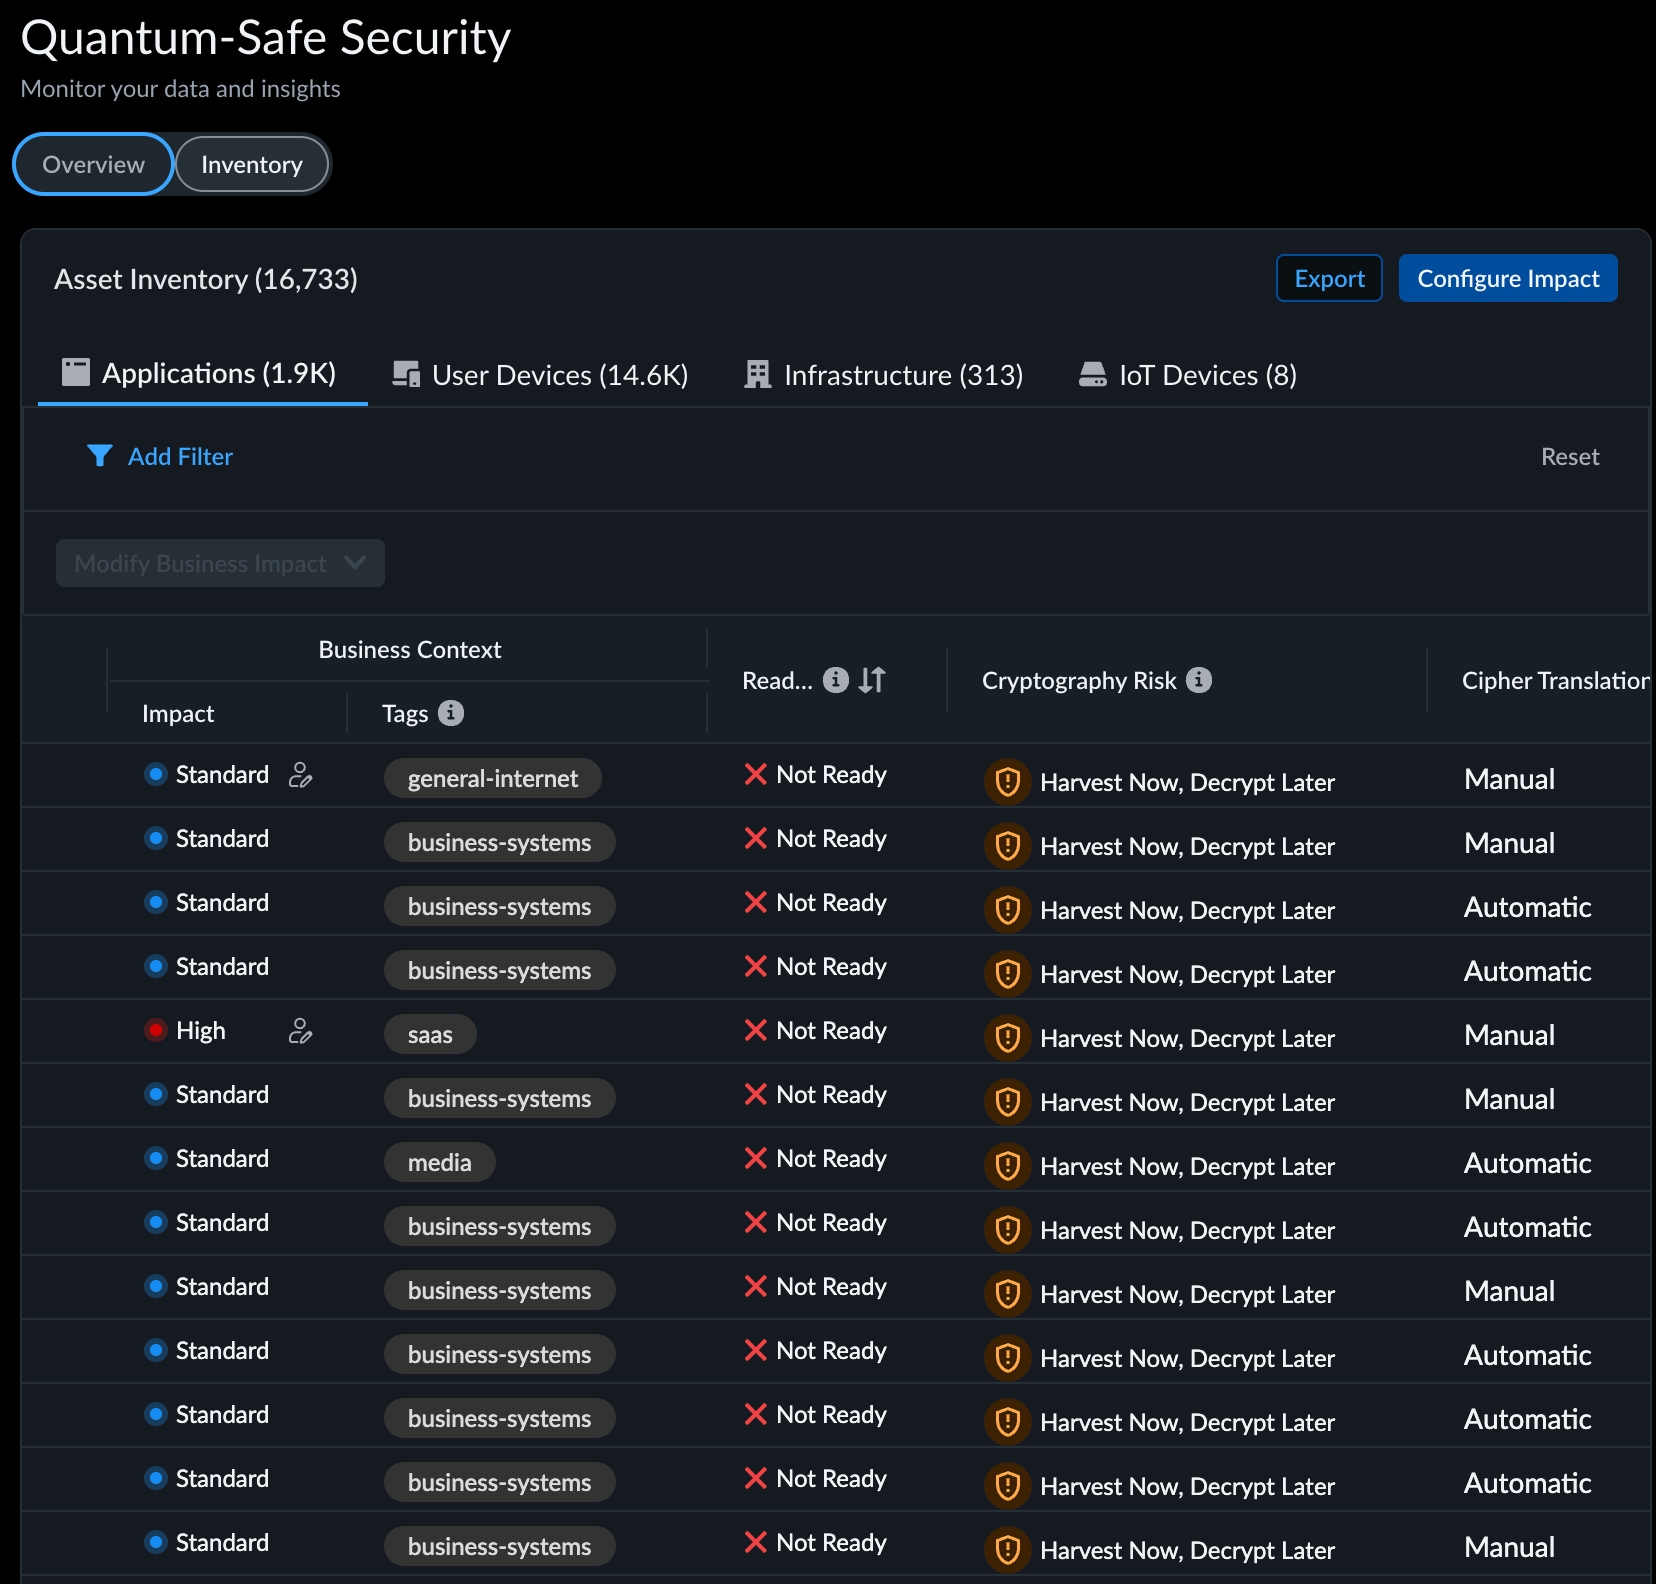
Quantum-Safe Security Asset Inventory with Cryptography Risk featuring Harvest Now, Decrypt Later (HNDL) Prioritization

Immediate Implementation

The Executive Order on Securing the Nation Against Advanced Cryptographic Attacks confirms that PQC is a national security imperative, not just a compliance requirement. For agencies, that means treating the shift to post-quantum cryptography as a strategic initiative that protects critical data today and safeguards it against tomorrow's threats. Our FedRAMP Moderate authorization reinforces that Palo Alto Networks is a proven partner in that effort, helping agencies build a cohesive posture that is "Secured in America" and made for the needs of the U.S. government. We're committed to helping the public sector modernize with confidence.

Get Ahead of the Mandate

Stop guessing which digital locks to change first. Quantum-Safe Security transforms your existing infrastructure into a high-fidelity sensor network to neutralize "harvest now, decrypt later" (HNDL) risks without new architectural complexity. Explore our FedRAMP Moderate authorized platform to see how you can achieve zero-downtime cryptographic resilience and bridge the gap for unpatchable legacy systems via in-line enforcement.