





As Best Buy expanded its use of Google Cloud for advanced analytics and AI, its technology teams faced two significant scaling challenges: Mitigating risk and managing administrative friction when syncing thousands of backend users from Microsoft Entra ID.
The retailer solved both problems and paved the way for a massive cloud expansion by implementing Google Cloud's Workforce Identity Federation. This direct approach allowed developers to access cloud resources securely using their existing Microsoft credentials without a separate identity store, giving technical leadership confidence that access remains strictly controlled, auditable, and manageable at scale.
Best Buy historically maintained complex synchronization pipelines to copy backend users from Entra ID to Google Cloud. Because the organization used Cloud Identity without a Google Workspace deployment, it needed a more direct approach. Previously, Best Buy's Power BI integration with BigQuery relied on service account credentials.
This pattern can work at a small scale, but quietly becomes a liability as your team grows.
Manually rotating keys for service accounts meant tracking the credentials each team held, and accepting that every key was a potential security vulnerability. Service account keys created daily friction for the Best Buy security and platform teams, and the technical debt compounded as data access requirements grew more complex.
To support tens of thousands of users, Best Buy modernized its identity architecture. The team adopted Workforce Identity Federation to federate existing Entra ID identities directly into Google Cloud.
Now, when developers access BigQuery through Power BI, they authenticate as themselves using their existing Entra ID identity. They no longer need to rotate keys, worry about credentials exposed in chat messages, or guess who performed an action in the audit log.
The architecture relies on two components working together: Entra ID handles authentication, Workforce Identity Federation brokers the trust relationship between Entra ID and Google Cloud. This federation is stateless on Google's side. It validates tokens at the moment of access instead of syncing user records. Removing the service account key layer greatly reduces the credential management burden.
Architecture
The diagram below shows how identity flows from Entra ID through the Workforce Identity Federation to the services teams use at Best Buy. The key change from the previous approach is the removal of the service account key layer entirely; there is no credential to manage between Entra ID and Google Cloud.
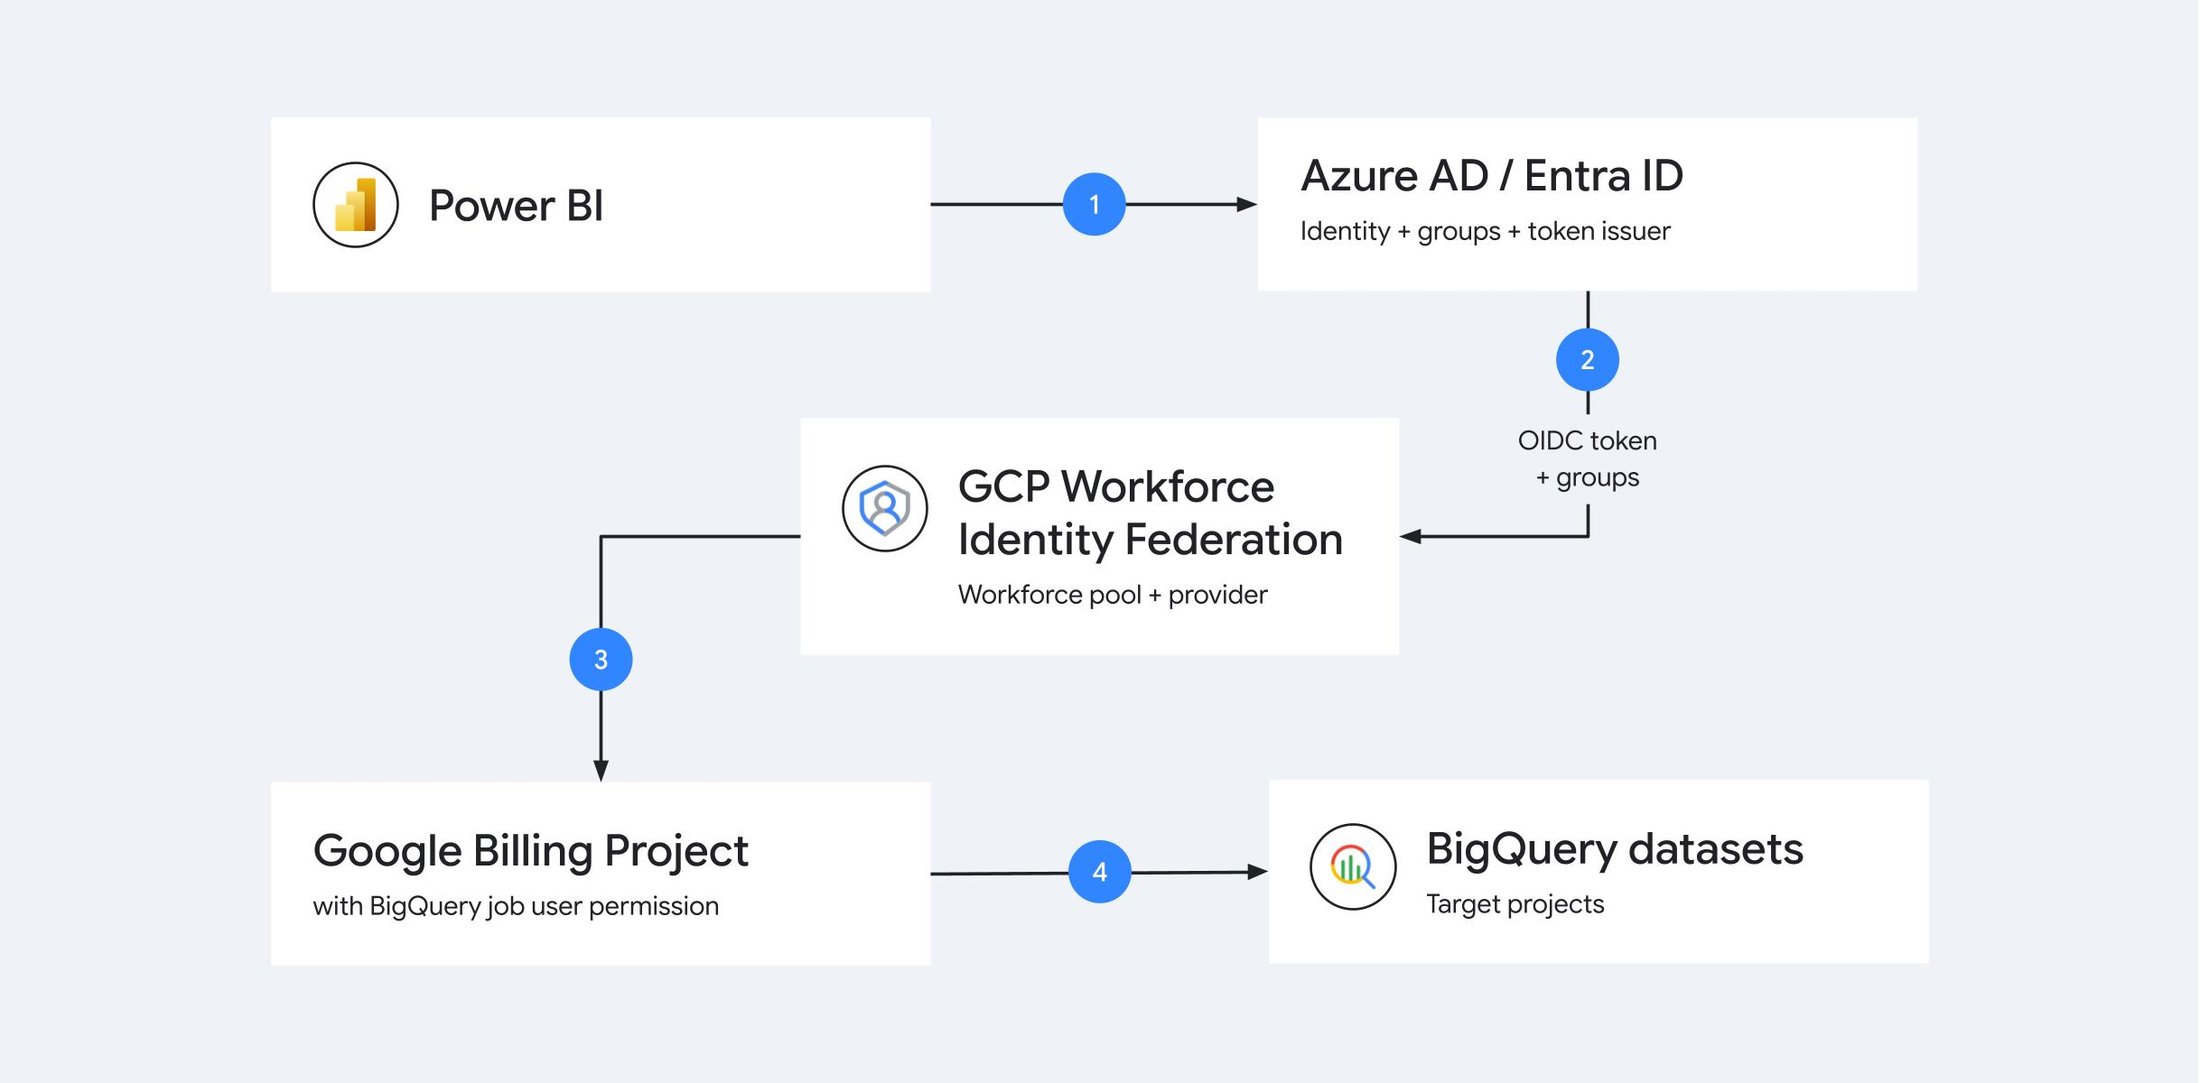
Identity flows from Entra ID through the Workforce Identity Federation to the services teams use at Best Buy
When implementing this architecture, Best Buy made several important technical choices:
Separate provisioning and SSO apps in Entra ID: The configuration follows the Entra ID provisioning and single sign-on (SSO) setup guide. You should separate the provisioning application from the SSO application in Entra ID. Running them as two distinct enterprise apps provides a cleaner separation of concerns; provisioning changes do not affect SSO configuration, and vice versa.
Place the automation OU carefully: You need to place the Entra ID provisioning service account in a separate organizational unit (OU) and explicitly disable SSO for that OU. This prevents a bootstrapping problem: If you enforce SSO globally, the provisioning account cannot authenticate to set up the provisioning in the first place.
Understand that syncless means stateless on Google's side: Workforce Identity Federation does not create or maintain user records in Cloud Identity. It validates tokens at the moment of access. This makes the architecture viable for Best Buy's target scale, because it eliminates synchronization lag, stale record cleanup, and separate provisioning pipelines.
For developers, the change was practically invisible. They authenticate once through their corporate Entra ID credentials, and access to BigQuery works automatically, whether through Power BI or direct API calls. The SSO experience matches everything else they access through their Microsoft identity.
For the security and platform teams, the benefits are significant. The attack surface from credential management disappears. Audit logs now show individual users instead of shared service account identities, and you can revoke access quickly based on the enterprise identity lifecycle rather than waiting for manual key rotation.
If you currently manage service account keys for developer access to Google Cloud, moving to Workforce Identity Federation is worth the effort. You gain significant security benefits, and the operational simplicity grows as your team expands. Best Buy is currently scaling this secure access to a broader workforce to power its future retail operations.
Google Cloud continues to make it easier for all organizations to bring their own identity providers. Recent updates simplify the setup for Ping Identity users and extend access to online billing accounts.
Ping Identity integration: If you use Ping Identity, you can follow a new, dedicated setup guide to configure federation. This guide provides step-by-step instructions so you can securely connect your workforce to Google Cloud resources.
Online billing support: Google Cloud now supports customers with online billing accounts. You can use Workforce Identity Federation for secure, syncless access without needing an enterprise billing agreement.
Google Cloud is committed to removing friction from cloud adoption and making it simpler for organizations to secure their environments. To explore these new capabilities and connect your organization's identity provider, read more about how Workforce Identity Federation allows you to federate identities directly, and explore our supported Google Cloud services.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。