








As an MSP, you need to be able to gather information from your clients, prospects, and vendors/suppliers to understand their risk, cybersecurity posture, and compliance requirements. Obtaining that information takes time, however, and you need align it to your security offering to take meaningful actions.
Todyl Security Assessments simplifies this process and integrates insights from your clients’ security programs directly into the same interface you use to manage them. Until the end of 2025, this feature is available for all Todyl partners at no extra cost.
Let’s explore why Security Assessments are a critical tool in your belt, and how you take advantage of them to improve your ability to interact with your clients’ security and compliance standings.
If you’ve ever tried to collect security or compliance information from clients, you know how painful it can be. Endless back-and-forth emails. Outdated spreadsheets. Partial answers that need constant clarification. What should be a quick information gathering process often turns into a multi-week slog.
For most MSPs, this process eats up valuable hours, time that could be spent on higher-value work like improving client security posture or onboarding new accounts. Instead, engineers and account managers find themselves stuck in administrative mode, trying to wrangle the right contacts, validate responses, and track what’s still missing.
It’s not just inefficient; it’s risky. When you can’t quickly get accurate answers about your clients’ controls, configurations, or compliance posture, you’re flying blind. You can’t confidently advise them, you can’t complete necessary assessments, and you can’t demonstrate due diligence if something goes wrong.
For MSPs managing multiple clients across industries, this problem multiplies fast. Each questionnaire or audit cycle becomes a manual grind: duplicating work, chasing down answers, and hoping no detail slips through the cracks.
In addition to these operational challenges, there’s a relational cost. Clients start to feel the strain of repetitive requests and confusing questionnaires, often wondering why their MSP doesn’t already “know” the answers. Each follow-up email chips away at the sense of trust and partnership that MSPs work so hard to build. Instead of feeling supported, clients start feeling audited, creating friction in what should be a collaborative security effort.
Security Assessments take the headache out of gathering critical information from clients. MSPs can now send structured, streamlined questionnaires that capture key security and compliance details directly from the source without the endless email threads or manual tracking.
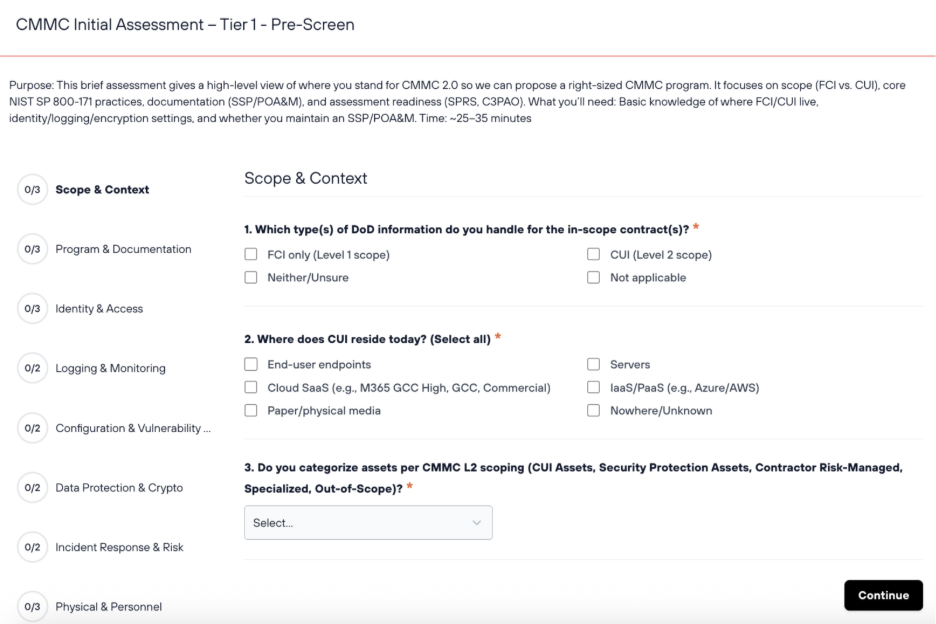
Each assessment helps you quickly get the data you need to evaluate client posture, identify gaps, and kick off remediation plans. Responses are centralized within Todyl, so you can immediately take action and tie answers directly into our growing GRC solution to streamline proof of compliance. That way, you always have an up-to-date view of each client’s security status and can easily demonstrate progress over time.
The feature comes with multiple prebuilt templates that you can send directly to clients to get answers fast regarding their general security posture, as well as multiple templates specific to critical compliance frameworks like CIS, CMMC, and HIPAA. You can see the templates available to you right now below:
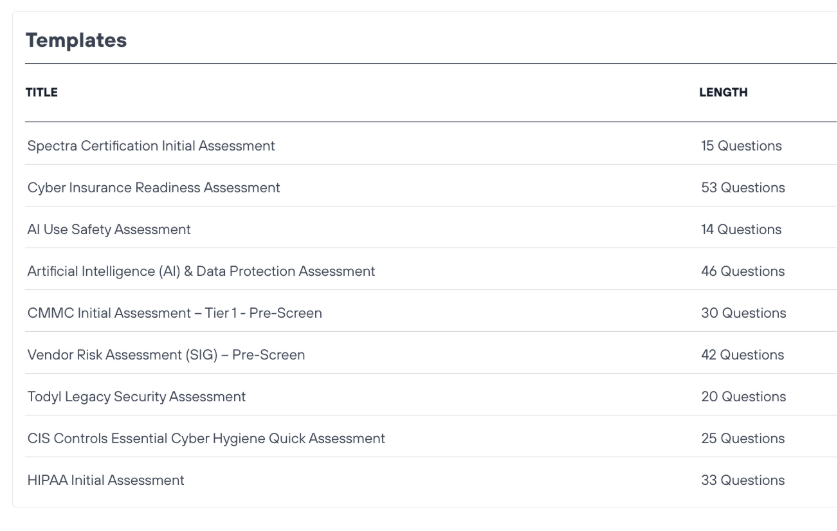
And, if you need to quickly expand upon or edit a template, you can clone it in one click, then add in your necessary questions and evidence gathering, including file uploads. Of course, if you have your own list of questions, or one supplied by an insurance adjustor or auditor, you can create your own templates from scratch.
Each assessment is tied directly to a specific client tenant and sent directly to client emails. The emails are gated for security purposes, preventing any misuse of clients’ critical security information.
You can also use Security Assessments for companies outside of your existing Todyl tenants, such as new clients or potential ones. Using the same process, you can send intake forms to understand companies’ current security posture, enabling a more prescriptive approach to managing their security program from square one.
The result is a more informed approach with less time wasted in back-and-forth conversations or risky, outdated documents and spreadsheets. Instead, with Security Assessments, you get the answers you need fast, so you can confidently manage security risks, prove compliance, and apply for cybersecurity insurance.
October is Cyber Action Month, and we want to help you to take action and benefit from Security Assessments today. Current Todyl partners can start using Security Assessments right now for free until the end of the year. Just click Assessments under the GRC tab to get started.
If you’re not a Todyl partner, you can get your free trial today. See how Security Assessments fit into the bigger picture of the Todyl Security Platform, helping you provide enterprise-grade cybersecurity through a comprehensive platform designed for MSPs.
Zach DeMeyer is Todyl's Product Marketing Specialist, sharing the story of how businesses can use the Todyl platform to consolidate their security operations with SASE, SIEM, MXDR, Endpoint, SOAR, and more. He loves being on the forefront of new and exciting technologies, spending the past 8 years working in identity, UCaaS, and other SaaS products in the cybersecurity and IT software space. When he's not working, Zach enjoys camping and hiking with his wife, dog, and friends, playing music, sewing, and eating tasty food.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。