







Tax season. Black Friday. Back to school. These aren't just busy times for your business; they're prime hunting season for cybercriminals to take advantage of when executing Business Email Compromises(BECs) and similar attacks. Bad Actors know that when everyone's inbox is flooded with expected messages about the same topic, people let their guard down. And few corporate events are as universally anticipated, or as ripe for exploitation, as the annual benefits open enrollment period.
Every fall, employees across the country expect emails about health insurance, 401(k) changes, and benefits deadlines. It's the perfect cover for a phishing attack. Threat actors craft convincing messages that look like they're from HR or your benefits provider, complete with urgent deadlines and links to "update your information." One distracted click by any employee and you’re compromised.
This isn't a theoretical threat. Todyl’s MXDR team recently detected and shut down a sophisticated phishing campaign that did exactly this—exploiting the end-of-year open enrollment window to target organizations with highly credible fake benefits emails. Here's how it unfolded, how we caught it, and what it means for your security posture.
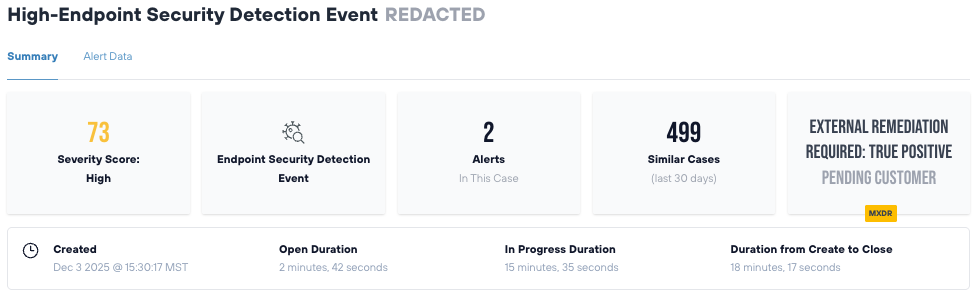
Time to Investigation: 2 minutes, 42 seconds
Time to Containment: 15 minutes, 35 seconds
Total Case Duration: 18 minutes, 17 seconds (from creation to close)
Result: Threat neutralized in under 20 minutes from initial alert, preventing potential data exfiltration, lateral movement, and business disruption.
~3:14 PM - User receives and opens a phishing email in Outlook containing a malicious link
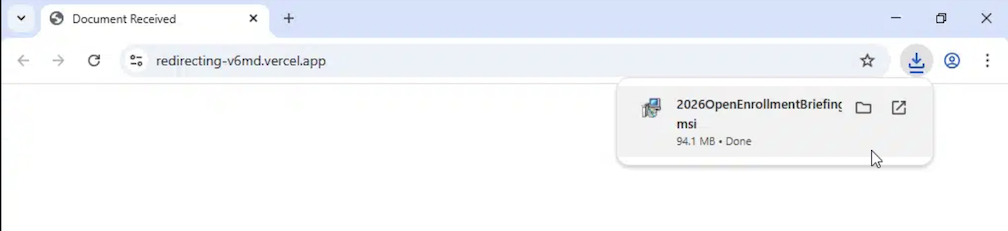
3:14:26 PM - User clicks embedded link, which launches Microsoft Edge and redirects through a malicious domain (redirecting-v6md[.]vercel[.]app)
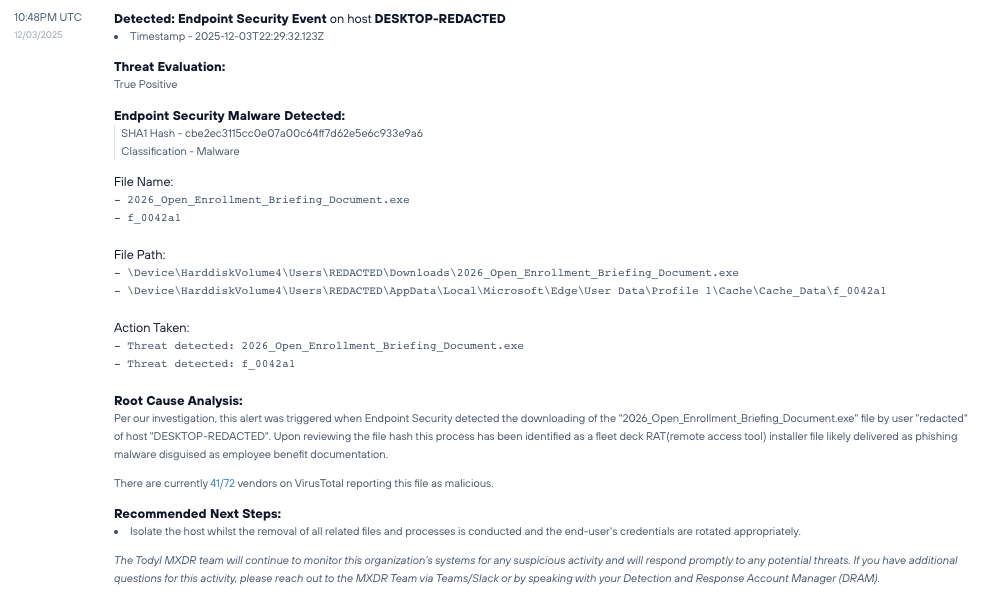
3:14:42 PM - (16 seconds later), malicious file "2026OpenEnrollmentBriefing.msi" downloaded (94.1 MB actual / 4.19 MB compressed)
3:14:42 PM - Todyl detects the attempted RAT (Remote Access Trojan) execution immediately
3:15:30 PM - MXDR case automatically created by Todyl platform
3:18:12 PM - Security analyst begins investigation (2 minutes, 42 seconds after case creation)
3:33:47 PM - Threat contained and case closed
| Attribute | Details |
|---|---|
| File Hash (SHA-1): | cbe2ec3115cc0e07a00c64ff7d62e5e6c933e9a6 |
| VirusTotal Detection: | 41/72 security vendors flagged as malicious |
| Threat Classification: | FleetDeck RAT / Tedy Trojan |
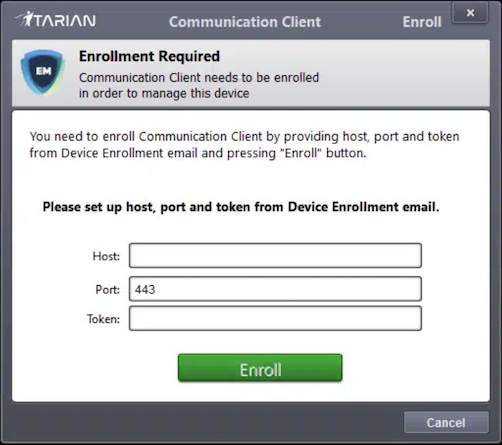
| C2 Infrastructure Contacted: | Primary domain: agentupdate[.]fleetdeck[.]io Multiple AWS CloudFront IPs (13.249.141.x range) Port 443 (HTTPS) for encrypted C2 communications |
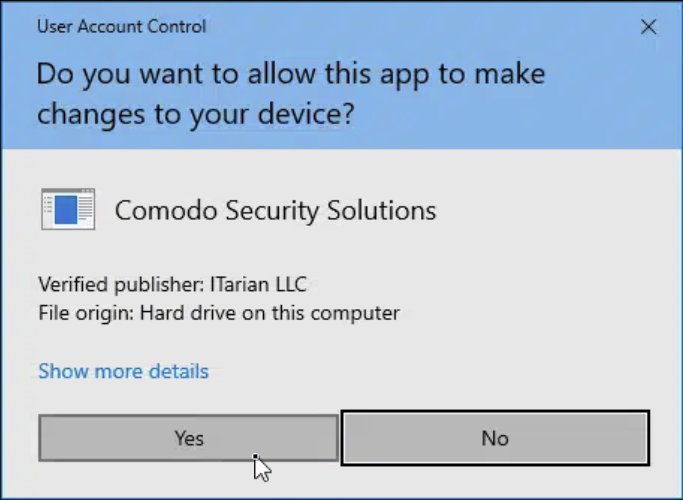
Upon execution in a controlled environment, the malware exhibited sophisticated evasion and social engineering tactics:
Business email compromise attacks are only getting more sophisticated and even the best-trained employees can slip up. Attackers know that open enrollment season, tax deadlines, and other routine events create the perfect cover for exploiting lax security measure and inattentive users. That's why layered security and rapid detection and response capabilities are essential.
At the end of the day, it's not about being paranoid, it's about being prepared. When attackers come after your users, you want to shut them down before they can do any damage. The right combination of solutions like SASE, SIEM, endpoint protection, and 24/7 detection & response can give you the tools you need to protect your environment and dramatically reduce your risk.
Stay vigilant. Stay protected. And if you need backup, we're here to help.
Nick is Todyl's Director of Advanced Threat Operations. After 5 years of working with the NSA, Space Force, and US Army Cyber, Nick made the switch to bring his expertise to the private sector at Todyl. With his experiences in cyber red teams, Nick has forged that mentality into his approach for defending Todyl partners from today's advanced threats. When he's not keeping Todyl partners safe, he enjoys building and racing motorcycles.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。