








Quick answer: No single tool secures an API. API security is a layered discipline. Secure-coding analyzers and SCA scanners catch code and dependency flaws; DAST tests running APIs; API gateways and IAM enforce authentication and rate limits; a WAF blocks known attack patterns; bot management stops automated abuse; and runtime API security adds continuous discovery and catches business-logic threats like BOLA that other tools miss. This guide maps these API security tools to seven risk domains so you can see your coverage—and your gaps.
APIs power mobile apps, partner integrations, cloud microservices, SaaS platforms, and AI services; they are the business.
According to Imperva’s State of API Security report, API traffic now accounts for over 71% of all web traffic. As APIs have exploded in number and importance, so has the challenge of securing them.
When organizations look for “API security,” they quickly face a confusing mix of tools:
Each tool does protect APIs, but only in its own narrow way.
API security is not a single product. It is an architectural discipline that spans the entire API lifecycle: from design to code, deployment, runtime, and monitoring.
This blog cuts through the noise. It shows exactly which risks each security component addresses, and where the gaps remain, so you can build a complete, layered defense.
API risks don’t come from one place. They appear at every stage of the software lifecycle. Here are the seven core risk domains you must understand:
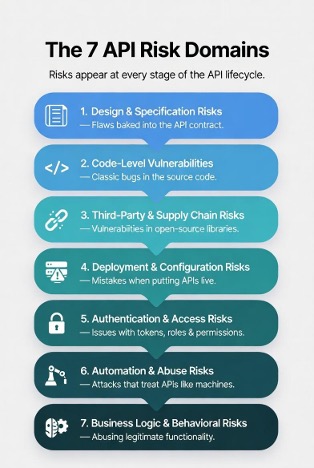
Real breaches almost always happen when risks from multiple domains line up.
Example:
A valid token (authentication risk) + excessive data exposure (design risk) + an exposed endpoint (configuration risk) + automated enumeration (abuse risk) = a major breach.
No single tool covers every domain. That’s why a layered approach is essential.
Enterprise API protection never comes from one product. It’s a combination of tools working in different layers. Here’s what each major component does:
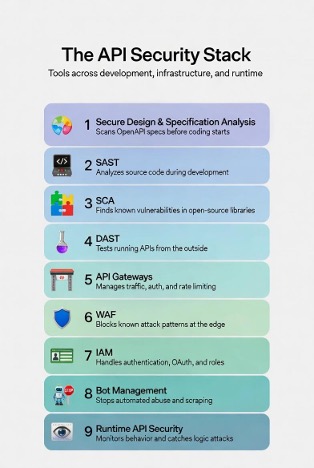
Here’s a clear, at-a-glance view of what each component covers:
| Security Component | Design | Code | Supply Chain | Config | Auth | Abuse | Logic |
| SAST | ❌ | ✅ | ❌ | ❌ | ⚠️ | ❌ | ❌ |
| SCA | ❌ | ❌ | ✅ | ❌ | ❌ | ❌ | ❌ |
| DAST | ❌ | ⚠️ | ❌ | ⚠️ | ⚠️ | ❌ | ❌ |
| WAF | ❌ | ⚠️ | ❌ | ⚠️ | ❌ | ⚠️ | ❌ |
| API Gateway | ❌ | ❌ | ❌ | ⚠️ | ✅ | ⚠️ | ❌ |
| IAM | ❌ | ❌ | ❌ | ❌ | ✅ | ❌ | ❌ |
| Bot Manager | ❌ | ❌ | ❌ | ❌ | ❌ | ✅ | ❌ |
| Runtime API Security | ⚠️ | ⚠️ | ❌ | ⚠️ | ⚠️ | ✅ | ✅ |
Legend
✅ = Strong / primary coverage
⚠️ = Partial or indirect coverage
❌ = No meaningful coverage
What Runtime API Security delivers
Quick takeaway on Runtime API Security
It shines brightest in Business Logic (its real superpower) and gives helpful visibility across most other domains, but it still works best alongside the other tools. Solutions like Imperva API Security from Thales are built specifically for this layer.
Building Your Layered API Security Strategy
API security isn’t about buying one magic product. It’s about understanding the full risk picture and picking the right tool for each layer.
Next Steps
Organizations that treat API security as an architectural discipline, not a checkbox, are the ones that move fast and stay secure.
What tools are used for API security?
There is no single API security tool. A complete stack layers several: secure-coding analyzers (SAST) and software composition analysis (SCA) for code and dependency flaws, DAST for testing running APIs, API gateways and IAM for authentication and rate limiting, a WAF for known attack patterns, bot management for automated abuse, and runtime API security for discovery and business-logic threats such as BOLA.
Is a WAF enough to secure APIs?
No. A WAF blocks known attack patterns at the edge, but it cannot see business-logic abuse like Broken Object Level Authorization (BOLA) and does not discover shadow or undocumented APIs. Imperva’s research notes that traditional tools such as a WAF struggle to detect API business-logic abuse, so runtime API security is needed alongside it.
What is runtime API security?
Runtime API security continuously discovers every API—including shadow and deprecated endpoints—monitors live traffic, and uses behavioral analysis and object-level authorization checks to catch business-logic attacks, including the low-and-slow threats other tools miss.
What are the main API security risks?
API risk spans seven domains across the lifecycle: design and specification, code-level, third-party and supply chain, deployment and configuration, authentication and access, automation and abuse, and business logic and behavioral risks. Most breaches happen when risks from several domains line up at once.
Protect your business for 30 days on Imperva.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。