








TL;DR: A critical remote code execution vulnerability has been disclosed in FastJson, a widely used JSON processing library for Java. The vulnerability, assigned CVE-2026-16723 with a CVSS score of 9.0 (Critical), affects FastJson versions 1.2.68 through 1.2.83 under specific Spring Boot deployment conditions and can be exploited using malicious JSON without authentication, enabling AutoType, or relying on third-party gadget classes.
Imperva customers are protected against exploitation attempts associated with this vulnerability. Organizations using FastJson 1.x should enable SafeMode immediately and prioritize migration to FastJson 2.x.
On July 21, 2026, the FastJson maintainers published a security advisory for a critical remote code execution vulnerability discovered by FearsOff Cybersecurity. FastJson is an open-source Java library originally developed by Alibaba for serializing Java objects into JSON and deserializing JSON into Java objects.
The vulnerability affects FastJson versions 1.2.68 through 1.2.83, including 1.2.83, the final release in the FastJson 1.x branch. It’s been assigned CVE-2026-16723, with a CVSS score of 9.0, or Critical. According to the official FastJson advisory, exploitation has been verified in Spring Boot applications deployed as executable fat JARs across Spring Boot 2.x, 3.x, and 4.x and JDK versions 8, 11, 17, and 21.
The issue is particularly dangerous because it is exploitable under FastJson’s default configuration. AutoType does not need to be enabled, and attackers do not need a suitable third-party gadget class to be present in the application’s classpath. Applications are potentially exposed when they process attacker-controlled JSON using common methods including JSON.parse, JSON.parseObject(String), and JSON.parseObject(String, Class).
Specifying a target class during deserialization does not fully mitigate the vulnerability. An attacker may still be able to place a malicious payload inside a field typed as an Object or Map.
FastJson supports polymorphic deserialization through the @type field, which identifies the Java class that should be instantiated from supplied JSON. Although FastJson 1.x disables AutoType by default and applies checks intended to prevent untrusted classes from being instantiated, the newly disclosed vulnerability exposes an alternate path through its internal type-resolution logic.
An attacker can submit specially crafted JSON containing a malicious @type value. During processing, FastJson may perform resource lookups based on the attacker-controlled class name. In affected Spring Boot fat-JAR deployments, an attacker can manipulate this behavior using nested JAR URLs, bypass FastJson’s normal type restrictions, and reach a code-execution path without supplying a conventional deserialization gadget.
This bypass is possible because FastJson 1.x can treat the presence of a @JSONType annotation as a trust signal during type resolution. The attacker-controlled resource lookup and annotation-based trust behavior combine to circumvent the protections normally associated with disabling AutoType.
Successful exploitation can allow an unauthenticated remote attacker to execute arbitrary code with the privileges of the affected Java application. This could lead to data theft, malware or webshell deployment, credential compromise, lateral movement, or complete takeover of the underlying server. Public proof-of-concept information is available, substantially increasing the likelihood of rapid exploitation.
FastJson 2.x is not affected. Its type-resolution architecture does not perform equivalent resource probing on user-controlled class names, does not use @JSONType as a trust signal, and uses an allowlist-first model for polymorphic type handling.
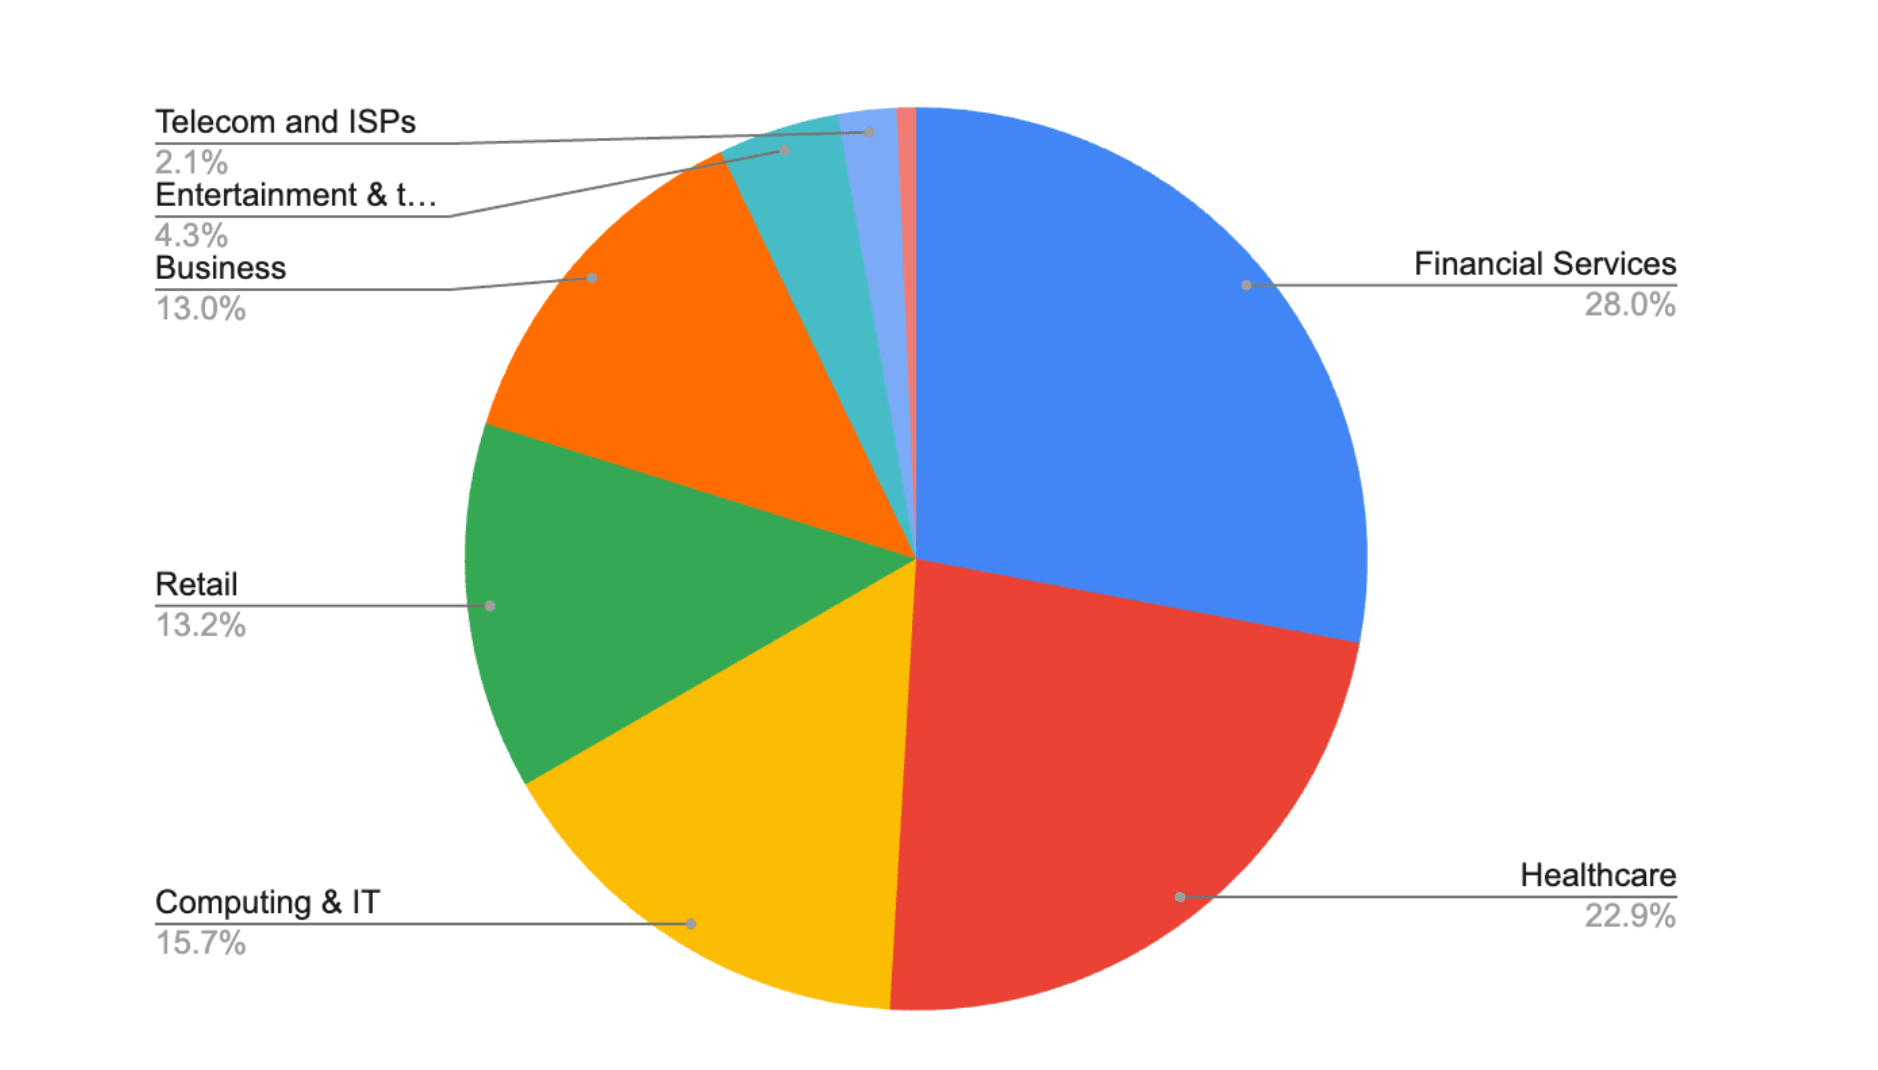
So far, attacks exploiting this vulnerability are targeting a wide range of organizations, across Financial Services, Healthcare, Computing, Retail, Business, and other industries.
Attacks are currently almost entirely targeting US-based organizations, with a few attacks in Singapore and Canada, although this will likely continue to expand globally.
Most attacks are coming from browser impersonators, although tools written in Ruby and Go account for about 30% of all attacks collectively.
Imperva customers are protected against exploitation attempts associated with CVE-2026-16723. Imperva Cloud WAF and WAF Gateway inspect incoming HTTP requests and identify malicious JSON payloads, suspicious @type values, nested JAR URL patterns, and remote code execution techniques before they reach vulnerable applications.
Organizations should not rely on perimeter protection as a substitute for remediation. FastJson 1.x is no longer actively maintained, and no patched 1.x version has been released for this vulnerability. Organizations using an affected release should take the following actions:
Because exploitation requires no authentication, no user interaction, and no external gadget library, exposed applications running affected configurations should be treated as high-priority remediation targets. Imperva customers remain protected while organizations identify vulnerable deployments, enable SafeMode, and migrate away from FastJson 1.x.
Protect your business for 30 days on Imperva.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。