



Artificial intelligence is creating a new attack surface organizations must secure. It’s defined by a collision of forces that make it complex:
If the response to both developments is simply to generate more alerts after suspicious activity begins, defenders will be trapped in a race they cannot sustainably win. For this reason, the new AI arms race starts well before an attack with AI visibility, control, and the ability to leverage AI to shrink the attack surface.
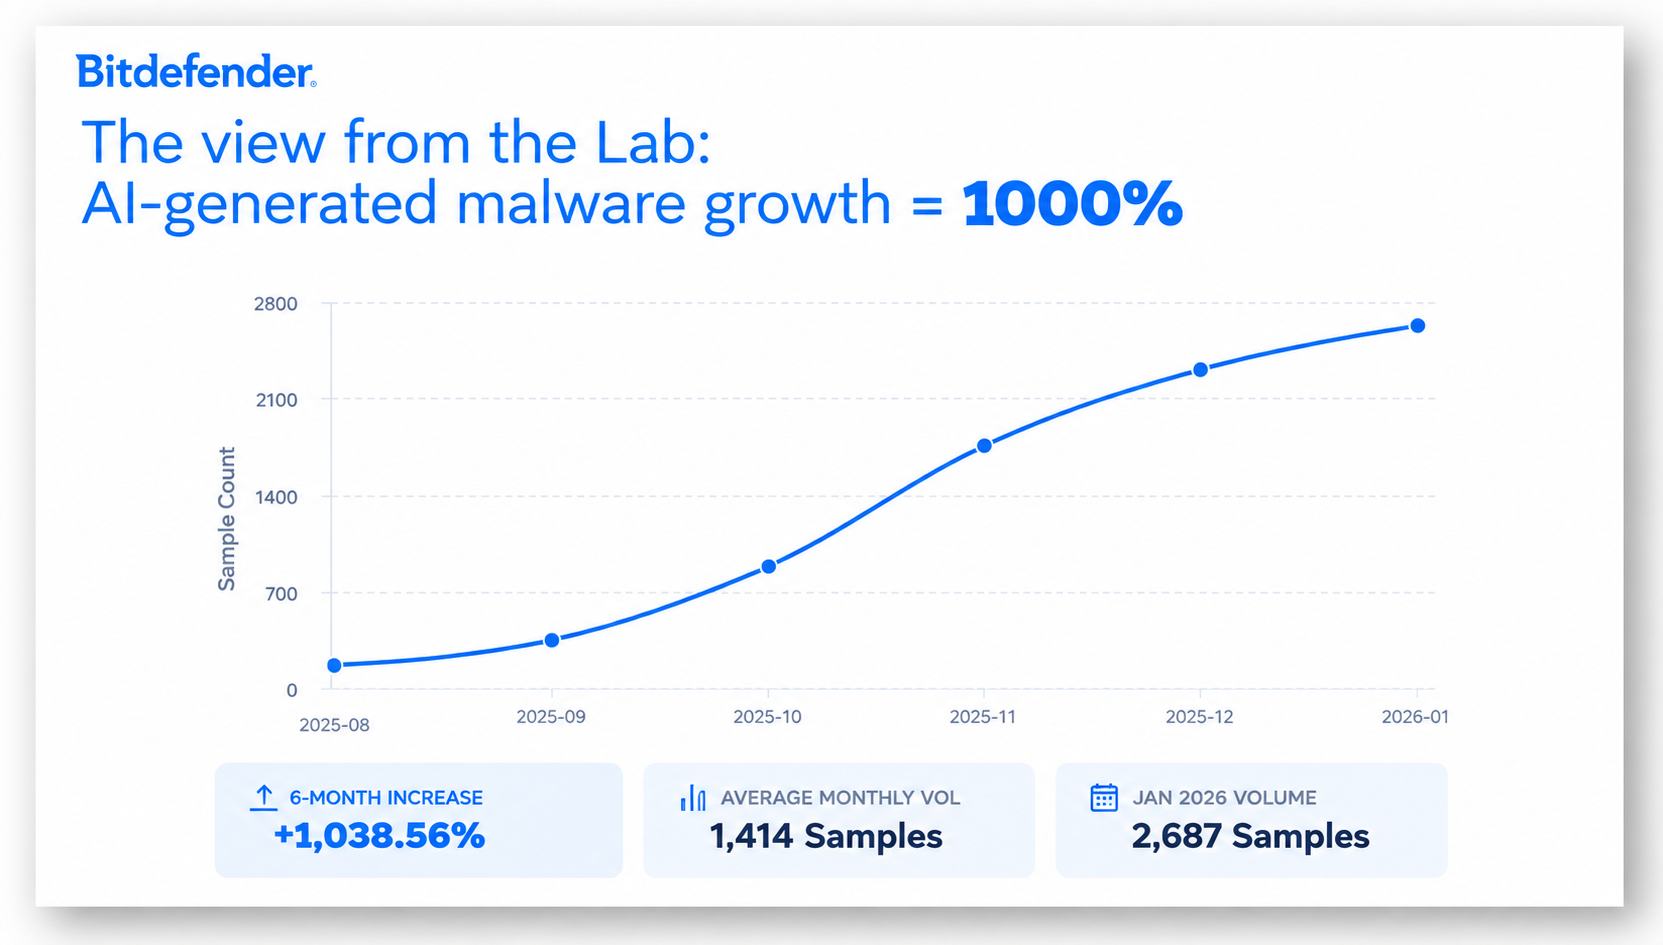
When it comes to AI generated malware, the trajectory is up and to the right.
From August 2025 through January 2026, Bitdefender Labs tracked more than a 1,000% increase in AI-generated malware samples. This is an early-warning signal that attackers are rapidly testing how AI can help them create, modify and scale malicious code.
According to 1,200 IT and cybersecurity professionals surveyed in the Bitdefender 2026 Cybersecurity Assessment, 59% say their organization has experienced social engineering attacks they believe involved AI, while 56% report encountering AI-generated malware-based attacks.
Most strikingly, 70% say they are seeing increasingly sophisticated phishing attacks enabled by AI tools.
As a result, 53% of respondents say AI helps attackers more than defenders.
The central problem is not only whether defenders can detect these attacks, but also whether organizations can continue relying so heavily on detection and response when attacks can be generated, adapted, and launched at machine speed.
AI tool adoption has moved ahead of governance. Security teams are now accountable for an attack surface they may not be able to see clearly, much less control consistently.
Employees are using a wide range of public AI services. Most previously approved tools are now adding AI capabilities. Developers are connecting models to business systems and data through APIs. And let’s not forget about all the potentially sensitive information end-users may be sharing with AI.
Data says IT and Security teams are struggling here: the cybersecurity assessment found that 44.8% of IT and security professionals have only partial visibility into AI use within the organization. And when it comes to 2026 priorities, the number one focus is, “Implementing comprehensive internal AI governance,” according to the research.
The new AI arms race requires a rebalancing of security priorities, with a pivot toward prevention. A prevention-first strategy moves beyond “How quickly can we detect this attack?” It asks, “How many attack opportunities can we remove before threat actors can take action?”
Detection and response still provide the critical safety net. Prevention reduces how often that net has to catch something and the chance an attack causes material harm.
Looking at internal AI risk, prevention depends on visibility. Organizations cannot reduce an attack surface they cannot see.
Security and IT teams need to understand which AI services are being used, what data and systems they can touch, and which behaviors create the greatest risk. That allows teams to prioritize governance instead of imposing blanket restrictions employees may circumvent.
It also lets organizations use controls they may already have.
Web access policies can address risky services. Hardening policies can reduce exploitable configurations and unnecessary functionality. Web filtering can limit access to public cloud models and Shadow AI.
The objective should not be to stop AI adoption. It should be to make adoption visible, intentional, and safer, without creating another isolated security program that adds more tools, consoles, and operational complexity.
Organizations must build AI into their modern security operations center or choose an MDR provider that utilizes AI in the SOC. It helps teams analyze signals, accelerate investigations, automate repetitive work, and respond more quickly. Those capabilities will become increasingly important as threats grow faster and more numerous.
However, the AI arms race will not be won by building faster detection alone. Organizations must also leverage AI-powered tools that can shrink the attack surface and create unique security settings for each user.
Defenders must apply intelligence before an incident begins: identify exposure, reduce privileges, harden environments, govern AI use, and continuously remove potential attack paths. That is how organizations change the equation from racing to contain every AI-enabled attack to denying more of those attacks the opportunity to succeed in the first place.
More: AI-Powered Security Across the Complete Attack Lifecycle
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。