






Socket proactively blocks malicious open source packages in your code.
For three days, Claude Fable 5 had users around the world one-shotting work they expected to take days or weeks: major code reviews, migrations, long-running builds, and projects some described as career-changing. Then access disappeared.
If you were waiting for the weekend to try Claude Fable 5, you’re out of luck.
Anthropic suspended access to Claude Fable 5 and Claude Mythos 5 on Friday night after receiving a US government export control directive blocking access by foreign nationals, including foreign national Anthropic employees. Anthropic said the practical effect of the order is that it must disable both models for all customers while it works to comply.
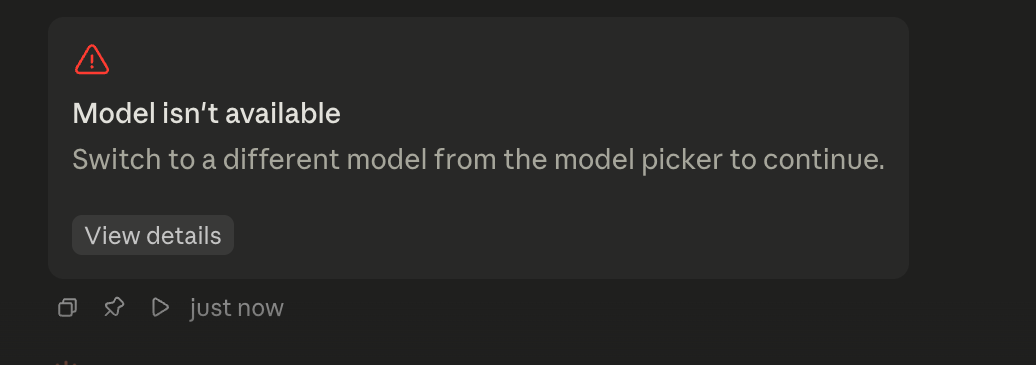
The shutdown came just three days after Anthropic launched Fable 5 as its most capable generally available model to date. In its June 9 launch post, Anthropic described Fable 5 as a “Mythos-class” model with safeguards for general use, including classifier-based fallback to Claude Opus 4.8 for some cybersecurity, biology and chemistry, and distillation-related requests. Mythos 5, the less-restricted version of the same underlying model, was limited to selected cyberdefense and infrastructure partners through Project Glasswing, with broader trusted access planned.
Anthropic said the government directive arrived at 5:21pm ET on June 12 and did not include specific details about the national security concern. The company said its understanding is that the government became aware of a method for bypassing, or “jailbreaking,” Fable 5.
Anthropic disputed the apparent technical basis for the directive. The company said it reviewed a demonstration of the technique being used to identify “a small number of previously known, minor vulnerabilities,” and said other publicly available models could find the same issues without requiring a bypass. Anthropic also said it has not received evidence of a universal jailbreak, meaning a method that broadly disables the model’s safeguards across many cyber capabilities.
Instead, Anthropic described the reported issue as a narrow, non-universal jailbreak that “essentially consists of asking the model to read a specific codebase and fix any software flaws.” That workflow is already common in defensive software engineering: feed a model a codebase, ask it to find bugs, and have it propose fixes.
The abrupt suspension immediately created customer fallout. In the r/ClaudeAI subreddit, users reported losing access mid-project, after upgrading paid plans, or while preparing to test Fable 5 before Anthropic’s temporary subscription access window expired on June 22. Now Anthropic is dealing with a launch-week nightmare: users who really wanted Fable paid up, lost access, and are demanding refunds.
Anthropic had already positioned Opus 4.8 as Fable’s safety fallback. After the suspension, it became the replacement. For users who had spent three days putting Fable through complex tasks, the return to other models felt like a painful downgrade.
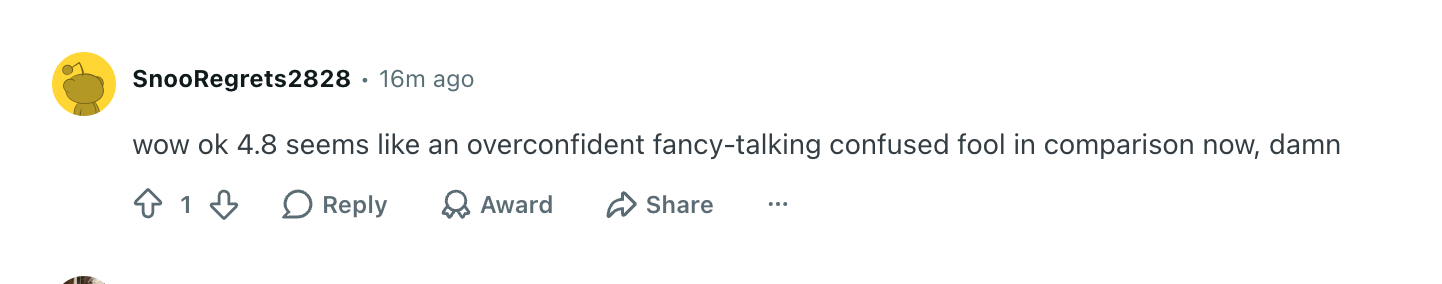
Some users said Anthropic’s support bot processed refunds quickly, while others said they were denied or told a refund would remove broader Claude access. Several also reported that Anthropic reset weekly usage limits, though that does not fully address customers who upgraded specifically for access to Fable 5.
The reaction was not aimed only at the government. Some users blamed Anthropic’s own safety messaging, arguing that the company had repeatedly emphasized the danger of its most capable models while also calling for stronger AI oversight. Now, those users are asking whether that framing made Fable 5 an easier target for intervention.
Anthropic said it is complying with the directive but disagrees with the decision. The company said a narrow jailbreak finding should not justify recalling a commercial model “deployed to hundreds of millions of people,” and warned that applying the same standard across the industry could halt new frontier model deployments.
The incident leaves Anthropic in an awkward position. Fable 5 was marketed as a major step forward for software engineering and long-context work, with safeguards designed to make Mythos-class capability safe for broad release. Days later, the model is unavailable to everyone, including developers who paid to use it before the June 22 cutoff.
Anthropic proved there was strong demand for Fable, then had to remove it from the users most eager to pay for it. The model’s first week now sits at the center of a larger fight over frontier AI access, where government intervention can reach directly into a commercial AI product and have it pulled from the market.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。