


Enterprises have adopted Claude faster than they have the security guardrails for it. An Anthropic API key has become one of the most powerful credentials in the building. With it, Claude can reach sensitive data, run code, and act on a user's behalf. Yet most security programs still treat it as an afterthought, something to rotate eventually and worry about later.
That gap matters because the question every security team should be able to answer is simple: when someone uses Claude, can you tell whether the activity is legitimate or the first visible step of a compromise? Today, for most teams, the honest answer is no. Not because the data isn't there, but because the data on its own doesn't say enough.
The Anthropic Compliance API does its job well. It gives you a clean, granular record of what happened across your organization: conversations, files, projects, and audit and activity events. As a system of record, the specification is precise and impressively detailed.
But a record of what happened is not the same as an understanding of why. An anomalous event might be a legitimate power user performing legitimate work. The same event might be an attacker operating with stolen access. Looked at in isolation, those two stories produce the identical log line. You cannot tell them apart from the event alone, and an alert you cannot interpret is not a signal. It is noise. Overwhelmed security teams do not need more noise. They need to know which events are worth acting on.
Here is the part that gets missed: the context that resolves the ambiguity is not in the compliance feed. It is in the runtime activity on the same machine, in the moments right before and right after the event.
That is the foundation Sysdig has built for over the past decade.
Our integration correlates each Anthropic Compliance event with what was actually happening on the host, whether that host is a user's laptop, a workload, or a managed service. A compliance event stops being an isolated data point and becomes evidence, tied to real, deterministic runtime behavior on the same system.
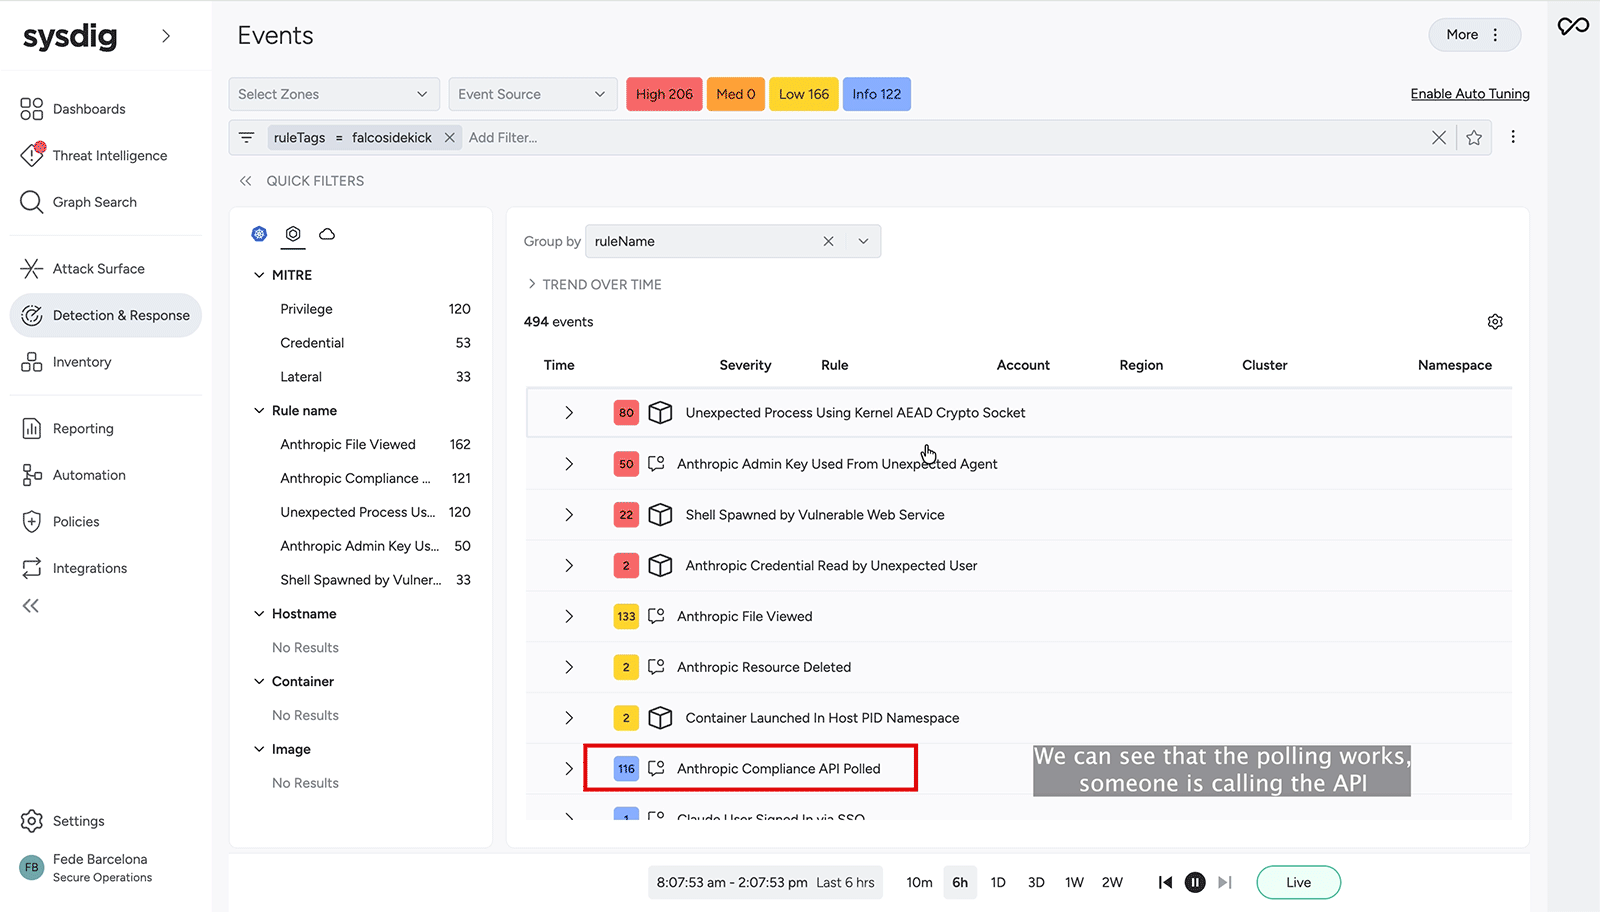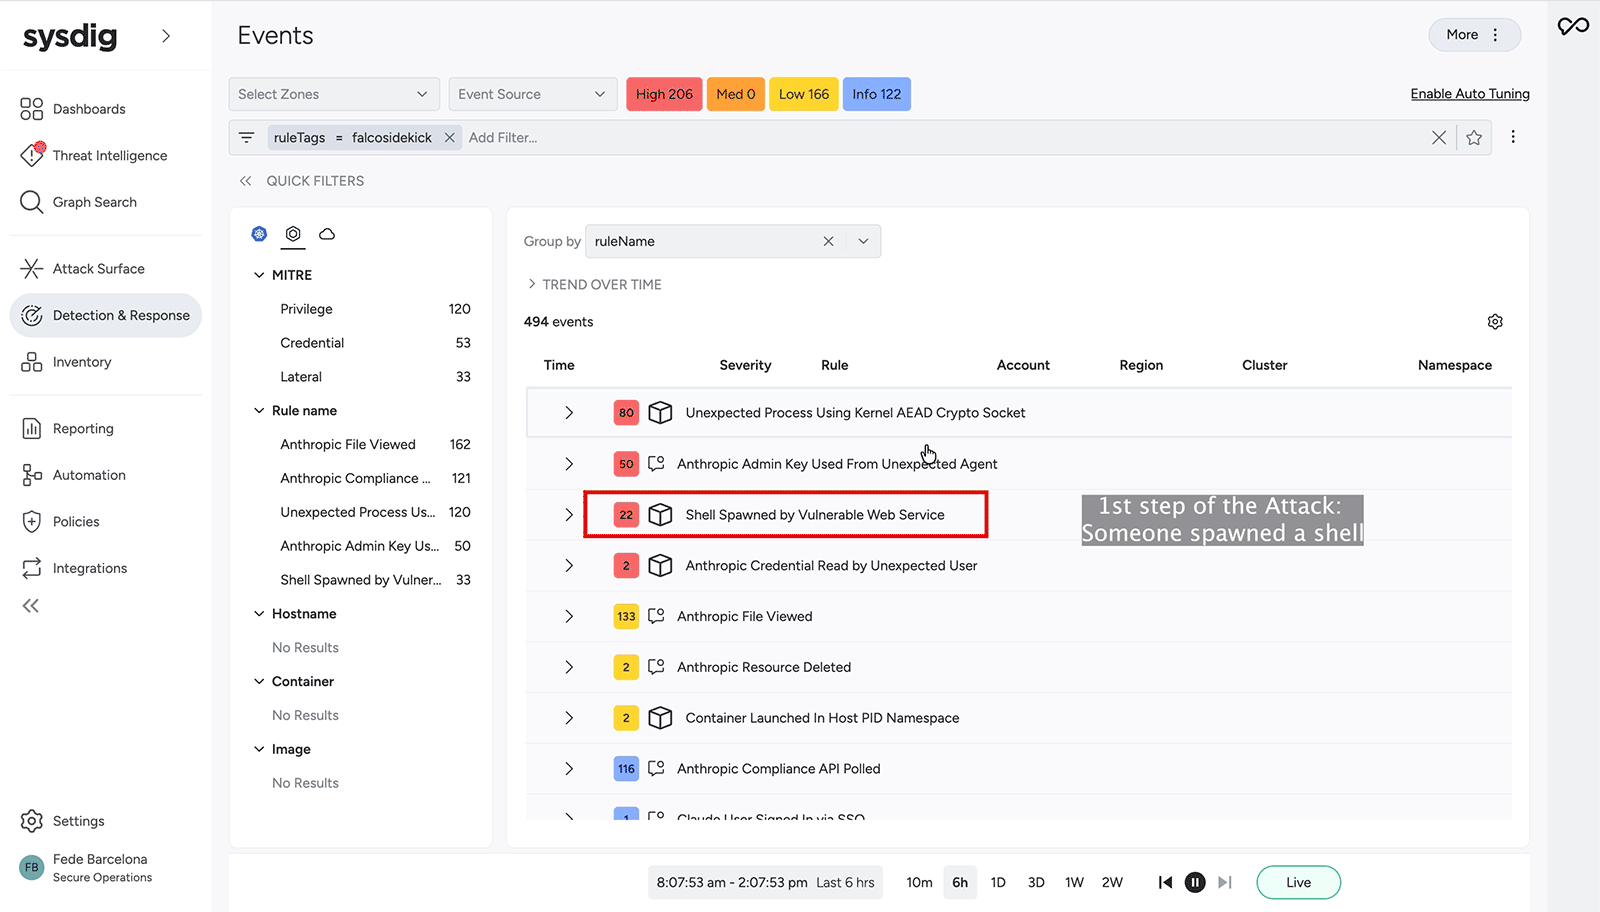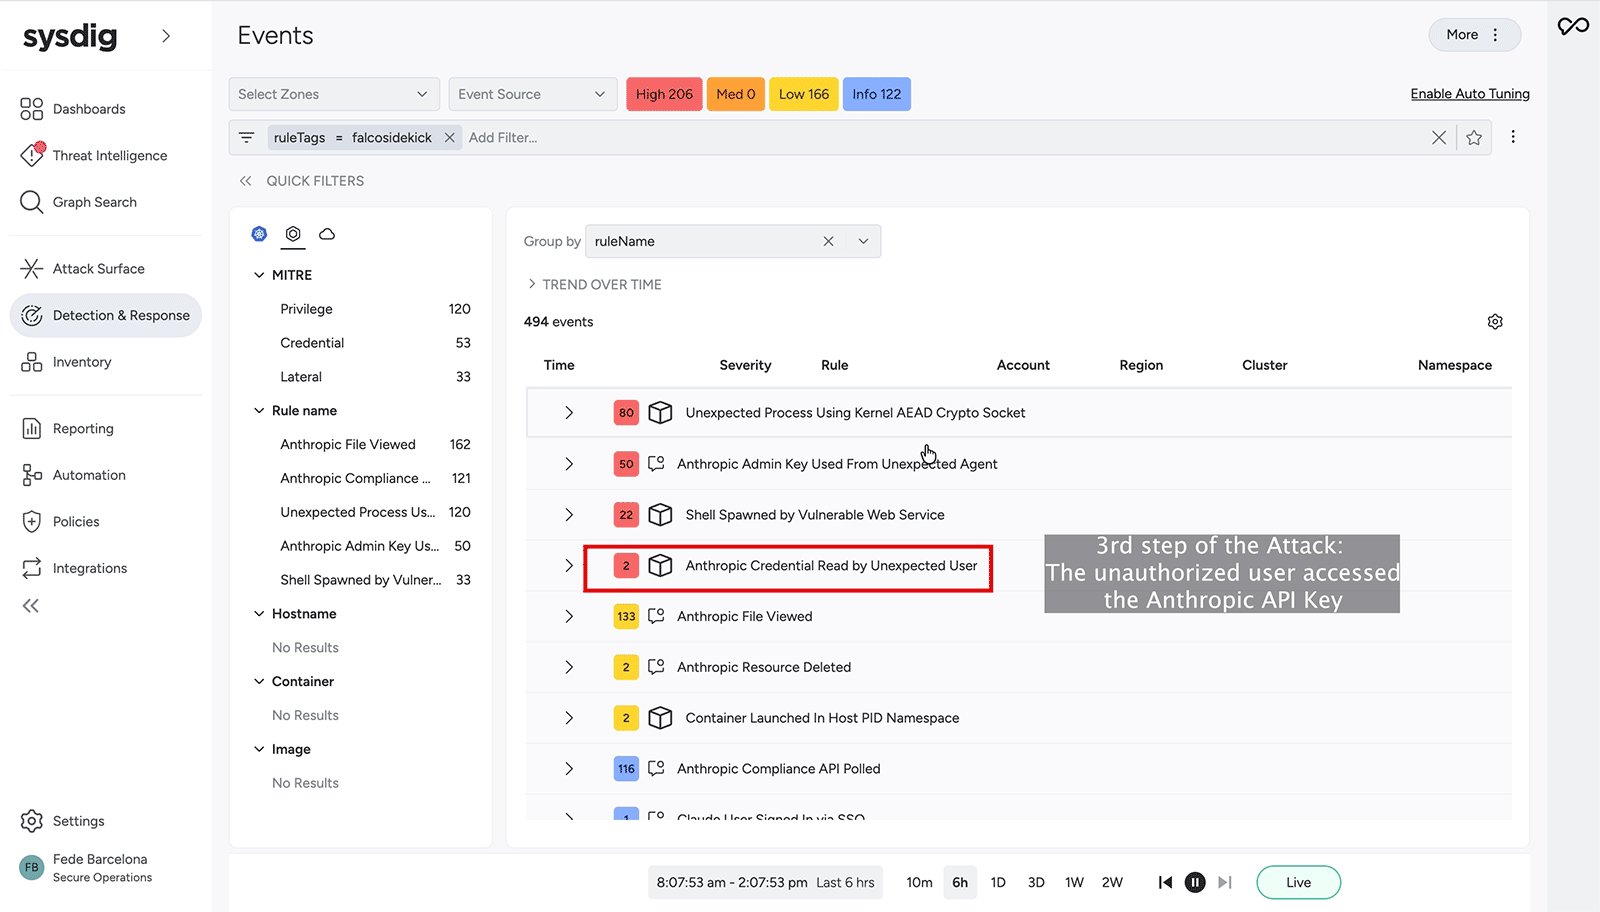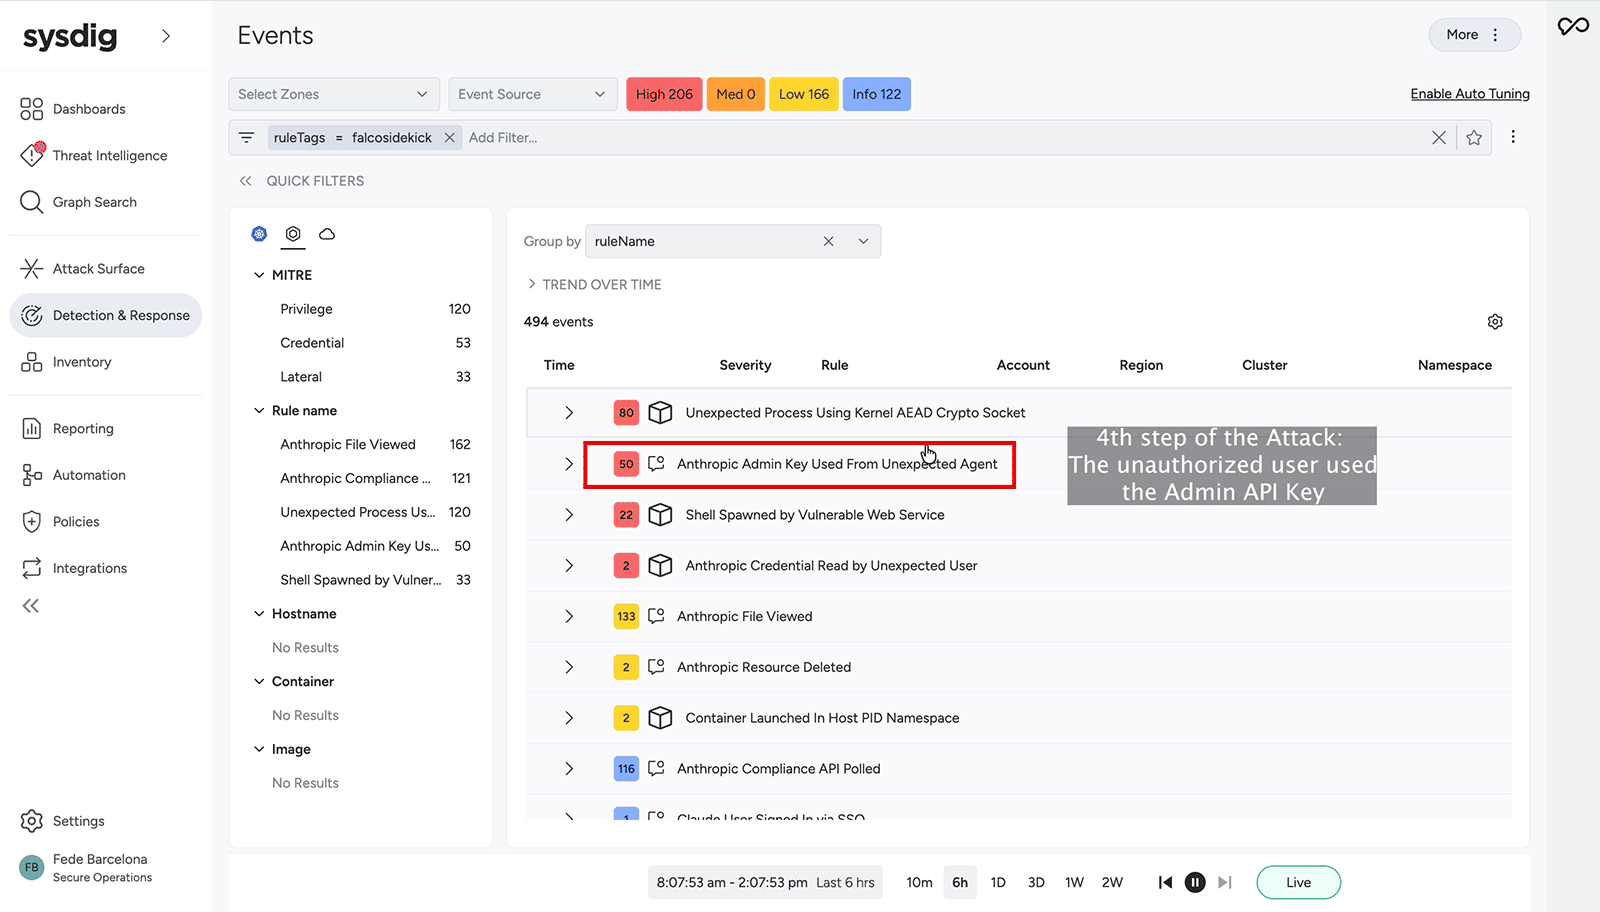
This is where the story usually changes. When you line up the compliance activity against the runtime timeline, you often find that the kill chain began well before anything appeared in the compliance log: a suspicious process, an unexpected network connection, a credential pulled from where it never should have been touched. The final API call is the part that was visible. The attack began earlier, and runtime context is what lets you see it. The result is the full attack story, not just the last frame.
This problem is about to get harder and faster.
Increasingly, the entity holding the Claude credential is not a person at a keyboard. It is an autonomous agent. Coding agents like Claude Code now operate across cloud and development environments at machine speed, which has two consequences for security teams. The volume of credential activity climbs sharply, and the window to respond collapses from days to minutes.
Human-driven triage cannot keep pace with that. By the time an analyst opens an isolated compliance alert, reconstructs the context by hand, and decides whether it matters, a machine-speed attacker is long gone.
This is one of the catalysts behind Sysdig's headless cloud security. When detection flows directly into automated, context-aware analysis and response, a correlated signal can be acted on immediately. AI agents get high-fidelity context from Sysdig's runtime intelligence via APIs and MCP rather than being locked behind a dashboard. The same runtime grounding that turns a compliance event into evidence is what lets an agent act on that evidence at the speed the threat demands.
That is the point worth holding onto. Correlation gives the alert its meaning. Acting on it at machine speed is what keeps the meaning useful.
You do not need a long checklist to get this right. You need three principles.
Treat the credential like the high-value secret it is. An Anthropic API key deserves the same scrutiny as any other powerful credential in your environment. Store it in a managed secret backed by a real secrets manager, never embedded in an image or hardcoded in a pipeline.
Never read a compliance event in isolation. A single event won’t tell you whether the activity is benign or malicious. Correlate it with runtime context from the same machine, and the ambiguity resolves itself.
Close the loop fast enough to matter. Context that arrives after the damage is done is a postmortem, not a defense. In an agentic world, response has to move at the speed of the attack.
The goal was never to generate more alerts about how people use Claude. The goal is to look at any single event and immediately know whether it is a person doing their job or an attacker using stolen access.
That is the shift this integration delivers: from an isolated alert to full runtime context, to machine-speed response. It is also what makes adopting enterprise AI something you can scale with confidence rather than cross your fingers and hope. The credential is new. The discipline is not. Watch it the way you watch everything else that matters, with the context of what is actually happening on the machine, and the noise turns back into signal.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。