







Securing large and complex cloud environments takes a lot of know-how and effort. Much has been written about the shortage of qualified professionals to fill open cybersecurity positions. What if AI can help fill the gap AND upskill existing staff to do more? This is the promise of modern solutions built on generative AI. Sysdig Sage, our AI cloud security analyst, delivers on the promise, empowering security staff of all skill levels to act with speed, confidence, and precision.
The traditional approach—relying on human triage, siloed tools, and disparate sources of information—can no longer keep up with the velocity and volume of cloud threats. That’s why AI is now being leveraged as a force multiplier for cloud security teams. Users are finding it an effective way to empower every analyst. AI is helping to cut through noise, speed up investigations, and focus on real risks.
By integrating AI throughout Sysdig’s cloud-native application protection platform (CNAPP), we’re helping cloud security teams tackle the unprecedented speed and sophistication of modern cloud attacks. With Sysdig Sage, users have AI assistance across the three primary security domains of CNAPP — cloud security posture management (CSPM), vulnerability management (VM), and cloud detection and response (CDR), bringing efficiency and precision to security operations.
Developed by Sysdig specifically for the speed and complexity of cloud-native environments, Sysdig Sage is a domain-specific cloud security expert designed to go beyond simple summarization. By employing generative AI with multi-step reasoning and deep contextual awareness, Sysdig Sage helps teams identify, investigate, and respond to threats in minutes.
Since its launch last year, we’ve expanded the capabilities of Sysdig Sage to assist across cloud security use cases. AI assistance helps you harden your environment and workloads to prevent security gaps. It also assists you with understanding security events in your cloud and how to respond. In the following sections, we’ll look at how Sysdig Sage helps you stay on top of cloud security threats.
Sysdig Sage’s AI-powered graph search enables teams to translate natural language queries into insights about their cloud assets, container workloads, and Kubernetes clusters. For example, you can simply ask, “Which workloads are running with critical vulnerabilities and public exposure?” Sysdig Sage generates precise SysQL queries in seconds. This eliminates the need for intricate query crafting and manual dashboard searches, surfacing key risk indicators in seconds.
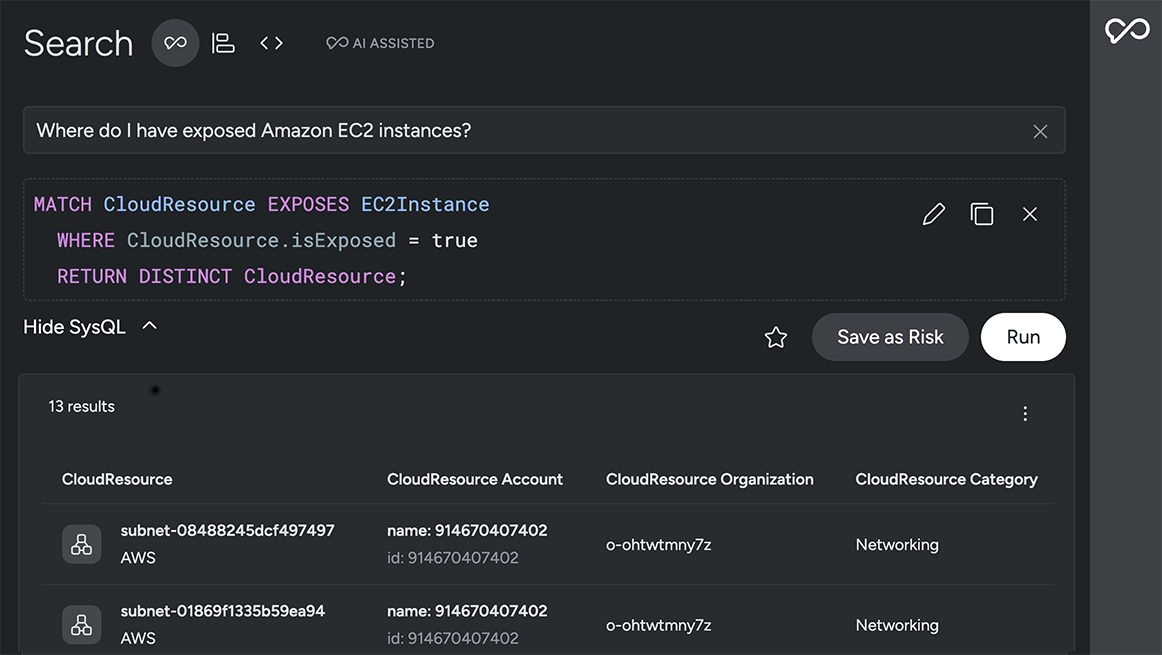
The ability to quickly slice and dice cloud info simplifies the proactive detection of risk and compliance issues. With Sysdig Sage, you can query our graph database for relevant cloud asset and risk details. Additionally, you can use the chat assistant to discuss the results, refine your query further as needed, and ask for remediation guidance.
Application security teams struggle with the sheer volume of known vulnerabilities across hosts and containers. Prioritizing critical vulnerabilities and exposures (CVEs) is a challenge if you don’t have the right risk context (see more about Sysdig vulnerability management here).
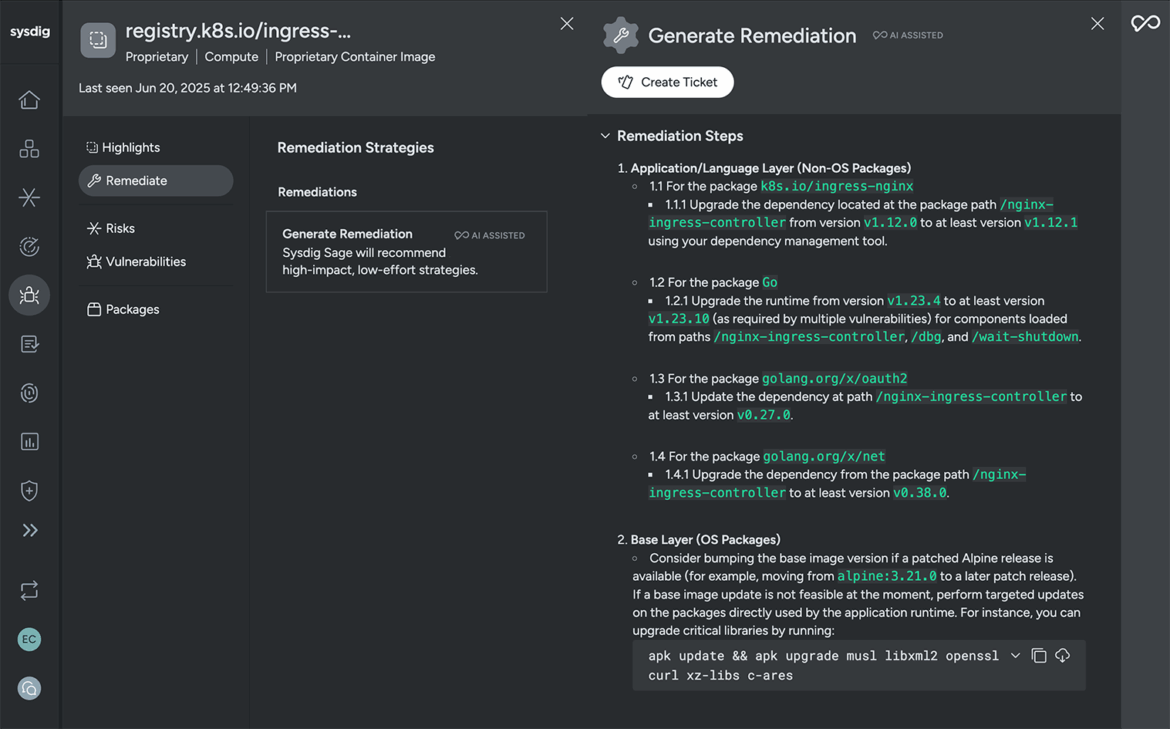
Developers don’t want to spend their time fixing CVEs, but they also know it’s key to avoiding potentially damaging security breaches. One of the issues developers and application security teams face is a lack of actionable remediation guidance. Without it, it can be arduous to figure out exactly what should be done to address a vulnerability without breaking the application.
Sysdig Sage employs generative AI to analyze live telemetry and vulnerability data. With a mouse click, it provides low-effort remediation recommendations in clear, step-by-step instructions. Using this info, developers can apply targeted, high-impact fixes without disrupting critical application dependencies. As a result, teams experience dramatically reduced remediation times, moving from weeks of vulnerability backlog to swift resolution in minutes.
Time is critical when dealing with runtime threats. Sysdig is renowned for its ability to detect and alert on active cloud events in real time, helping teams act fast to block threats. Our engine is built on open source Falco, which provides runtime security across hosts, containers, Kubernetes, and cloud environments. According to users, applying AI in this domain has enabled up to 76% faster response time for cloud security incidents.
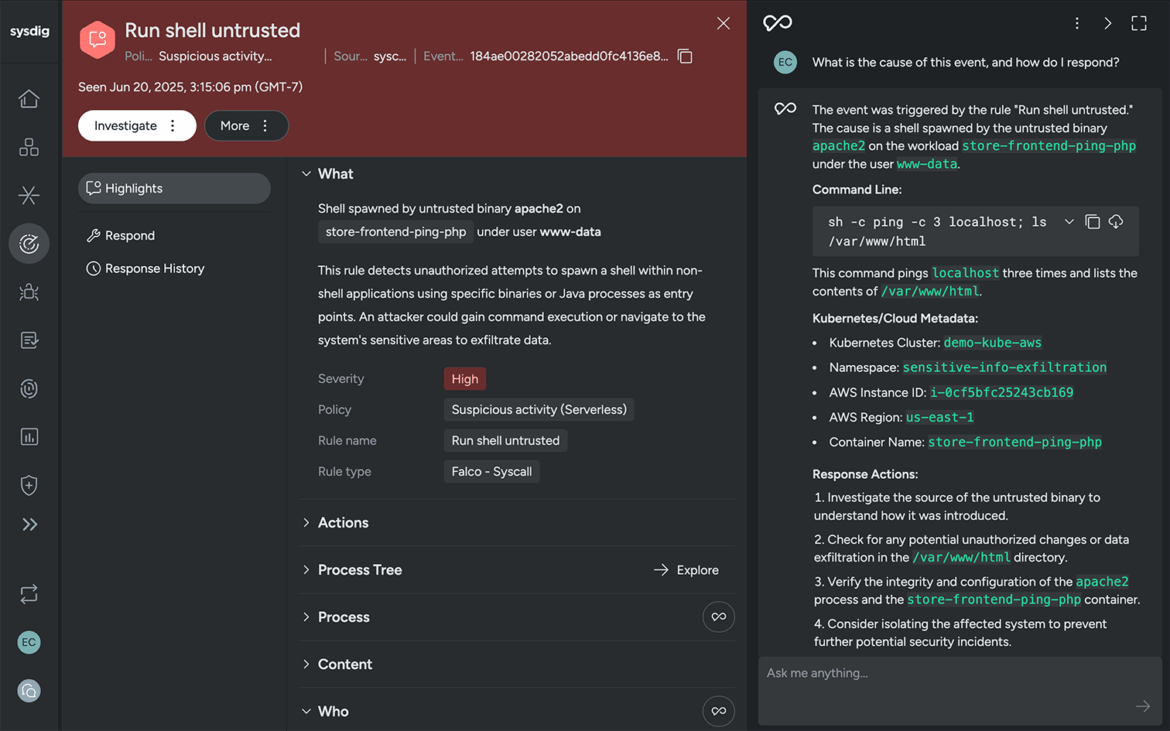
For CDR, AI contributes easy-to-understand descriptions and summaries of critical threats in your environment. This saves time by eliminating the need for external searches for information or relying on colleagues for help. Then, through a simple AI conversation, users gain more and more clarity. Sysdig Sage helps you uncover the “who, what, when, where, and how” of suspicious events and attacks.
A simple prompt such as “What is the cause of this event, and how do I respond?” yields a detailed, context-rich explanation of the threat and immediate, prescriptive actions for mitigation. Security teams no longer need to hop across various screens or sift through event logs. By guiding defenders through attack paths and recommended responses, Sysdig Sage significantly reduces mean-time-to-response (MTTR) and helps prevent threats from escalating into breaches.
Sysdig Sage isn’t just another tool — it’s your always-on security teammate. You can look at it as a way to boost the capabilities of your existing team without adding headcount. It’s like having a domain-specific expert who deeply understands security, as well as the context of your cloud. Anytime you need it, you can ask for insights and targeted recommendations.
Ultimately, Sysdig Sage redefines cloud security by making security searchable, explainable, and actionable. Leveraging advanced AI, you’re equipped to address threats rapidly and empowered to confidently and securely innovate, knowing your skilled AI teammate is ready to help you achieve your goals.
Experience the power of Sysdig Sage — AI-powered CNAPP security simplified, accelerated, and smarter than ever. To see it in action, try the Sysdig Sage product tour!
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。