


Our 2026 Cloud-Native Security and Usage Report confirms that security teams are taking vulnerabilities seriously, with a 75% YoY reduction in exploitable in-use vulnerabilities. However, it also revealed a concerning trend: Vulnerabilities are growing, and teams are struggle to keep up.
Are we reaching the limit of human scale? And, if so, what can security teams do to catch up?
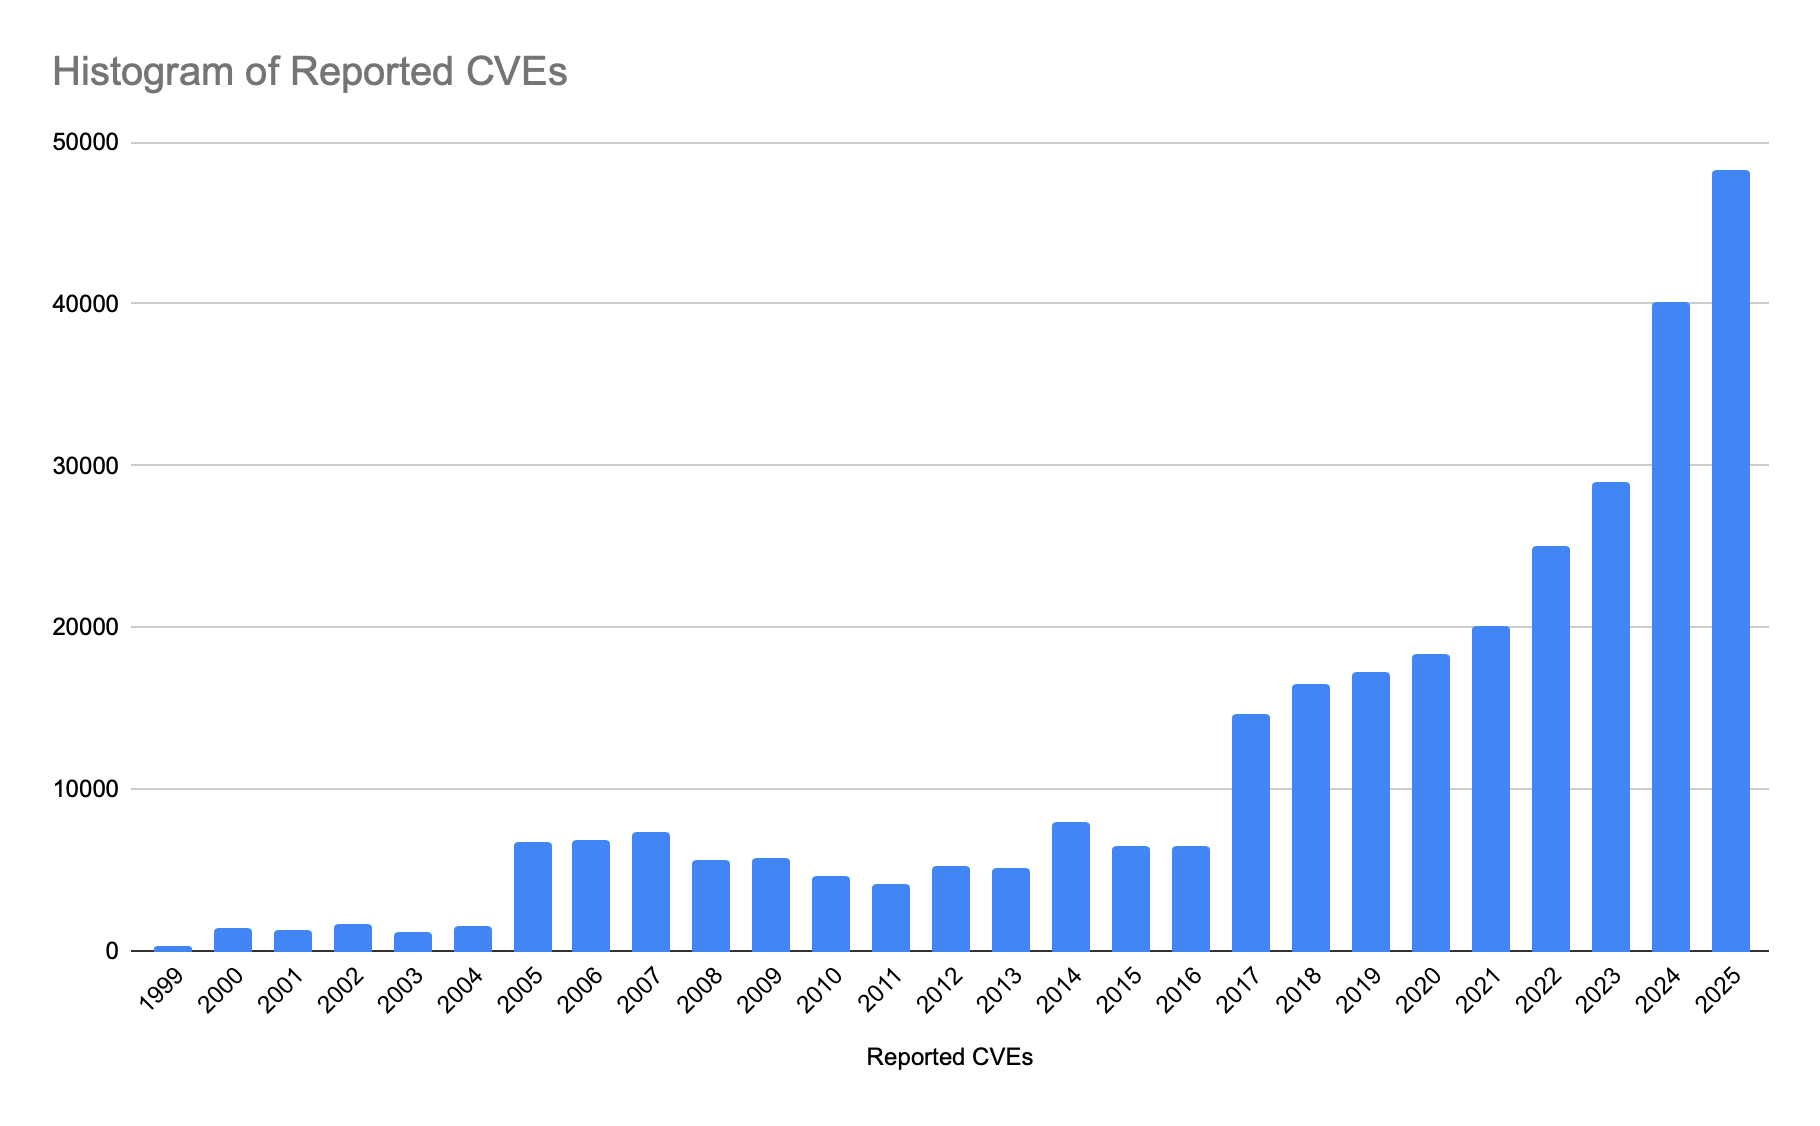
The MITRE Corporation tracks reported vulnerabilities on cve.org. The trend is scary, showing an exponential growth in recent years:
To help our users navigate this issue, we introduced Risk Spotlight in 2022. This tool assists Sysdig users in identifying vulnerabilities that are in use, have an existing exploit, and have a fix available. A 75% reduction in this kind of vulnerability year-over-year among our users demonstrates how effective Risk Spotlight is.
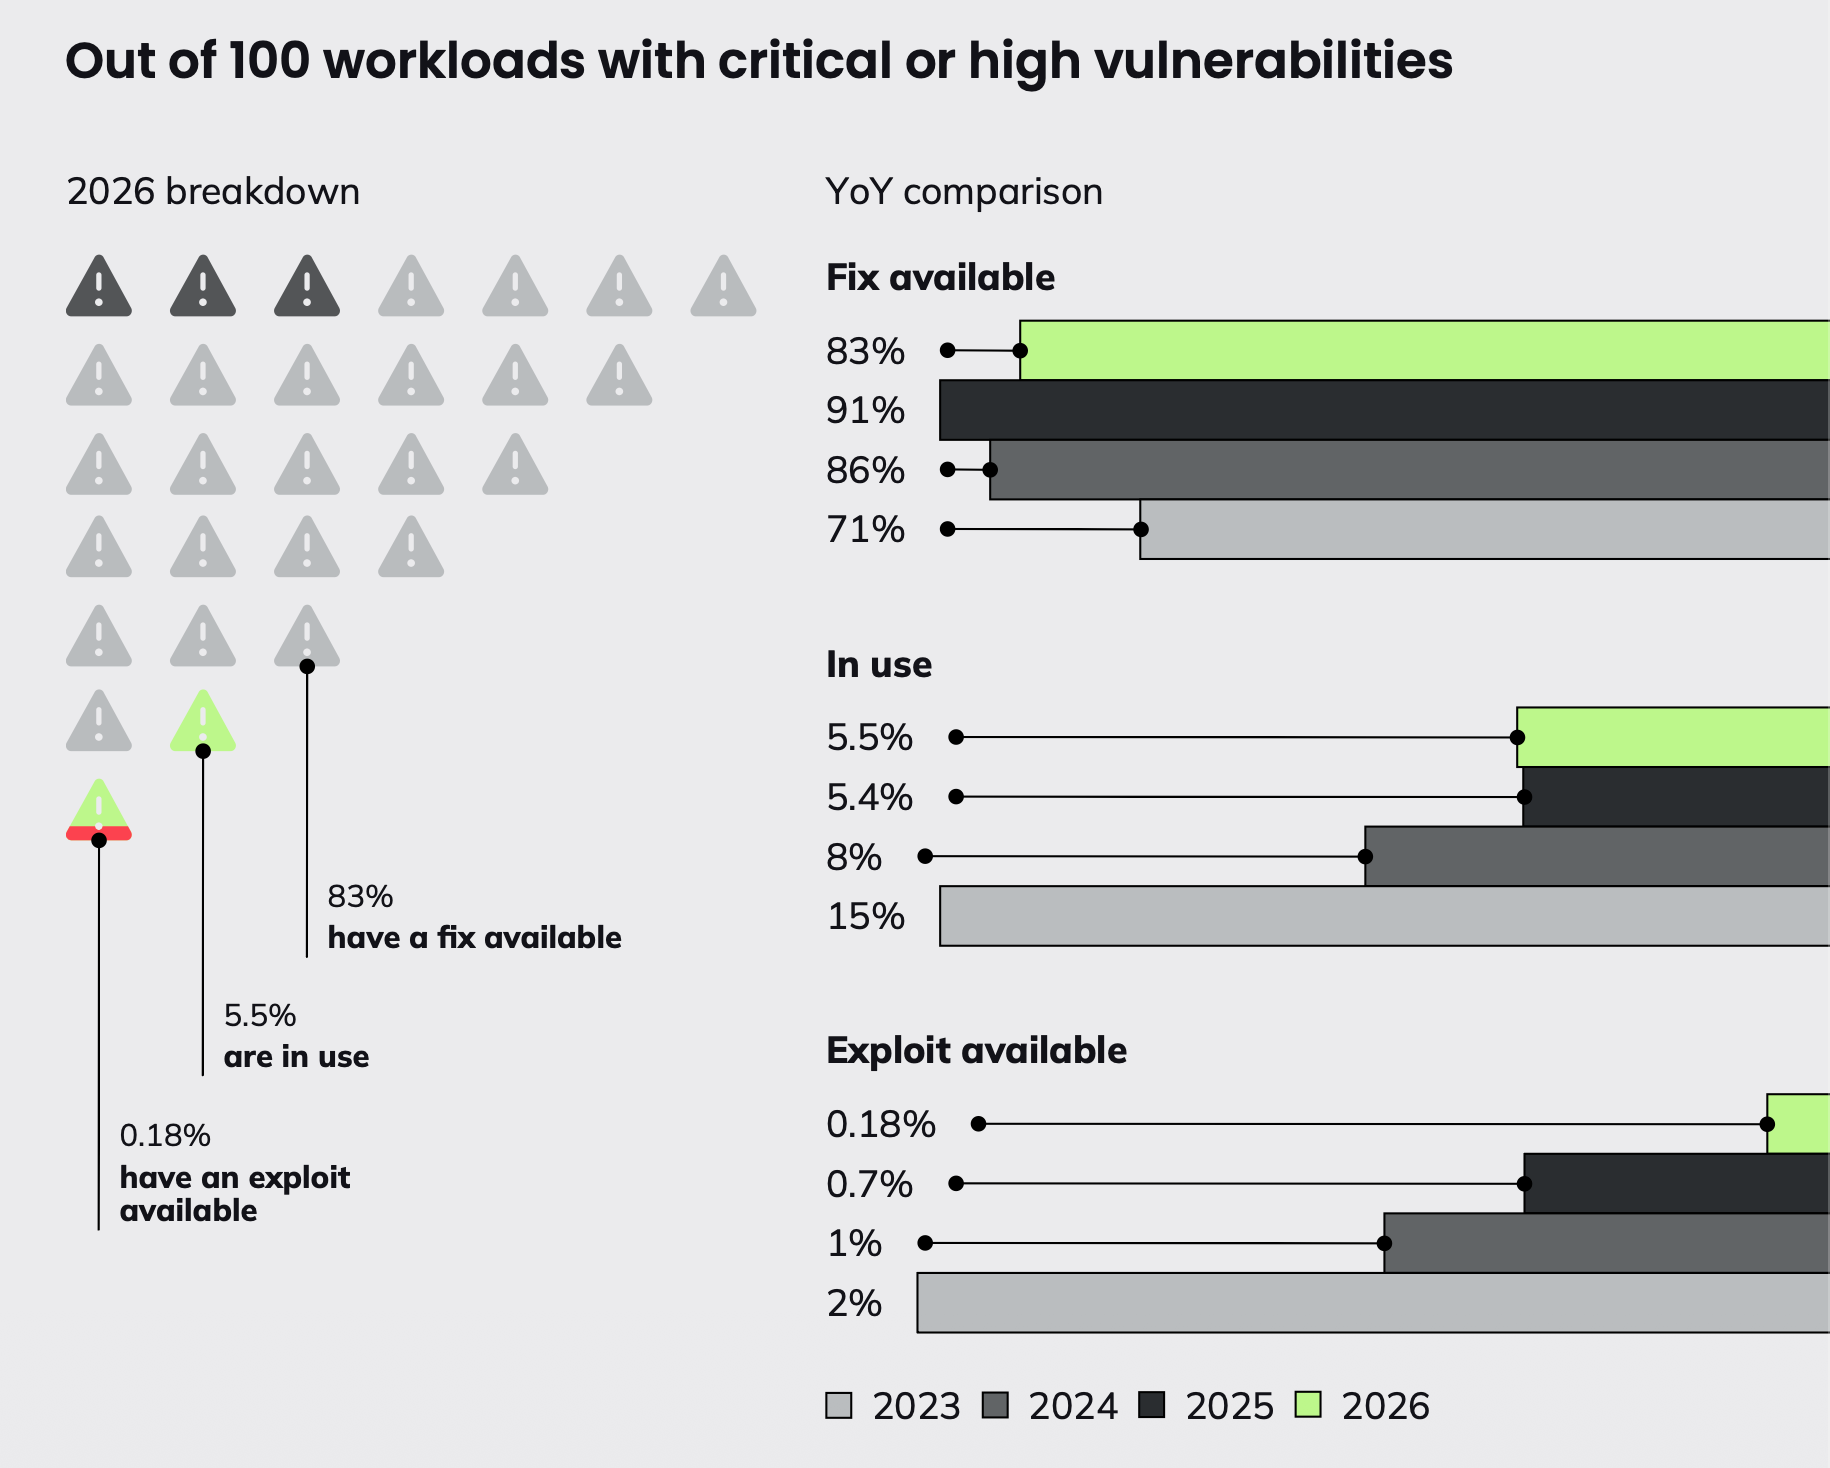
This metric also highlights the impact that security tools have when they align with the user’s needs.
However, in-use vulnerabilities, including those without a known exploit, have plateaued at 5% since last year.
This shows that while teams are doing great work prioritizing, they struggle to address the overall exponential increase in vulnerabilities. As a result, there is a huge gap with the in-use vulnerabilities without known exploits.
What is new this year is that the absence of a known exploit no longer guarantees security. An exploit can be crafted and weaponized within a few hours with the use of AI, as the Sysdig Threat Research Team (TRT) and Project Glasswing are proving over the last few weeks.
Dealing with vulnerabilities running in production is becoming increasingly important as the window between vulnerability disclosure and exploit weaponization collapses. According to VulnCheck:
And now, we’ve seen how AI is expanding to cybersecurity. On the one hand, Anthropic’s Project Glasswing is an AI capable of detecting software vulnerabilities, deemed too risky for the general public. On the other hand, we’ve recently seen how an AI-assisted cloud intrusion achieves admin access in 8 minutes.
We expect that, as attackers continue to use AI in their operations, vulnerability weaponization will approach near‑real time. With this scenario in mind, focusing solely on vulnerabilities being actively exploited is no longer enough, and runtime security takes on greater importance as a last line of defense.
Slowly, but steadily, organizations have realized the value in stateful detections and also shifted to automated response actions for modern threats. According to our 2026 Cloud-Native Security and Usage Report, the adoption of automated response is surging:
However, to cope with the exponential growth of vulnerabilities and break through the 5% ceiling, organizations need a paradigm shift in their tools. More and more, AI is becoming not only the natural next step in automation, but economically and operationally justified.
We believe that autonomous remediation, driven by agentic AI and executed within human‑driven guardrails, is how organizations will keep pace with shrinking exploit timelines.
You may shiver at the thought of granting power over your infrastructure to an AI; it’s understandable. However, the key to success is in the details.
We’ve been here before. A few years ago, automating tasks in critical areas was also a controversial topic. What has changed since then to explain the widespread adoption of automated responses we detected in our report?
A silent transformation in the industry has taken place over the last few years. Engineering has adapted to put automation first. Practices that sounded peregrine, like CI/CD, Infrastructure as code, and DevOps, are now the norm. At the same time, tools, policies, and processes have matured to keep automations within safe margins.
As a result, suspicious processes are now killed automatically, which was something unthinkable years ago.
Organizations adopting agentic AI must undergo a similar transformation to succeed. Agents are a lot like kids; in the absence of guardrails, they will introduce operational risk at some point. These guardrails become the new focus of humans in the agentic era, in particular:
Only when humans govern and define these guardrails can they advance with machine‑speed security.
The cybersecurity ecosystem is moving faster than human speed. In the cat-and-mouse game that cybersecurity is, it's no longer enough to focus on some vulnerabilities, as automating runtime response with agentic AI is becoming a requirement.
If organizations want to succeed in this change of paradigm, they must go through a transformation to ensure they are in control of their agent’s guardrails.
Get more insights on our 2026 Cloud-Native Security and Usage Report.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。