


Security teams are integrating foundation models into operational workflows for alert triage, investigation, remediation. For these agents to be effective, they need structured access to security intelligence such as runtime detections, identity analysis, vulnerability context, and data security findings.
But for many teams hoping to take advantage of the speed and scale of agentic security, there’s a data-sized gap in their workflows. The gap isn’t in the availability of data; it’s making that data callable from an agentic workflow. That’s where headless cloud security that leverages a model context protocol (MCP) server comes into play.
The Sysdig MCP server, available on the AWS Marketplace, enables security teams leveraging agentic AI to use Sysdig data for a wide range of use cases with workflows that align to their specific needs.
For this blog post the focus will be on Sysdig’s data security findings, cloud-native data security posture management (DSPM) capabilities delivered by Sysdig through an integration with Bedrock Data.
Data security findings discovers and classifies financial data, personally identifiable information (PII), and personal health information (PHI) to help security teams understand, investigate, and remediate risks such as exposure.
The core AI stack runs entirely inside AWS, meaning model inference, tool orchestration, and agent memory all stay within your account boundary.
Here is how the components come together:
Before walking through the demo scenarios, here is what this environment requires.
To connect your AWS environment to Sysdig, we use a specific skill that packages complex security workflows into actions that any AI agent can execute. Skills offer pre-built expertise without the friction of legacy onboarding workflows.
Instead of manually configuring cloud accounts, IAM roles, and scanning policies, you can invoke a Skill and it handles the end-to-end setup.
For this demo, we use the Onboarding skill to connect the target AWS account to Sysdig Secure. The agent calls the Skill, which provisions the necessary cloud infrastructure and enables DSPM scanning – all from a single conversational prompt.
A Sysdig Secure account with Data Security Findings enabled for your AWS storage (S3 and RDS) is required to scan, classify , and map a risk profile such as public exposure or IAM, attack paths for the stored data.
We use three AgentCore resource types:
The Gateway is what makes this setup practical. It gives the agent a single, stable URL to reach Sysdig’s tools, while AgentCore handles networking, scaling, and IAM trust between the Runtime and the client.
Any client that supports the MCP can serve as the local surface.
For this blog post, we use OpenCode as the single interface for the entire workflow: it handles your questions, routes tool calls to the AgentCore Gateway, and runs LLM inference on Amazon Bedrock.
With the stack deployed and the Sysdig MCP server connected, we can now run some prompts against live data to return traceable, tool-backed answers.
The scenario: Your security team is kicking off a data security review. Before prioritizing remediation, you need an accurate picture of what sensitive data exists across your cloud environment and how much of it is publicly accessible right now.
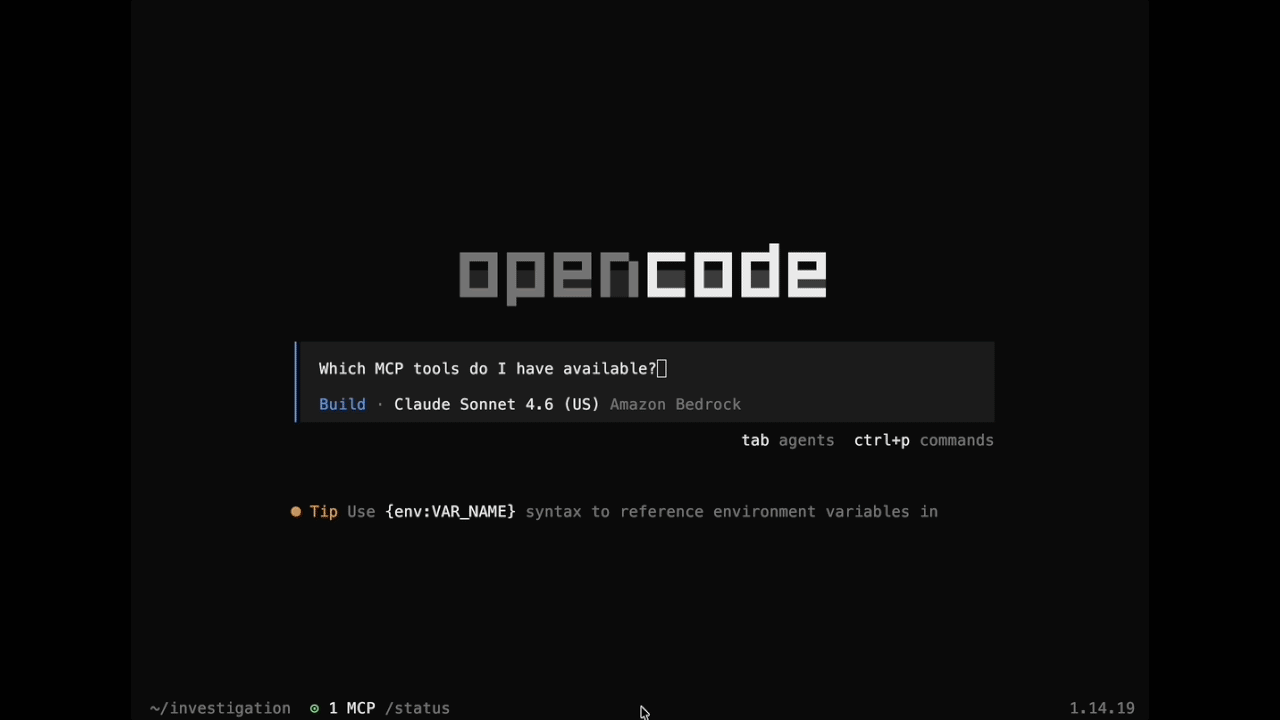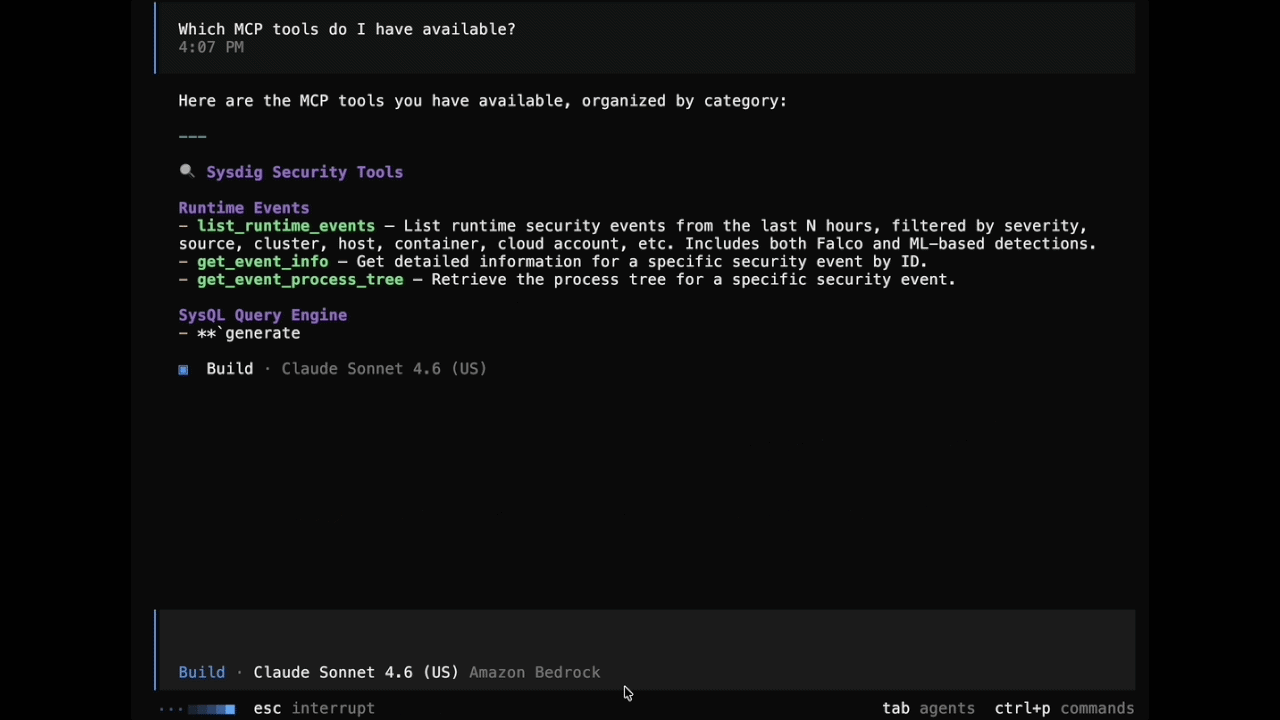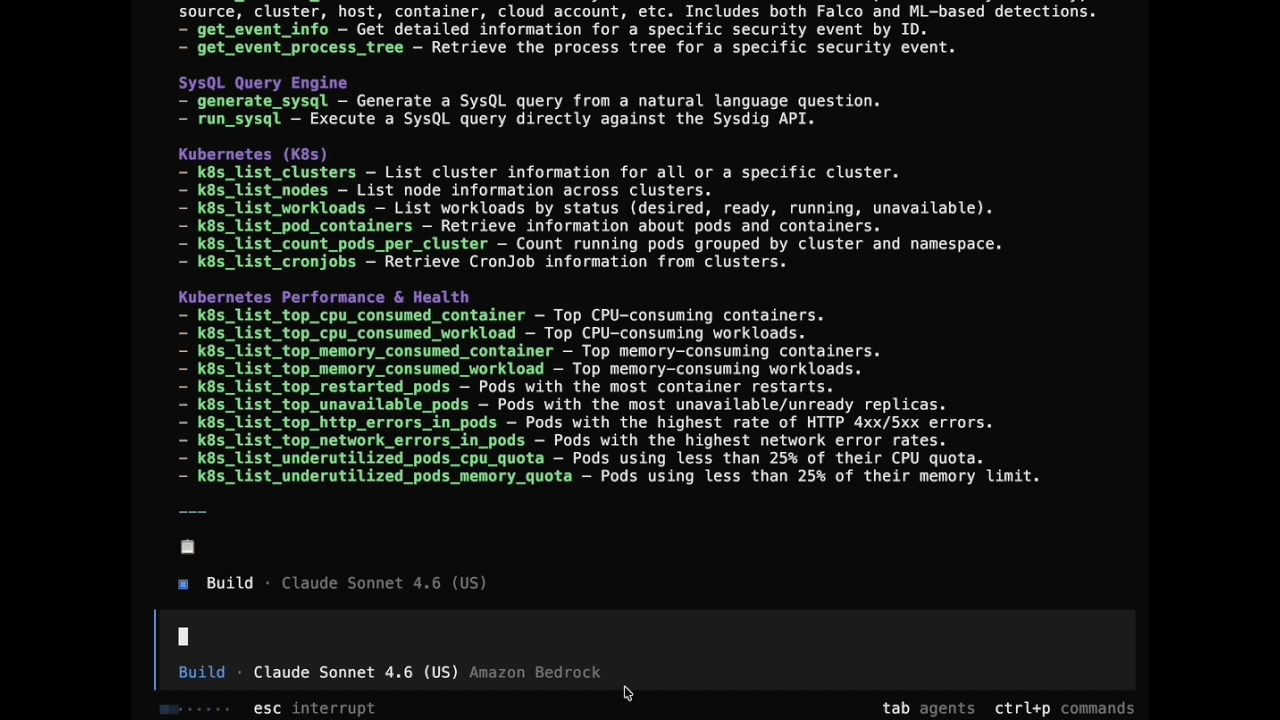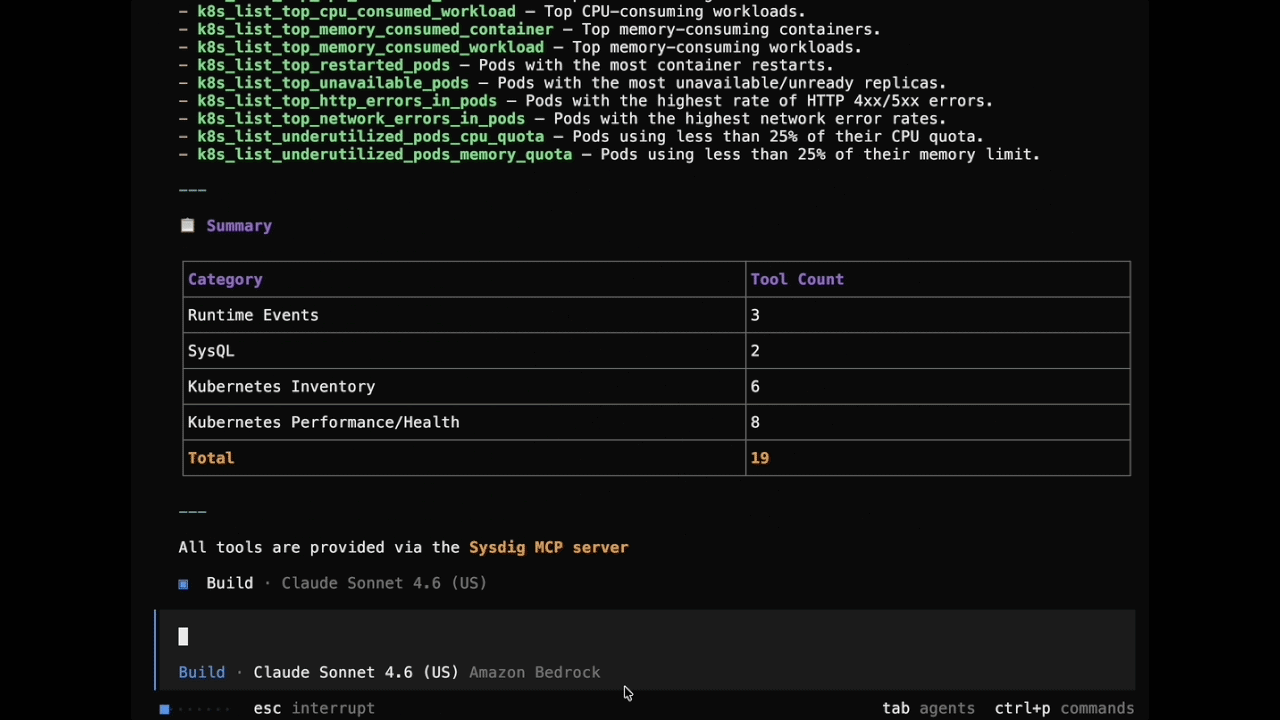
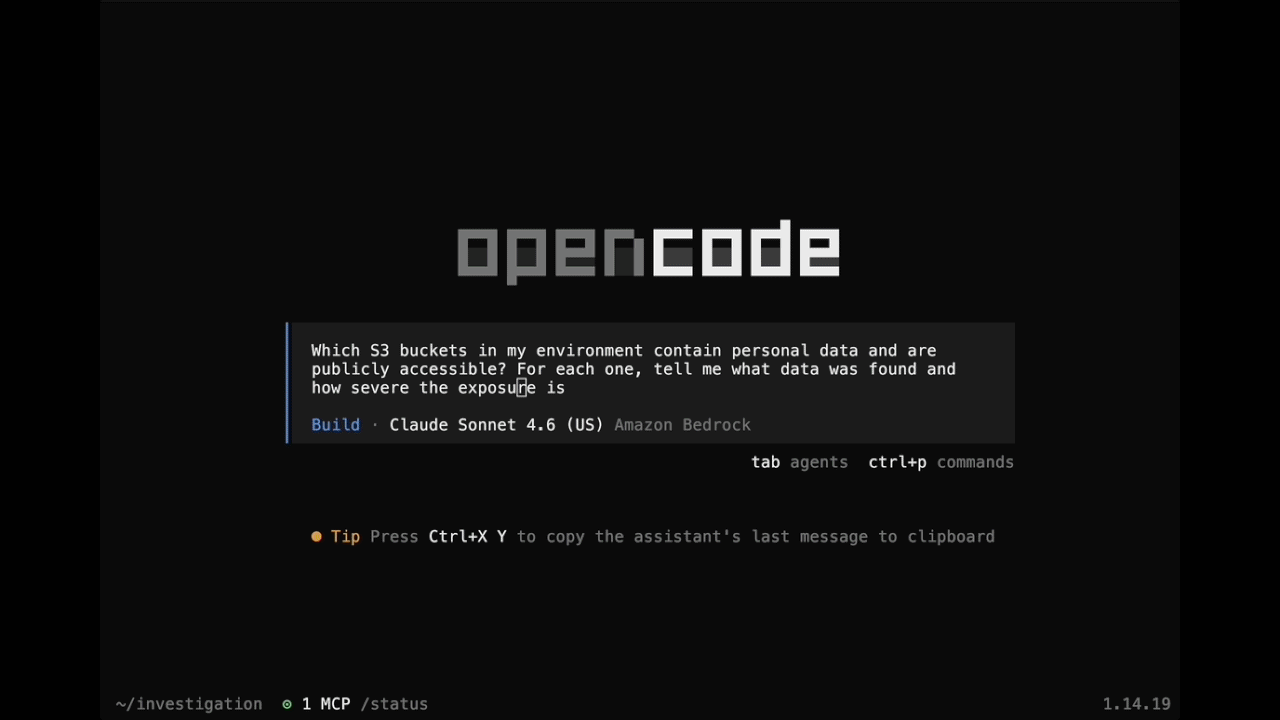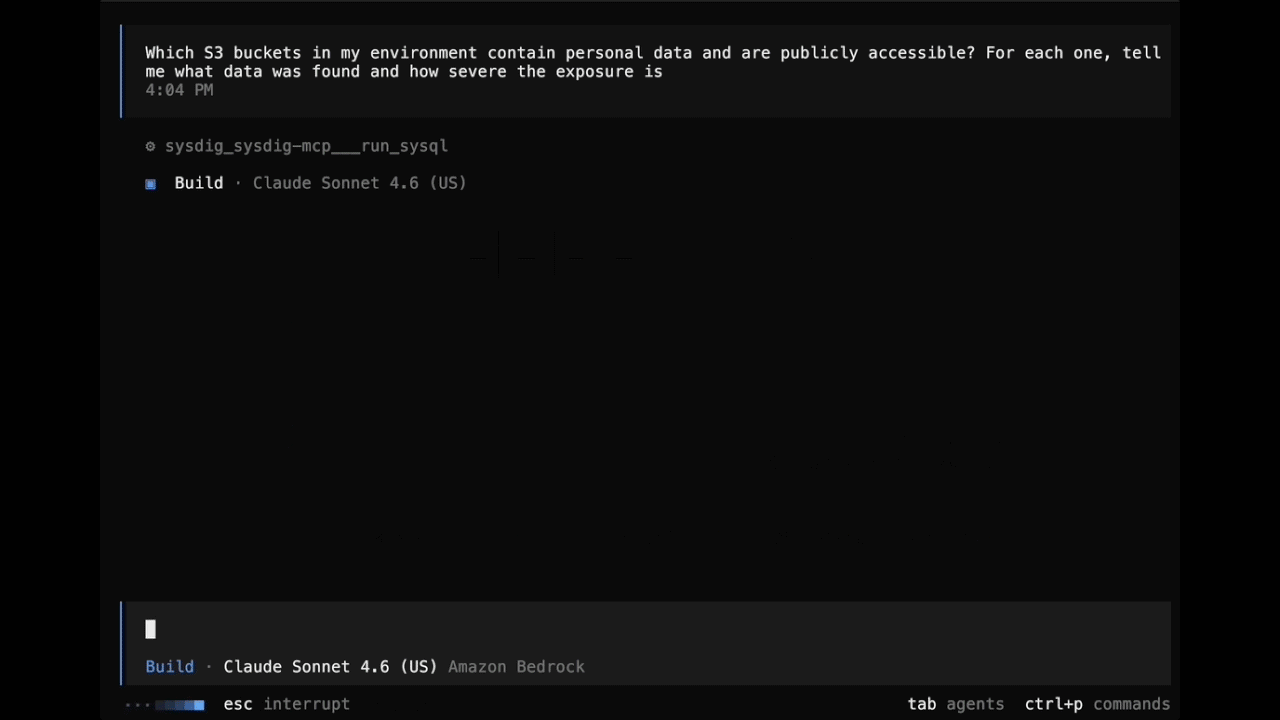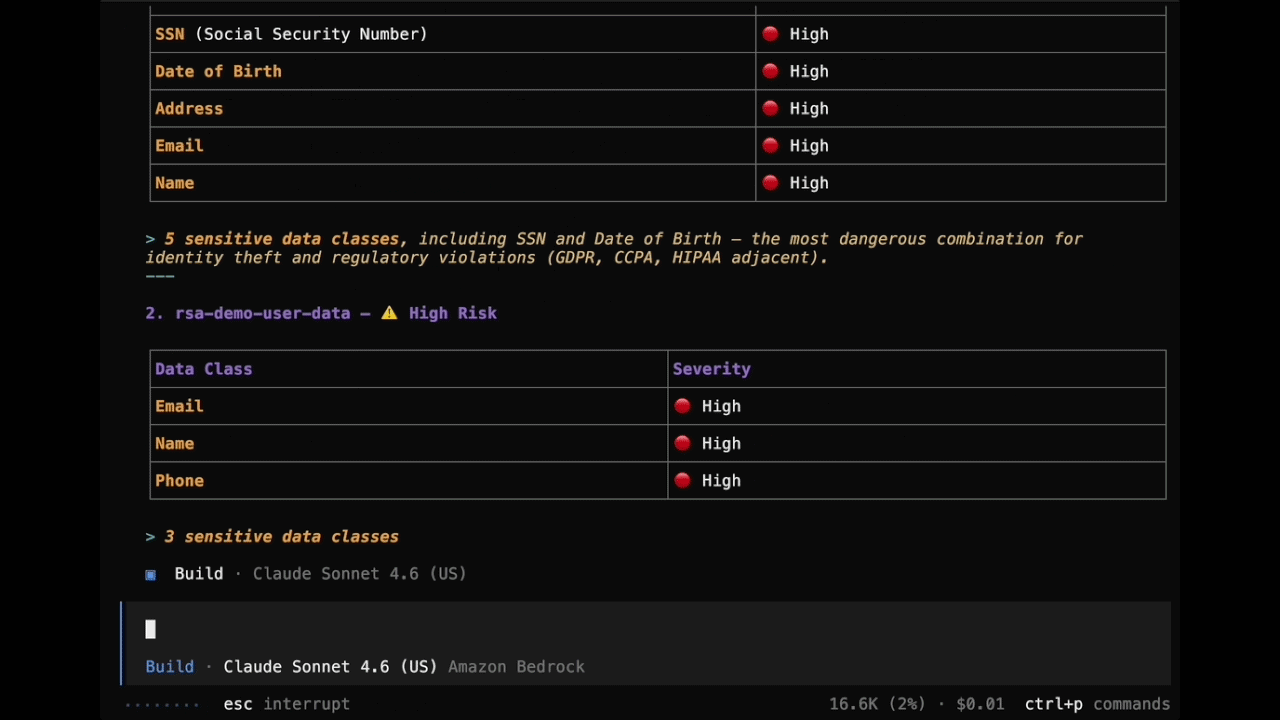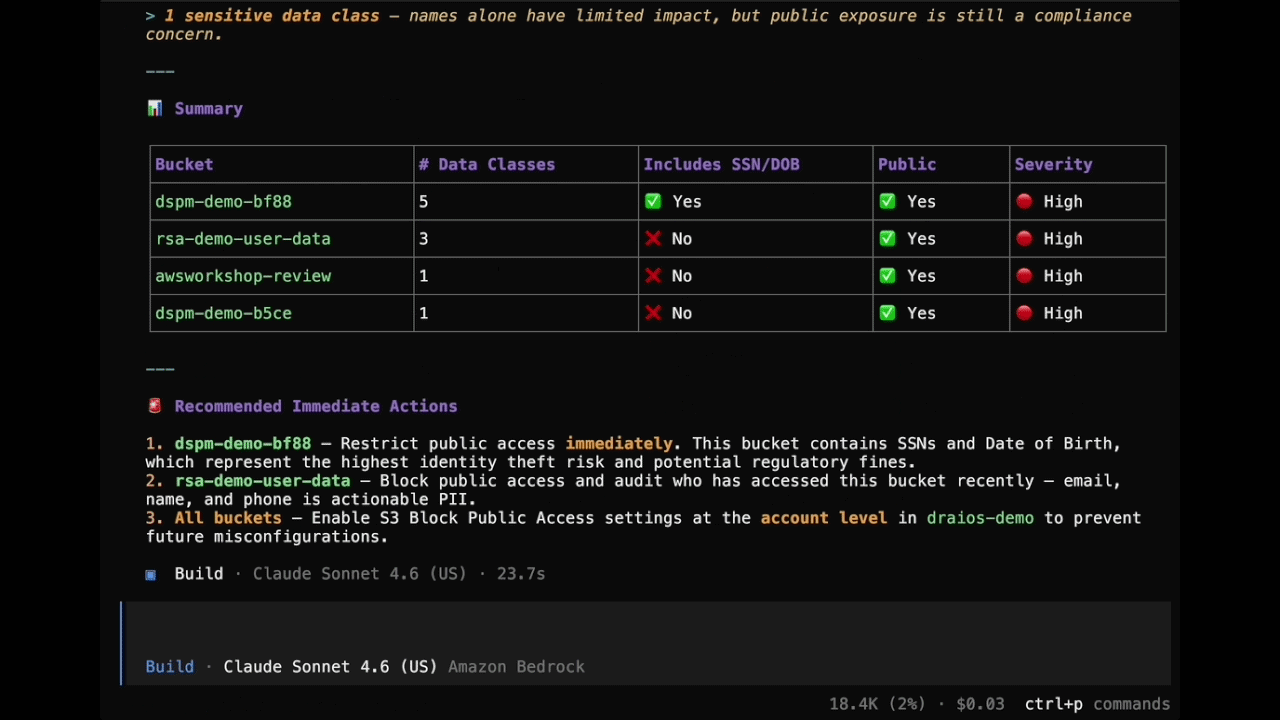
The agent queries Sysdig's DSPM graph directly to provide information about S3 buckets that are both publicly exposed and contain classified sensitive data, filtered to the Personal data category. It returns a structured inventory that includes bucket names, owning accounts, exposure status, the specific data classes detected, and the severity of each finding.
Remediation is out of scope for this scenario, but the same conversational surface extends naturally into action via an AWS MCP server, CLI-driven skills, or whatever fits your workflow.
The scenario: Your compliance team needs interpretation of the data security findings provided by Sysdig Secure. Which findings map to which regulations? Where are the non-obvious risks hiding? Which combinations of data classes could make a single bucket a top-priority target for adversaries?
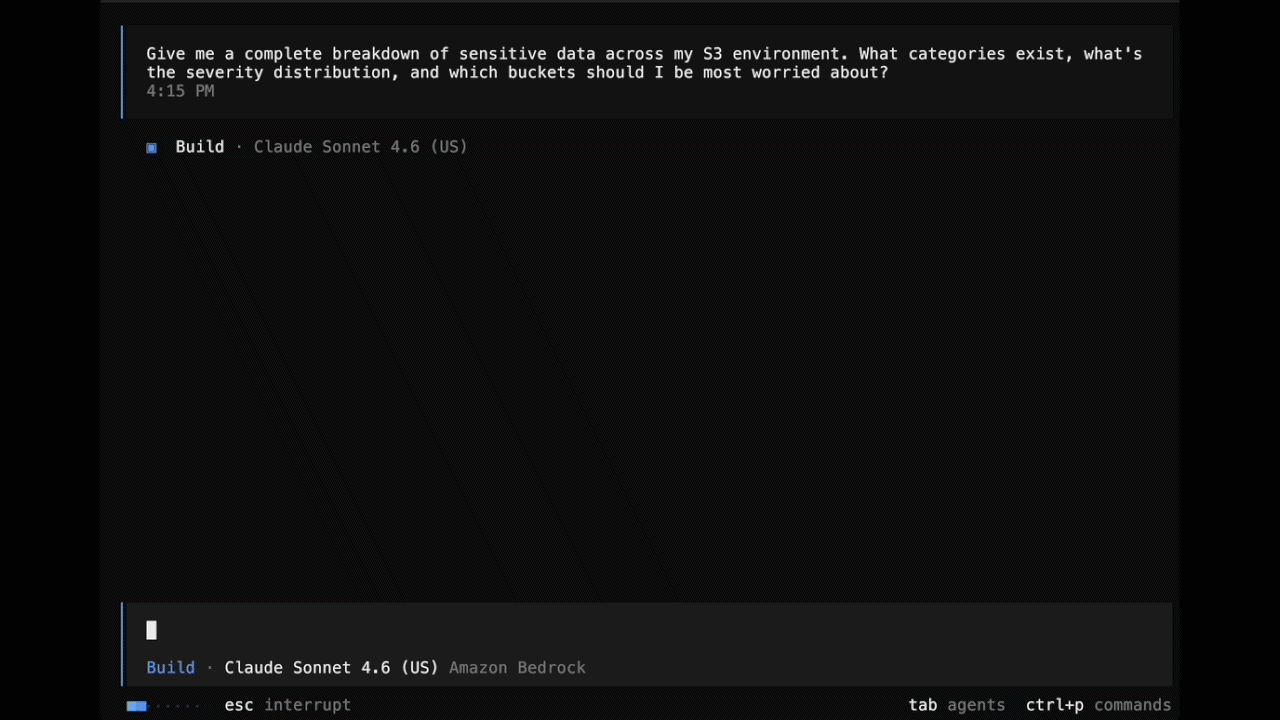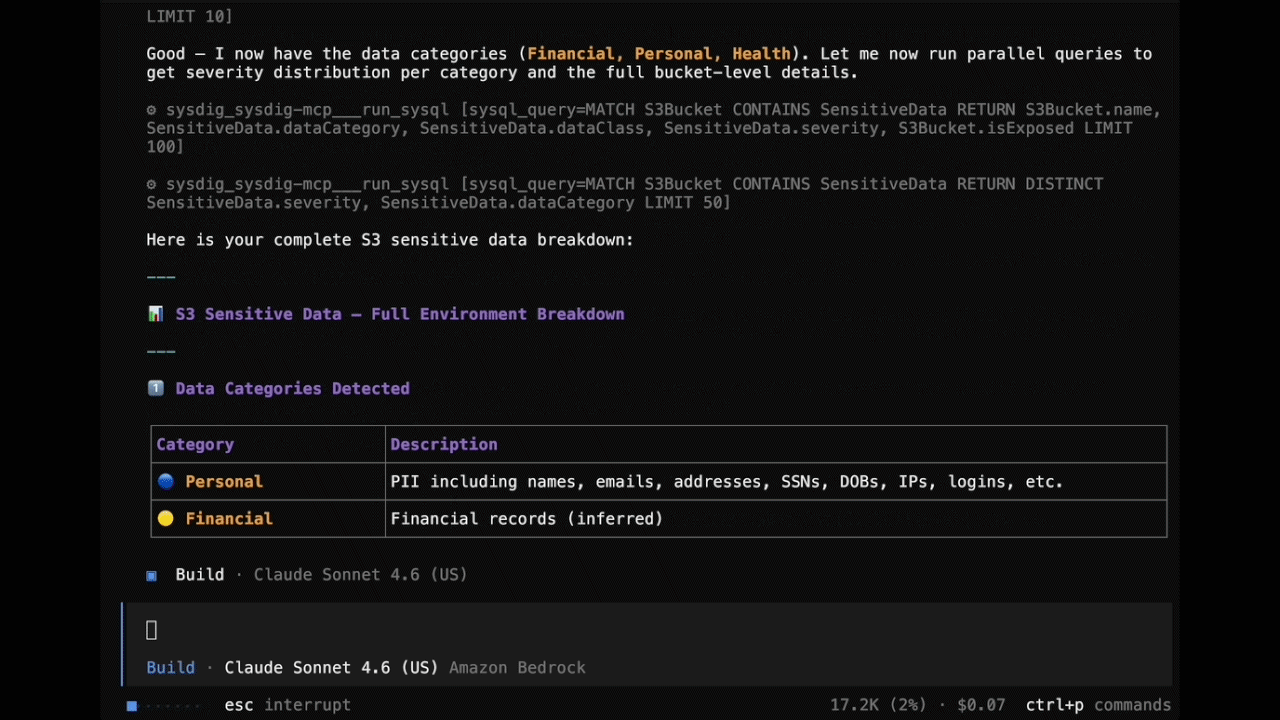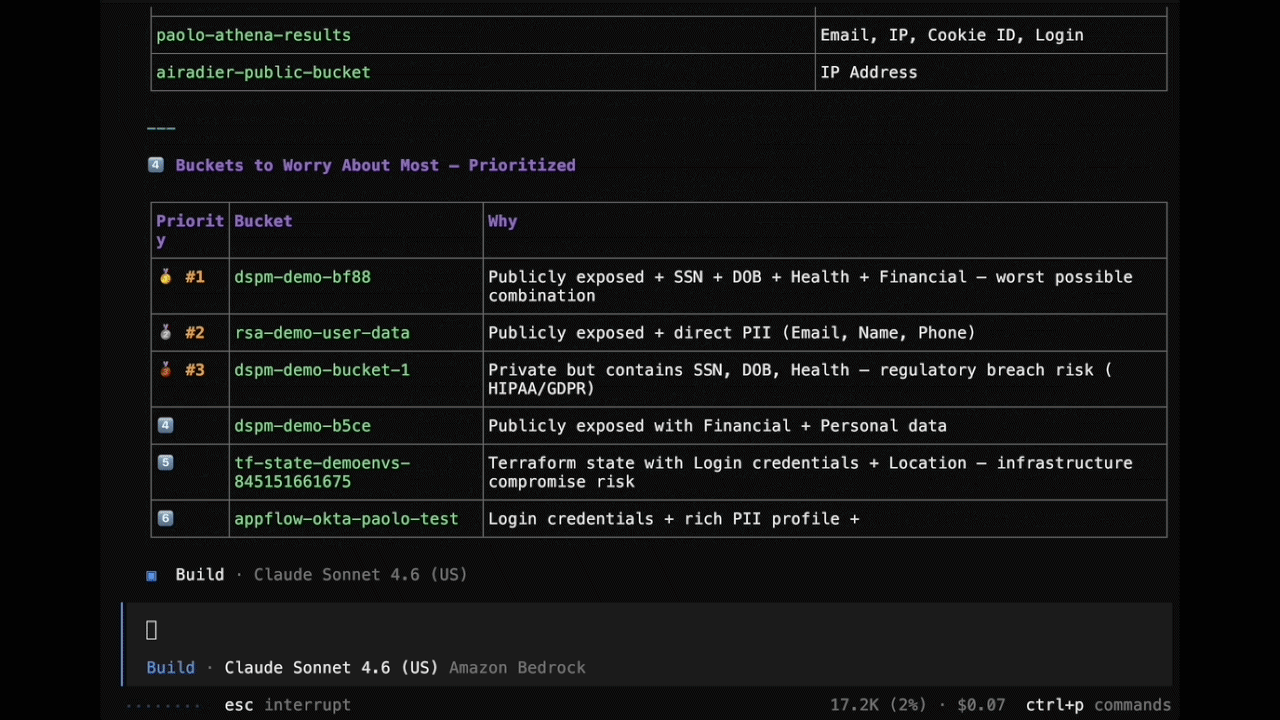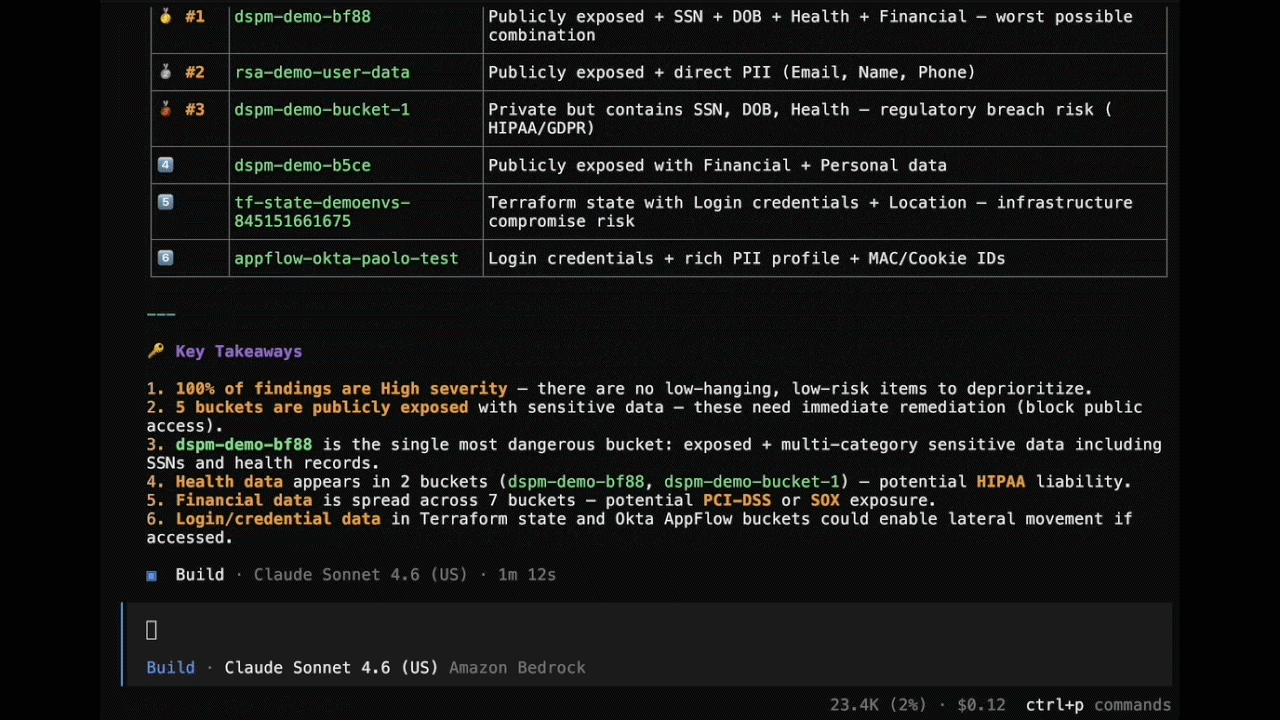
The agent runs parallel QL queries against Sysdig Secure data, including distinct data categories, severity distribution, and full bucket-level detail. The agent then reasons over the combined output.
It maps data classes to regulatory frameworks such as HIPAA for health data and PCI DSS/SOX for financial data. Using this information, the agent identifies non-obvious risks such as login credentials in Terraform state as a lateral-movement enabler, and then prioritizes these risks using several factors that provide context beyond severity alone.
The result is a stacked risk ranking, led by a publicly exposed bucket containing PII like social security numbers and dates of birth, as well as health and financial data. The list of risks also includes a bucket that isn't publicly exposed but still ranks top-three on regulatory breach risk alone.
Identifying the risk is half the problem – you still need to close the gap. When the Sysdig MCP is paired with an AWS CLI MCP server on Amazon Bedrock, the same conversational workflow extends from investigation into remediation.
In this example, an agent identifies an overly permissive IAM role granting access to sensitive S3 buckets. With this information, the agent can draft a scoped-down IAM policy that removes the unnecessary permissions:
Restrict the access. Apply a deny policy on the EKS-Node-PaymentsRole for the three sensitive buckets you identified.
The investigation log containing every tool call, every finding, and every policy change remains a traceable record for your incident documentation.
Each scenario above requires traversing multiple security domains like storage configuration, IAM access paths, runtime detections, and data sensitivity in a single investigation. The Sysdig MCP server exposes each of these as discrete, queryable tools.
An agent can chain these disparate signals in whatever order the investigation demands, and because each step maps to a specific tool call, the result is a traceable chain of evidence, not a hallucinated summary. This powerful capability enables:
Headless cloud security powered by skills and MCP servers marks a major transition for organizations. Security teams can evolve to being orchestrators rather than operators. The DSPM scenarios in the post are a starting point.
Ultimately, how you choose to use headless cloud security will be up to you.
To learn more about Sysdig headless cloud security, sign up for our newsletter to get the latest agent skills, educational content, and practical guidance.
When you’re ready to see headless cloud security for yourself, request a demo.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。