







This week bore witness to some interesting events and milestones as Anthropic announced the availability of Claude Fable 5, a descendant of their Mythos Preview model, and Microsoft published their largest Patch Tuesday in history with over 200 vulnerabilities. The two are not unrelated.
But let’s be clear about what was released because the coverage of Andropic’s new model is unfortunately prone to misunderstandings and misstatements. Anthropic did not release Mythos Preview as a publicly available model. That model still only remains available to the original Glasswing initiative companies and a second cohort of around 150 additional organizations who can now access Claude Mythos 5, which is largely identical to Claude Fable 5 but with some of the safeguards denuded.
What was released was a model of similar capabilities, but one which has been crafted in such a way as to route any cybersecurity prompts and discussions to an Opus 4.8 model in order to make it “safe for general usage.” This means that it is pointless to benchmark Fable 5 for cybersecurity capabilities given this routing behavior. We already know how Opus 4.8 performs when searching for vulnerabilities in code. Queries into how to make bioweapons are also met with a lesser model which is the compromise that Anthropic seems to have reached when deciding how to continue to ride the wave of attention and concern that Mythos Preview created in April.
For a select few, their first interactions with Mythos Preview go back to the end of March during RSAC Conference in San Francisco. I myself have not had access to the model, but I have had the pleasure of meeting with several people who *did* spend time scanning and probing their software repositories to learn what surfaces. The truth of the matter seems to sit somewhere in between a Chicken Little response that the sky is falling and a nothingburger (with an impressive marketing impact for a pre-IPO company that amazingly does not provide much depth of transparency in what they are doing with their work, despite lovely blog posts that continue to espouse the tautology that their latest model is the most impressive thing since sliced bread).
At Aikido our self-securing software and autonomous pentesting journey has led us to the understanding that you definitely do not require Mythos Preview (or Fable 5 for that matter) to do great work securing your software and finding vulnerabilities, IDORs (Insecure Direct Object References) and business logic flaws that have been sitting undiscovered (and sometimes for years). In a recent pentest one of our clients performed, their JWTs were present but entirely irrelevant and unused in the authentication of API calls.
"Full fathom five thy father lies”
By William Shakespeare
(a song from the Tempest)
Full fathom five thy father lies;
Of his bones are coral made;
Those are pearls that were his eyes:
Nothing of him that doth fade,
But doth suffer a sea-change
Into something rich and strange.
Sea-nymphs hourly ring his knell:
Ding-dong.
Hark! now I hear them,—ding-dong, bell.
In thinking about what to share in this blog post, I keep coming back to this: everyone is still trying to shove Mythos into the “AI hacker” box because that was the first frame they heard. Anchoring bias is a hell of a drug. Mythos was not designed for security vulnerability discovery or hacking, but once a narrative gets its shoes on, it starts sprinting around the room, knocking over lamps. The actual story of building resilient infrastructure by securing software is more boring, more useful, and therefore harder to market. It is about understanding where systems are brittle, where operations are incoherent, and where security teams are drowning in everything except the one clean CVE headline that makes a conference slide look heroic.
Vulnerability discovery is maybe 20% of the issue set that needs to be fixed. The other 80% is not CVE-related at all: misconfigurations, exposed services, stale permissions, ghost assets, broken identity edges, duct-taped SaaS workflows, and all the weird little sins that accumulate because organizations are made of humans and procurement cycles. CVEs, as a practical prioritization primitive, are kind of dead in the water anyway. The same can also be said of the CISA KEV catalog. They still matter, but the fetishization is embarrassing. A colleague recently joked about a CVSS of “11,” in the Spinal Tap sense, and that is about right: we have turned severity scoring into theater while the real blast radius lives in the places nobody wanted to inventory.
The other myth that needs to die is that zero-days were somehow supply constrained. They were not. Adding 20,000 more vulnerabilities does not magically create 20,000 buyers. Demand for new vulns is fairly constant, perhaps on the order of 30 per month according to research from Resecurity, because buyers have budgets, operational constraints, targeting requirements, and, occasionally, adult supervision. The market does not suddenly become infinite because Claude Fable 5 or Mythos can shake more bugs out of the tree. You can flood the bazaar with shiny knives, but if the people buying knives only need a few very specific ones, the rest become inventory, noise, or LinkedIn thought leadership.
Which means the likely future is not “AI unleashes the apocalypse by discovering more bugs.” The more likely future is that tokens get spent on defensive scans, remediation workflows, exposure management, and boring-but-profitable hygiene. Tokens of Mythos and Fable 5 will not power millions of threat actor scans and attacks. Threat actors are cheap bastards and lazy, which is why social engineering will continue to be their favorite way to print money. Why burn compute and operational risk on exotic exploit chains when you can still get someone to approve an invoice, reset MFA, or click the shiny thing? With the Glasswing initiative, Mythos and Fable 5, the economic gravity points toward defense, triage, and cleanup. Not because attackers have become noble, but because crime, like enterprise software, follows the path of least resistance.
So maybe that is the actual Glasswing story: not the birth of some flawless machine predator, but a sea-change in how we understand the wreckage already beneath us. “Full fathom five thy father lies,” Shakespeare wrote, and that feels right for the CVE era. The old body of vulnerability management is down there somewhere, its bones made coral, its eyes turned pearls, still recognizable if you squint, but no longer alive in the way people keep pretending it is. Nothing of it has simply faded. It has transformed into something rich and strange: exposure, identity, configuration, workflow, incentive, and the messy economics of what attackers actually bother to do. We are so focused on thinking that infosec is a technology problem that we have lost sight of the real elements that we need to contend with: the who and the why for attackers, threat actors, nation states and bored teenagers like Shiny Hunters and TeamPCP. Infosec is a people problem at heart.
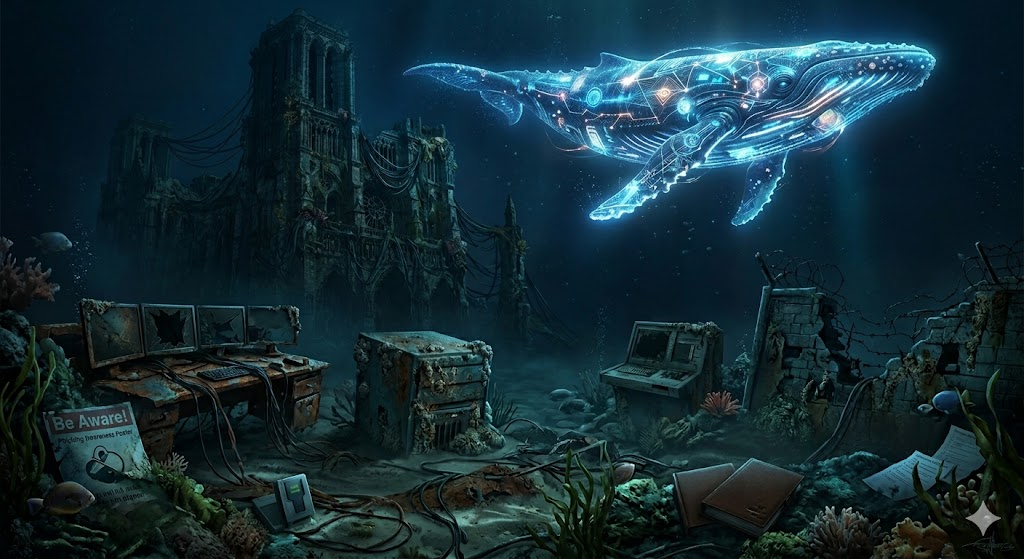
The bell is tolling for a simpler story: the one where more vuln discovery automatically means more hacking. Ding-dong. The richer and stranger version is that defenders may finally have a machine fast enough to map the ocean floor: the misconfigurations, the abandoned assets, the stale permissions, the non-CVE monsters quietly eating the ship from below.
And that is where I think the tokens go. Not into some cinematic zero-day arms race, but into the unglamorous defensive work that security teams have needed all along. The sea-nymphs can ring the knell for the old myths. The future is not less strange, but it may be more honest.
Oh, and don’t bother asking about what happened to Fable 1, 2, 3 and 4. They are likely relegated to the digital basement of Anthropic, sitting in cyber formaldehyde as specimens of imperfect LLM DNA that will never see the light of day.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。