



Our malware detection pipelines recently lit up on a small cluster of packages on npm that looked... familiar.
Packages like json-bigint-extend, jsonfx, and jsonfb were mimicking the popular json-bigint library: same functionality, an identical README file, and even an author name uncomfortably close to the original maintainer.
Most of the time, this pattern indicates common supply-chain attacks, such as typosquatting and dependency confusion, designed to compromise systems and exfiltrate secrets. But this one felt different almost immediately.
It was not trying to hit everyone. It was trying to hit something.
At first glance, json-bigint-extend behaves exactly like the legitimate json-bigint library: it exports the familiar parse/stringify functions used to support large integers in JSON. In fact, most developers and organizations wouldn’t notice anything unusual. This payload is specifically engineered to stay quiet and only trigger when it detects it is running inside a specific target environment, by checking the value of a specific environment variable called SERVICE_NAME.
Once it detects it is in the right environment, it installs two backdoors:
First, it installs a targeted Express middleware, wired specifically into a payment route (/v1/pay/purchase-goods). This middleware is designed to dynamically execute additional code fetched from an endpoint. Upon further inspection of the fetched code, it seems to be a complex cashflow-rewriting system used to manipulate a gambling game.
const routeInjectionRules = {
    '/v1/pay/purchase-goods': {
      identify: function (handlers, fn, index) {
        ...
      },
      position: 'after',
      extraMiddlewares: [function (req, res, next) {
       // Translation: [Plugin] Mount risk middleware as post-payment success logic.
log('[插件] 支付成功后的后置逻辑挂载risk');
       riskCode(req, res, next); // Executes dynamically fetched code
      }]
    }
  };
Secondly, a prototype-level middleware that quietly monkey-patches Express.js, adding global middleware to every POST route. This middleware listens for a secret x-operation header and unlocks four types of commands to the operator:
Inside the package, there is also an embedded HTML page for a “Directory compression download service” (Chinese title: 目录压缩下载服务).
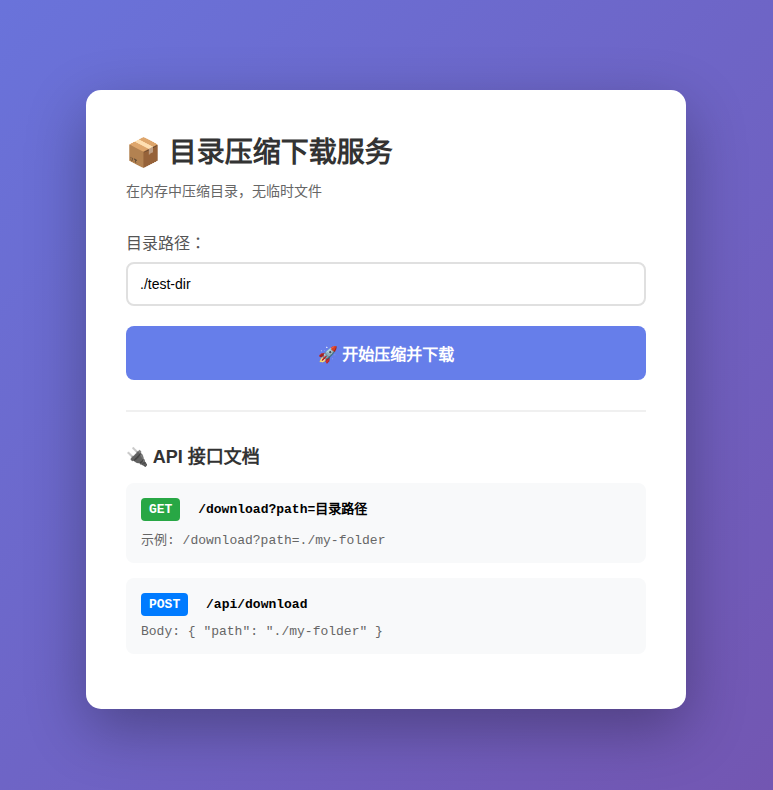
While this page was never hooked up anywhere in the backdoor code we observed, it appears to be an operator-facing UI for browsing and exfiltrating directories as zip files.
The scary part: that riskCode(...) function called in the middleware is remote-controlled and updated every 30 seconds.
While the payload is not actively invoked (yet), we observed logic capable of retroactively adjusting a user's recent game history. The most sophisticated component of this backdoor is the fixFlow function, a balance manipulation engine that retroactively rewrites a user's gambling history to achieve a desired balance change while maintaining the appearance of legitimate gameplay.
The main orchestration happens in this fixFlow, which executes a four-phase pipeline:
// Takes a desired amount as argument
async fixFlow(backupAmount) {


  // Phase 1: Load recent cashflow records
  const original = await this.getCashFlow();

  // Phase 2: Compute required adjustments to betting history
  const adjuster = new GameResultAdjuster({ debug: false });
  const adjustResult = adjuster.adjustDBData(original, backupAmount);
  const { backupRecords, adjustedResult } = adjustResult;
  const rewritten = this.writeBackFlowData(backupRecords);

  // Phase 3: Validate consistency
  const validation = this.validateCashFlowChain(...);
  if (!validation.isValid) {
    ...
  }

  // Phase 4: Persist to database
  await this.updateUserCashFlow(rewritten);
  await sendToUser(userId, { pop: false });
  await this.updateUserGameRoundFlow(gameTasks);

}
The function loads recent cash-flow records and converts them into structured game logs. Afterwards, the adjustDBData method generates replacement betting outcomes engineered to produce a fabricated balance change. What’s interesting is that instead of relying on one algorithm, it runs two competing strategies (greedy vs backtracking), and selects the approach with the highest "realism" score. After verifying the rewritten balance chain for consistency, updateUserCashFlow and updateUserGameRoundFlow write the altered records via Prisma back into the live production database, while sendToUser pushes the updated balance event to the user’s device.
The greedy approach divides the desired target amount evenly across available rounds. It's fast but produces suspicious patterns. Imagine you need to distribute 300 fabricated coins across 3 game rounds. The greedy approach simply divides evenly: 100 per round. For each round, it sets the payout to achieve that round's desired result. However, this has the tendency to look fake. Real games don't hit consistent results every single round.
The backtracking approach explores the full solution space, trying different bet/payout combinations until finding one that hits the desired target within a 0.01% error margin. Instead of committing to decisions immediately, it explores the full tree of possibilities. Try a bet amount, see where it leads, and if it doesn't work out, undo it and try a different bet. This is like solving a maze by trying every path until you find the exit. This approach finds a realistic chain of results that accounts for constraints, such as the user's available cash at the time of betting.
It works something like this:
The algorithm employs several optimizations, such as memoization to avoid re-exploration of failed attempts, and reachability pruning to skip branches that cannot mathematically reach the desired target.
After both strategies run, the system applies a sophisticated quality scoring mechanism that evaluates how "realistic" a forged gambling history appears. This score determines which fraud strategy's output gets used, and serves as a metric for the attack's success.
// Generate a quality score
const overallQuality = this.evaluateLogsQuality(adjustedGameLogs, completeness.actualNetGain);
The evaluateLogsQuality function starts at 100 points and deducts penalties for suspicious patterns. Some of these penalties include:
In conclusion, it means the goal is not just fraud. It is fraud that survives internal consistency checks, fabricating wins and losses while keeping accounting consistent using a clever anti-detection mechanism.
We can’t say for certain which game is being targeted, but surrounding references suggest it may be a gambling app called Bappa Rummy. One of the endpoints referenced in the file is gameland.myapptest.top/v1, and a quick SSL certificate transparency search for that domain shows related hosts like gali.web.test.myapptest.top. Inspecting it reveals what looks like a broken landing page tied to Bappa Rummy, making it a plausible target of the backdoor. The app seems to be widely promoted online through referral programs and alternative app stores, but is no longer listed on the official Google Play Store.
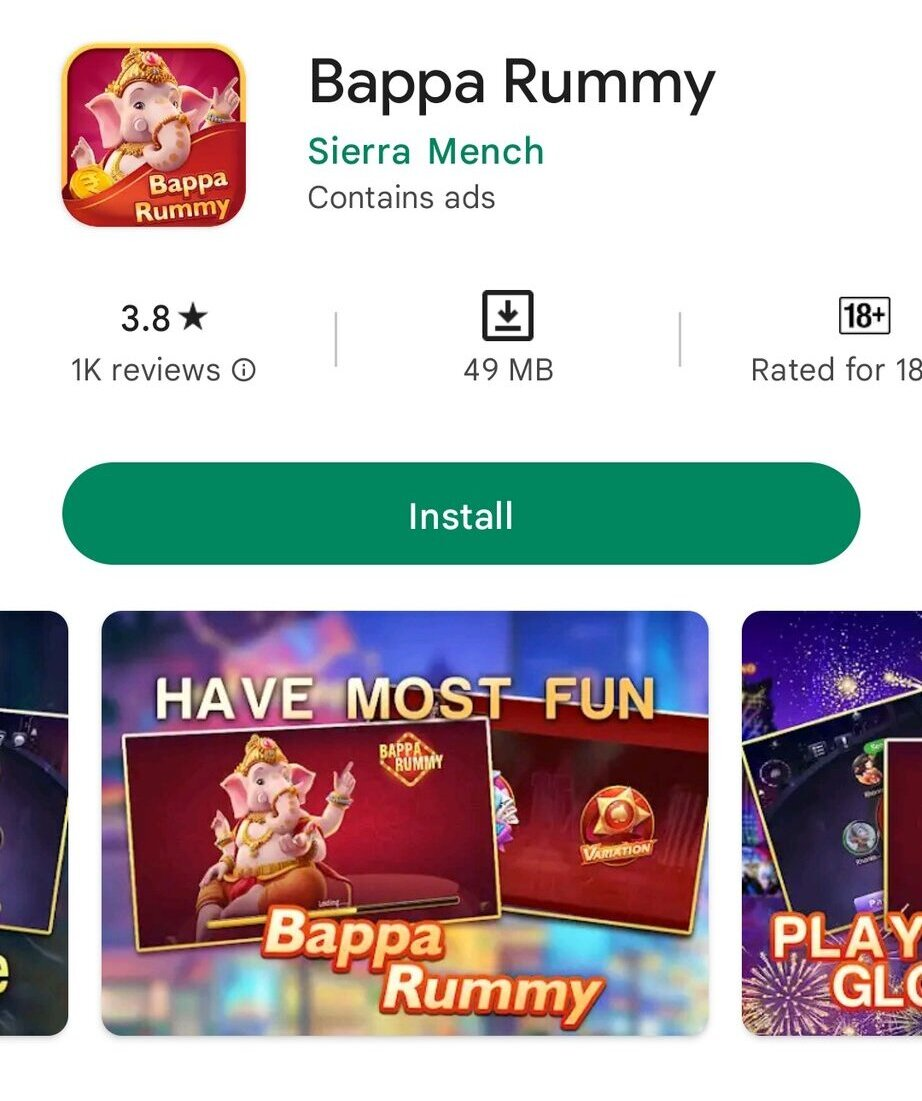
While we don't know who is behind the backdoor, the scary part is what it does once it lands in the right environment. This is not “just” a typical dependency implant that exfiltrates source code, secrets, or customer data.
Instead, it hooks directly into business logic, executes remote-controlled code on real traffic, and can rewrite database-backed financial history. If your monitoring assumes database logs are trustworthy, this kind of manipulation can stay invisible for a long time.
If you already use Aikido, this package would be flagged in your feed as a 100/100 critical finding.
Not on Aikido yet? Create a free account and link your repositories. The free plan includes our malware detection coverage (no credit card required).
Finally, having a tool that can stop malware in real time as it appears can prevent a serious infection. This is the idea behind Aikido Safe Chain, a free and open-source tool that wraps around npm, npx, yarn, pnpm, and pnpx and uses both AI and human malware researchers to detect and block the latest supply chain risks before they enter your environment.
Packages and authors:
The backdoor communicates with a remote host for both payload updates and logging.
Observed endpoints:
https://payment[.]y1pay[.]vip/v1/risk/get-risk-codehttps://payment[.]y1pay[.]vip/v1/risk/loghttps://payment[.]snip-site[.]cchttps://gameland[.]21game[.]livehttps://gameland[.]myapptest[.]top/v1https://gameland[.]nbzysp1[.]com/v1https://gameland[.]21game[.]live/v1Other IOCs and huntable behaviors:
x-operation header with one of the four operation tokens: express.Route.prototype.post
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。