





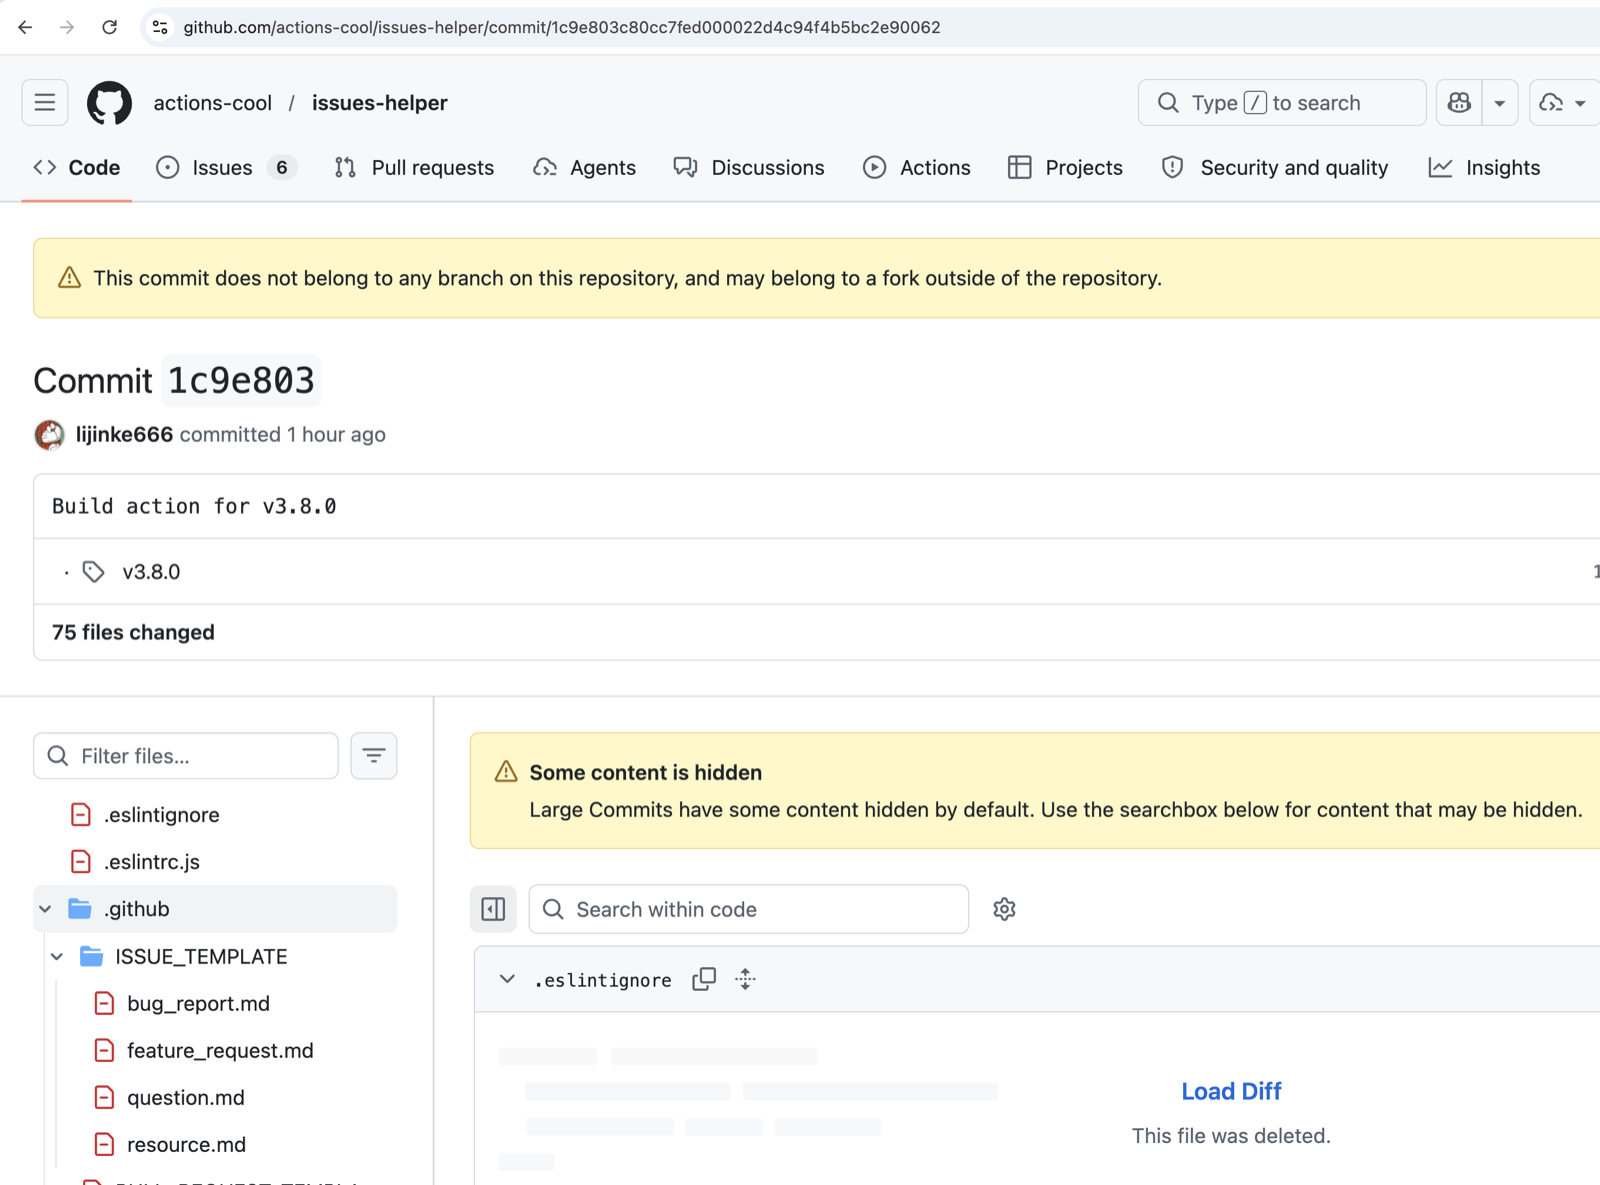
The popular GitHub Action actions-cool/issues-helper has been compromised. Every existing tag in the repository has been moved to point to a imposter commits that does not appear in the action's normal commit history. That commit contains malicious code that exfiltrates credentials from CI/CD pipelines that run the action.
Because every tag now resolves to malicious commits, any workflow that references the action by version pulls the malicious code on its next run. Only workflows pinned to a known-good full commit SHA are unaffected.
A second action in the same organization, actions-cool/maintain-one-comment, has also been compromised by the same actor using the identical pattern - every tag moved to an imposter commit, same bun + Runner.Worker memory-read payload, and the same exfiltration domain t.m-kosche.com. Everything below about detection, IOCs, and remediation applies equally to maintain-one-comment. We have notified the maintainers via GitHub issue #11.
actions-cool/issues-helper repository.bun JavaScript runtime to the runner.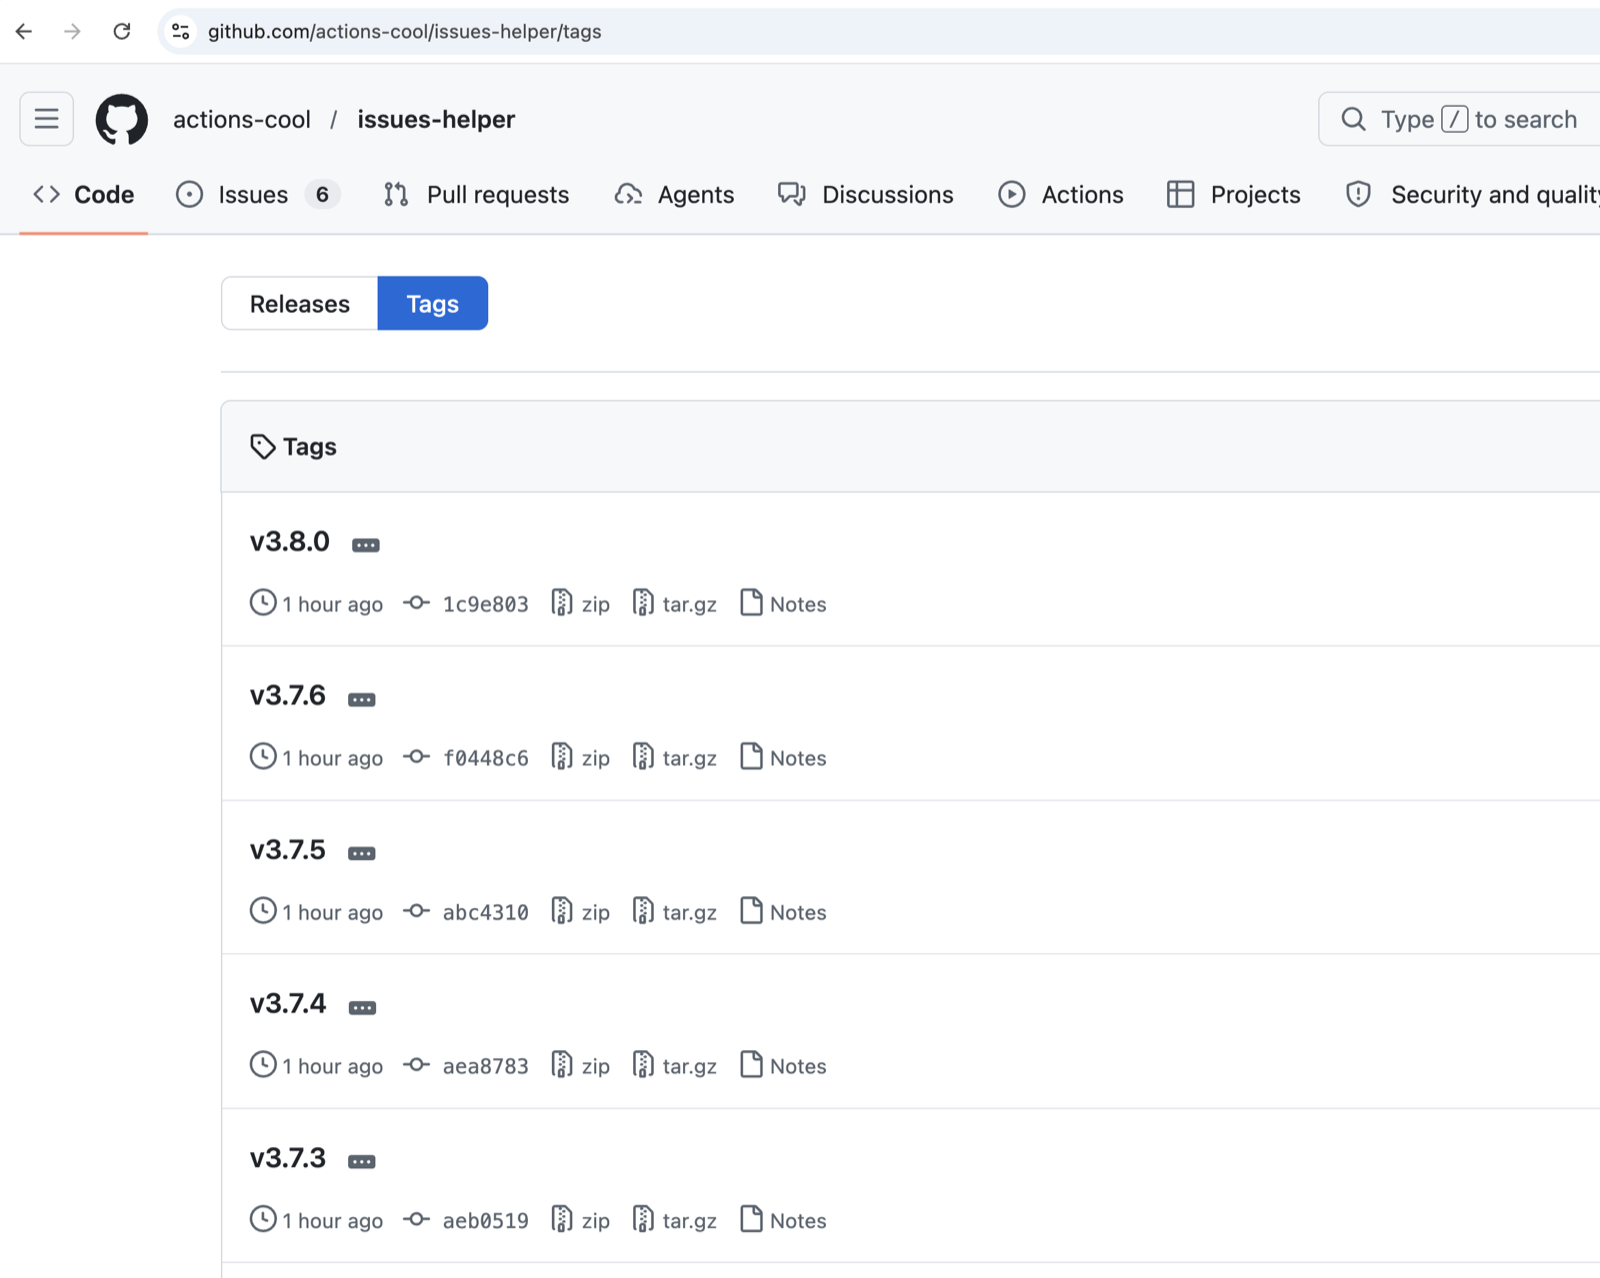
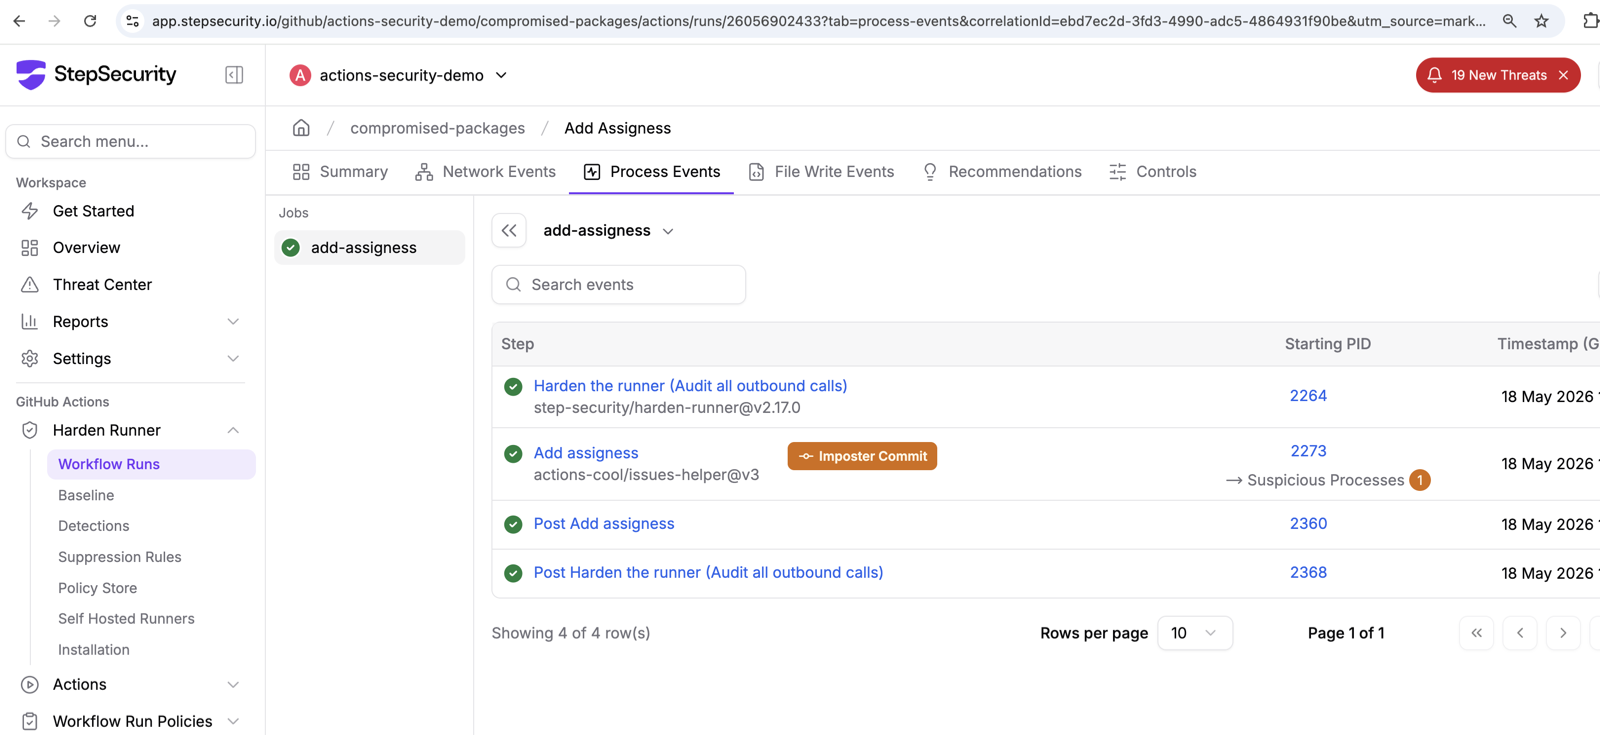
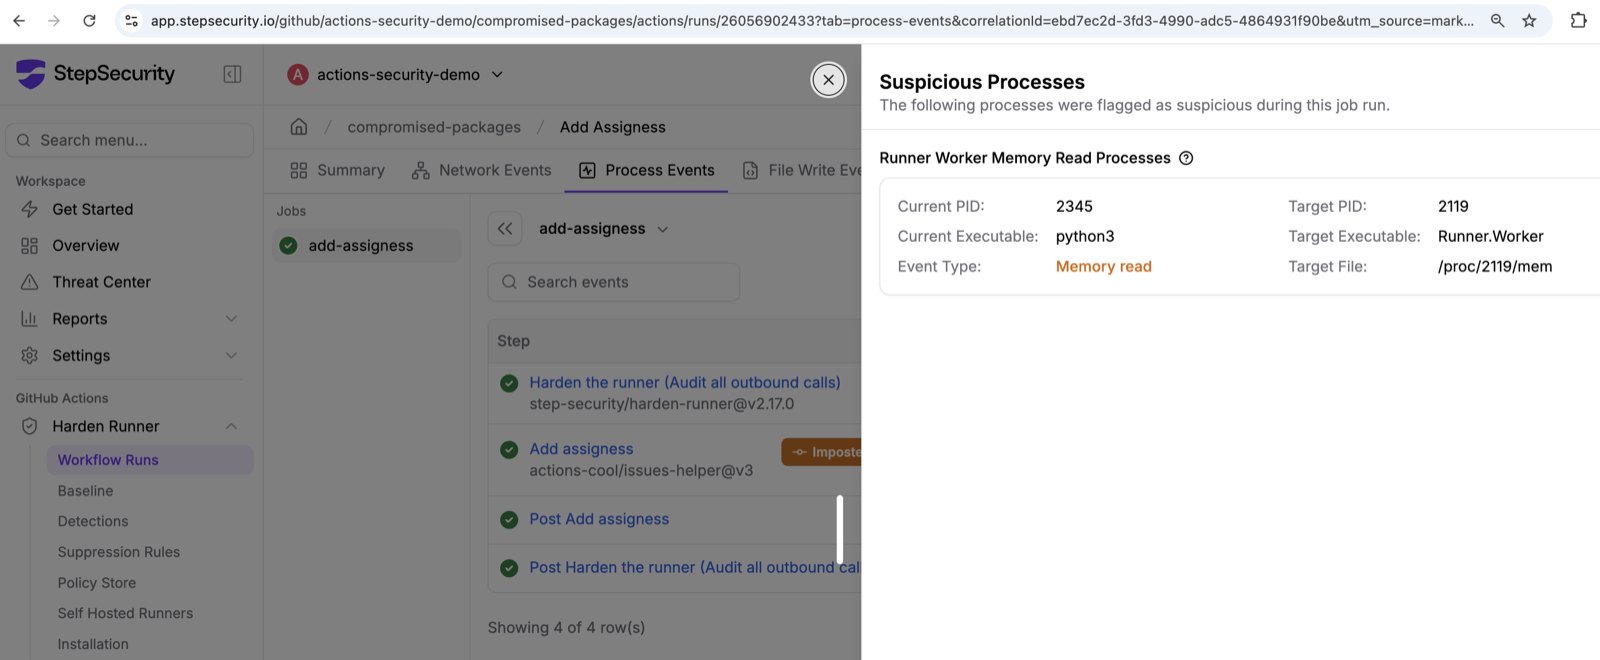
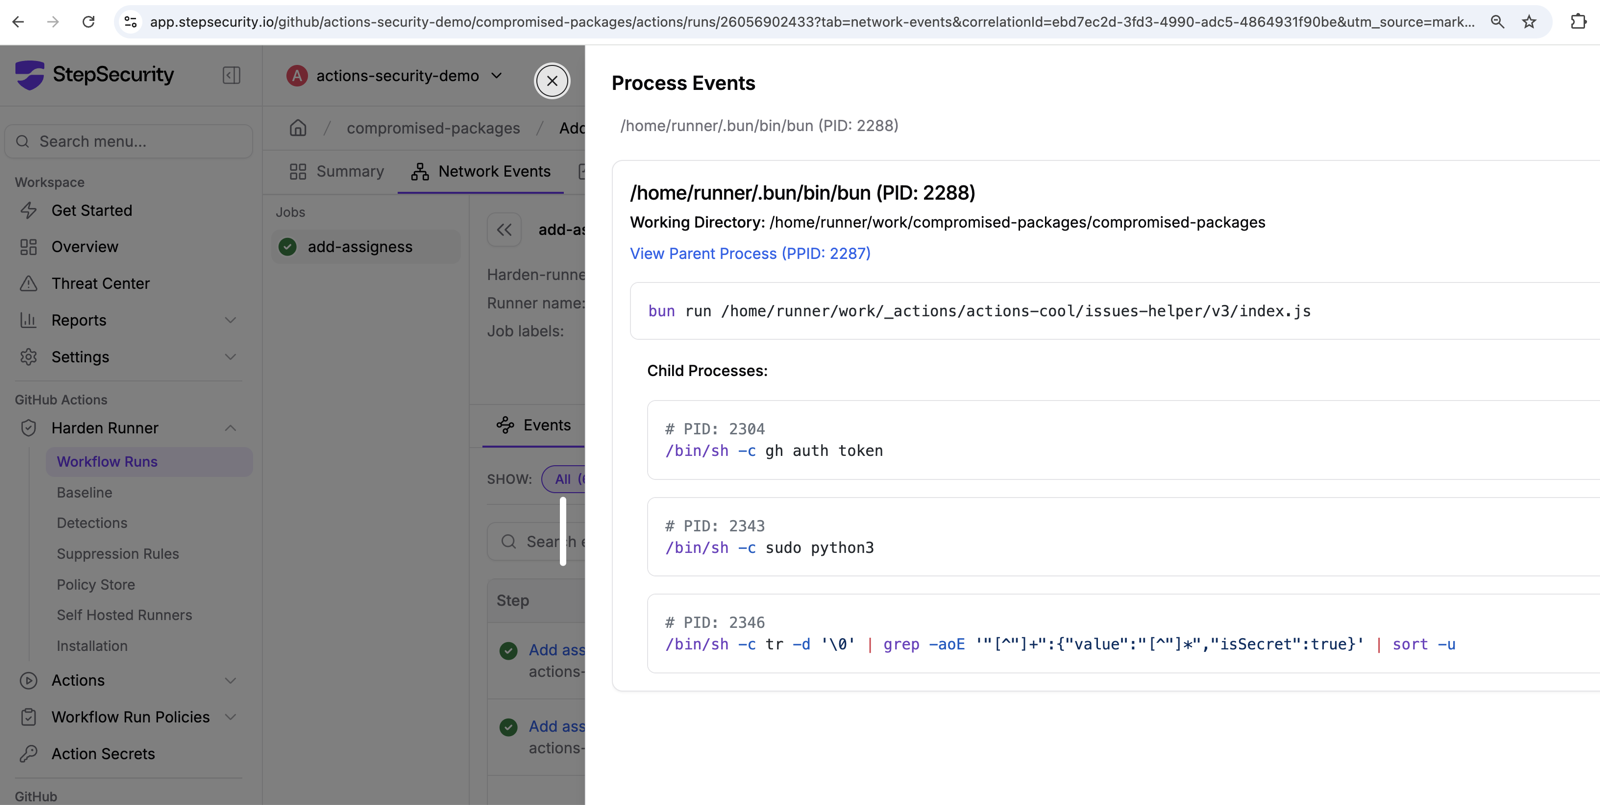
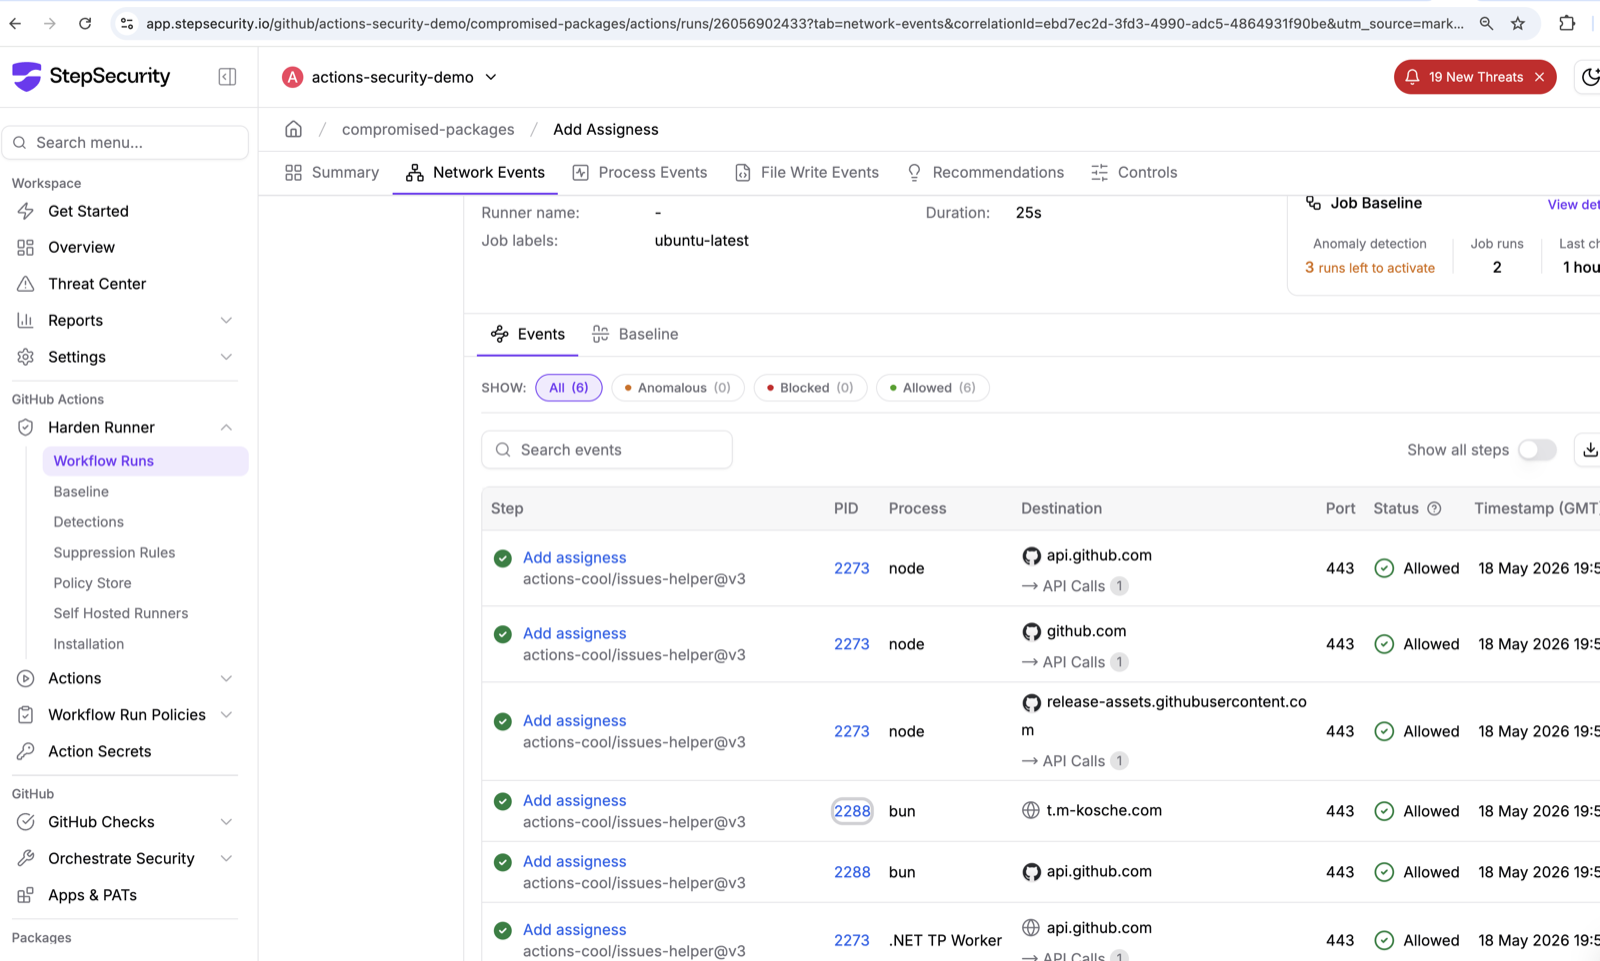
You can see this behavior in a controlled Harden-Runner test run here: https://app.stepsecurity.io/github/actions-security-demo/compromised-packages/actions/runs/26056902433
Harden-Runner captured the bun download, the Runner.Worker memory read, and the outbound call to t.m-kosche.com.
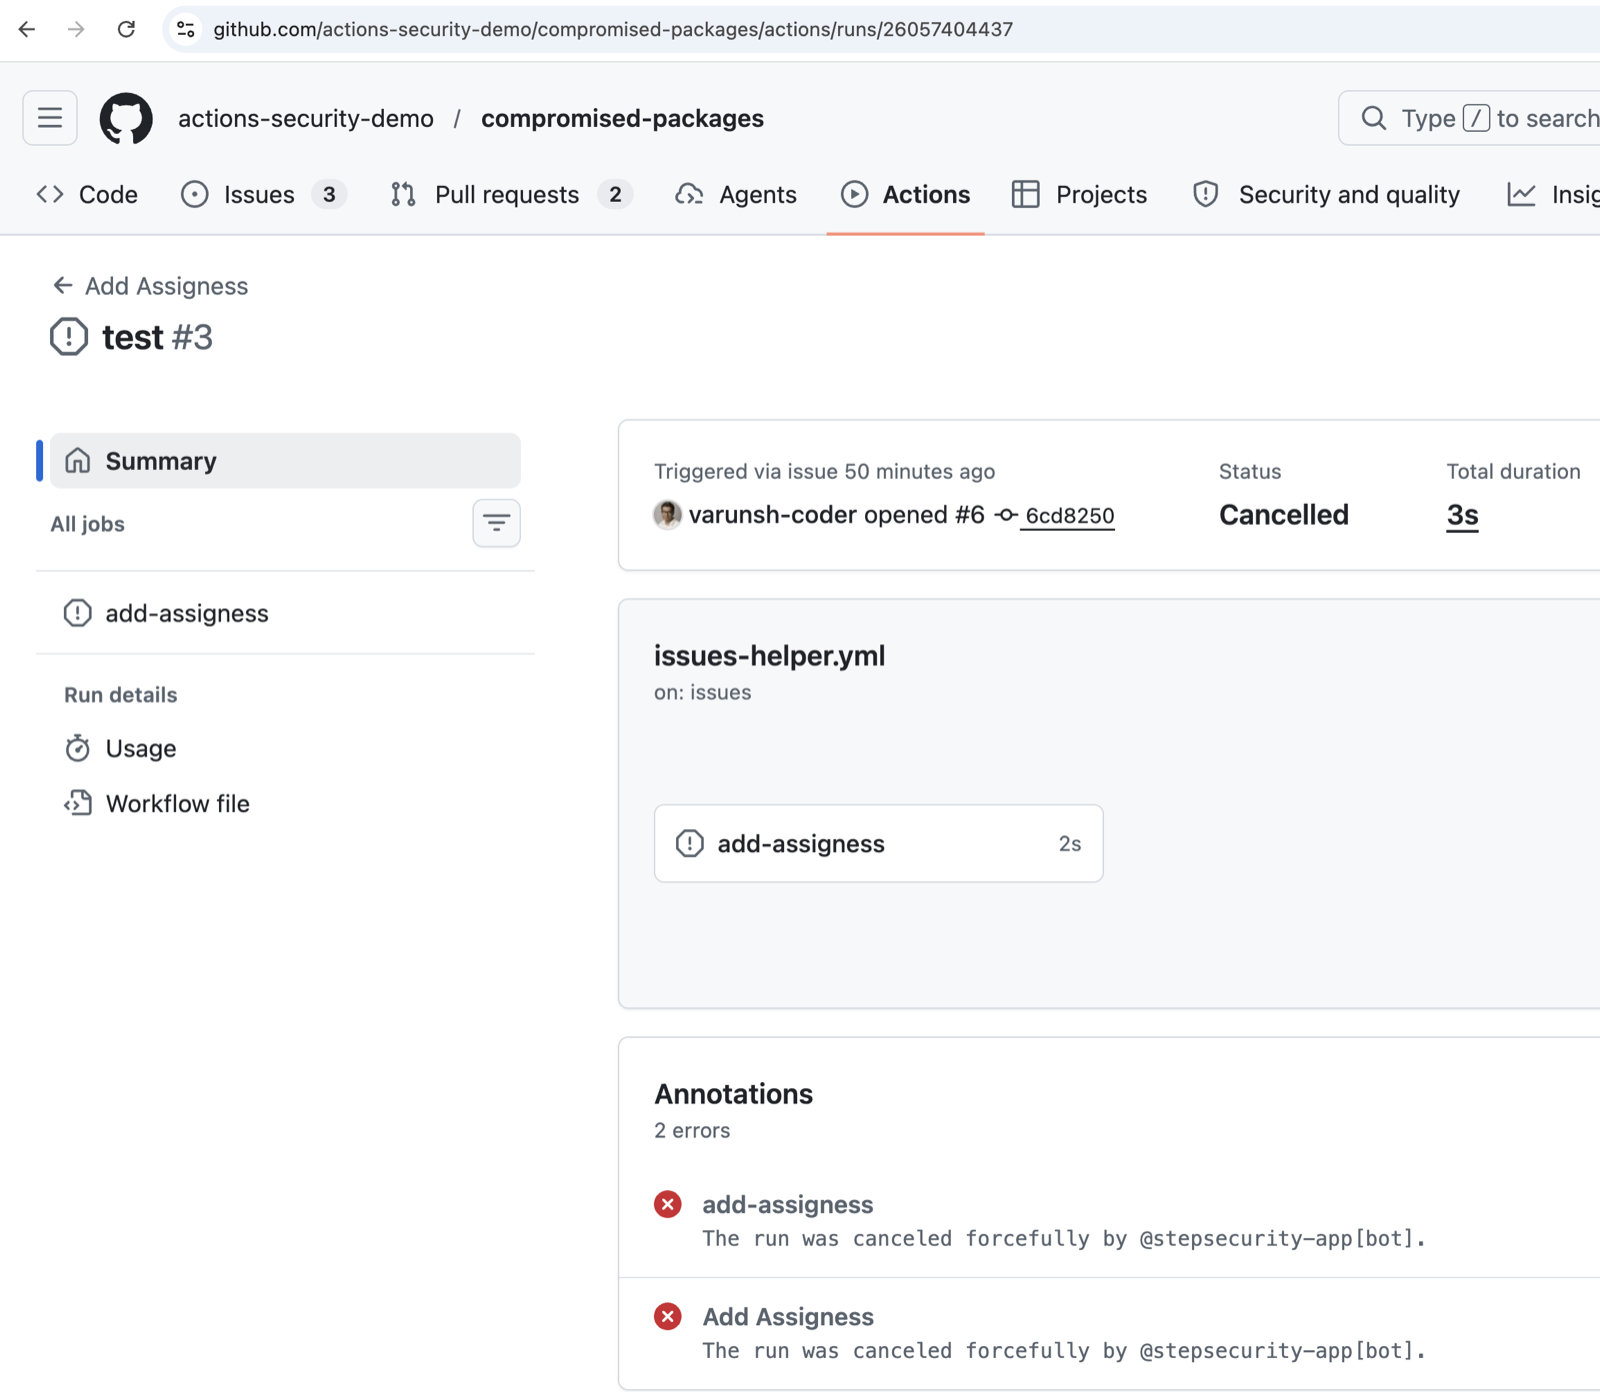
StepSecurity has added actions-cool/issues-helper to its Compromised Actions Policy. For any enterprise customer with this policy enabled, any workflow run that references this action will be blocked before it executes, preventing the malicious code from ever running in the customer's CI/CD environment.
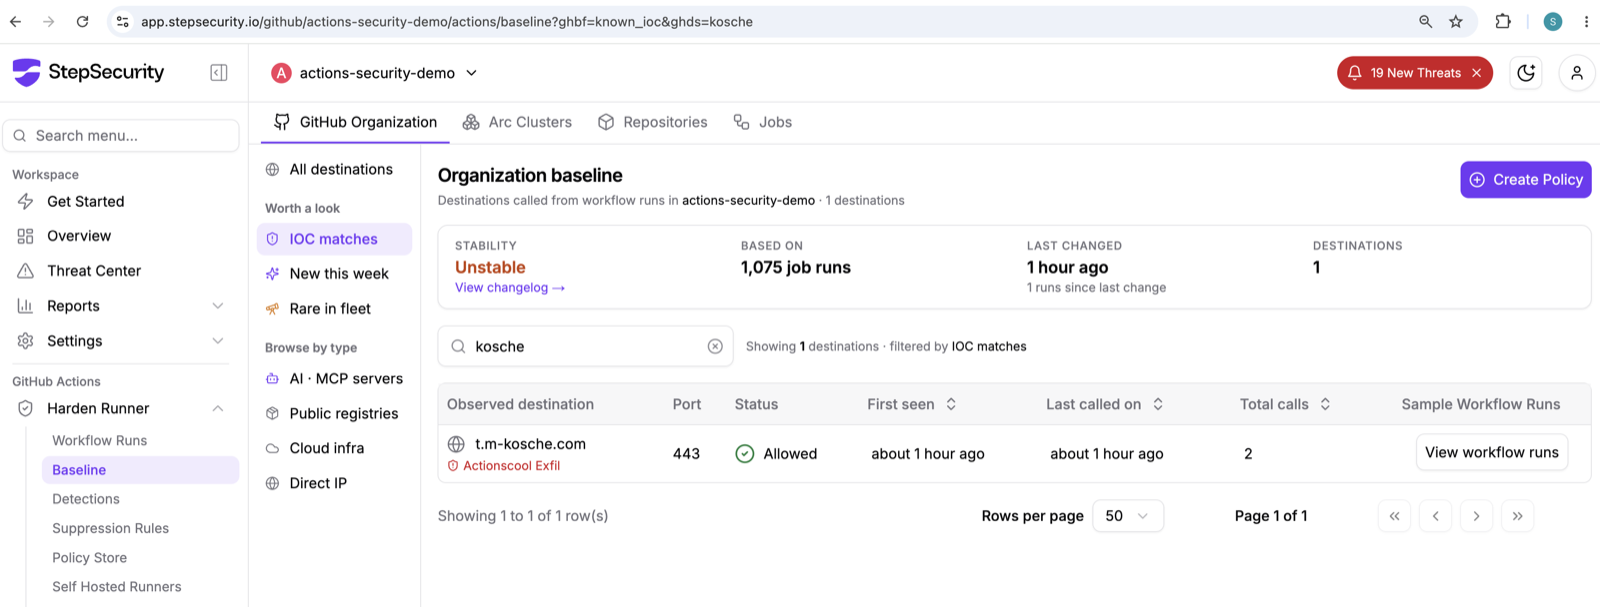
StepSecurity has added the attacker's exfiltration domain to the Harden-Runner global block list. Any workflow protected by Harden-Runner will automatically block outbound connections to this domain - even in audit mode, and without any per-workflow configuration. This gives customers defense-in-depth: even if a compromised action somehow runs, the credentials cannot leave the runner.
StepSecurity's Action-Uses-Imposter-Commit detection flags any workflow that references a GitHub Action via a commit SHA (or via a tag that has been moved to a commit SHA) which does not match any legitimate tag or branch head of that action's repository - exactly the signature of this attack.
actions-cool/issues-helper — every tag (53 in total) moved to an imposter commitactions-cool/maintain-one-comment — every tag (15 in total) moved to an imposter committ.m-kosche.com — receives the encoded credentials harvested from Runner.Worker memory. Added to the Harden-Runner global block list.bun JavaScript runtime to /home/runner/.bun/bin/bun/proc/<Runner.Worker PID>/mem from a python3 child processgh auth token, sudo python3, and tr/grep pipelines filtering for "isSecret":truet.m-kosche.com on port 443The attacker generated a unique imposter commit per tag — each with a fake "Build action for vX.Y.Z" message that mirrors the legitimate maintainer's commit-message style. The tells are the timestamps: all 53 imposter commits in issues-helper were created within a 3-minute, 16-second window, and all 15 in maintain-one-comment within 39 seconds. Every commit below is dangling — none are reachable from the action's default branch.
actions-cool/issues-helper — 53 imposter commits (2026-05-18T19:10:24Z → 19:13:40Z):
v3.8.0 → 1c9e803c80cc7fed000022d4c94f4b5bc2e90062v3.7.6 → f0448c62fc57b8a5ce23d8acd6e795cdd76a3b6cv3.7.5 → abc4310e6b8520aff6af79a4880217917cd1436bv3.7.4 → aea87833045e38098e64310e962b897ae8aaba33v3.7.3 → aeb05195dbd618afce6f22ca4937e46940d86be1v3.7.2 → 4b10341e231301a86c66f6c09e3e4de76d8719fev3.7.1 → 8a3a7c2960ff3a4e3fd1481cfd1eb31301e16337v3.7.0 → aa44b5492c787fbc4c51edb8d98d88b668fe89d1v3.6.3 → 03bbf452b52fb318196d9c193fd178a79a6d7f9bv3.6.2 → 257849272e291fb74ff4bee4d3be4796dd35fbbbv3.6.1 → 4bb72d31eaee87562b70a0cf1b93579bb2b14c23v3.6.0 → e0585c10366288eeec3117d65ed24240ccbf1f47v3.5.2 → 419b34c603623ea8749a98b7153df20e389dd0ecv3.5.1 → 8cc2629c5681d794c494b79283d23aa3ce78749cv3.5.0 → 4b69521f9829a1114b94d74fdc1a38f2291d8c34v3.4.0 → dc5687b71897e8b57bc9743e325ac72cee763c9cv3.3.3 → 3846bd4230da36f68a4cc1527298ca9ab2652fb9v3.3.2 → 459b0cfc4dd708b6218b72a7a01dda6c6a7ab0c0v3.3.1 → fa6a4ca487f2dc699d428126ea2b18e9d0d15c9dv3.3.0 → 15c89f718cd325833aad8000d3ec72e2660f6584v3.2.1 → a7d3c46a35564fa85321f3557700f6ea0c0616a9v3.2.0 → 85c9d842e1c0f41f8805f17600c25237e08a0224v3.1.0 → 64ed6d61b6eee8744417e1d1cc651665a8bce236v3.0.1 → d9b1764cbe78ec9b12f01a66b2d2c902b15981b6v3.0.0 → b9c83f01929e190cda300e76f688bf7ea7e37a7av3 → 147337a919d92f4bf42f02843682d694650f1e22v2.5.0 → e9631d2e615d95a19111c272049444fb073a99bev2.4.3 → 91b26b99c50ad890f98c2184d251bd3a16f5b1b1v2.4.2 → 3f4d6804812734dfe945bbe8ef619f151e4b27f6v2.4.1 → 46eff1378ad0faee27c017ebd97f605548777098v2.4.0 → 071e169dfb36005b3262b3853c9894698b8b303bv2.3.1 → 55253d49c68133ae52e791a3f1f8242b191f5e91v2.3.0 → edf8cf78d6feeb5a73cda9317af5ddfc4da6c5fdv2.2.1 → a0c53dd42fc842d2f9276c5a1d4f9a26abe8713dv2.2.0 → 896379edfaac994ff214a3097c6c82e21be16066v2.1.2 → 9bd6ce03e0c279f347b519548b87d26699ad31c9v2.1.1 → d2877f69bae9d8dcbadb06b3214ebf0789ed566ev2.1.0 → 601e1296a5a0853b5e109f9820151c72619e11e4v2.0.0 → 75fb02043af24e6f3eaf534464de338173993629v2 → 3480e51eec2be03a70d6fe17507413a96fe5b57dv1.12 → 67716d94ad07d7fe793cabc6f6d1ffe24f77bdf7v1.11 → cd96d6518c6338f8510638bce764c7abd7194983v1.10 → 6a538e928b8856062de61103ed5a08f0ea0faee9v1.9 → 9793761b1bc3dde7ad1ccb9be6211919e20a3f01v1.8 → 8a64710bb8fee9f5c92eb1a816e016ed00fbcce0v1.7 → 710ff89debb143f6859cf8d54c0e8739224ff6c1v1.6 → 3904fe935f1a18fee5dbad6db46a66c9dcffde01v1.5 → cfbd14ccc97afd3baa822bd231df8460e4f02f29v1.4 → 15dc537110a44b0625622e82b7d6ca95583f276av1.3 → e778a401e233bf0a416f3fe2a52d9039949b30a6v1.2 → 203671479d663755cb5bf8ffbeca6d2b685af7aev1.1 → a7156495f3403674cafe3796382bded1d9af8931v1 → 5c267592a87e92c2b005b338bd0d2724c2f64acbactions-cool/maintain-one-comment — 15 imposter commits (2026-05-18T19:30:30Z → 19:31:09Z):
v3.3.0 → 7f6120bb10c870b9fde146961a18e5bf0b3d4401v3.2.1 → 4a6ac28684e2b0c48d502b31363ec5dd72f9d7ffv3.2.0 → f3593fb4454aff5a6e1fb67024f94bfa48591dd5v3.1.1 → 5d844d6b1c6a0c09a96844521bb01f149d9fe2c1v3.1.0 → 2ab0aa3449ffe526ea64489193955d82a6848669v3 → c43d668894bebbeea688878ab6774fa405f22251v2.0.2 → 93ec180e89e8fdd8525869daa5590c433b6c30fbv2.0.1 → cbb2ba52a811cb6152eee0607519cc5df78289b5v2.0.0 → 99b7f41bf9e14a2a2c7cc524731336543f552178v2 → ef01721dfd04f9c7ff1a256292f7dceabfd08d9bv1.2.1 → d6622cc2415156cf4e81cf57866420479a966b3av1.2.0 → 74b8a9a600daf6fc6070ca0a10d840a7bb6890aev1.1.0 → cae76b34894429e693e9b0d2731e7654c373ce81v1.0.0 → 7bb44528a0869f4074cc5448601804878704963fv0.0.1-wip → 8bb68050bc2a353f9d3032e2b42732a69d97499b
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。