惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

M
MIT News - Artificial intelligence
罗磊的独立博客
Hugging Face - Blog
Hugging Face - Blog
Apple Machine Learning Research
Last Week in AI
Last Week in AI
S
SegmentFault 最新的问题
让小产品的独立变现更简单 - ezindie.com
美团技术团队
人人都是产品经理
人人都是产品经理
WordPress大学
WordPress大学
The Cloudflare Blog
IT之家
IT之家
雷峰网
雷峰网
小众软件
小众软件
博客园 - 叶小钗
博客园 - 聂微东
爱范儿
爱范儿
博客园 - 司徒正美
博客园 - 三生石上(FineUI控件)
V
Visual Studio Blog
博客园 - 【当耐特】
V
V2EX
博客园_首页
T
Tailwind CSS Blog

Step Security Blog

Announcing Dependabot Configuration Enhancements: Cooldown and Group Support - StepSecurity Securing Vibe Coding and AI Coding Agents: An End-to-End Approach with StepSecurity - StepSecurity Introducing StepSecurity Dev Machine Guard: Protecting Developer Machines from Supply Chain Attacks - StepSecurity Top 2024 Predictions for CI/CD Security - StepSecurity Dev Machine Guard Is Now Open Source: See What's Really Running on Your Developer Machine - StepSecurity Datadog's DevSecOps 2026 Report Validates What We've Been Building - StepSecurity hackerbot-claw: An AI-Powered Bot Actively Exploiting GitHub Actions - Microsoft, DataDog, and CNCF Projects Hit So Far - StepSecurity Cline Supply Chain Attack Detected: cline@2.3.0 Silently Installs OpenClaw - StepSecurity @velora-dex/sdk Compromised on npm: Malicious Version Drops macOS Backdoor via launchctl Persistence - StepSecurity axios Compromised on npm - Malicious Versions Drop Remote Access Trojan - StepSecurity Behind the Scenes: How StepSecurity Detected and Helped Remediate the Largest npm Supply Chain Attack - StepSecurity 10 Layers Deep: How StepSecurity Stops TeamPCP's Trivy Supply Chain Attack on GitHub Actions - StepSecurity Malicious IoliteLabs VSCode Extensions Target Solidity Developers on Windows, macOS, and Linux with Backdoor - StepSecurity TeamPCP Plants WAV Steganography Credential Stealer in telnyx PyPI Package - StepSecurity litellm: Credential Stealer Hidden in PyPI Wheel - StepSecurity Checkmarx KICS GitHub Action Compromised: Malware Injected in All Git Tags - StepSecurity CanisterWorm: How a Self-Propagating npm Worm Is Spreading Backdoors Across the Ecosystem - StepSecurity Trivy Compromised a Second Time - Malicious v0.69.4 Release, aquasecurity/setup-trivy, aquasecurity/trivy-action GitHub Actions Compromised - StepSecurity bittensor-wallet 4.0.2 Compromised on PyPI - Backdoor Exfiltrates Private Keys - StepSecurity Malicious npm Releases Found in Popular React Native Packages - 130K+ Monthly Downloads Compromised - StepSecurity Malicious Polymarket Bot Hides in Hijacked dev-protocol GitHub Org and Steals Wallet Keys - StepSecurity ForceMemo: Hundreds of GitHub Python Repos Compromised via Account Takeover and Force-Push - StepSecurity xygeni-action Compromised: C2 Reverse Shell Backdoor Injected via Tag Poisoning - StepSecurity kubernetes-el Compromised: How a Pwn Request Exploited a Popular Emacs Package - StepSecurity How StepSecurity Caught a Release Storm in Microsoft’s @types Packages - StepSecurity Harden Runner Now Supports Windows and macOS GitHub Actions Runners - StepSecurity 10,000 Open-Source Projects Now Secured by Harden-Runner Community-Tier: A Milestone Three Years in the Making - StepSecurity 20+ Popular NPM Packages Compromised (Chalk, Debug, Strip-ANSI, Color-Convert, Wrap-ANSI...) - StepSecurity 2024 in Review: The Evolution of CI/CD Security & What's Next - StepSecurity How to Use Docker in Actions Runner Controller (ARC) Runners Securely - StepSecurity
StepSecurity’s Unified Protection Across the SDLC Infrast...
2026-04-09 · via Step Security Blog

The cybersecurity community has finally woken up to a harsh reality: supply chain attacks aren't just targeting your final products anymore—they're compromising the entire infrastructure that builds your software. From the Ultralytics hijack through the devastating Shai-Hulud campaigns, to the recent TrustWallet compromise, attackers have realized that the highest ROI comes from targeting the factories, not just the products.

While the industry rushes to create frameworks and threat models to understand these attacks, organizations are left with a critical question: How do I actually protect my software development lifecycle today?

Building on Industry Research: From Framework to Implementation

The recent introduction of SITF (SDLC Infrastructure Threat Framework) by Wiz represents important progress in mapping supply chain threats. Their framework correctly identifies the five critical pillars under attack:
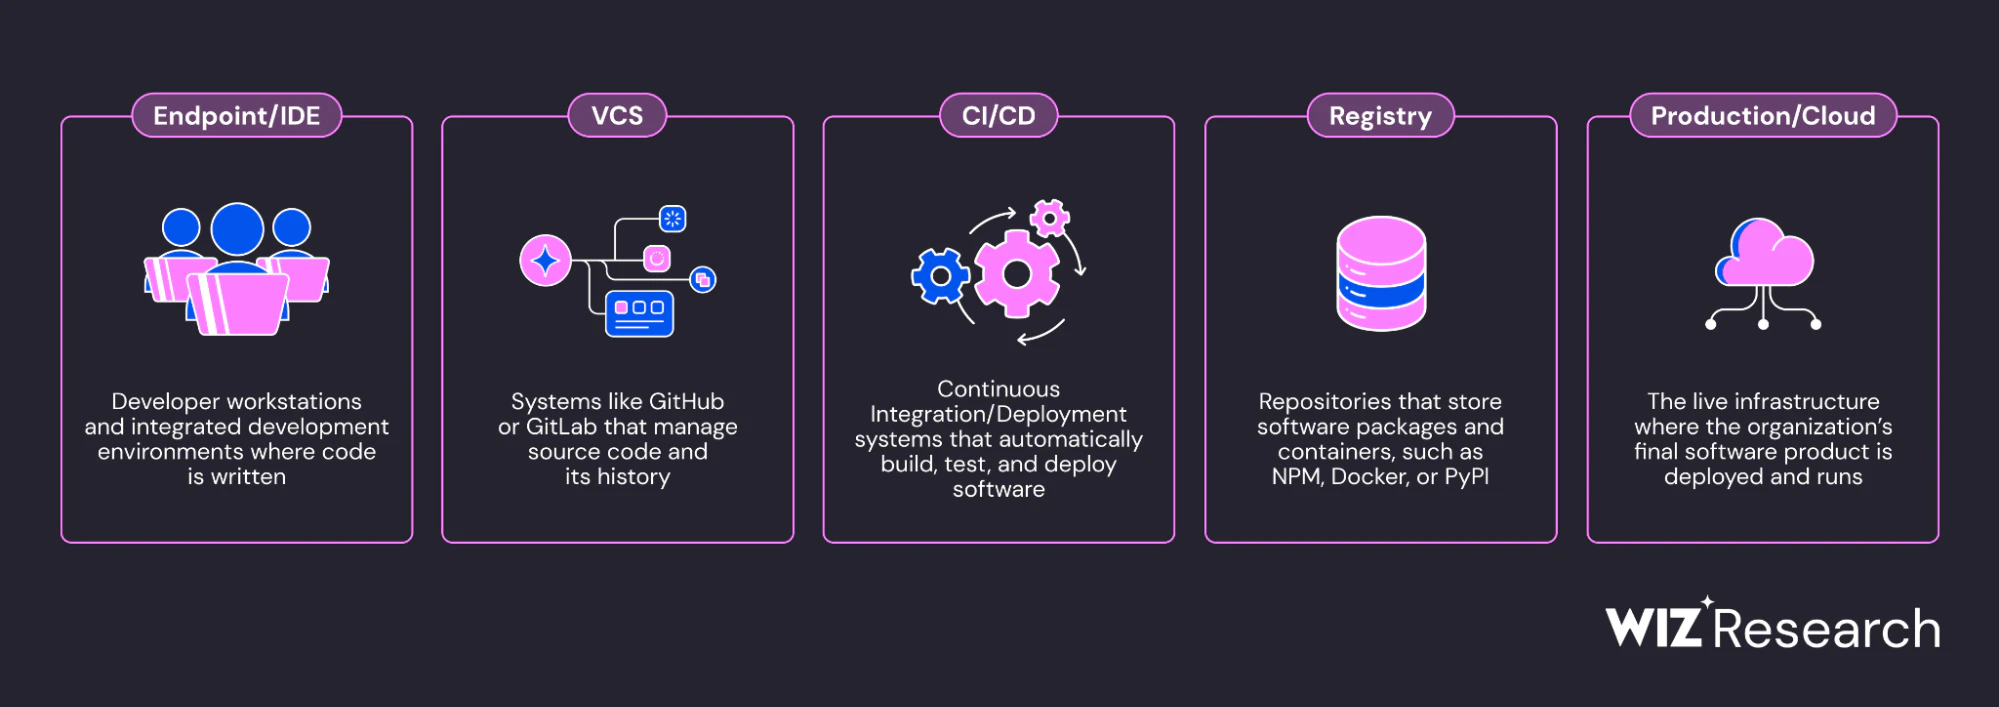
  • Developer Endpoints/IDEs: Where code is written and dependencies are consumed
  • Version Control Systems (VCS): Where source code and secrets are stored
  • CI/CD Pipelines: Where software is built, tested, and deployed
  • Package Registries: Where dependencies and artifacts are published
  • Production Environments: Where software ultimately runs

                 Source: Wiz Research

This comprehensive mapping validates what StepSecurity has been building toward - complete coverage across the entire software development lifecycle. The framework provides excellent guidance for organizations looking to understand their threat landscape.

At StepSecurity, we've taken this understanding and built actual deployed solutions across each of these critical areas.

StepSecurity's Implementation: Comprehensive Coverage Across Critical SDLC Pillars

Building on the comprehensive threat mapping that frameworks like SITF provide, StepSecurity has developed and deployed solutions across four of the five critical pillars. Our platform delivers active protection at the stages where modern supply chain attacks most commonly initiate and propagate.

Here's how StepSecurity provides comprehensive coverage across the SDLC:

Stage 1: Developer Environment Protection

Product: Dev Machine Guard Protection: IDE extension monitoring, dependency visibility for human and AI actions, AI coding agent security, MCP server monitoring, policy enforcement

Modern attacks increasingly target developer machines as the entry point into your software supply chain. Dev Machine Guard monitors what's actually happening on developer endpoints—from malicious packages being installed to AI coding agents making suspicious network calls.

Stage 2: Source Code & Dependency Security

Product: npm Package Search + GitHub Checks Protection: Package risk assessment, cooldown periods, compromised package detection, provenance verification

Your VCS and dependency management represent critical control points. npm Package Search provides real-time intelligence on package risks, allowing you to directly search for and view all compromised packages in the ecosystem, while GitHub Checks integrates directly into your pull request workflow to enforce security policies before code is merged.
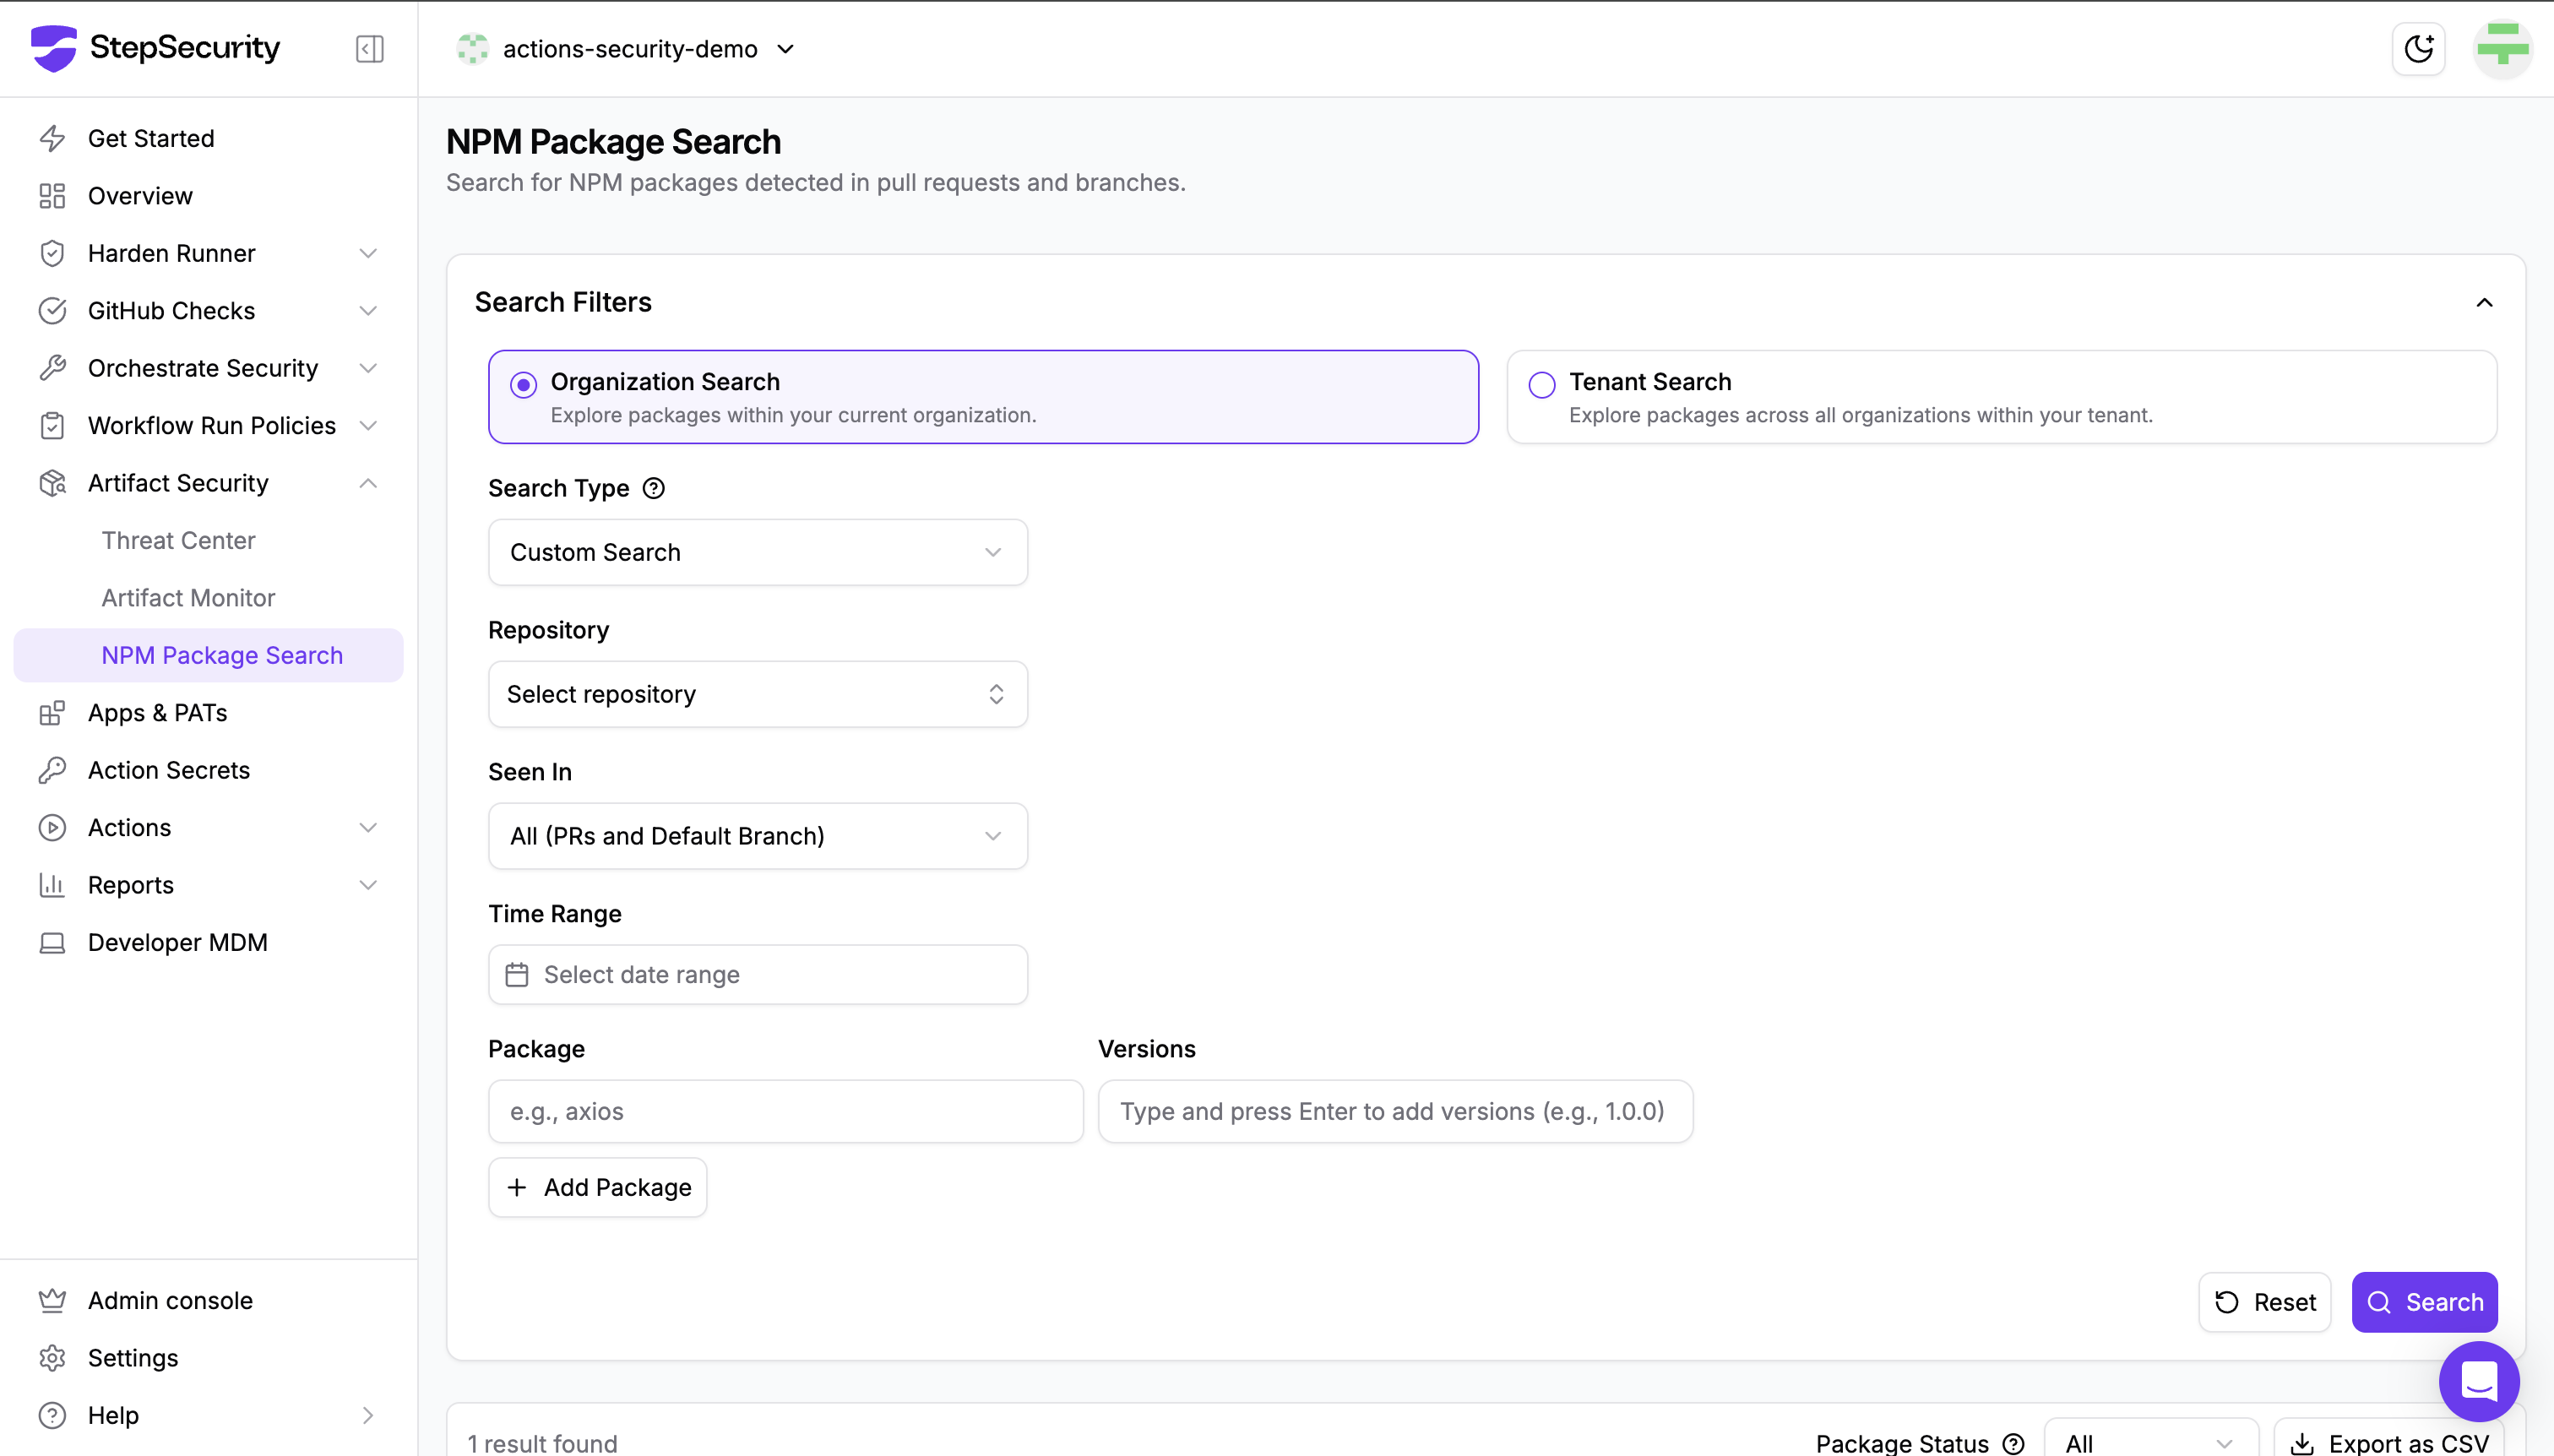
StepSecurity NPM Package Search

Key protections include:

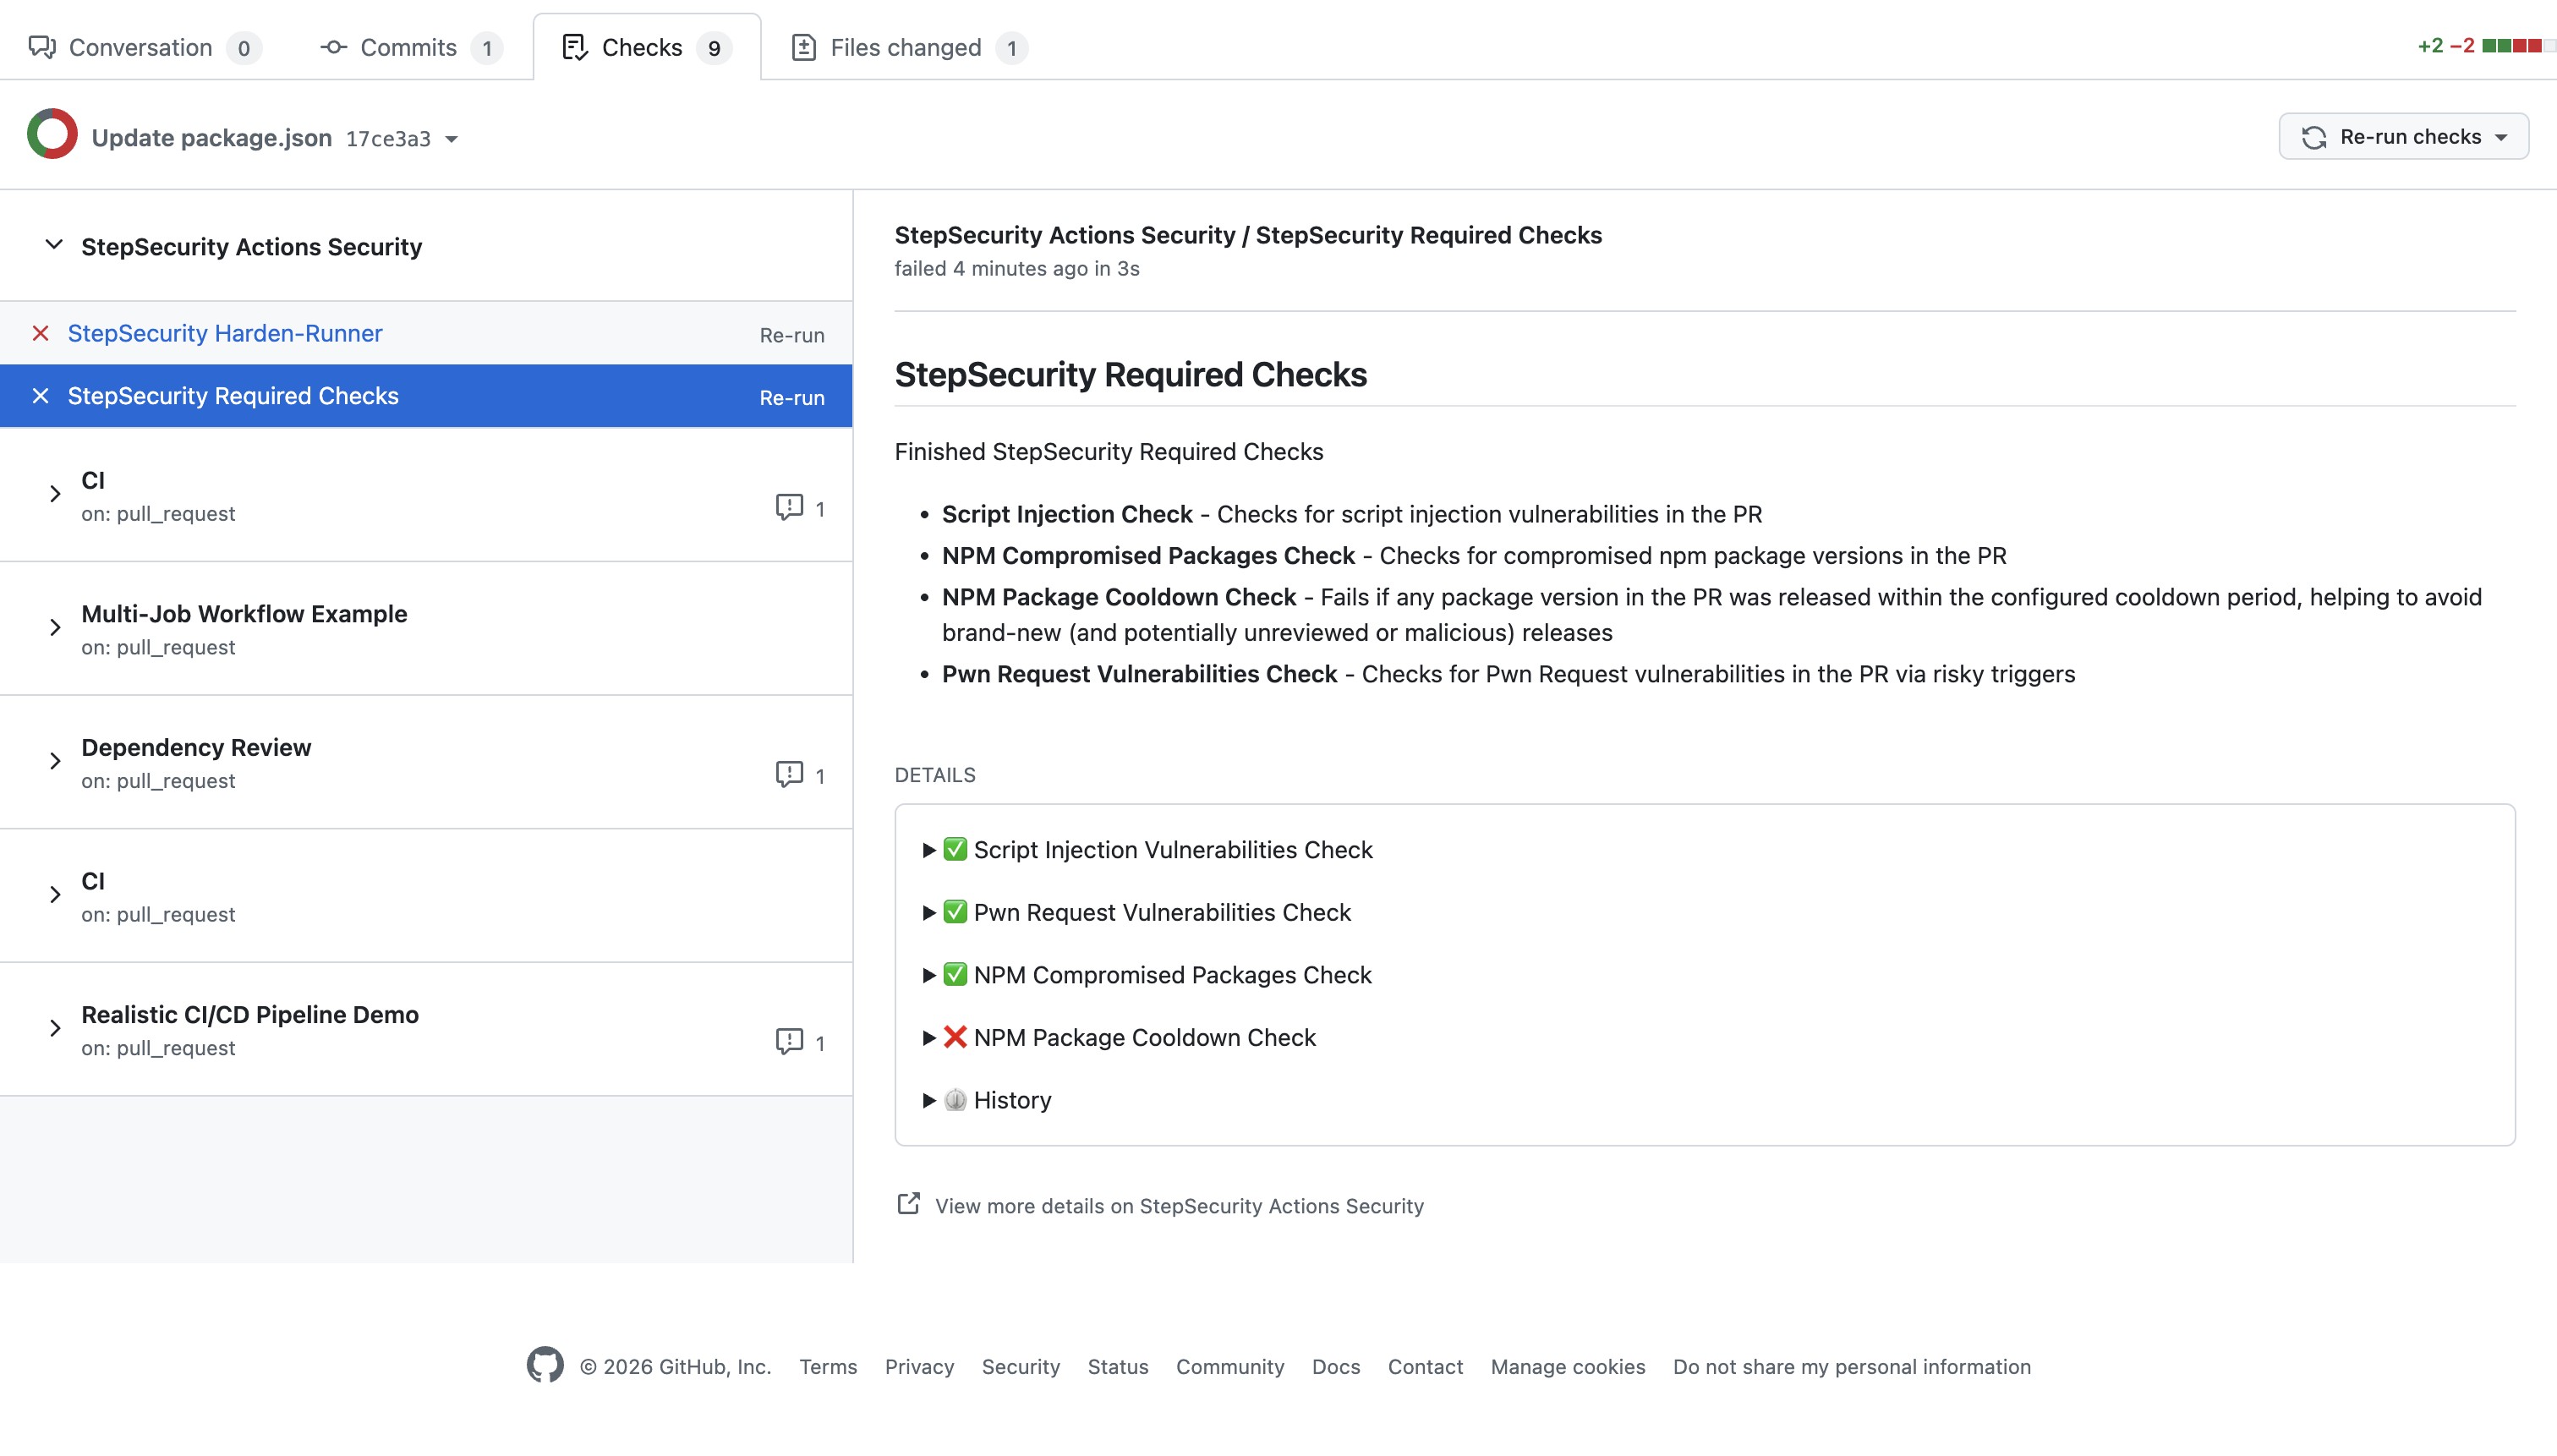
  • Cooldown Check: Automatically blocks dependencies published within the last 2 days (configurable), preventing the adoption of unvetted packages during the critical window when most supply chain attacks are discovered
  • Compromised Updates Check: Maintains a real-time database of compromised packages, often updated before official CVEs are published, blocking known malicious dependencies at the pull request level

StepSecurity enforcing security checks on a GitHub PR

Stage 3: CI/CD Pipeline Security

Product: Harden-Runner + Actions Governance  

Protection: Runtime monitoring, network egress control, baseline anomaly detection, secret protection, third-party Actions security

Your CI/CD pipelines have become the primary target for sophisticated attackers. Harden-Runner provides "EDR for CI/CD," monitoring every process, network call, and file access during your builds, establishing baselines and detecting anomalous behavior that indicates compromise. Actions Governance assesses the risk of third-party Actions and provides secure alternatives (StepSecurity Maintained Actions). For workflow files, StepSecurity identifies and remediates insecure workflow configurations org-wide with a single policy update.

Stage 4: Registry & Artifact Security

Product: Artifact Monitor + npm Package Search Protection: Artifact integrity verification, malicious package detection, registry monitoring

Package registries serve as both attack vectors and propagation mechanisms. Our registry protection monitors for malicious artifacts, verifies integrity, and prevents compromised packages from entering your supply chain.
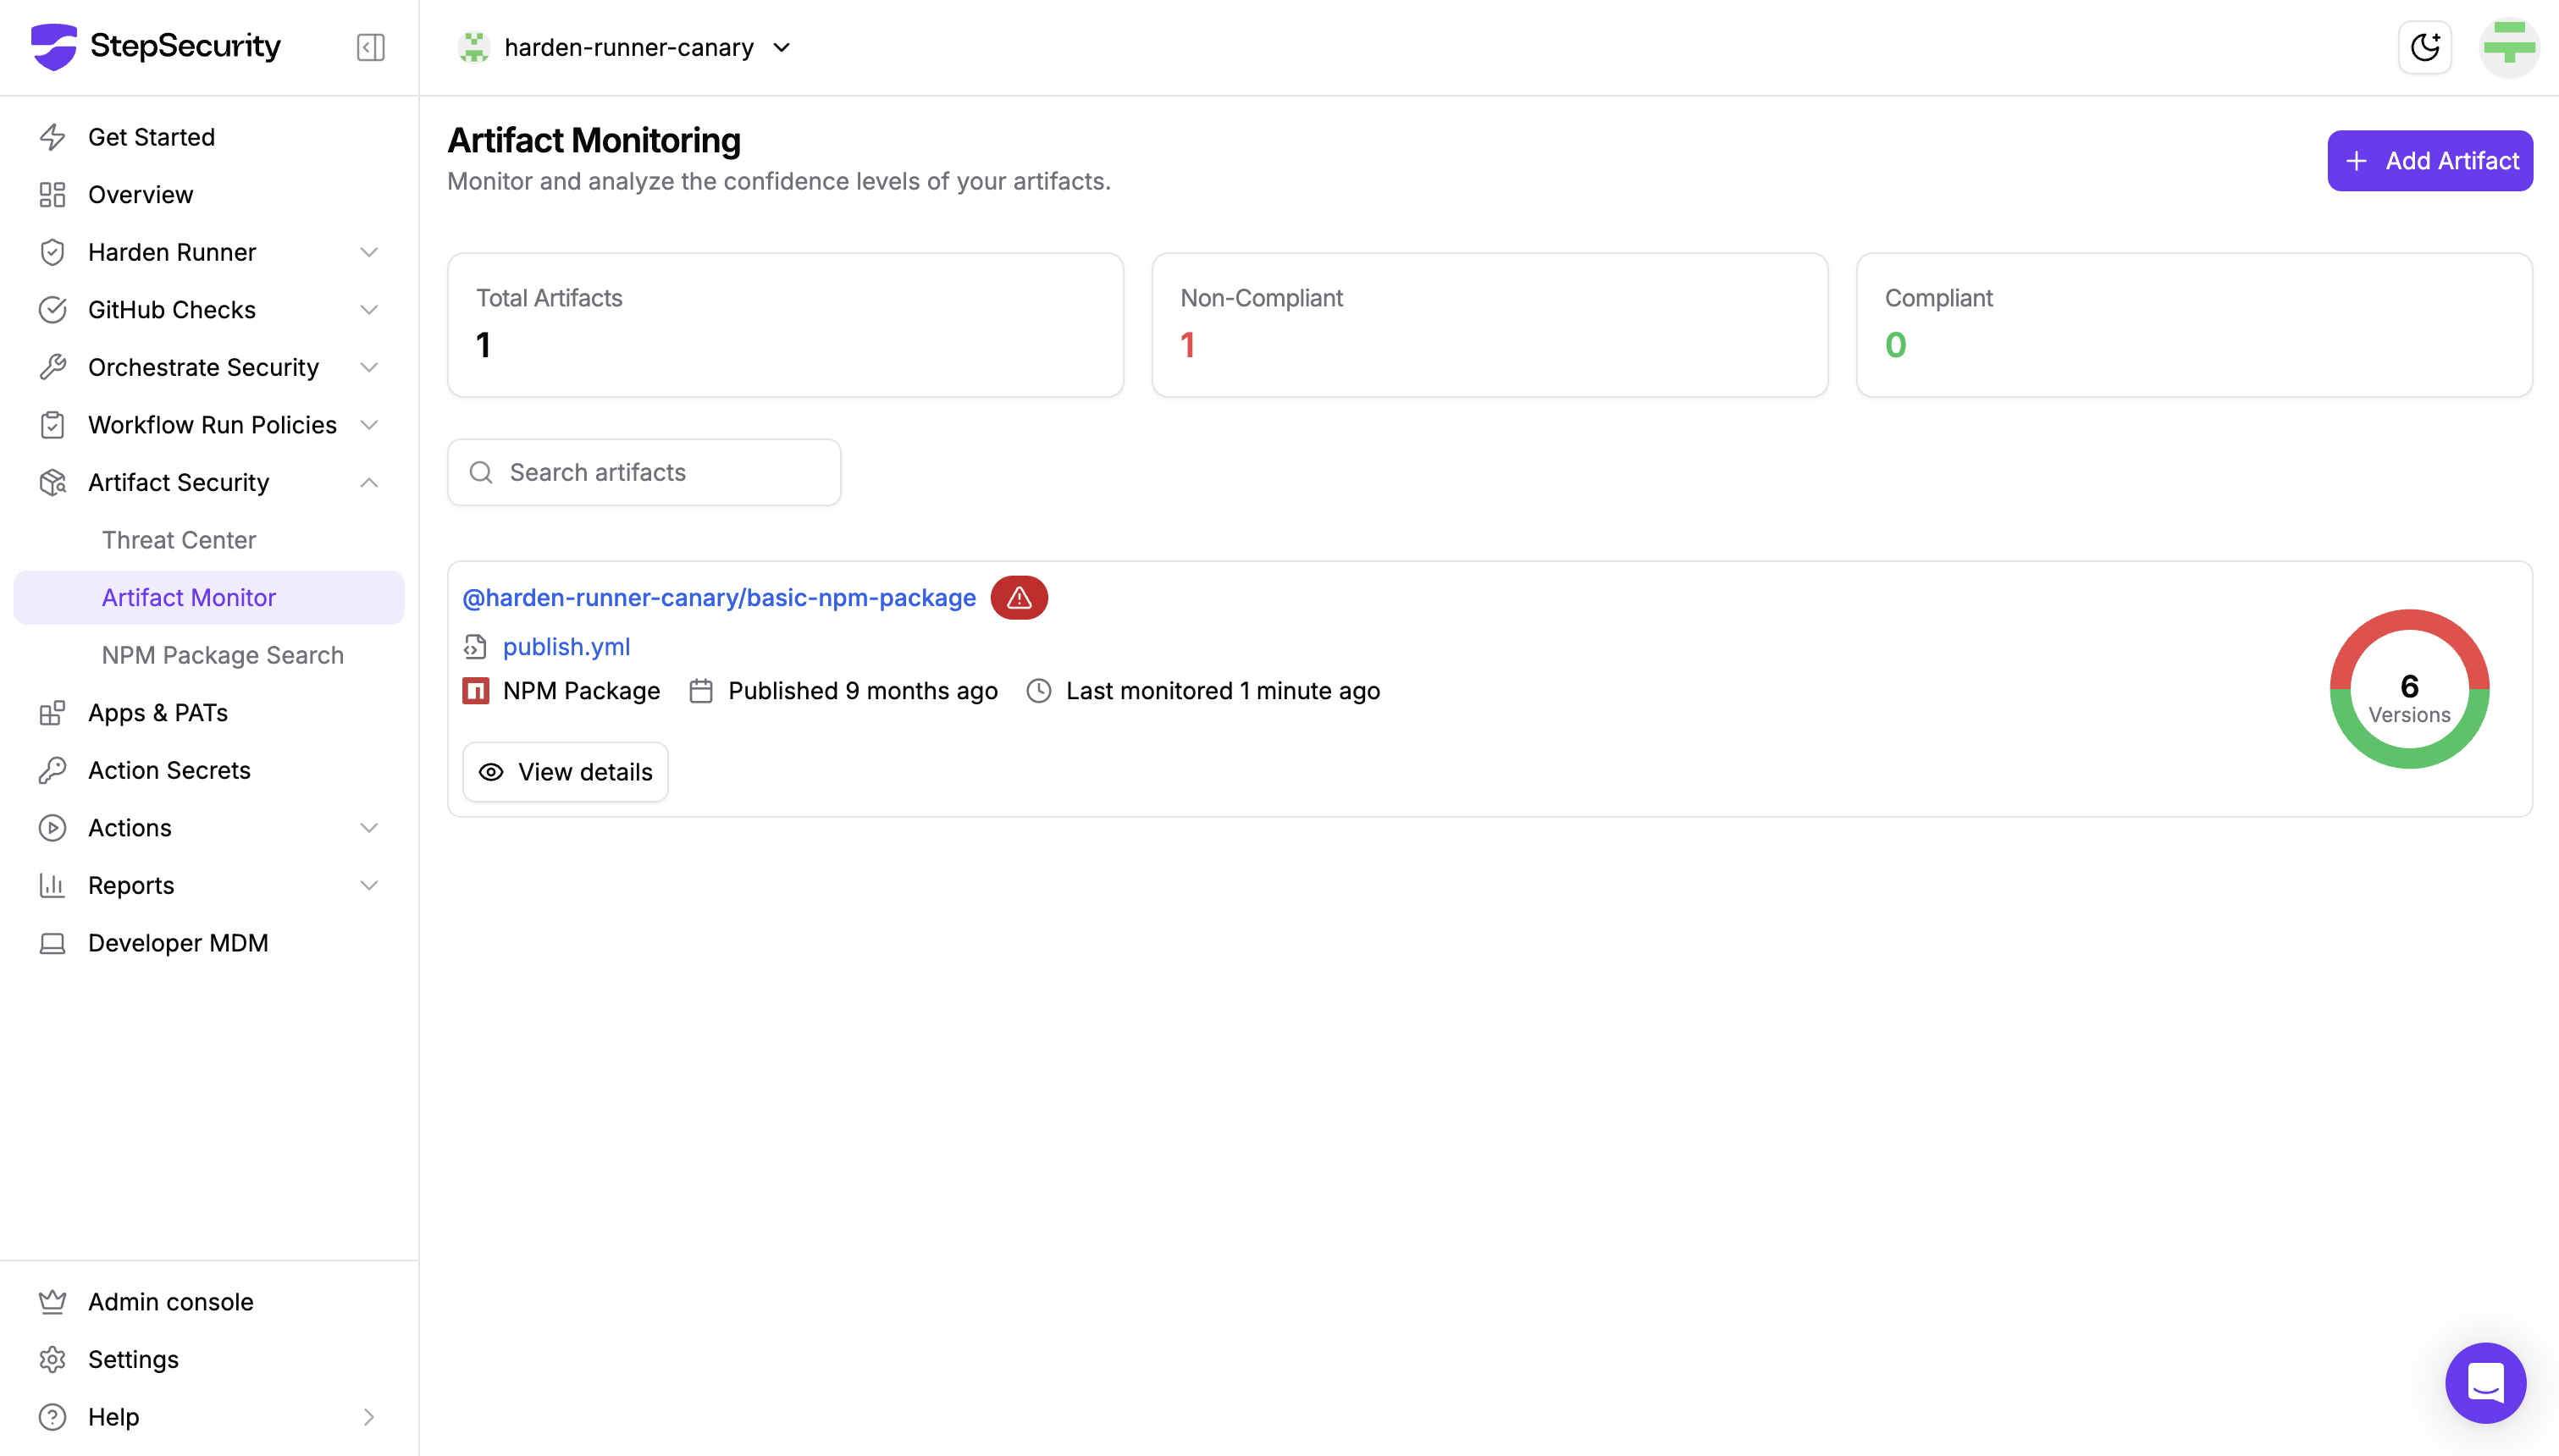
StepSecurity Artifact Monitor

Why Complete Coverage Matters

Modern supply chain attacks succeed because they exploit the gaps between security tools. An attacker blocked at the CI/CD level will pivot to developer machines. A registry-focused defense will miss VCS compromises. Point solutions create point failures.

The Shai-Hulud campaign perfectly illustrates this reality—it succeeded by moving fluidly between developer endpoints, CI/CD systems, package registries, and back to endpoints. This validates the multi-pillar approach that frameworks like SITF advocate for, and demonstrates why StepSecurity built unified defense across these critical attack stages.

By securing the development and delivery pipeline comprehensively, StepSecurity prevents attacks from reaching production in the first place—stopping supply chain compromises at their source rather than trying to detect them after deployment.

With StepSecurity's comprehensive platform:

  • Defense in depth: Multiple intervention opportunities across the development and delivery pipeline
  • Unified visibility: Correlation of threats across all critical SDLC stages
  • Coordinated response: Integrated incident response throughout the development lifecycle
  • Continuous protection: Real-time defense at the stages where attacks most commonly begin and spread

Ready Today, Not Tomorrow

While the industry debates frameworks and threat models, StepSecurity customers are already protected. Our platform is deployed across thousands of organizations, actively blocking supply chain attacks every day.

The question isn't whether you need SDLC security—recent attacks have settled that debate. The question is whether you want theoretical frameworks or actual protection.

Don't wait for the next Shai-Hulud. The time for frameworks has passed—the time for protection is now. Start your free trial today and see StepSecurity block real CI/CD threats in real time.