



惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

Google DeepMind News
L
LangChain Blog
H
Help Net Security
博客园_首页
T
Tailwind CSS Blog
Microsoft Security Blog
T
The Blog of Author Tim Ferriss
雷峰网
雷峰网
Recent Announcements
D
DataBreaches.Net
U
Unit 42
Vercel News
Vercel News
I
InfoQ
Martin Fowler
Martin Fowler
Microsoft Azure Blog
Apple Machine Learning Research
S
SegmentFault 最新的问题
Jina AI
Jina AI
博客园 - 叶小钗
博客园 - 【当耐特】
罗磊的独立博客
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
月光博客
月光博客
Last Week in AI
Last Week in AI

Step Security Blog

Announcing Dependabot Configuration Enhancements: Cooldown and Group Support - StepSecurity Securing Vibe Coding and AI Coding Agents: An End-to-End Approach with StepSecurity - StepSecurity Introducing StepSecurity Dev Machine Guard: Protecting Developer Machines from Supply Chain Attacks - StepSecurity Top 2024 Predictions for CI/CD Security - StepSecurity Dev Machine Guard Is Now Open Source: See What's Really Running on Your Developer Machine - StepSecurity Datadog's DevSecOps 2026 Report Validates What We've Been Building - StepSecurity hackerbot-claw: An AI-Powered Bot Actively Exploiting GitHub Actions - Microsoft, DataDog, and CNCF Projects Hit So Far - StepSecurity Cline Supply Chain Attack Detected: cline@2.3.0 Silently Installs OpenClaw - StepSecurity StepSecurity’s Unified Protection Across the SDLC Infrastructure Threat Framework (SITF) - StepSecurity @velora-dex/sdk Compromised on npm: Malicious Version Drops macOS Backdoor via launchctl Persistence - StepSecurity axios Compromised on npm - Malicious Versions Drop Remote Access Trojan - StepSecurity Behind the Scenes: How StepSecurity Detected and Helped Remediate the Largest npm Supply Chain Attack - StepSecurity 10 Layers Deep: How StepSecurity Stops TeamPCP's Trivy Supply Chain Attack on GitHub Actions - StepSecurity Malicious IoliteLabs VSCode Extensions Target Solidity Developers on Windows, macOS, and Linux with Backdoor - StepSecurity TeamPCP Plants WAV Steganography Credential Stealer in telnyx PyPI Package - StepSecurity litellm: Credential Stealer Hidden in PyPI Wheel - StepSecurity Checkmarx KICS GitHub Action Compromised: Malware Injected in All Git Tags - StepSecurity CanisterWorm: How a Self-Propagating npm Worm Is Spreading Backdoors Across the Ecosystem - StepSecurity Trivy Compromised a Second Time - Malicious v0.69.4 Release, aquasecurity/setup-trivy, aquasecurity/trivy-action GitHub Actions Compromised - StepSecurity bittensor-wallet 4.0.2 Compromised on PyPI - Backdoor Exfiltrates Private Keys - StepSecurity Malicious npm Releases Found in Popular React Native Packages - 130K+ Monthly Downloads Compromised - StepSecurity Malicious Polymarket Bot Hides in Hijacked dev-protocol GitHub Org and Steals Wallet Keys - StepSecurity ForceMemo: Hundreds of GitHub Python Repos Compromised via Account Takeover and Force-Push - StepSecurity xygeni-action Compromised: C2 Reverse Shell Backdoor Injected via Tag Poisoning - StepSecurity kubernetes-el Compromised: How a Pwn Request Exploited a Popular Emacs Package - StepSecurity How StepSecurity Caught a Release Storm in Microsoft’s @types Packages - StepSecurity Harden Runner Now Supports Windows and macOS GitHub Actions Runners - StepSecurity 10,000 Open-Source Projects Now Secured by Harden-Runner Community-Tier: A Milestone Three Years in the Making - StepSecurity 20+ Popular NPM Packages Compromised (Chalk, Debug, Strip-ANSI, Color-Convert, Wrap-ANSI...) - StepSecurity 2024 in Review: The Evolution of CI/CD Security & What's Next - StepSecurity
StepSecurity Detects Early Supply Chain Risk Signals in k...
2026-02-11 · via Step Security Blog

Supply chain security stories often focus on confirmed compromises. But many real risks begin much earlier, with small and legitimate changes that quietly weaken trust.

This post is about how a valid npm release introduced behavioral changes that reduced established trust signals, how those changes were detected early, and why this class of signal matters for both maintainers and consumers.

What We Observed

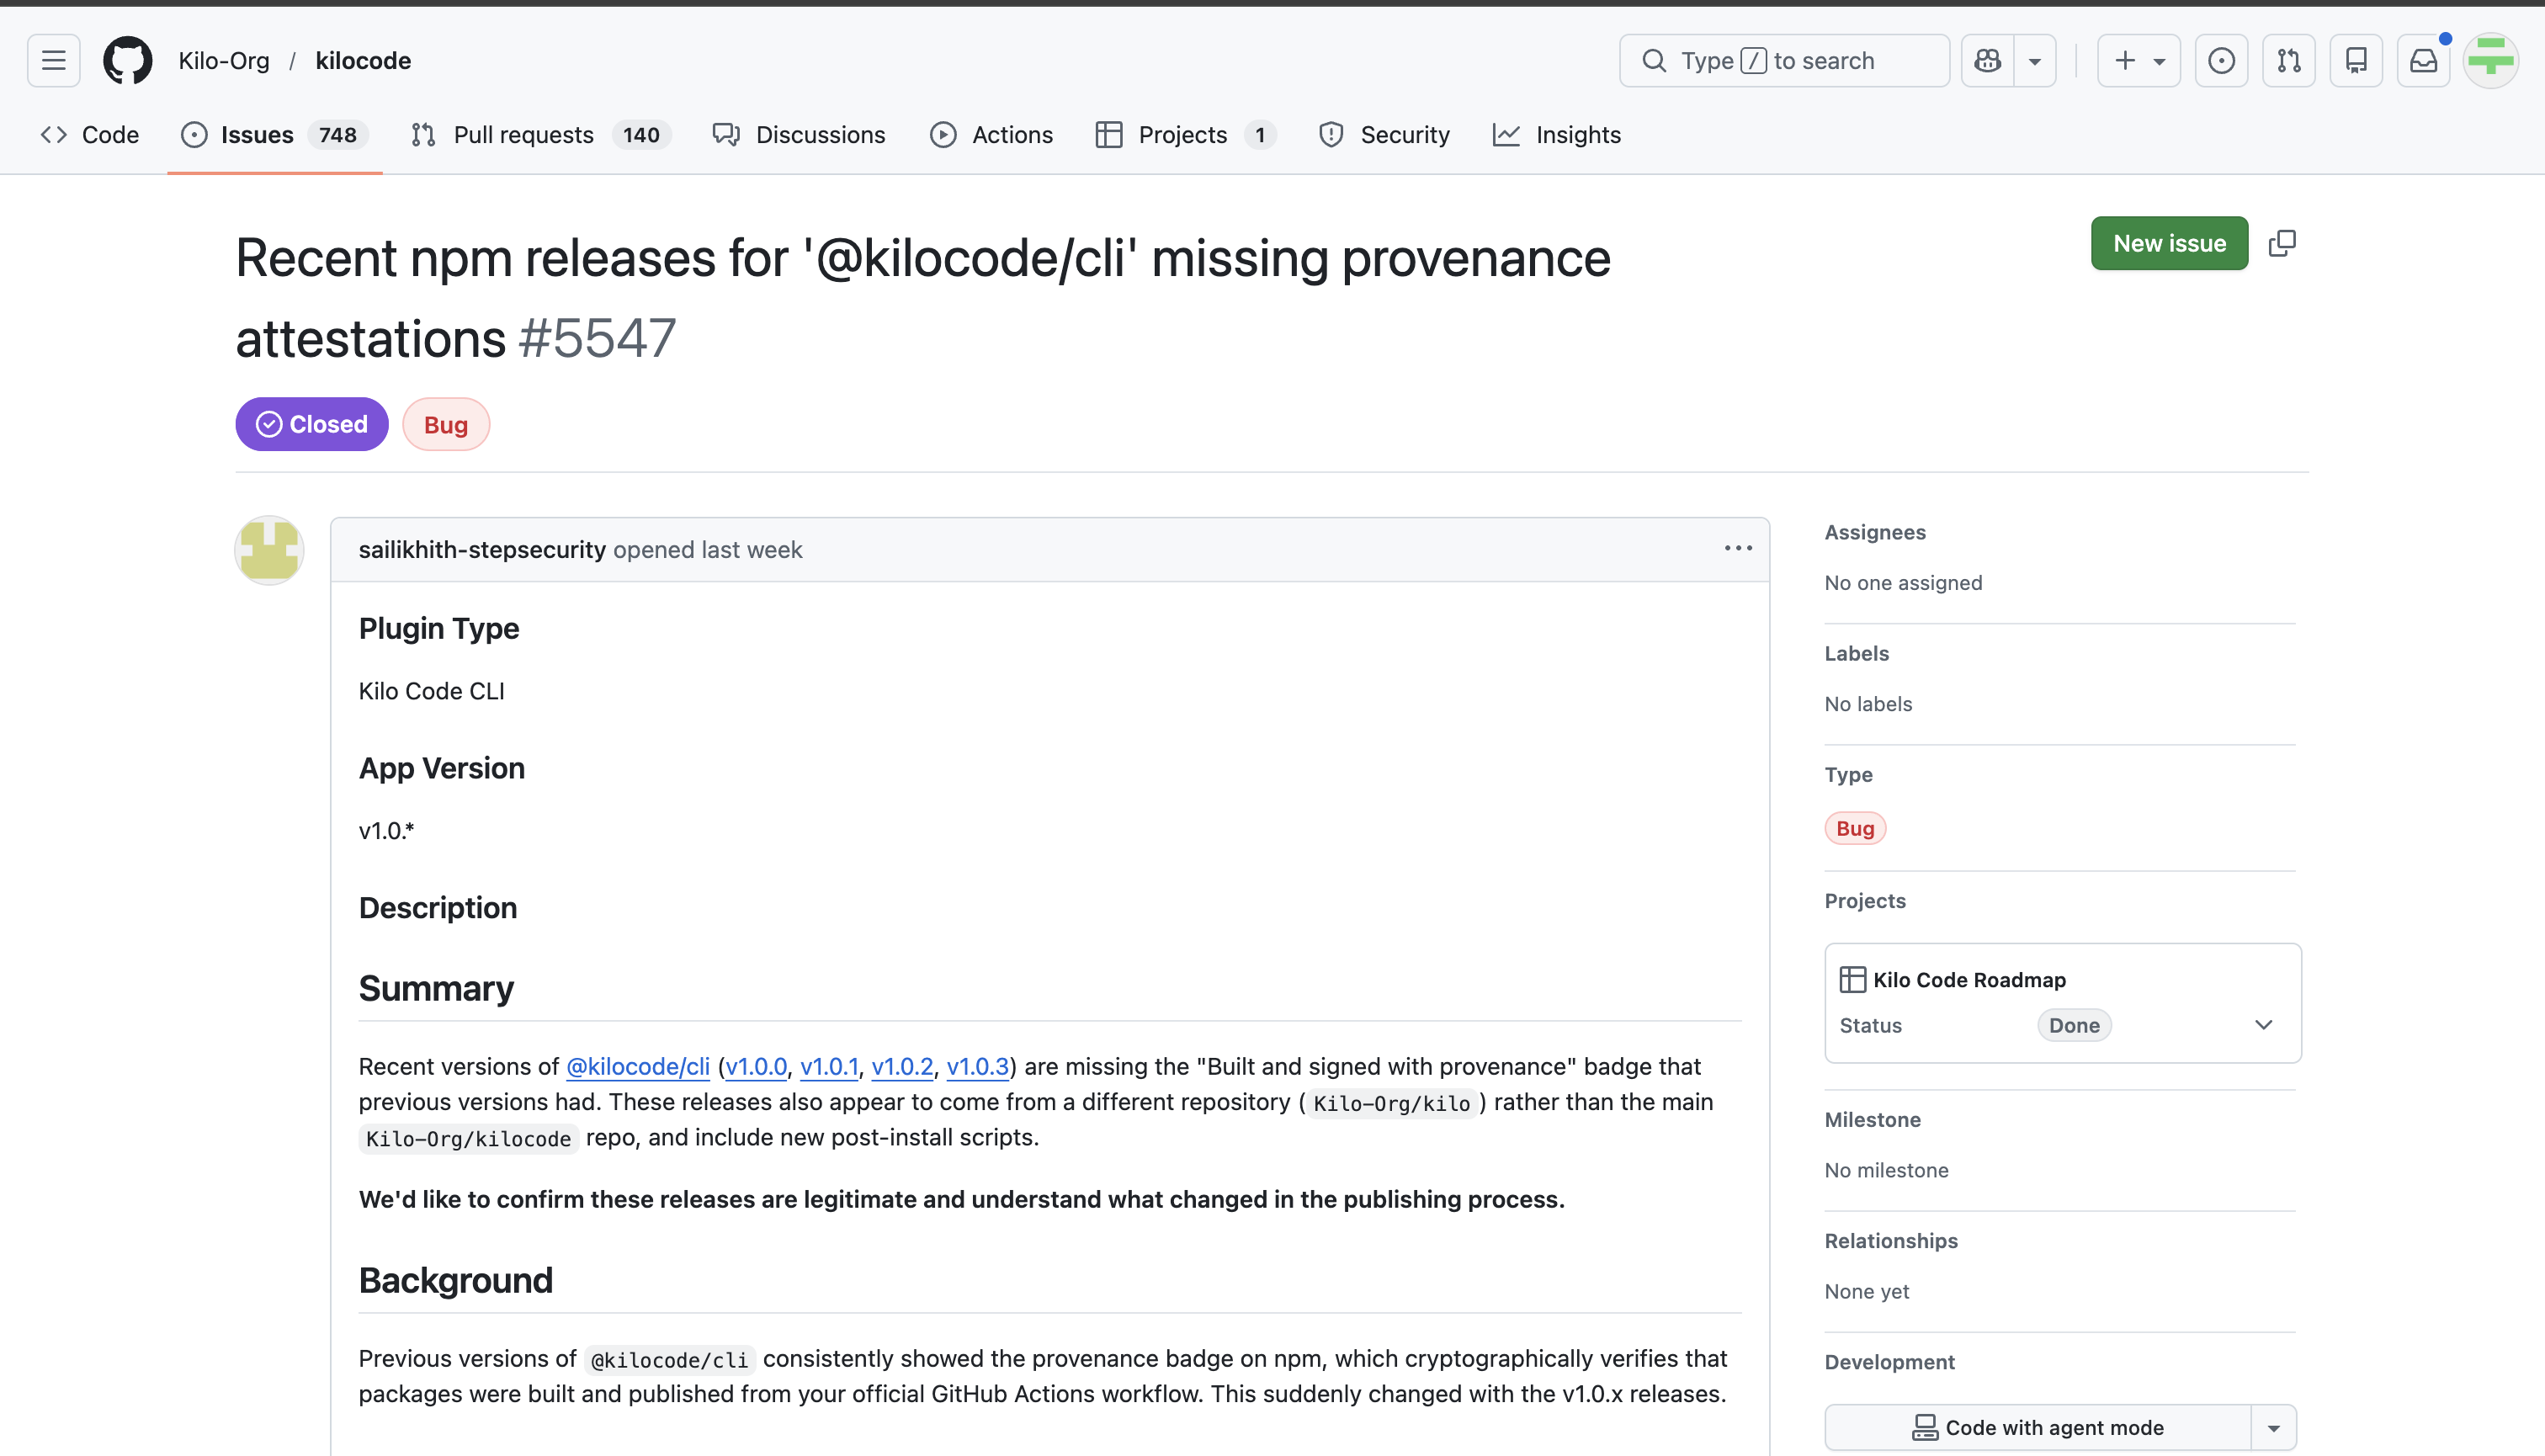
On January 29, StepSecurity’s monitoring flagged a new npm release of @kilocode/cli that differed from previous releases in several important ways.

The release showed:

  • Missing npm provenance attestations, even though earlier versions included them. The release pipeline had moved to a new repository, and provenance was not carried over.
  • A newly introduced postinstall script. The script performs OS and architecture detection and creates symlinks to platform-specific binaries such as @kilocode/cli-darwin-arm64. The binaries were not verified using checksums or signatures.

These changes stood out because they altered how the package is built, published, and executed during installation.

The release was legitimate. We opened a GitHub issue to flag the risk signals, and the maintainers responded quickly and fixed the issues.

You can see the full discussion here: https://github.com/Kilo-Org/kilocode/issues/5547
This was a positive outcome and a good example of maintainers engaging constructively on security feedback.

Why This Was Interesting

The reason this release mattered had nothing to do with malicious intent. It mattered because it changed trust assumptions.

Post-install scripts are a high-risk execution point

Post-install scripts run automatically on developer machines with user privileges. This makes them a powerful and sensitive mechanism.

Recent campaigns, including Shai-Hulud, have abused post-install scripts to gain an initial foothold by:

  • Dropping malicious binaries
  • Executing shell commands
  • Exfiltrating credentials

Introducing a new post-install script is therefore a meaningful behavioral change, even when the goal is convenience or platform support.

When binaries are fetched or linked during installation, verifying their integrity with checksums or signatures is critical.

Provenance can be lost during routine pipeline changes

Moving a release pipeline or changing repositories is common and often necessary.

What is easy to miss is the silent loss of provenance attestations during that transition.

Provenance provides cryptographic proof of where and how a package was built and published. When it disappears, consumers lose an important trust signal, even though the package may still function exactly as expected.

Nothing breaks, but trust is weakened.

Supply chain issues often start as valid releases

Many high-impact supply chain attacks did not begin with obviously malicious code.

They started with legitimate releases that introduced new behavior, new execution paths, or new assumptions about trust.

By the time malware is present, the opportunity for early intervention is often gone.

This is why detecting behavioral changes matters.

How This Was Detected

This signal was identified by StepSecurity’s agentic package analysis platform, which continuously evaluates npm packages and releases in real time.

The system evaluated:

  • Changes in release behavior compared to prior versions
  • Loss of previously present provenance attestations
  • Introduction of install-time execution paths
  • Binary handling without integrity verification

This type of analysis focuses on deviation and risk signals, not just confirmed incidents.

Our goal is to surface these signals early, while there is still time to respond and fix issues before they escalate.

Best Practices for npm Maintainers

If you maintain npm packages, especially widely used CLI tools, a few practices can significantly improve trust:

  • Preserve provenance attestations across all releases. Even when changing repositories or CI pipelines, ensure provenance remains intact.
  • Treat post-install scripts as a last resort. If you must use them, keep logic minimal and transparent.
  • Verify all binaries used during installation. Use checksums or signatures to ensure integrity.
  • Assume consumers are monitoring behavior changes. Clear documentation and consistency build long-term trust.