

惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

MongoDB | Blog
MongoDB | Blog
J
Java Code Geeks
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
D
DataBreaches.Net
腾讯CDC
GbyAI
GbyAI
I
InfoQ
博客园 - Franky
G
Google Developers Blog
Last Week in AI
Last Week in AI
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
V
Visual Studio Blog
Vercel News
Vercel News
博客园_首页
MyScale Blog
MyScale Blog
Martin Fowler
Martin Fowler
N
Netflix TechBlog - Medium
V
V2EX
T
The Blog of Author Tim Ferriss
M
MIT News - Artificial intelligence
雷峰网
雷峰网
H
Hackread – Cybersecurity News, Data Breaches, AI and More
大猫的无限游戏
大猫的无限游戏
The GitHub Blog
The GitHub Blog

Step Security Blog

Securing Vibe Coding and AI Coding Agents: An End-to-End Approach with StepSecurity - StepSecurity Introducing StepSecurity Dev Machine Guard: Protecting Developer Machines from Supply Chain Attacks - StepSecurity Top 2024 Predictions for CI/CD Security - StepSecurity Dev Machine Guard Is Now Open Source: See What's Really Running on Your Developer Machine - StepSecurity Datadog's DevSecOps 2026 Report Validates What We've Been Building - StepSecurity hackerbot-claw: An AI-Powered Bot Actively Exploiting GitHub Actions - Microsoft, DataDog, and CNCF Projects Hit So Far - StepSecurity Cline Supply Chain Attack Detected: cline@2.3.0 Silently Installs OpenClaw - StepSecurity StepSecurity’s Unified Protection Across the SDLC Infrastructure Threat Framework (SITF) - StepSecurity @velora-dex/sdk Compromised on npm: Malicious Version Drops macOS Backdoor via launchctl Persistence - StepSecurity axios Compromised on npm - Malicious Versions Drop Remote Access Trojan - StepSecurity Behind the Scenes: How StepSecurity Detected and Helped Remediate the Largest npm Supply Chain Attack - StepSecurity 10 Layers Deep: How StepSecurity Stops TeamPCP's Trivy Supply Chain Attack on GitHub Actions - StepSecurity Malicious IoliteLabs VSCode Extensions Target Solidity Developers on Windows, macOS, and Linux with Backdoor - StepSecurity TeamPCP Plants WAV Steganography Credential Stealer in telnyx PyPI Package - StepSecurity litellm: Credential Stealer Hidden in PyPI Wheel - StepSecurity Checkmarx KICS GitHub Action Compromised: Malware Injected in All Git Tags - StepSecurity CanisterWorm: How a Self-Propagating npm Worm Is Spreading Backdoors Across the Ecosystem - StepSecurity Trivy Compromised a Second Time - Malicious v0.69.4 Release, aquasecurity/setup-trivy, aquasecurity/trivy-action GitHub Actions Compromised - StepSecurity bittensor-wallet 4.0.2 Compromised on PyPI - Backdoor Exfiltrates Private Keys - StepSecurity Malicious npm Releases Found in Popular React Native Packages - 130K+ Monthly Downloads Compromised - StepSecurity Malicious Polymarket Bot Hides in Hijacked dev-protocol GitHub Org and Steals Wallet Keys - StepSecurity ForceMemo: Hundreds of GitHub Python Repos Compromised via Account Takeover and Force-Push - StepSecurity xygeni-action Compromised: C2 Reverse Shell Backdoor Injected via Tag Poisoning - StepSecurity kubernetes-el Compromised: How a Pwn Request Exploited a Popular Emacs Package - StepSecurity How StepSecurity Caught a Release Storm in Microsoft’s @types Packages - StepSecurity Harden Runner Now Supports Windows and macOS GitHub Actions Runners - StepSecurity 10,000 Open-Source Projects Now Secured by Harden-Runner Community-Tier: A Milestone Three Years in the Making - StepSecurity 20+ Popular NPM Packages Compromised (Chalk, Debug, Strip-ANSI, Color-Convert, Wrap-ANSI...) - StepSecurity 2024 in Review: The Evolution of CI/CD Security & What's Next - StepSecurity How to Use Docker in Actions Runner Controller (ARC) Runners Securely - StepSecurity
Maven Support Comes to GitHub Checks and OSS Package Sear...
2026-06-25 · via Step Security Blog

For most of the last two years, the loudest supply chain attacks lived in npm and PyPI. Java teams watched from a distance and assumed the blast radius stopped at JavaScript and Python. It does not.

When the Shai-Hulud worm came back for its second wave, it did not stay in npm. The same payload that hit PostHog's npm packages also surfaced on Maven Central, where an automated process that re-publishes npm modules as Maven artifacts had rebundled a compromised version before the mirrored copies were purged. Separately, attackers slipped a malicious lookalike of the widely trusted Jackson JSON library into Maven Central, using namespace impersonation and a multi-stage, obfuscated payload to deliver Cobalt Strike to anyone who pulled the wrong coordinate. The Java ecosystem is squarely in scope.

The uncomfortable part is why these attacks work. A compromised version gets published, a build resolves it, and the malicious artifact runs with whatever access that build has, often in CI, often with secrets in reach. The window between "published" and "discovered" is where the damage happens, and traditional vulnerability scanners that wait for an official CVE are usually too slow to help. Java's transitive dependency trees, where a single direct dependency can pull in dozens of indirect ones, only widen the surface.

Until now, StepSecurity customers could close that window for npm and PyPI but not for Maven. Today that changes.

What's new

Maven is now a first-class ecosystem in two places, alongside npm and PyPI.

GitHub Checks

Two new PR Content Security controls bring the same protection Java teams have wanted to the pull request, before a risky dependency ever merges:
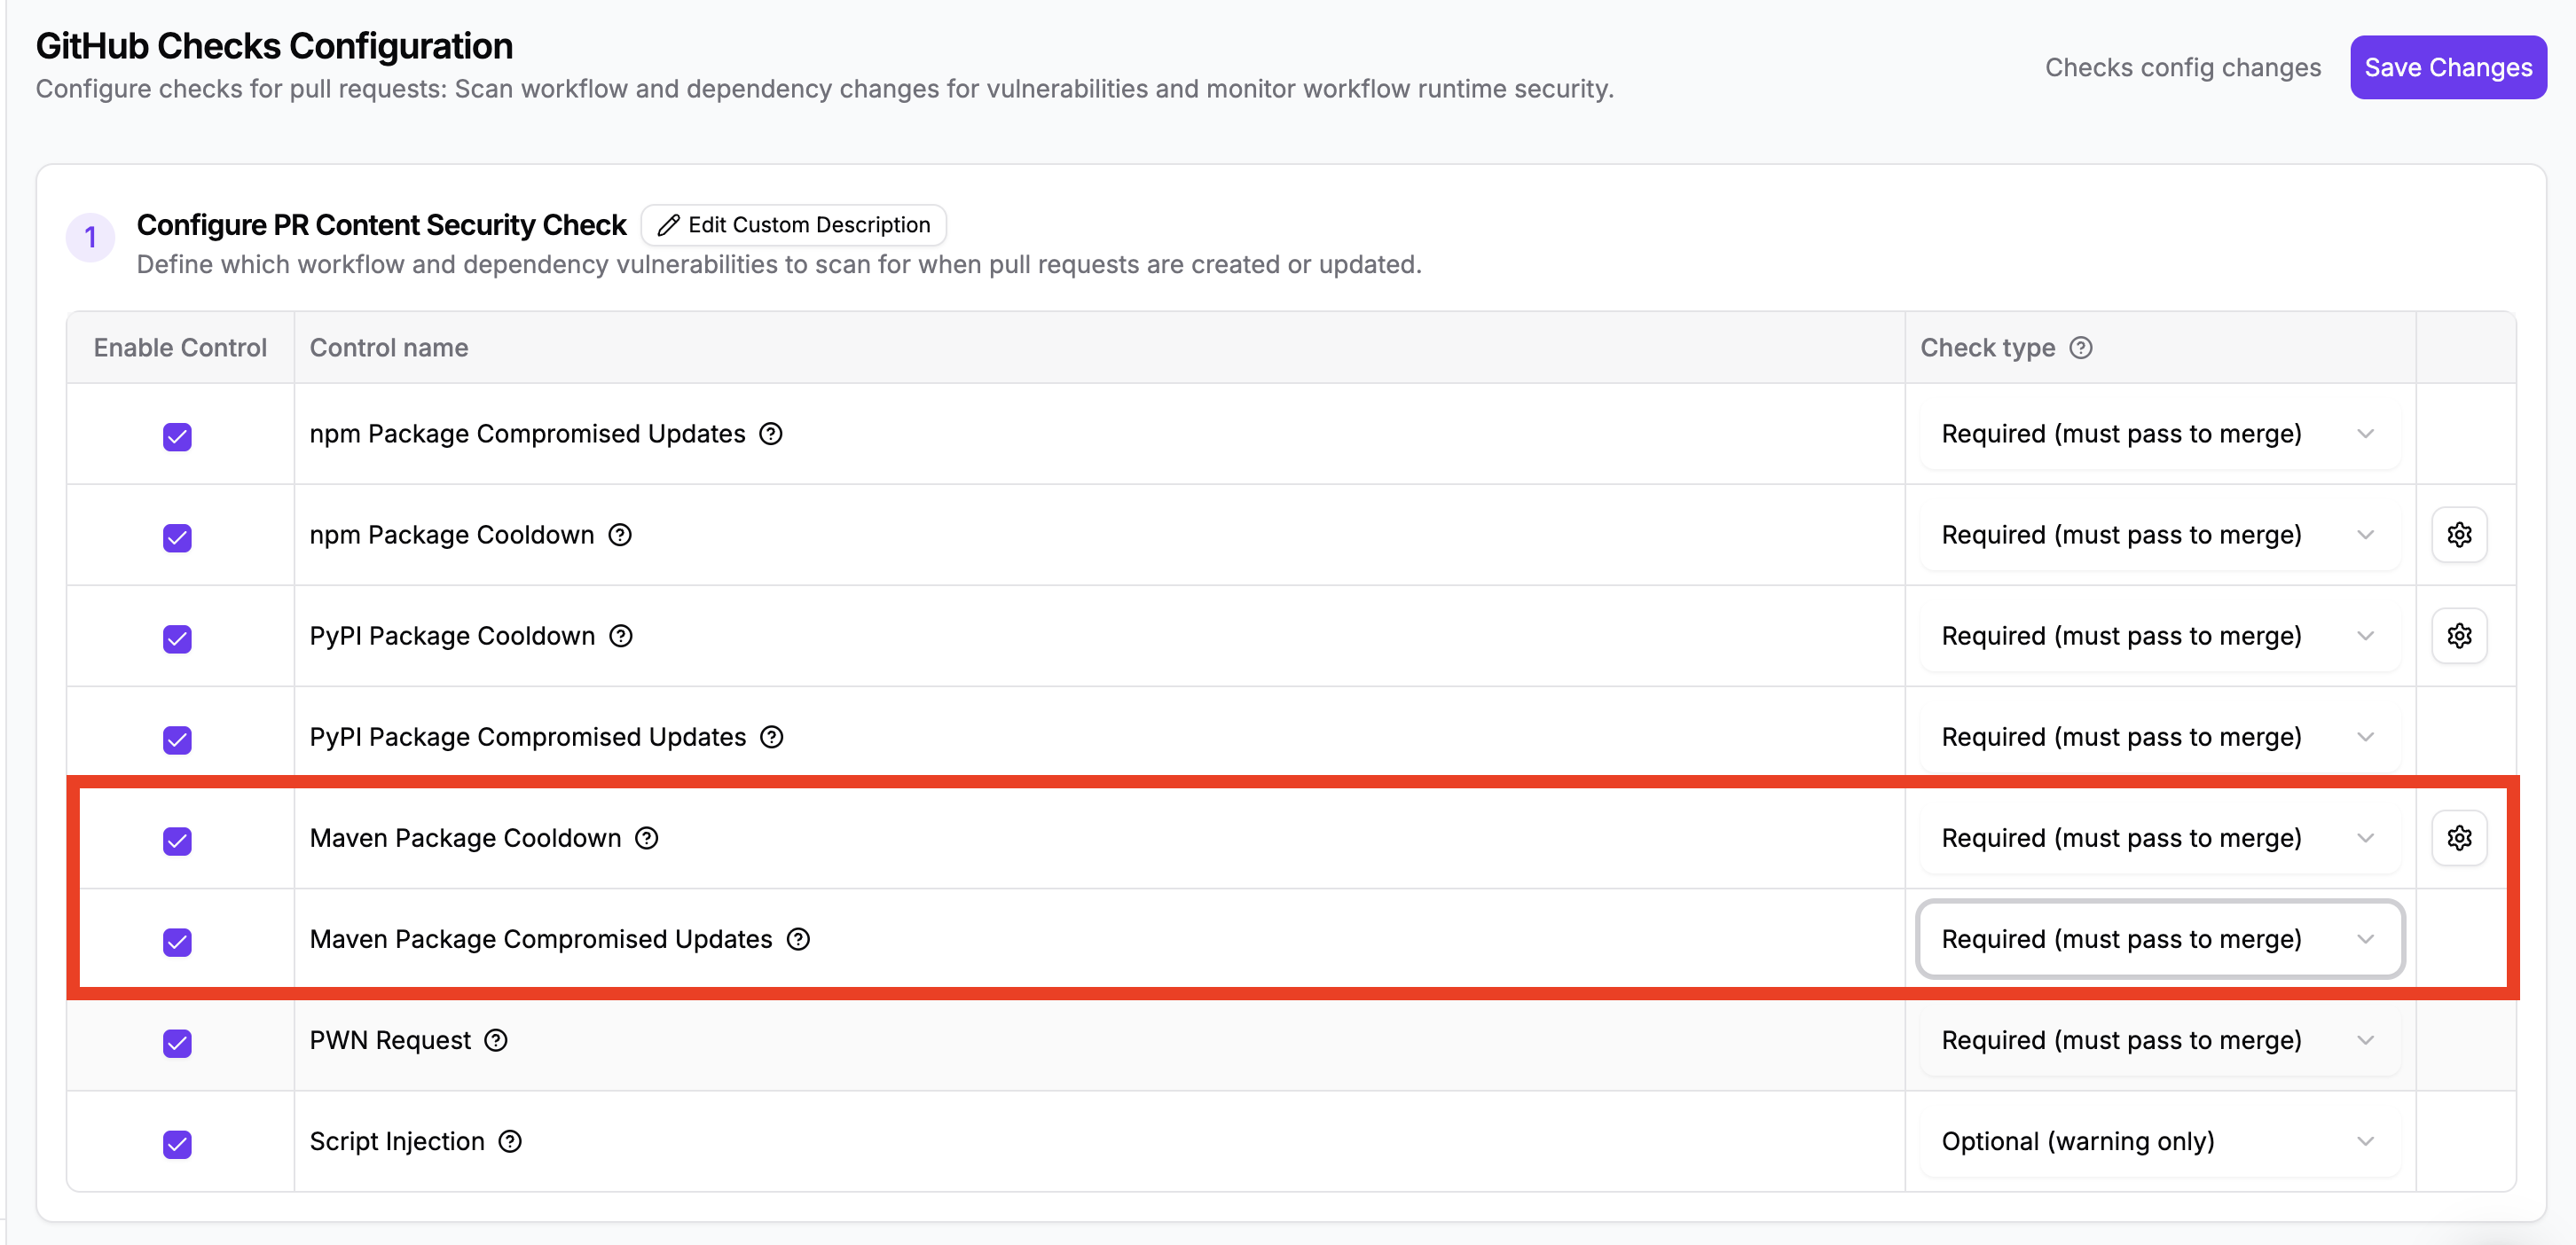
  • Maven Package Compromised Updates blocks any pull request that introduces or updates a Maven dependency flagged in StepSecurity's compromised-packages database. Because StepSecurity's SOC maintains that database in real time, often ahead of an official CVE, the check can stop a malicious release at the speed of the ecosystem rather than the speed of disclosure.
  • Maven Package Cooldown blocks pull requests that add recently published Maven versions until they age beyond a configurable cooldown window. Most malicious releases are caught within the first day or two of publication, so a short waiting period gives the ecosystem and StepSecurity's threat intelligence time to react before the version reaches your build.

Both controls can be set to Required (blocks the merge on failure) or Optional (advisory only), exactly like their npm and PyPI counterparts. If a critical patch genuinely needs to ship inside the cooldown window, the existing Approve All override applies here too.

OSS Package Search

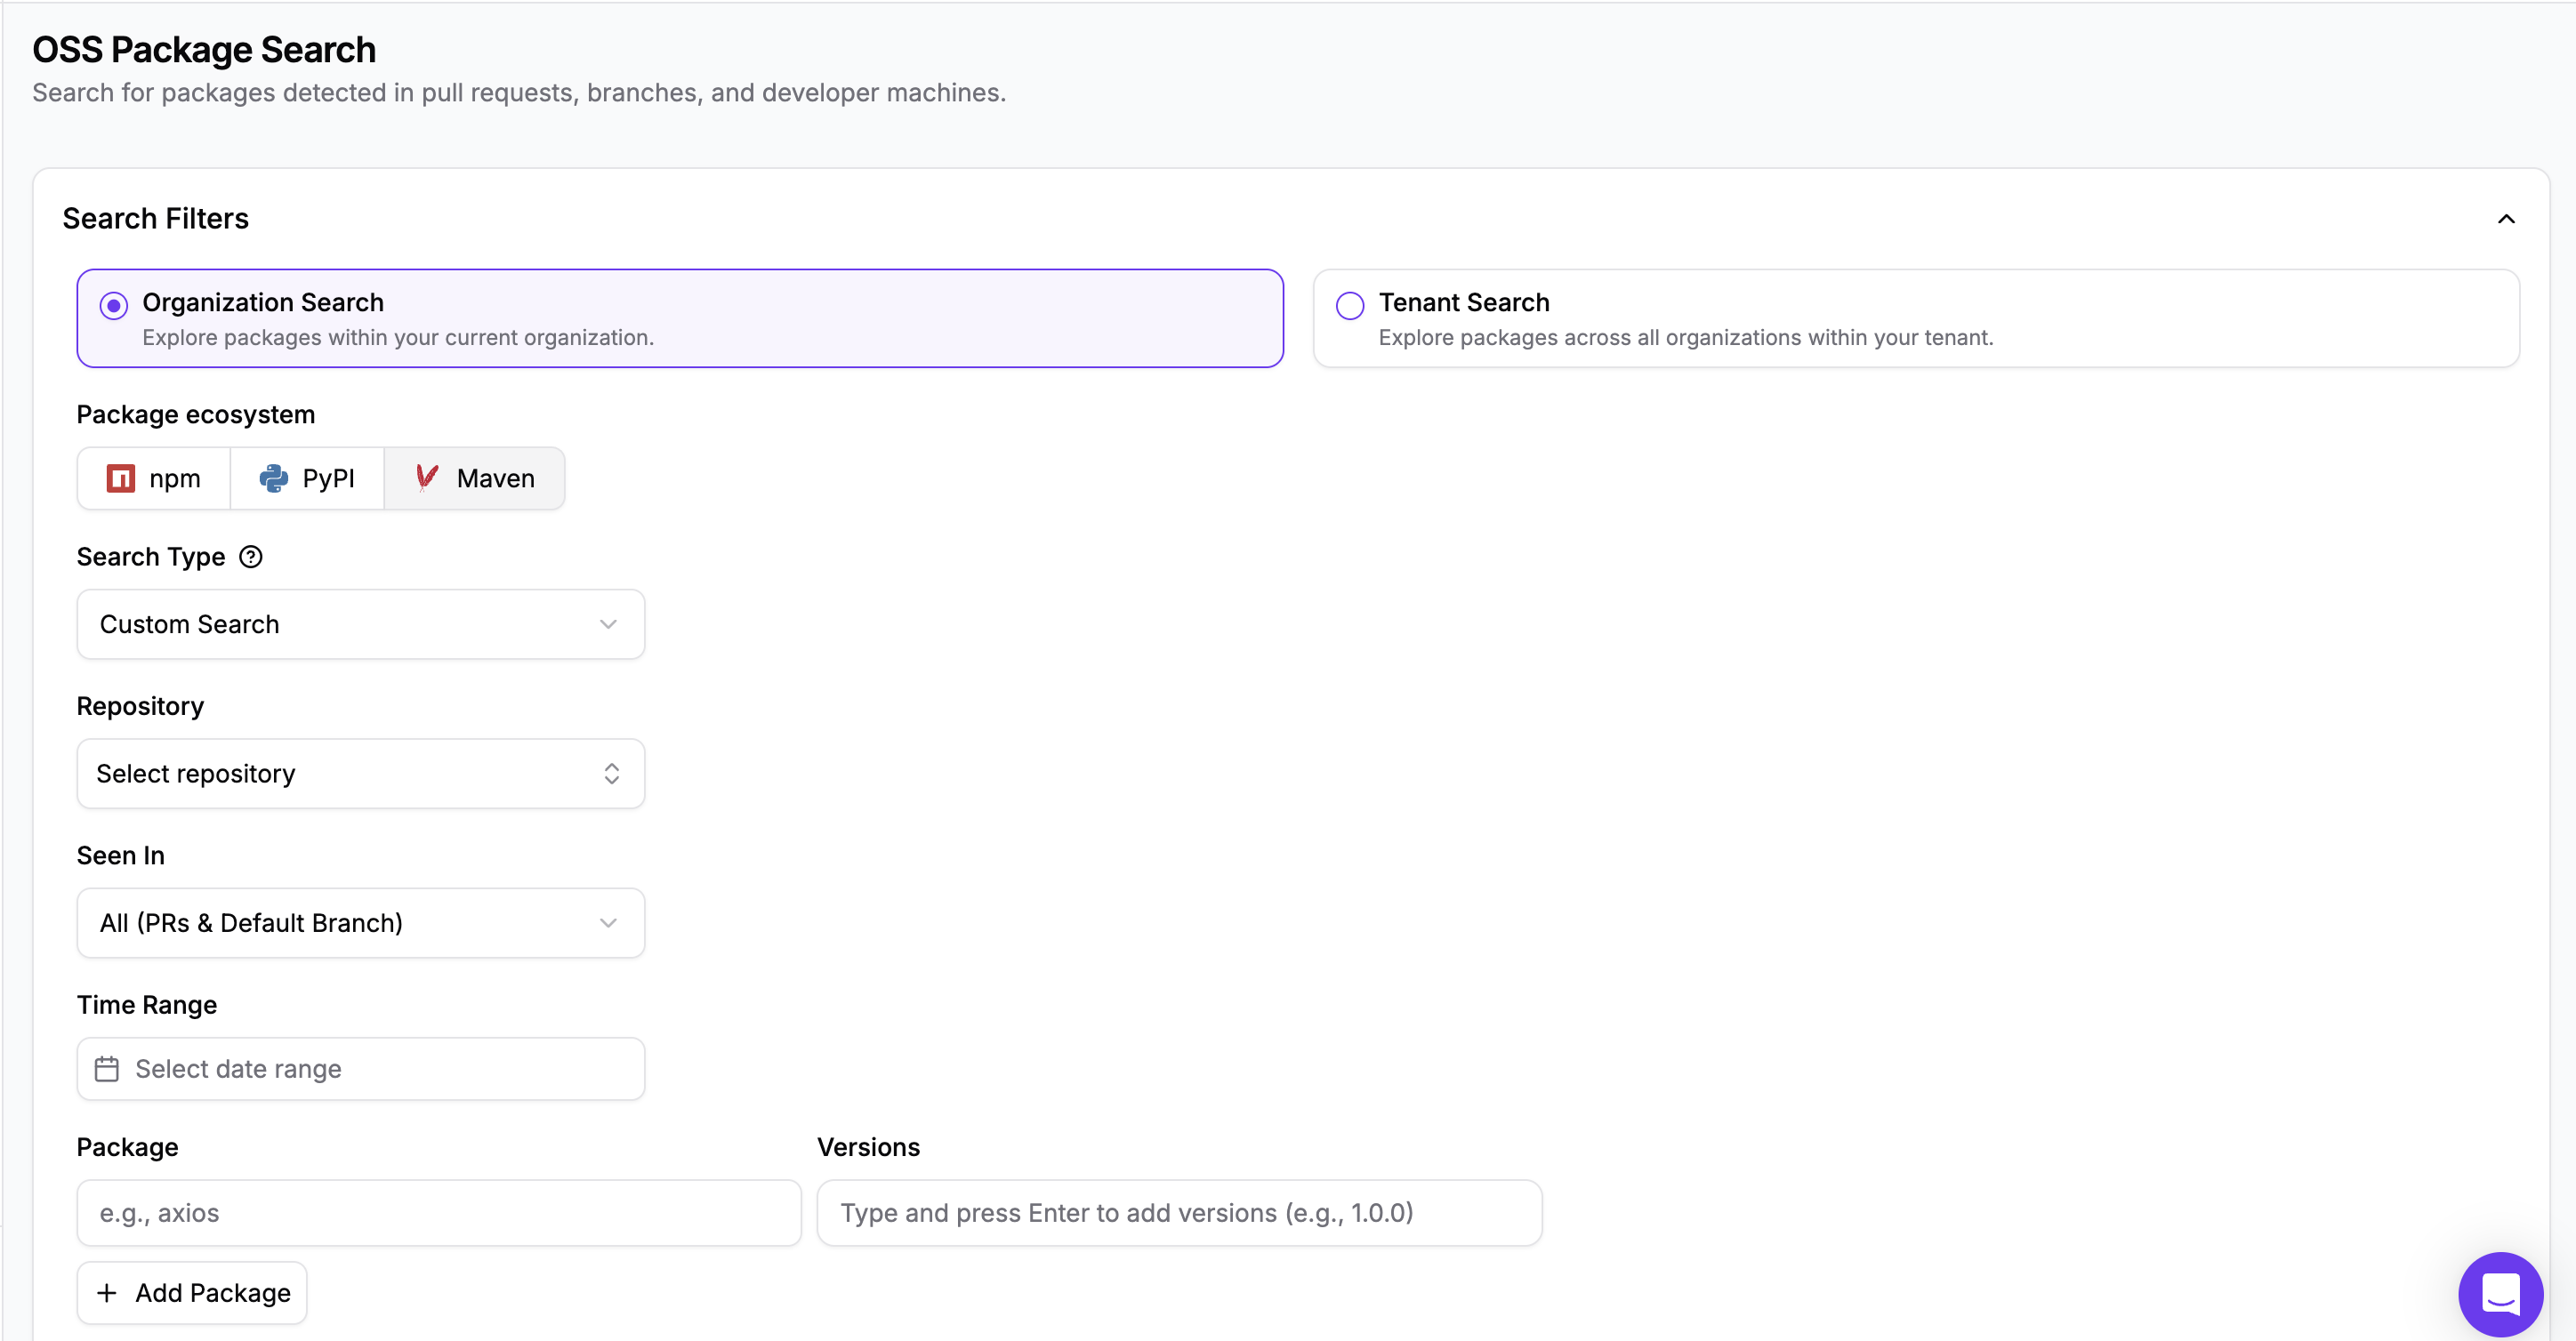
Maven now appears in the Package ecosystem toggle, so when a Maven package is reported compromised, you can immediately answer the only question that matters during an incident: where is it. OSS Package Search finds every place a specific Maven package and version appears across your pull requests, default branches, and developer machines, links CI/CD findings straight to the pull request that introduced the dependency, and lets you export the results to CSV for tracking remediation.
Coming soon

Maven support is launching in GitHub Checks and OSS Package Search first. Two more pieces are on the way:

  • Secure Registry will add Maven so that compromised and freshly published Java packages can be blocked at install time, the same way npm and PyPI already are. This extends the cooldown and compromised-package controls from the pull request all the way down to the registry layer, where every build and developer machine fetches its dependencies.
  • Dev Machine Guard will add Maven coverage on developer machines, so Java dependencies can be inventoried and audited across your fleet alongside npm and PyPI.

Getting started

Maven controls and search behave just like the npm and PyPI features you already use, so there is nothing new to learn:

  • In GitHub Checks, open Configuration, enable Maven Package Compromised Updates and Maven Package Cooldown, set each to Required or Optional, tune the cooldown window, and apply the controls to your repositories.
  • In OSS Package Search, select Maven from the Package ecosystem toggle and search for any package across your organization or tenant.

Java has been part of the software supply chain attack surface for a while. Now it is part of the same defenses you already trust for npm and PyPI. For the full picture of how StepSecurity tracks these campaigns, see How Harden-Runner detected Shai-Hulud in CNCF's Backstage repository.