








In fast-paced enterprise environments, deviations from defined security policies are inevitable. Workflows evolve, new actions are introduced, and configurations drift. Such deviations, if unresolved, create vulnerabilities that attackers can exploit.
A vivid example was the recent tj-actions breach, where the popular GitHub Action tj-actions/changed-files was compromised, leading organizations to rapidly pin dependencies across numerous workflows. Remediation efforts required painstaking manual updates across multiple repositories—complex, slow, and error-prone.
To address this critical challenge, StepSecurity is excited to announce a powerful new feature: Policy-Driven Automated Pull Requests, designed specifically to automate and simplify the remediation of security deviations.
When security deviations occur, immediate remediation is essential. But traditional approaches—email notifications, manual updates, or spreadsheet tracking—are inefficient and prone to human error. Without automation, organizations waste valuable hours, allowing vulnerabilities to linger. This manual process significantly slows down remediation, especially during security incidents like the tj-actions breach.
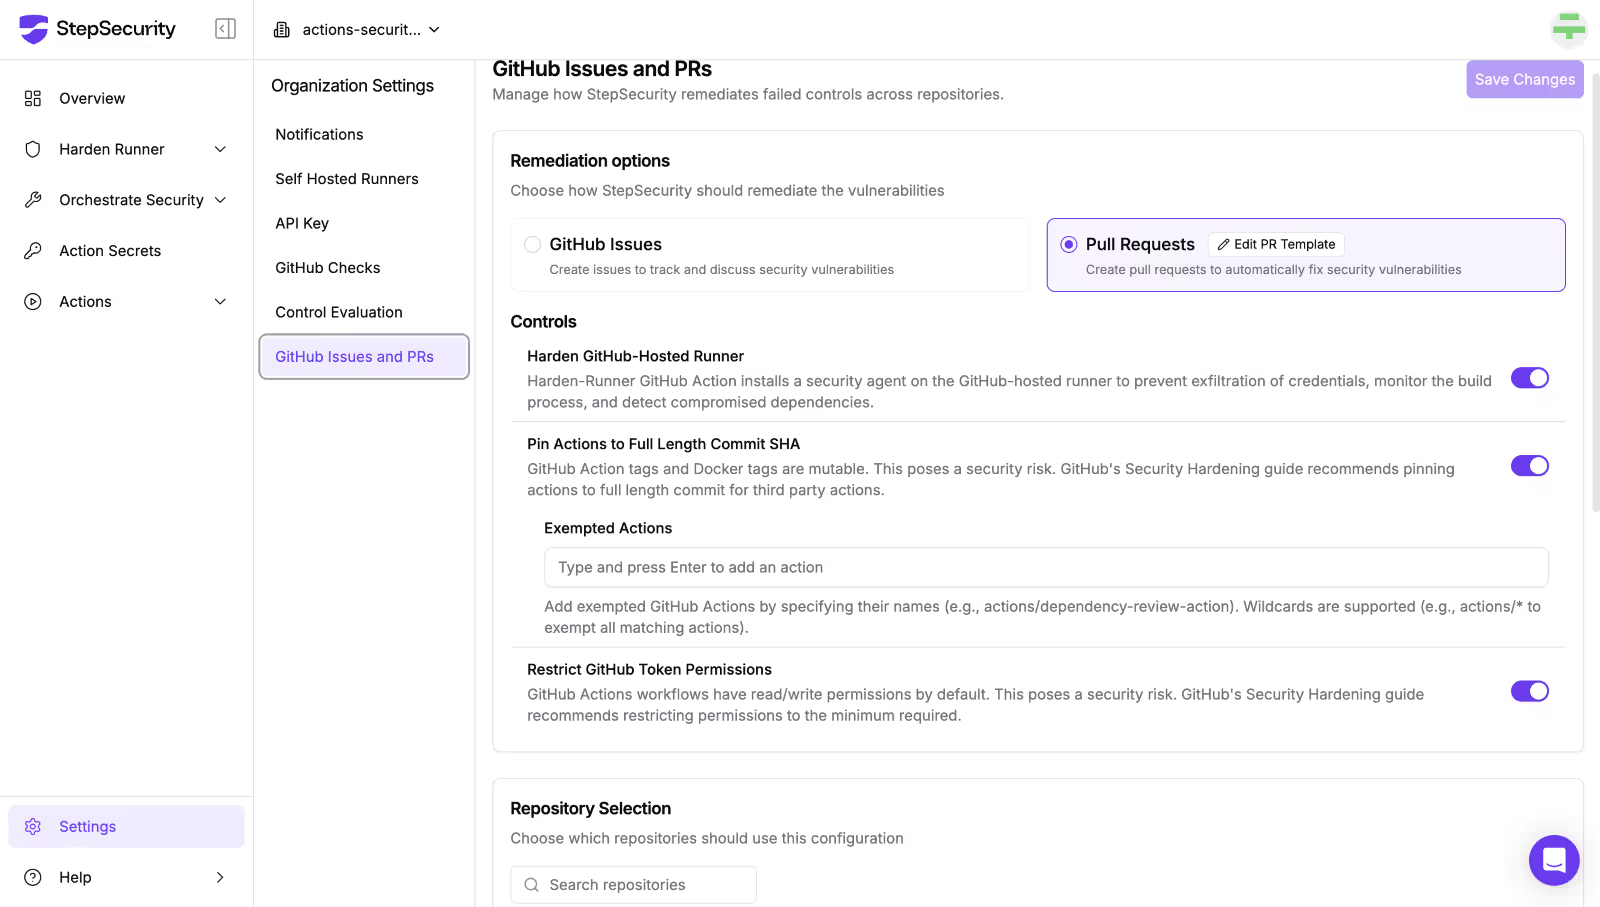
Our Policy-Driven Automated Pull Requests feature resolves these issues by automating security policy enforcement directly within GitHub. When deviations from security policies occur, StepSecurity automatically opens GitHub Issues or Pull Requests, providing immediate, actionable tasks.
Set the security policies your organization wants to enforce, such as pinned actions, minimal permissions, and Harden-Runner usage.
StepSecurity continuously scans your GitHub repositories to detect policy deviations instantly.
Once a deviation is detected, StepSecurity creates either a GitHub Issue or an automated Pull Request:
1. Issues provide notification and guidance.
2. Pull Requests deliver ready-to-review fixes directly into your workflows.
We recommend adopting automation gradually through our Crawl-Walk-Run approach to ensure smooth adoption across your organization:
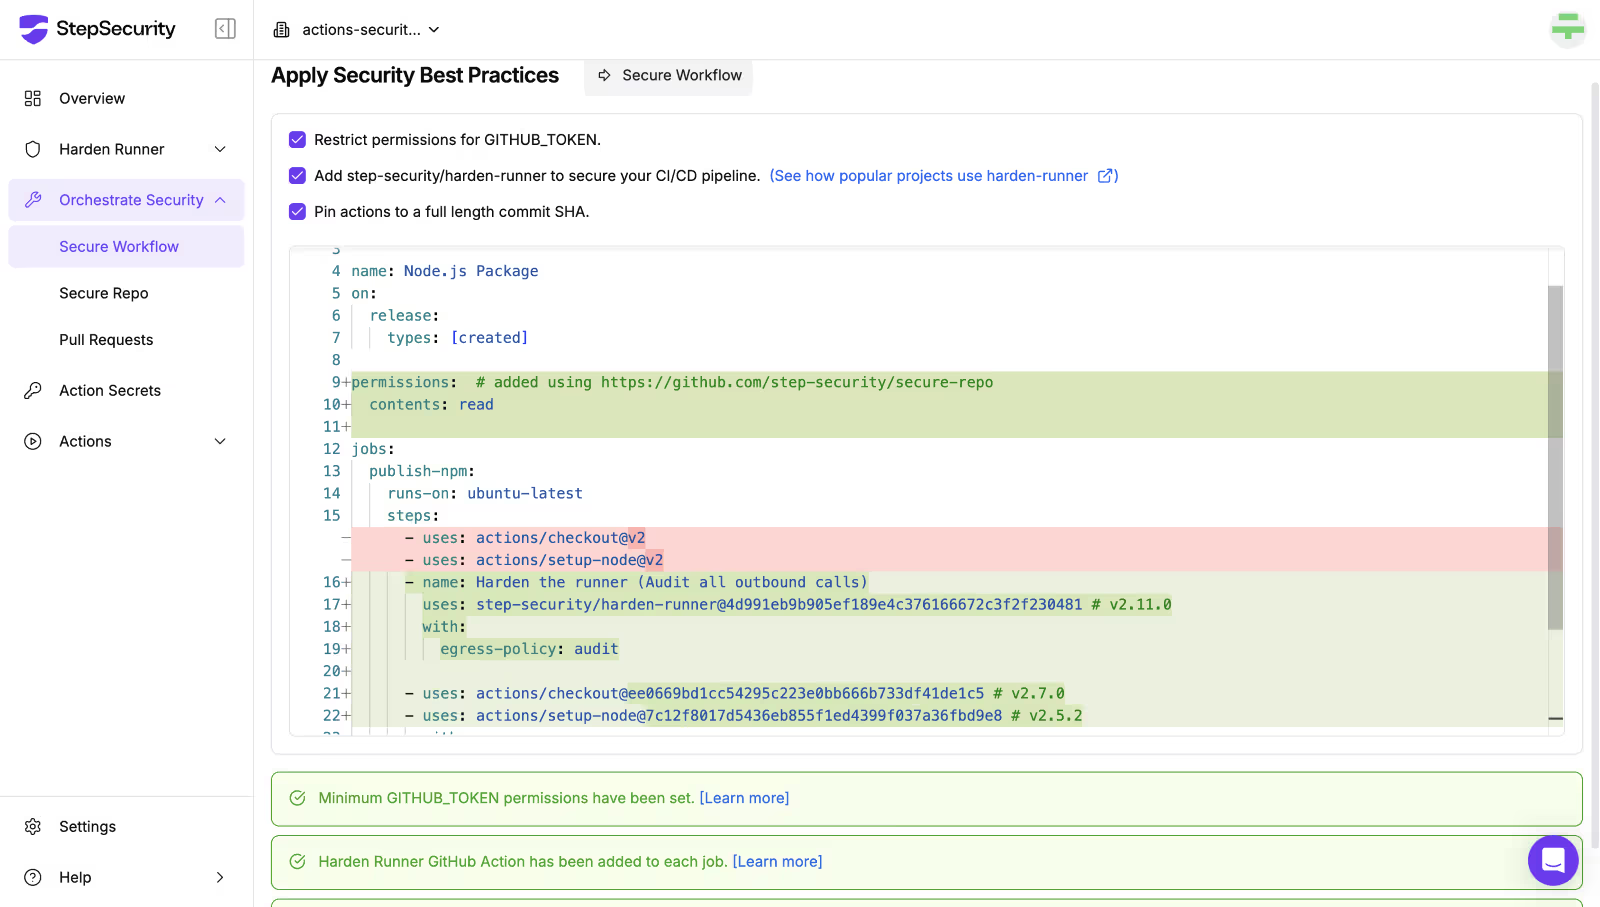
Begin your remediation journey by addressing security deviations one workflow at a time using StepSecurity Secure Workflow. This tool analyzes an individual GitHub Actions workflow file and automatically applies security best practices, such as pinning dependencies to specific commit SHAs, restricting permissions, and integrating Harden-Runner for robust runtime security. The Secure Workflow interface provides developers with clear recommendations and easy-to-review changes, fostering a deeper understanding of security principles and best practices.
After gaining confidence at the workflow level, you can scale your remediation efforts repository-wide using StepSecurity Secure Repo. Secure Repo scans all GitHub Actions workflows in a repository simultaneously, generating a comprehensive pull request containing all required security fixes. This holistic approach ensures consistent and complete security policy adherence across entire repositories with a single PR, significantly streamlining the remediation process.
Once comfortable with workflow and repo-level fixes, you can activate automated GitHub issue creation. Whenever StepSecurity detects a deviation from your configured security policies, it automatically opens a descriptive issue directly in the repository, clearly outlining the identified deviations and providing actionable guidance to fix them. Developers can also leverage ChatOps within these issues to perform various operations, such as creating pull requests directly from issue discussions. This integrated notification and interactive process places security directly into developers' everyday workflows, ensuring deviations are promptly addressed and reducing the risk of issues going unnoticed.
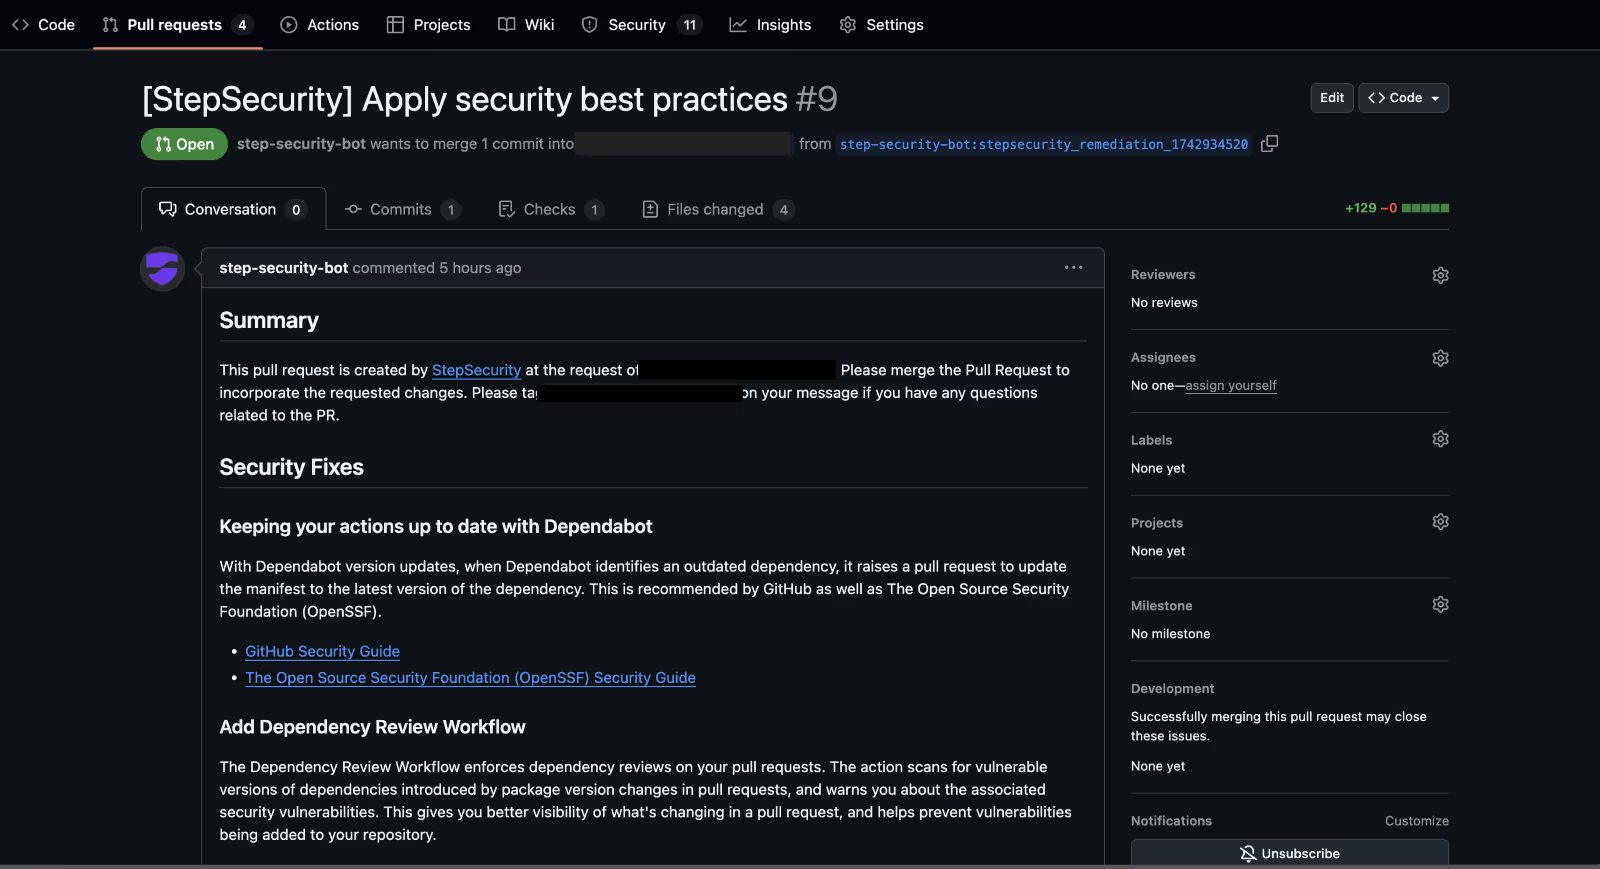
Finally, for maximum efficiency and swift remediation, enable full automation with Policy-Driven Automated Pull Requests. When enabled, StepSecurity directly generates pull requests for detected deviations, providing fully-prepared, security-enhancing changes that developers simply need to review and merge. By automating the complete cycle from detection to remediation, teams dramatically reduce the time and effort required to maintain optimal security posture.
A key philosophy behind this feature is shifting security left to developers in a way that’s easy and enables self-service. This feature empowers developers by integrating security directly into their existing workflows. Developers receive actionable tasks within familiar GitHub interfaces, eliminating context-switching and accelerating fixes.
The underlying remediation tools, Secure Workflow and Secure Repo, also remain available as self-service, fostering proactive security adoption among development teams.
Implementing Policy-Driven Automated Pull Requests is straightforward:
Customization is easy, allowing policy adjustments and tailored messaging to fit organizational needs and developer preferences.
With Policy-Driven Automated Pull Requests, StepSecurity delivers a robust, developer-centric approach to automated security remediation. This feature transforms security from a complex, manual burden into a seamless, automated, and integrated process—allowing teams to rapidly fix deviations, maintain compliance, and mitigate risks proactively. For more details, check out the feature documentation here.
Stay secure, move fast—let automation handle the rest.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。