




GitHub has introduced a powerful new capability: custom images for GitHub-hosted runners. This feature is now available in public preview and it fundamentally changes how organizations manage security and tooling inside their CI environments
With this capability now in public preview, teams can bake StepSecurity's Harden-Runner directly into their runner images, eliminating the need to add the Harden-Runner action to individual workflows while gaining persistent, organization-wide runtime protection.
Until now, securing GitHub Actions workflows with runtime protection on GitHub-hosted runners required a workflow-by-workflow approach. Teams had to add the Harden-Runner action as the first step in each job across every workflow file. While this provided comprehensive security monitoring and policy enforcement, it came with several operational challenges:
Workflow File Proliferation: Organizations with hundreds or thousands of workflows faced the tedious task of updating each workflow file individually. Even with automation tools like Secure Repo and Policy Driven PRs, maintaining consistency across a large codebase required ongoing effort.
Developer Friction: Every new workflow required developers to remember to include the Harden-Runner step. This created friction in the development process and opened the door to inconsistent security postures across different teams and projects.
Governance Gaps: Without centralized enforcement, security teams had limited ability to ensure every workflow was protected. A single forgotten step could leave a critical build pipeline vulnerable to supply chain attacks.
Maintenance Overhead: Updates to security policies or Harden-Runner versions required coordinated changes across multiple workflow files, creating operational burden for security and DevOps teams.
These challenges became particularly acute for enterprises running thousands of workflows across multiple repositories.
GitHub's custom runner images feature fundamentally changes this equation. Organizations can now create custom virtual machine images based on GitHub's curated base images and include all the tools, dependencies, and security agents they need. This includes the Harden-Runner agent.
When you bake Harden-Runner into a custom runner image, the security agent becomes part of the infrastructure itself rather than a step in each workflow. Every job that runs on a runner using this custom image automatically inherits the built-in runtime protection and monitoring capabilities without requiring any changes to workflow files.
This architectural shift delivers several immediate advantages:
Transparent Security: Workflows run with full runtime protection without developers needing to modify their workflow files or even be aware of the underlying security mechanisms. The protection is simply there, enabled by default.
Centralized Control: Security teams can manage and update the Harden-Runner agent through runner image lifecycle management rather than chasing down individual workflow files across repositories.
Consistent Policy Enforcement: When security policies are attached through the Policy Store, they apply uniformly to all workflows running on runners with the custom image. This eliminates the governance gaps that come with workflow-level approaches.
Simplified Onboarding: New projects and workflows automatically benefit from runtime security the moment they use a runner with the custom image. There's no security checklist to complete, no steps to remember.
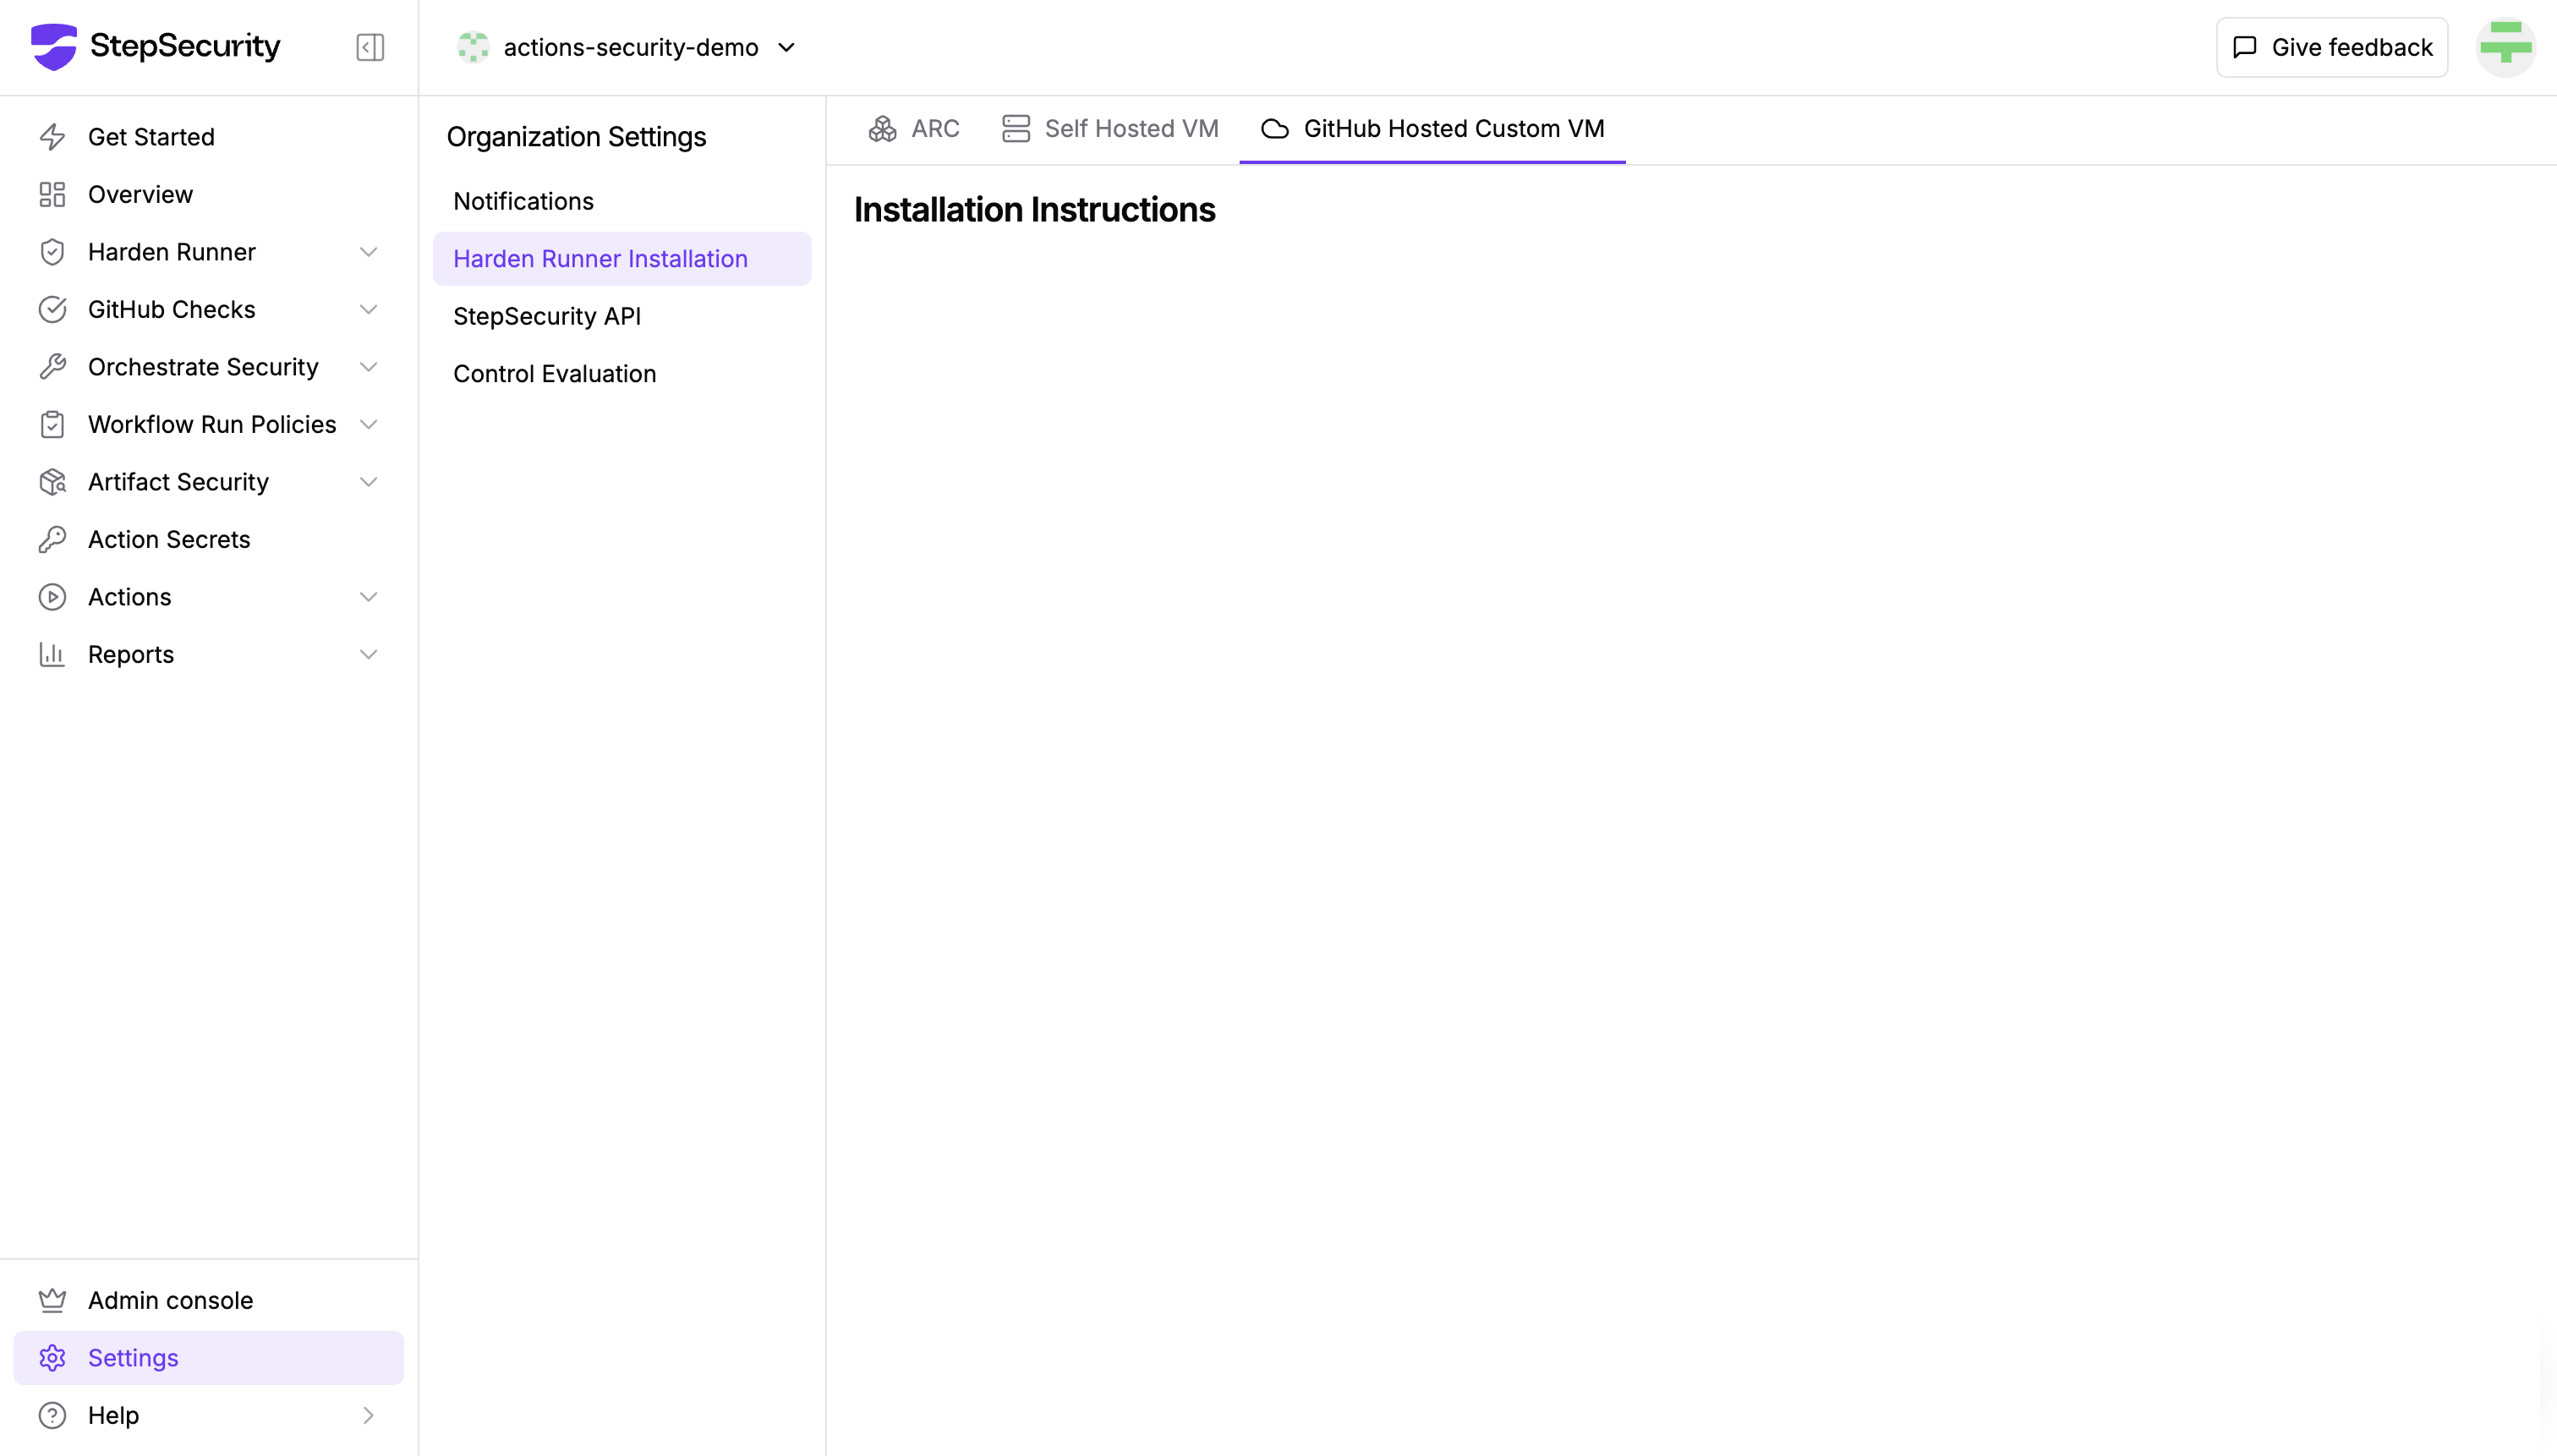
Under Settings → Harden-Runner Installation, you can find the installation instructions for GitHub-hosted custom VM images
A common question is what happens if some workflows still include the Harden-Runner GitHub Action step.
The short answer: there is no conflict.
When Harden-Runner is baked into the image, the baked-in agent starts when the VM starts. If a workflow also includes the Harden-Runner action, the action simply detects the already-running agent. It skips redundant setup. Workflows continue to work normally.
This allows teams to migrate gradually. You do not need to update hundreds of workflows before switching to custom images. The baked-in installation takes precedence and the job execution remains stable.
The combination of custom runner images and baked-in runtime security represents a maturation of CI/CD security practices. Rather than treating security as an add-on that developers must remember to include, it becomes part of the platform itself.
This mirrors the evolution seen in other areas of infrastructure security. Just as modern cloud environments provide security controls at the infrastructure layer rather than requiring each application to implement its own security, custom runner images with baked-in Harden-Runner bring platform-level security to CI/CD pipelines.
For organizations running GitHub Actions at scale, this architectural approach solves the operational challenges that have historically limited runtime security adoption. Security teams gain centralized control and consistent enforcement. Developers get transparent protection without workflow complexity. And the organization achieves comprehensive visibility into CI/CD runtime activity across all workflows and repositories.
Corporate laptops and production servers have long benefited from strong security monitoring. CI/CD runners, which handle equally sensitive data including cloud secrets, production builds, and source code, deserve the same level of protection. Custom runner images with baked-in Harden-Runner make this protection practical to deploy and maintain at enterprise scale.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。