





Configuring cloud-based environments is complex, as it requires considering networking, subscriptions, services, and all the components that make up the underlying infrastructure. Manual setup is error-prone, inconsistent, and difficult to reproduce.
This tutorial shows how to set up a fully automated cloud environment using GitLab as the main operations brain. All the cloud infrastructure is defined as code (hosted on GitLab) and deployed on AWS with OpenTofu through GitLab CI/CD pipelines. On top of this, these pipelines also handle the build and deployment of a real web application, using GitOps practices with Argo CD.
First, it is important to understand why infrastructure as code (IaC) and GitOps matter, and how GitLab brings these practices together in a single platform.
IaC ensures environments are:
GitOps extends these principles into the application lifecycle. Instead of manually applying changes to Kubernetes clusters (or other infrastructure), the desired state of applications lives in Git. A GitOps operator like Argo CD continuously ensures the cluster reflects what is in the repository. This brings:
GitLab combines all the capabilities required for this approach:
With GitLab, everything from provisioning cloud infrastructure to application delivery happens through one platform.
To follow this tutorial, you will need:
This tutorial includes instructions to:
Read on to learn how to reproduce this example in your own GitLab environment. You can find the source code of this example in the SATEC Public Demo Group.
The first step is to provision the cloud infrastructure with OpenTofu (the open-source Terraform fork). We can declaratively define networking components and create an Amazon EKS cluster.
To make this process reproducible and secure, we rely on GitLab CI/CD variables instead of hardcoding values. These variables allow us to configure the AWS environment dynamically across pipelines.
The following environment variables are required and need to be declared under Settings > CI/CD > Variables in the parent group (to be inherited by all projects):
All variables are defined as protected in GitLab, and sensitive ones such as the AWS secret access key are also masked, ensuring they are only exposed in secure CI/CD contexts. Security can be further enhanced by following this CI/CD variables tutorial. Separating code from configuration makes the pipeline both flexible and independent of environments.
Once configured, the OpenTofu pipeline can be executed automatically to:
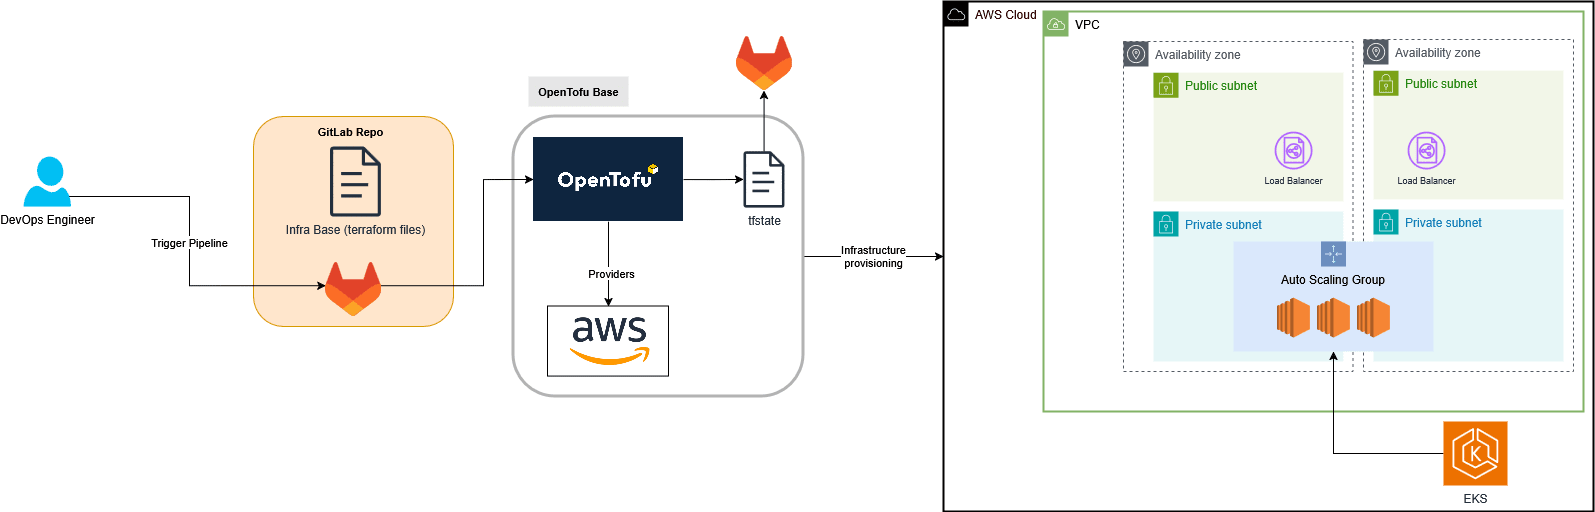
The diagram above illustrates how the infrastructure provisioning process works.
At the end of this stage, the AWS environment and Kubernetes cluster are fully provisioned and ready to operate.
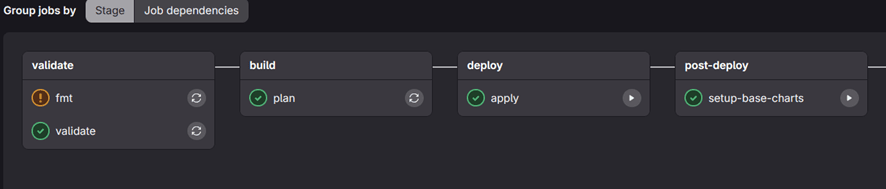
The final step of this process (post-deploy) is to trigger a secondary GitLab pipeline (located in a dedicated repository), which is responsible for deploying Argo CD and CertManager automatically into the new EKS cluster using the Helm Provider.
Once the AWS infrastructure and the EKS cluster have been successfully provisioned, the next step is to configure the Kubernetes tools required to operate the environment, which are Argo CD, CertManager, and Ingress NGINX Controller.
This process is fully automated through a secondary GitLab pipeline hosted in a separate repository.
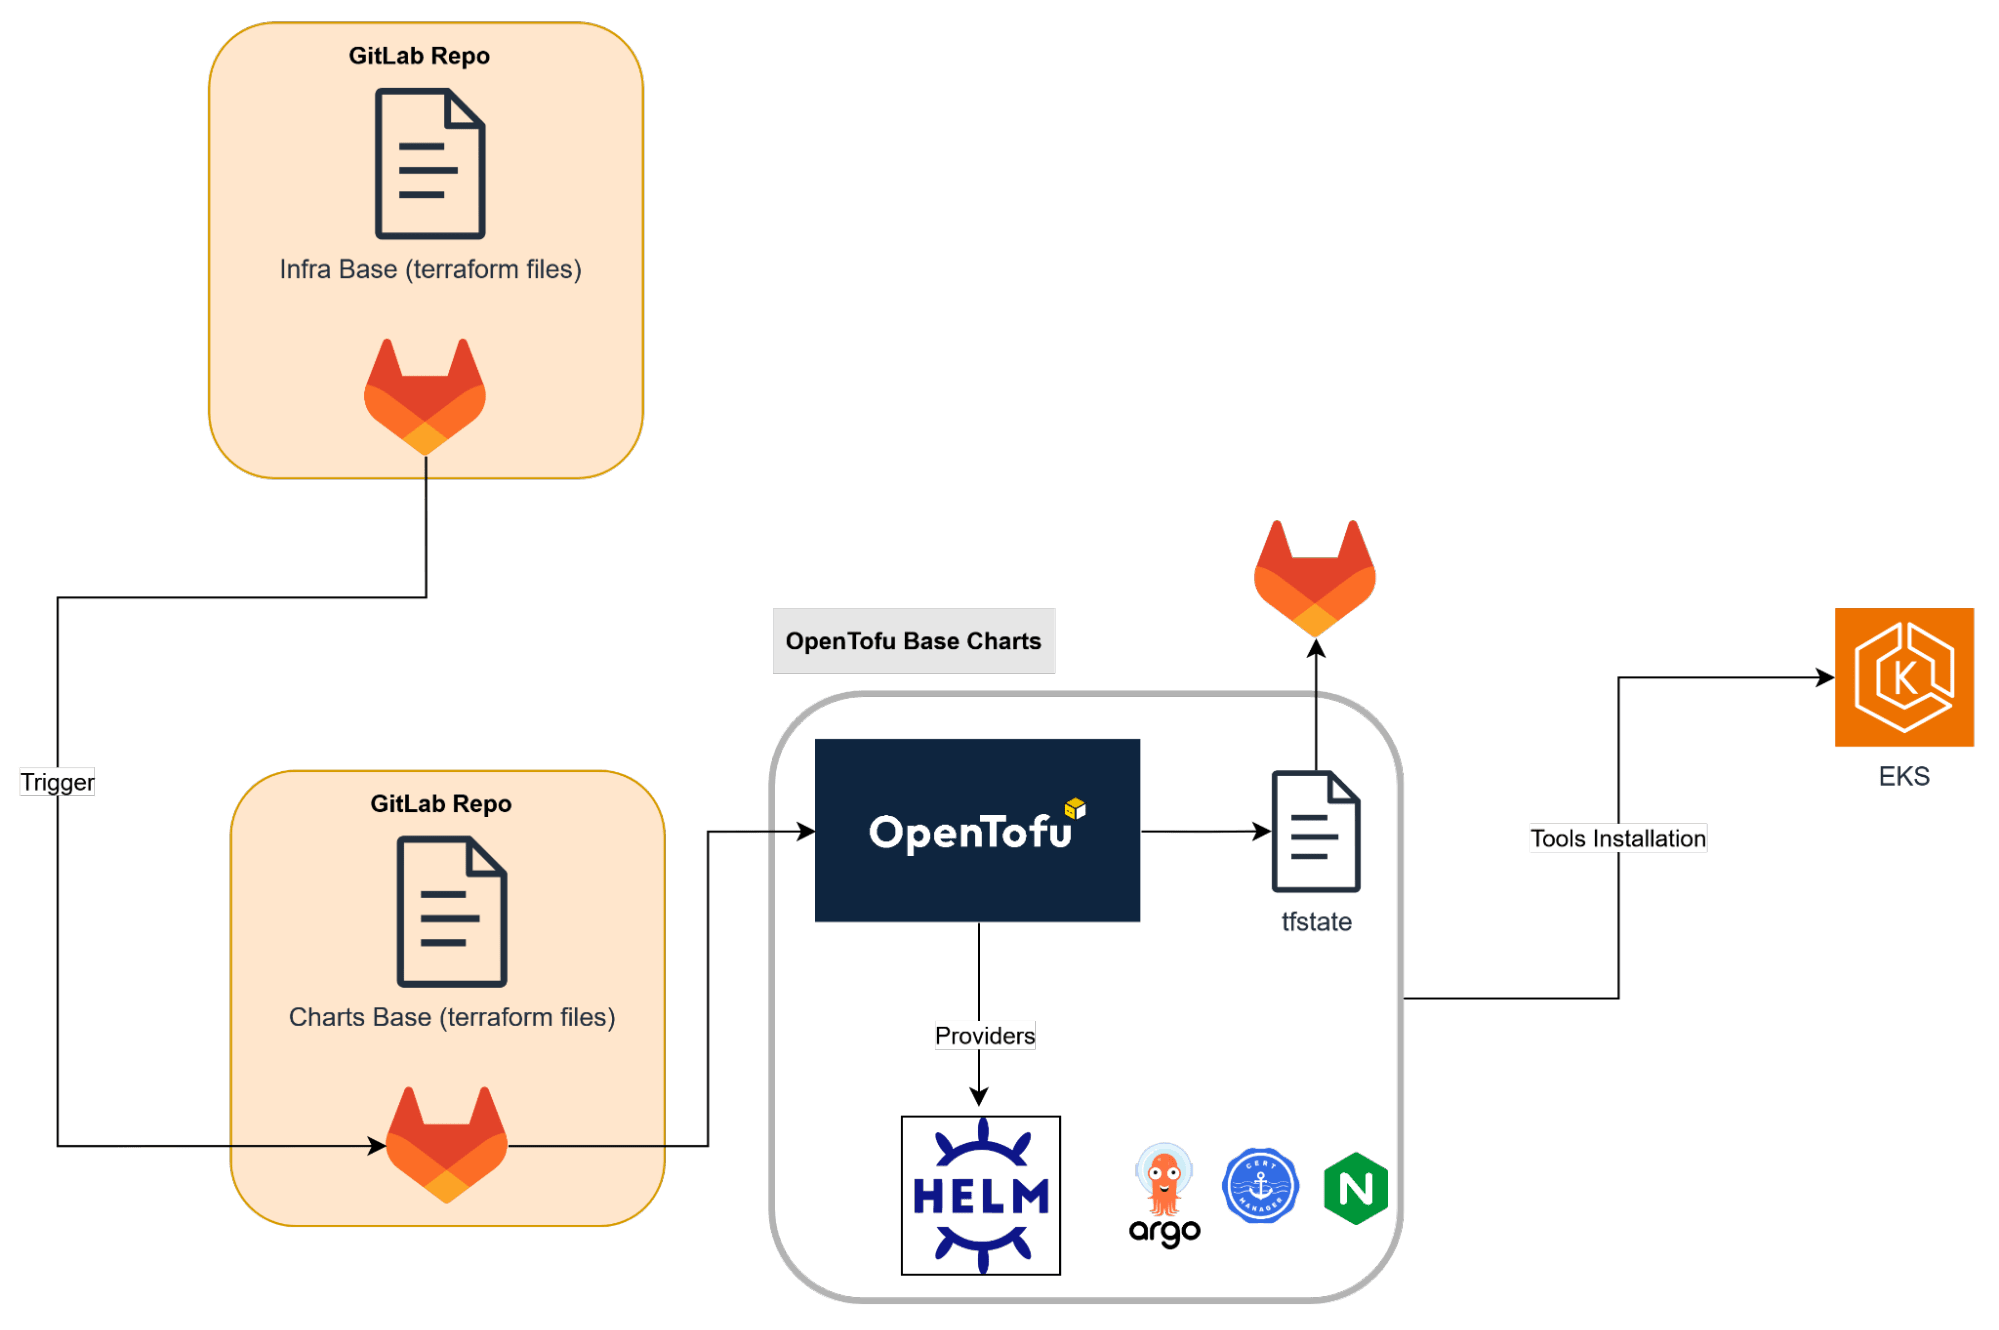
The execution of this second pipeline is triggered automatically from the infrastructure pipeline, using a trigger job once the OpenTofu provisioning stage has completed successfully.
In practice, this means that the deployment of these core components happens seamlessly as part of the same end-to-end workflow, there are no manual steps required. The deployment itself is handled by OpenTofu using the Helm provider, which allows managing Helm charts declaratively as code through GitLab.
A simplified workflow looks like this:
Once all the core Kubernetes components (Argo CD, CertManager, and Ingress NGINX Controller) are installed, the final stage of the automation pipeline begins. This step is executed automatically right after the Helm chart installation process is completed.
A third GitLab pipeline is triggered, responsible for deploying a sample web application into the newly created EKS cluster through Argo CD.
The diagram below shows the overall process:
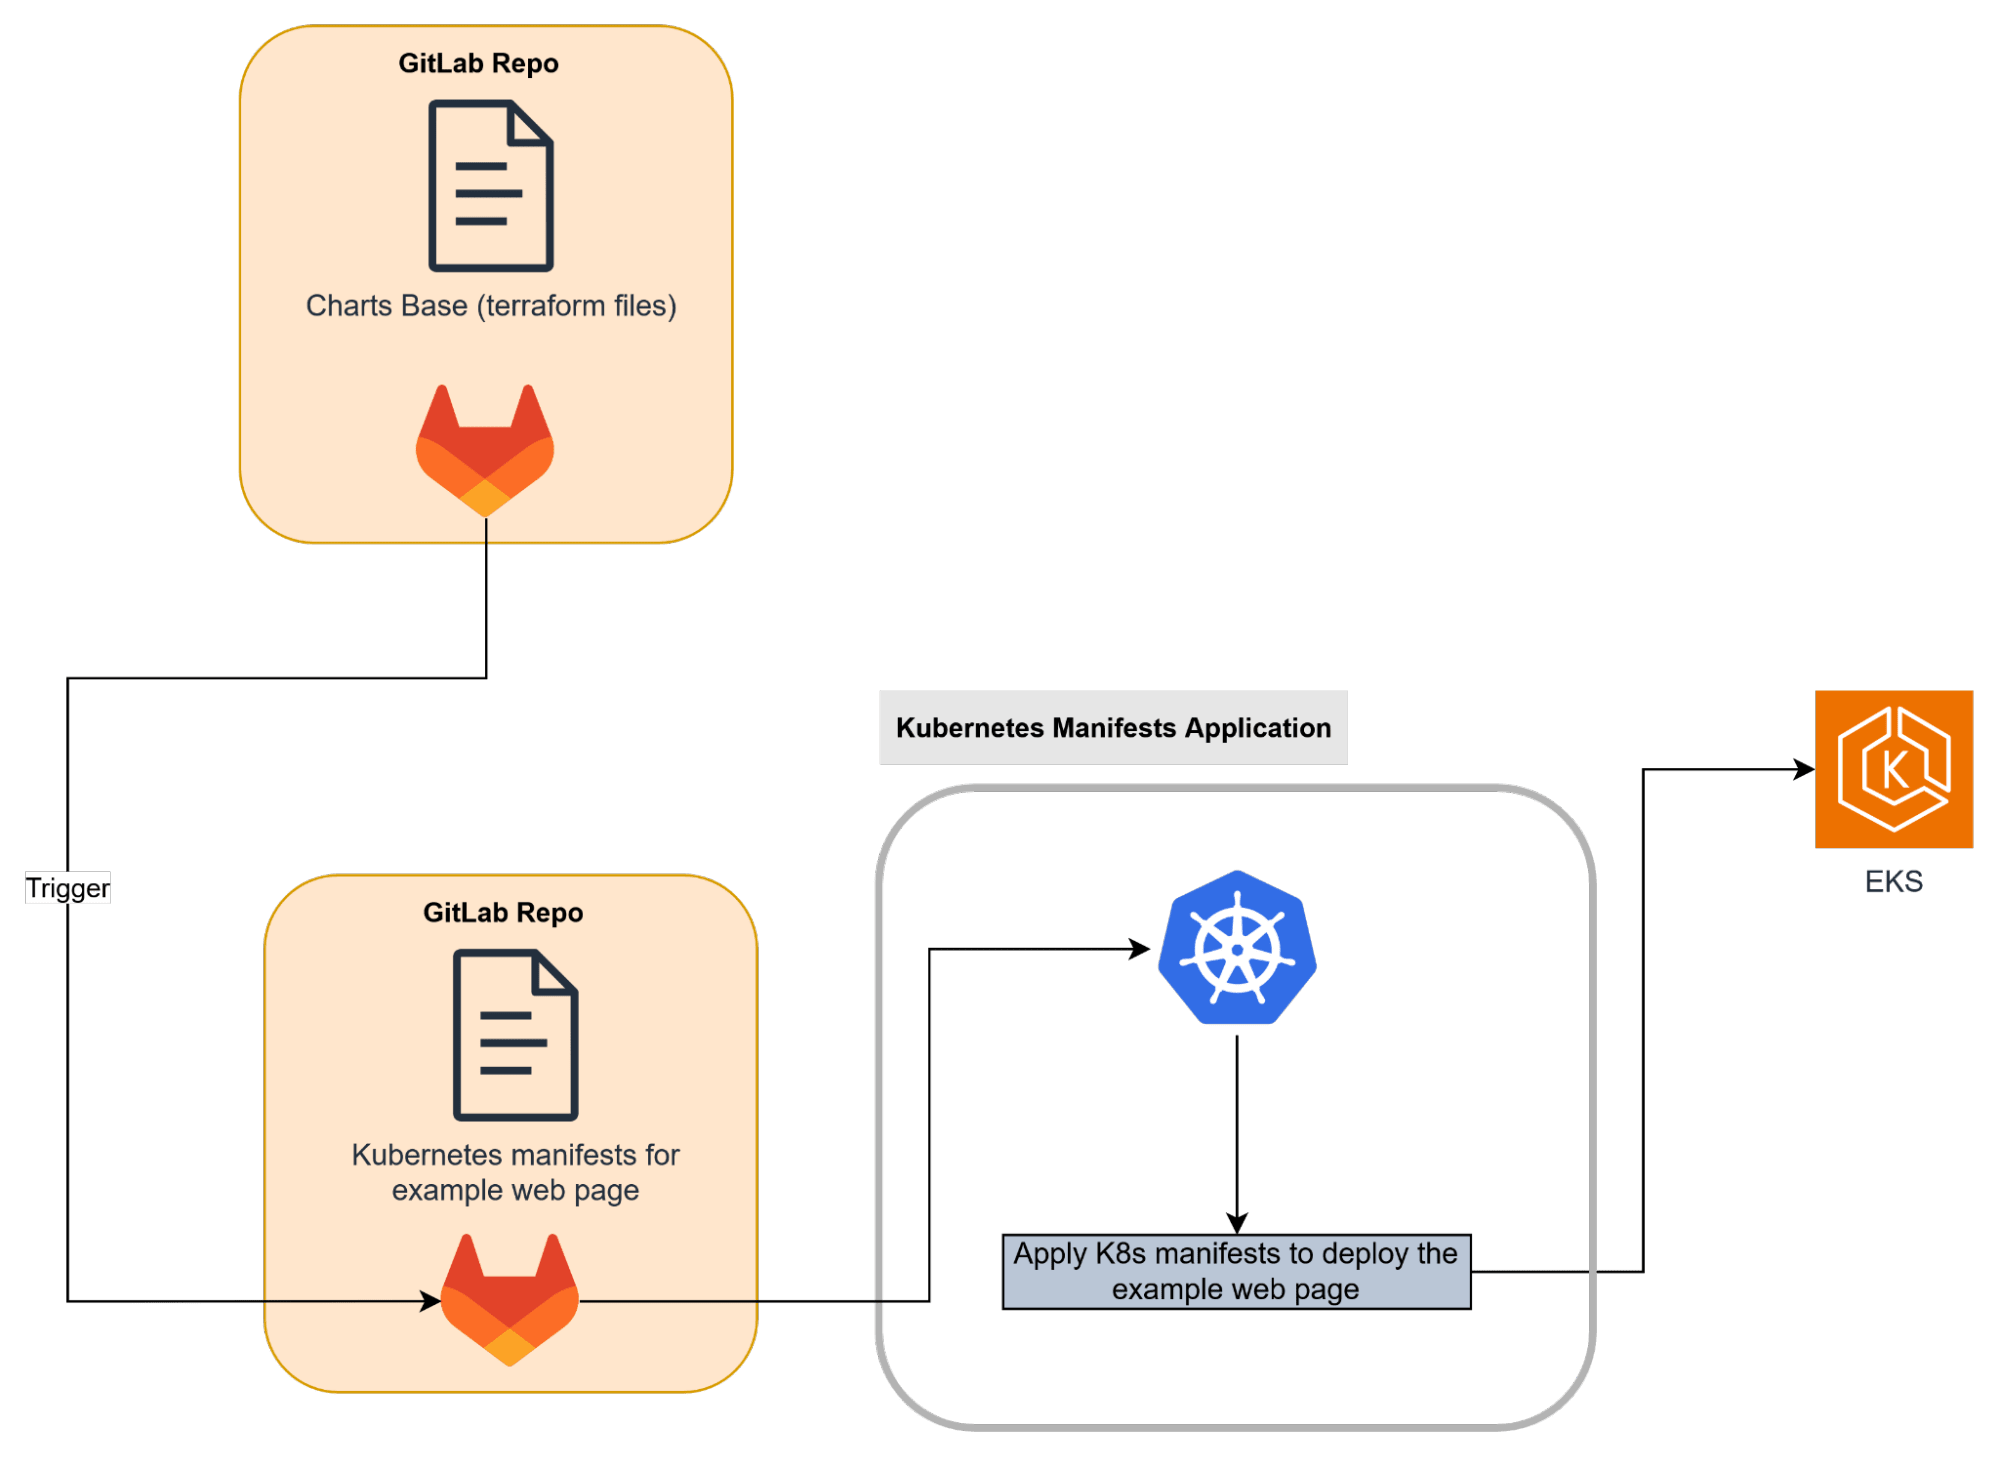
In this stage, GitLab uses the kubeconfig generated by OpenTofu to connect to the cluster and apply the Argo CD application manifests that define the desired state of the web application.
The pipeline:
All these actions are performed automatically through GitLab CI/CD, with no manual intervention.
Once the manifests are applied, the Argo CD controller detects them and synchronizes the application state with the repository, deploying the sample web page into the EKS cluster.
The result is a fully operational Kubernetes environment, where:
This approach ensures end-to-end automation, traceability, and reproducibility, all managed by GitLab.
Before the application is deployed through Argo CD, it must first be built, containerized, and published to the GitLab Container Registry.
This process is managed through a dedicated CI/CD pipeline and follows a GitOps repository structure, where the source code and Kubernetes manifests are stored in separate repositories.
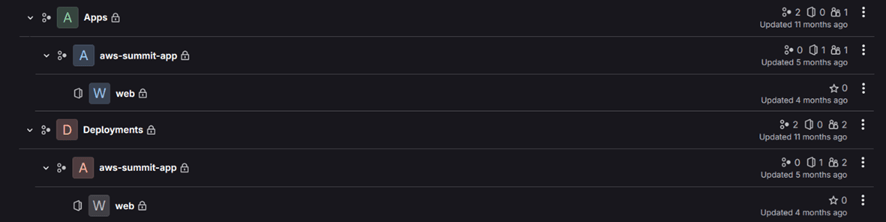
In this setup, the GitLab group is organized into two main sections:
This separation enables a clean GitOps workflow because application code and deployment configurations are independent but remain synchronized through automation.
The CI/CD pipeline defined in the application repository automates the following tasks:
These are performed automatically by committing the new image tag or creating a merge request.
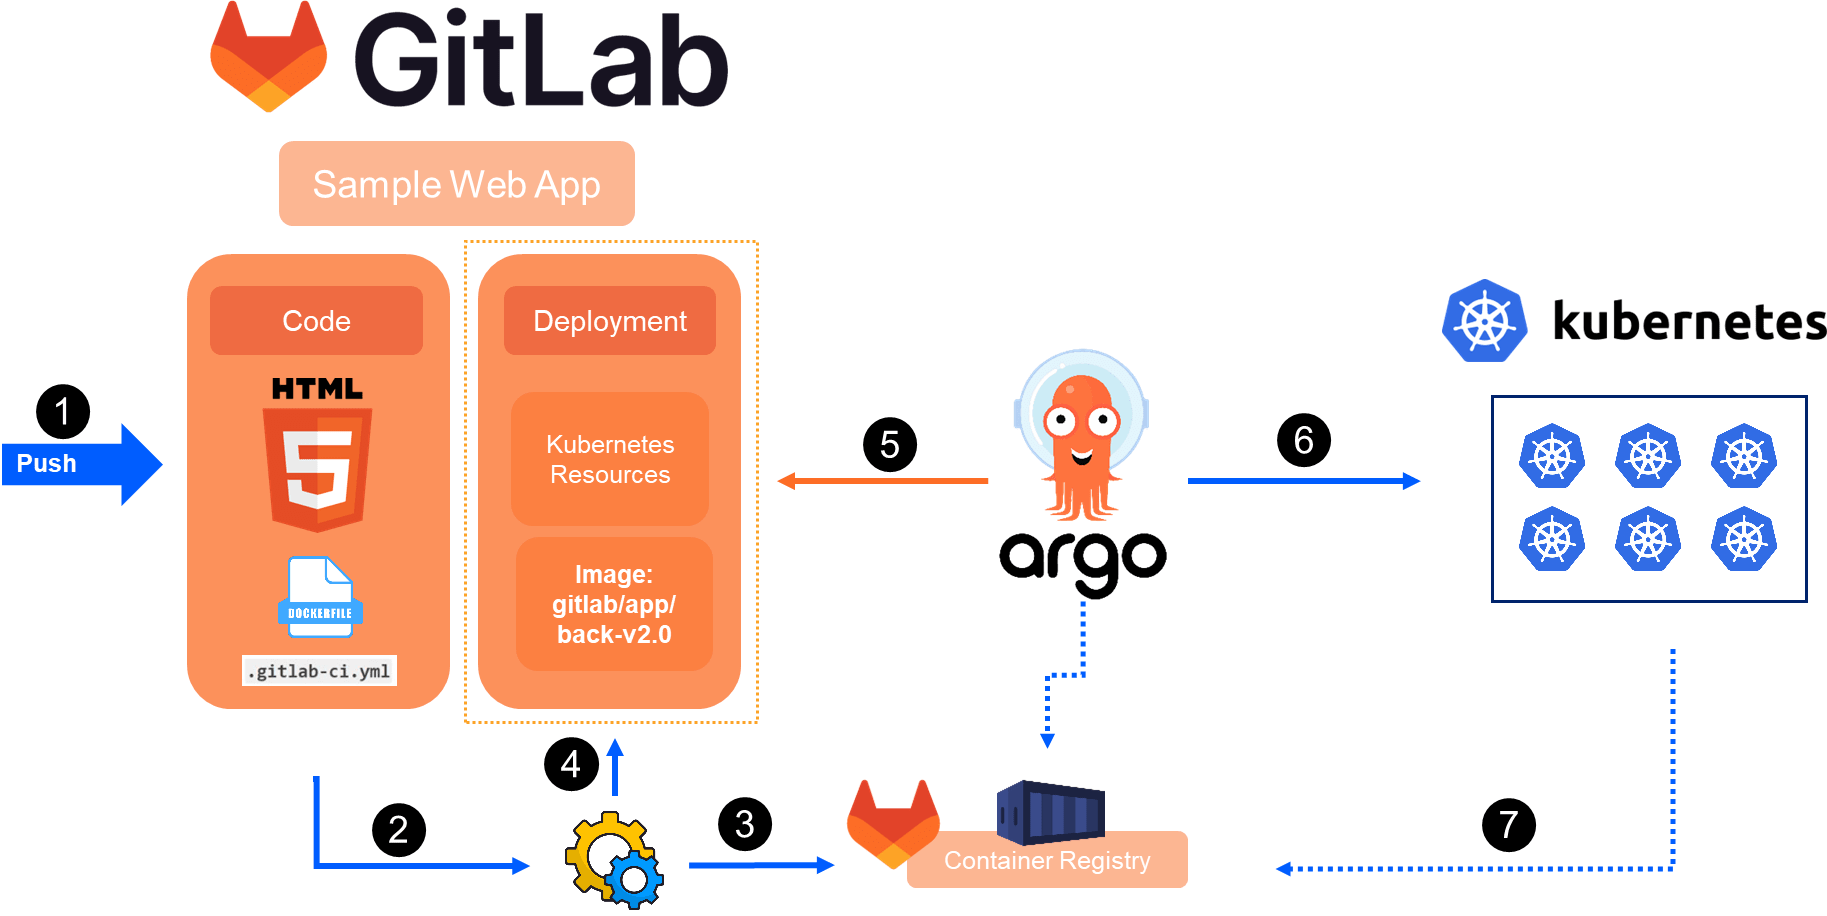
Once the commit or merge request is created, Argo CD automatically detects the change in the deployment repository and synchronizes the updated manifests with the Kubernetes cluster, ensuring that the new application version is deployed without any manual intervention.
This tutorial demonstrated how to build a fully automated cloud environment with GitLab as the central hub, achieving the goals we set out at the beginning: infrastructure that is reproducible, versioned, and automated. By combining OpenTofu for infrastructure provisioning, GitLab CI/CD for pipeline orchestration, and Argo CD for GitOps-based application delivery, teams can manage the entire lifecycle — from cloud resources to running applications — through a single platform.
As a GitLab partner with deep expertise in cloud infrastructure and DevSecOps practices, Clober (SATEC group) can help organizations implement similar automated environments tailored to their specific needs.
Note: This blog post is based on a live demo originally presented at AWS Summit Madrid 2025 by the Clober DevSecOps team (SATEC group).
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。