
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

H
Help Net Security
月光博客
月光博客
IT之家
IT之家
B
Blog RSS Feed
T
Tailwind CSS Blog
The GitHub Blog
The GitHub Blog
博客园 - 三生石上(FineUI控件)
MyScale Blog
MyScale Blog
J
Java Code Geeks
Stack Overflow Blog
Stack Overflow Blog
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
Cyber Security Advisories - MS-ISAC
博客园 - Franky
博客园 - 叶小钗
阮一峰的网络日志
阮一峰的网络日志
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
U
Unit 42
博客园_首页
B
Blog
V
V2EX
腾讯CDC
Vercel News
Vercel News
量子位
Microsoft Security Blog

Tenable Blog

How it works: Inside the agentic harness for Tenable Hexa AI Introducing the CyberAgents Exchange AI Inspector: Rigorous review for community-built AI September 2026 Microsoft Patch Tuesday | Tenable® Claude Mythos 5 is coming to Tenable One, powering the new “Adversary View” CVE-2026-75650: StyleSmuggler Adobe Commerce FAQ | Tenable® Why post-quantum defense starts with crypto visibility Building an exposure management program the business tr Tenable & SentinelOne: 93 CVEs Expose Edge Risk | Tenable® Siemens S7 PLC threat: What you need to know | Tenable® Oracle Critical Security Patch Update August 2026 | Tenable® How to detect & respond to cloud ransomware attacks in Azure Agentic AI Threat Cluster: What It Means for Your Exposure August 2026 Microsoft Patch Tuesday | Tenable® Agentic AI for Cybersecurity: See Security Teams Built at Black Hat USA 2026 An inside look at code security with Claude Mythos Preview Watch Tenable Hexa AI automate remediation with agentic routines How Claude Mythos Preview is changing code security at Tenable What do federal & state cyber rules mean for water utilities? What Canada’s Bill C-8 means for critical infrastructure security Minnesota Water Cyber Attack and CISA Advisory AA26-097A Oracle July 2026 Critical Patch Update 1235 CVEs | Tenable® AI agent config attacks: How attackers turn trusted Dev harness files into payloads wp2shell: WordPress Core Pre-Auth RCE FAQ | Tenable® SharePoint CVEs FAQ: CVE-2026-56164, CVE-2026-32201, CVE-2026-45659 | Tenable® Build agentic AI security at Tenable Swarm, Black Hat 2026 SonicWall CVE-2026-15409 and CVE-2026-15410 zero-day exploited | Tenable® Understanding Anthropic’s new AI agent Claude Tag’s access model in Slack 5 reasons to integrate AppSec data with your exposure management platform July 2026 Patch Tuesday: Largest Patch Tuesday 569 CVEs FedRAMP High, IL5, and zero trust: How federal agencies can secure cloud environments
Unlocking foundational visibility for cyber-physical syst...
2026-04-15 · via Tenable Blog

Stop managing risk in silos. VM-Native OT Discovery, now available in Tenable Vulnerability Management and Tenable Security Center provides unified visibility across IT and OT domains. See every asset and manage your total cyber exposure in a unified view.

Key takeaways

  1. The air gap is dead. IT security teams are inheriting responsibility for operational technology (OT), but often lack visibility into these systems.
     
  2. Security teams face significant barriers with OT security. Fear of disrupting fragile devices and the high cost of specialized hardware have created a dangerous "black box" in the attack surface.
     
  3. The perfect “on-ramp” to OT security. A new OT Discovery engine embedded in Tenable Vulnerability Management and Tenable Security Center allows security teams to safely profile OT, IoT, and shadow IT assets using the tools they already own.

For decades, the concept of the "air gap" — a physical isolation between IT networks and critical operational technology (OT) — provided security leaders with a sense of comfort. The assumption was simple. Digital threats stay on the corporate network, while physical operations run safely in isolation.

In today's hyper-connected world, that assumption is often wrong and leaves your OT environment exposed to preventable cyber risk.

From modern data centers and smart hospitals to commercial real estate and universities, the line between the digital and the physical has blurred. IT security teams are increasingly inheriting responsibility for securing cyber-physical systems (CPS) — the HVAC controllers keeping servers cool, the badge readers securing facility entrances, and the power distribution units keeping the lights on.

Yet, for many organizations, these OT assets are a massive blind spot.

The "black box" problem

While vulnerability management programs have matured rapidly for IT assets, covering everything from cloud workloads to laptops, operational environments are often a "black box."

This visibility gap usually stems from two distinct barriers:

  • There is a pervasive (and historically valid) fear that scanning OT/IoT assets with traditional IT security tools could knock fragile devices offline, disrupting critical business operations.
     
  • Traditional OT security tools often require a massive undertaking. The complexity and cost of deploying expensive specialized hardware, managing long-term evaluations, architecting complex mirror ports, and navigating the political minefield of installing new appliances in sensitive production environments make these projects difficult to justify.

The result is a dangerous paradox. Security teams are responsible for the risk of interconnected systems, but don’t have the tools to see or secure them. Attackers, however, face no such barriers, frequently pivoting from compromised IT networks to poorly defended OT assets to maximize impact.

Rethinking converged OT/IT security

To secure the modern attack surface, organizations must stop managing IT and OT risk in silos. Security leaders need a unified view that treats a vulnerability on a programmable logic controller (PLC) with the same rigor and context as a vulnerability on a Windows server.

Achieving this requires a fundamental shift in how we approach asset discovery. Security teams need streamlined methods that provide the necessary depth of OT visibility for compliance and risk reduction, without the friction of deploying hardware across physical sites. They need a way to safely seeshadow OT assets using the infrastructure already in place.
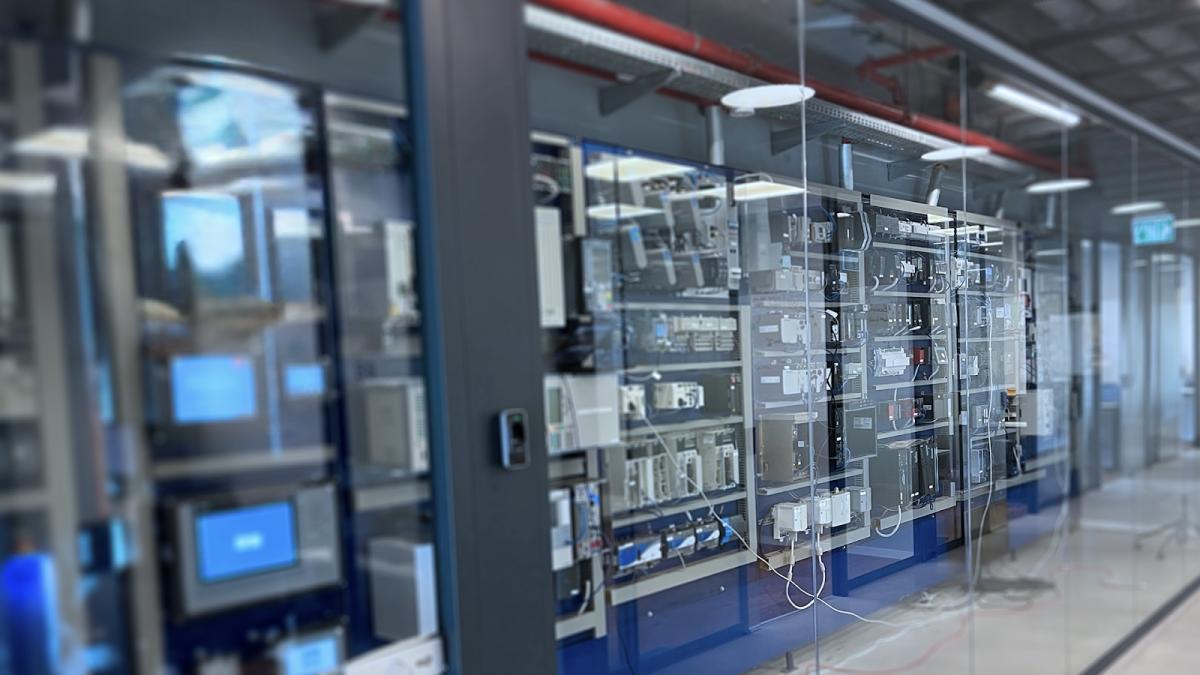
 

Tenable’s research and testing lab for operational technology (OT)

Image: A segment of Tenable’s research and testing lab for operational technology (OT).

Introducing VM-Native OT Discovery

Our latest release fundamentally changes the economics and accessibility of OT security tools. We are excited to announce OT Discovery, a new capability embedded directly inside the Tenable One Exposure Management Platform that provides security teams with foundational visibility into OT and IoT environments. It’s the perfect on-ramp to OT security, so you can uncover hidden OT risks and deep asset-level details. 

Here is how it changes the game for your security program:

  • Safe visibility for cyber-physical systems. OT Discovery uses the same Active Query engine found in our specialized Tenable OT Security solution—now natively integrated into Tenable Vulnerability Management and Tenable One. It performs "smart," protocol-aware handshakes to verify assets before querying them so you can safely profile PLCs, human-machine interfaces (HMIs), IoT devices, and shadow IT assets across your environment.
     
  • Unified OT/IT exposure management. By integrating OT asset data, including vendor, model, and firmware details, directly into your existing dashboards, you can break down silos and view your organization's total risk exposure in a single pane of glass.
     
  • Extend the value of your security investments. No need to rip and replace or install new hardware. This capability enables you to extend the value of your existing vulnerability management toolsets to uncover the OT risk hiding on your network.

Breaking down silos across IT and OT

Adopting a unified approach to OT/IT exposure management builds trust.

Historically, the relationship between IT security and facility operations teams has been strained. IT wants to scan and patch known vulnerabilities. Operations teams require uptime and stability. When IT security teams try to enter the OT space with aggressive scans or unfamiliar hardware, friction is inevitable.

VM-Native OT Discovery changes the conversation. Because Tenable relies on trusted, safe query methods through familiar infrastructure, the security team can approach the ops team with reliable data and real-time exposure intelligence.

Instead of asking, "Can we install a black box on your network?" you can say, "We noticed three unmanaged PLCs communicating on the subnet. Here is exactly what they are. Let’s work together to secure them now rather than waiting 6-12 months to patch during the next maintenance interval."

Get started with OT security today

OT security is no longer just for industrial giants and organizations managing critical national infrastructure. Every manufacturer, warehouse operator, and organizations smart building management systems face operational risk.

Ready to get visibility into your OT blind spots? You don't need a massive budget or a year-long deployment project to get started. Watch this quick demo to see how you can secure your most critical assets with the vulnerability management tools you already use.


Are you an existing Tenable customer? Explore the user guide documentation for Scan Templates and Discovery Settings to get started.
Learn more

Anthony Johnson

Anthony Johnson

Senior Product Marketing Manager

Anthony Johnson leads product marketing and GTM strategy for Tenable’s operational technology (OT) security and vulnerability management practice areas. He focuses on the convergence of industrial innovation and cyber resilience, exploring critical themes such as CPS/IoT security, cloud adoption in OT, and the role of AI in protecting critical infrastructure. Drawing on a diverse background across technology, management consulting and public sector verticals, Anthony provides strategic insights to help organizations drive innovation without compromising security.