







Sovereignty has become the driving principle of Europe's technology conversation. Every policy discussion, every emerging legislative development, every procurement process, every boardroom debate comes back to which platforms and partners to trust.
Trust goes beyond compliance. It demands integrity, accountability, and transparency about the limits of what any provider can guarantee – rather than making commitments that sound reassuring but cannot be verified.
We have spent considerable time listening to public sector organizations, critical national infrastructure operators, and regulators across Europe. This is not a new concern. Over the years, what organizations are asking for has become increasingly specific. They want their data to remain in Europe. They want to know precisely who can access it and who holds the encryption keys. And they want every access event logged and visible. They want operations managed locally, under local jurisdictions and subject to local laws.
These are governance requirements as much as technical ones. And what they add up to is a demand for verifiable control, not more contractual promises. The distinction matters enormously. Telling an organization you will protect their data is one thing; giving them the architecture and the visibility to verify that protection themselves is another.
It is worth being clear about who is driving this conversation. These requirements are not universal. A large enterprise running productivity tools has different needs from a government ministry managing sensitive national data or a critical infrastructure operator running systems that society depends on for clear drinking water. What we are describing here is what we hear from the most demanding end of the spectrum: public sector and critical national infrastructure. And that is where we focus, because getting it right there matters most.
The announcement of the Sovereign Cortex with T Securities, together with Deutsche Telekom and Google Cloud, is our direct response to these demands and the next step in our long-standing commitment to Europe. It is not a marketing position – it is a framework that provides customers actual controls. It is built on the five elements that reflect how we fundamentally think about sovereignty. One that will set the standard across every solution we build for the region.
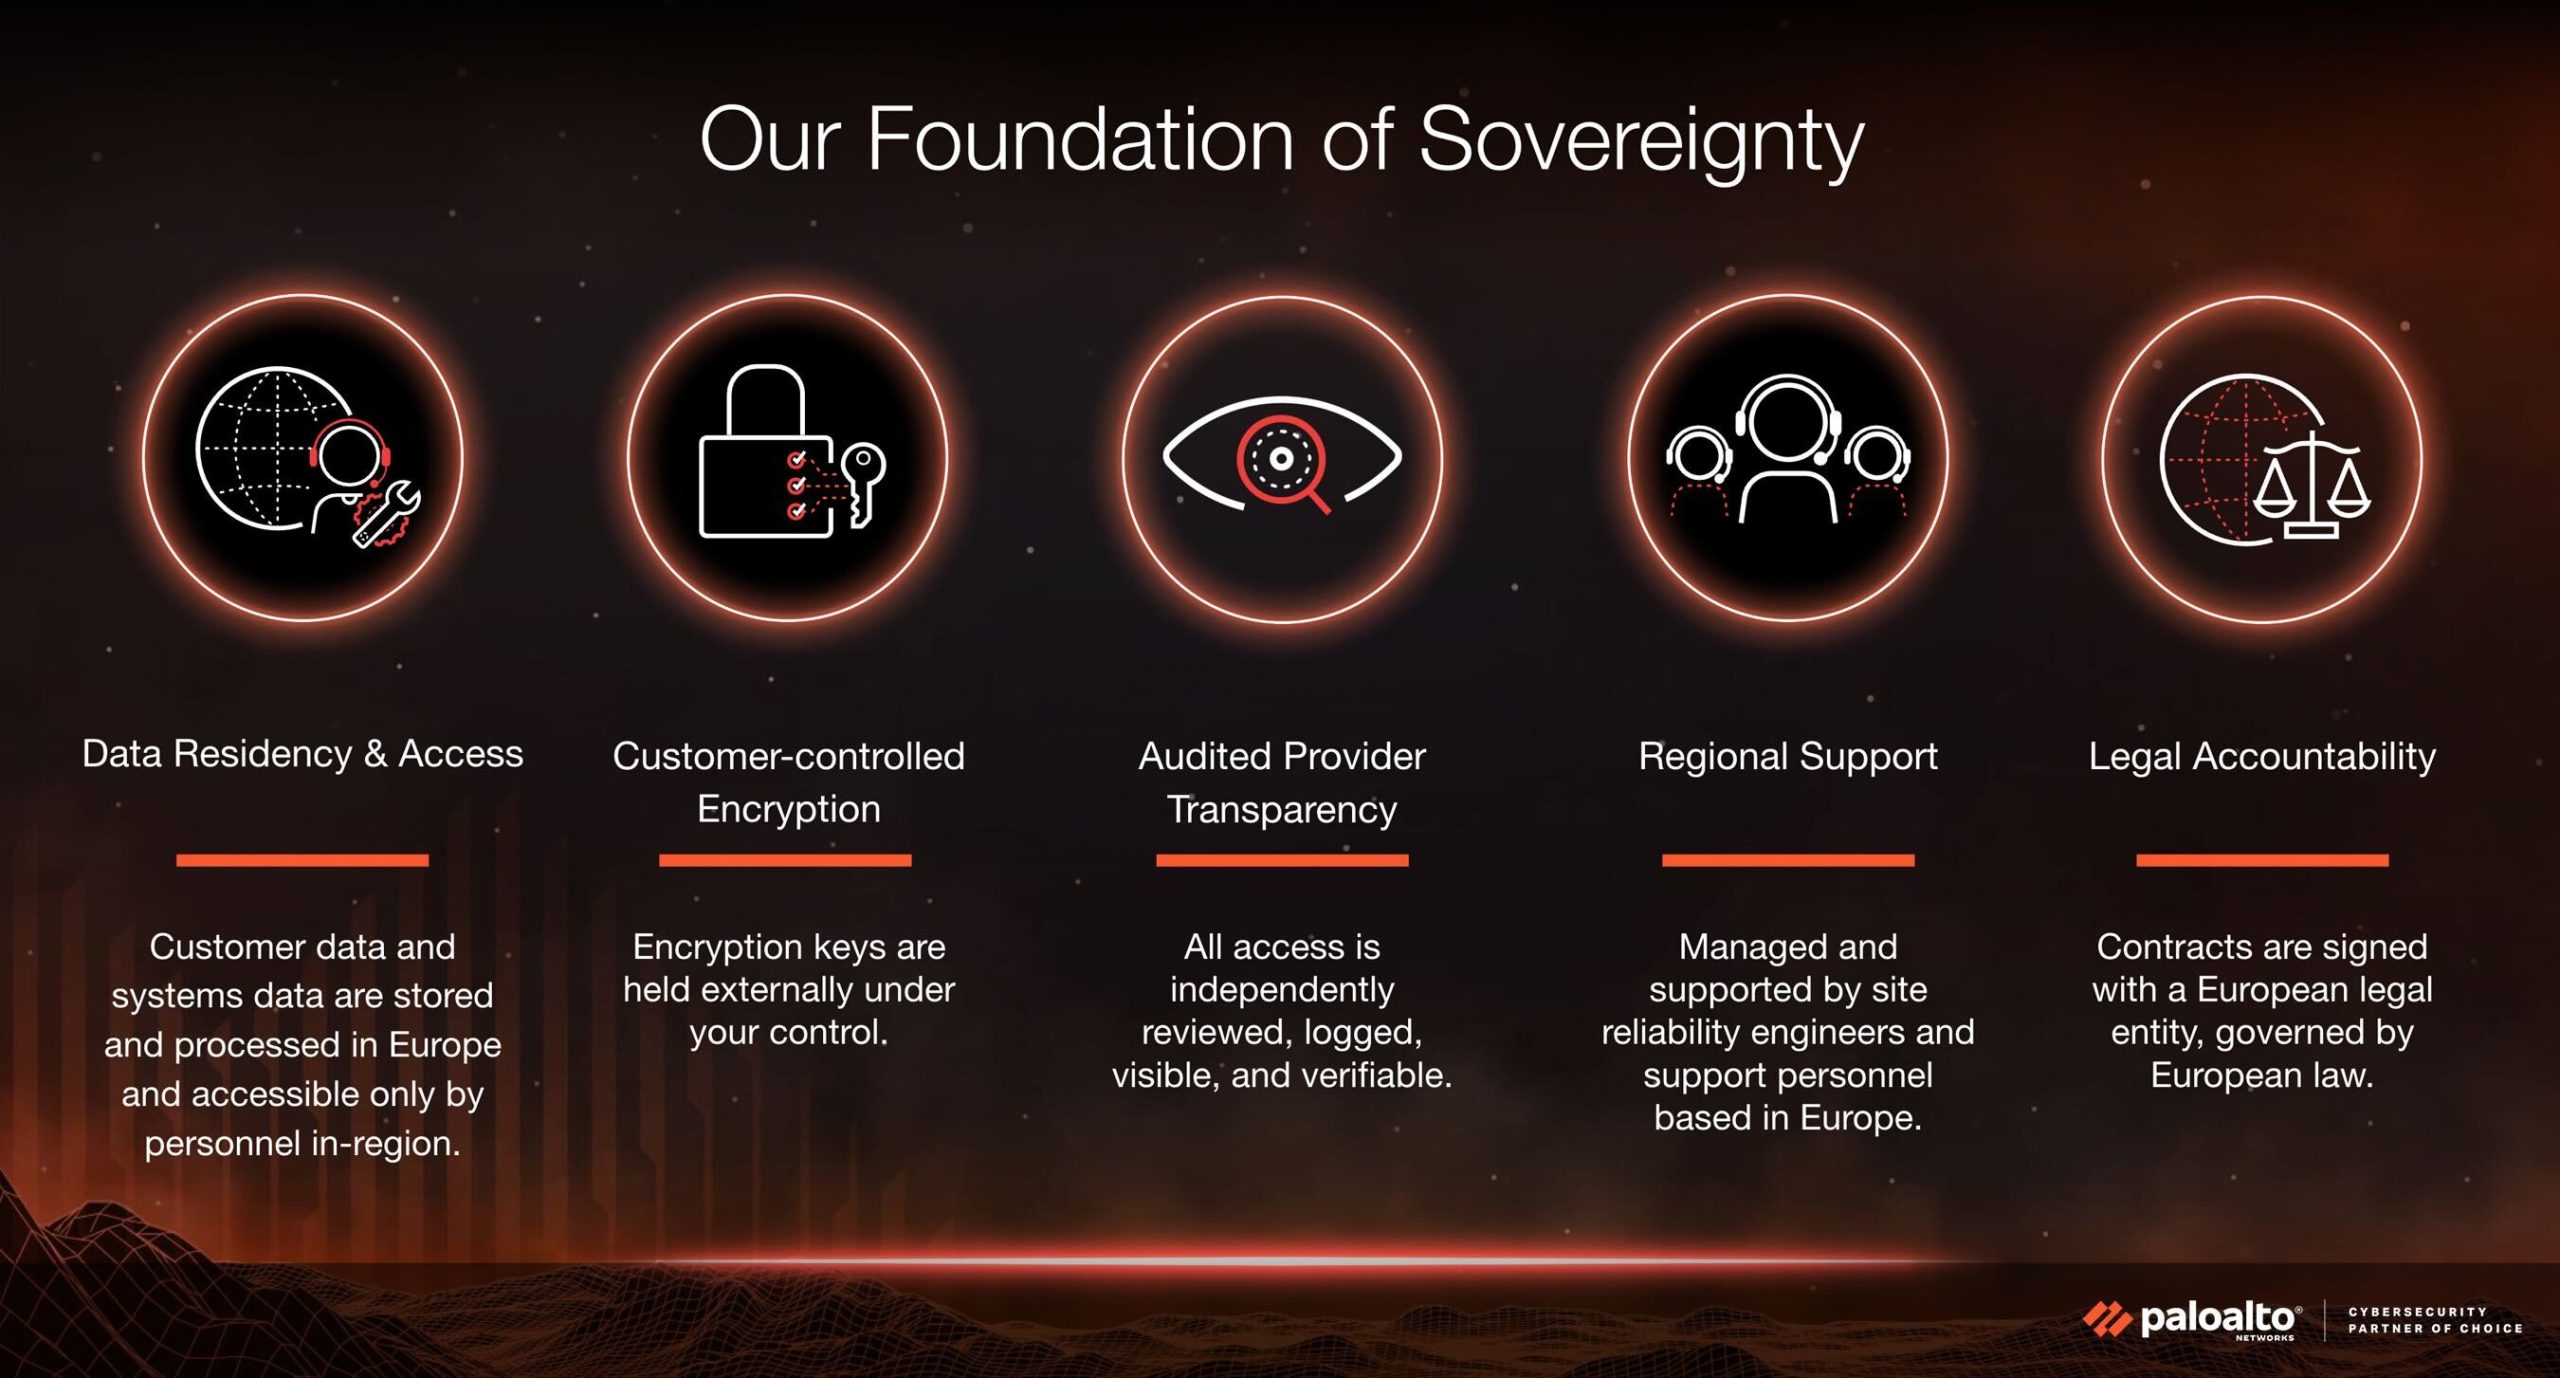
Each element of this framework was designed from the outside in, with the input of every European organization we collaborated with.
Here is what I believe, having spent years in this conversation across Europe. Trust is not something a provider can simply assert. It is something that has to be earned, over time, through consistent and verifiable action.
For technology companies operating in Europe, that means placing meaningful control with a trusted local European partner, being transparent about what we can and cannot guarantee, and treating sovereignty not as a compliance exercise but as a design principle.
It also means being honest about the journey. We have done significant work, yet we have further to go. The organizations we serve deserve partners who acknowledge that openly rather than presenting a finished picture.
What drives this work is straightforward: we believe in Europe’s digital future. We believe in the missions of the organizations we work with every day, whether they are protecting critical public services, securing national infrastructure, or safeguarding the data that citizens and institutions depend on. Being a committed partner to those organizations is not a product decision. It is a values decision.
And that is precisely why trust is the measure we hold ourselves to. The direction is clear, the commitment is real. But commitment means nothing without trust – and trust, like everything worth having, has to be earned every day.
Forward-Looking Statements
This blog contains forward-looking statements that involve risks, uncertainties and assumptions, including, without limitation, statements regarding the benefits, impact, or performance or potential benefits, impact or performance of our products and technologies or future products and technologies. These forward-looking statements are not guarantees of future performance, and there are a significant number of factors that could cause actual results to differ materially from statements made in this blog. We identify certain important risks and uncertainties that could affect our results and performance in our most recent Annual Report on Form 10-K, our most recent Quarterly Report on Form 10-Q, and our other filings with the U.S. Securities and Exchange Commission from time-to-time, each of which are available on our website at investors.paloaltonetworks.com and on the SEC's website at www.sec.gov. All forward-looking statements in this blog are based on information available to us as of the date hereof, and we do not assume any obligation to update the forward-looking statements provided to reflect events that occur or circumstances that exist after the date on which they were made.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。