


惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

博客园 - 叶小钗
Last Week in AI
Last Week in AI
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
雷峰网
雷峰网
GbyAI
GbyAI
Hugging Face - Blog
Hugging Face - Blog
N
Netflix TechBlog - Medium
博客园 - 聂微东
Y
Y Combinator Blog
罗磊的独立博客
博客园_首页
小众软件
小众软件
有赞技术团队
有赞技术团队
爱范儿
爱范儿
F
Fortinet All Blogs
C
Check Point Blog
Google DeepMind News
云风的 BLOG
云风的 BLOG
Apple Machine Learning Research
M
MIT News - Artificial intelligence
月光博客
月光博客
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
博客园 - 司徒正美
aimingoo的专栏
aimingoo的专栏

Hackread – Cybersecurity News, Data Breaches, AI and More

Operation Endgame Disrupts StealC, Amadey and SocGholish Malware Networks New GhostShell Hacking Group Targets Ukraine’s Drone Defense Sector Fake npm Packages Impersonate PostCSS Tool to Steal Chrome Passwords Best Crypto Payment Solutions for E-Commerce Businesses Internet Society Foundation Opens Global Call for Common Good Cyber Fund to Strengthen Cybersecurity LastPass Confirms Customer Data Breach After Klue OAuth Token Theft ‘Cordyceps’ CI/CD Flaw Exposes Microsoft, Google, Apache Repos to Pipeline Hijacking The Rise of AI-Powered Academic Fraud: Beyond Traditional Plagiarism New CryptoBandits Malware Uses USB Drives and Tor to Steal Crypto The Evolution of iGaming Fraud: What Security Teams Should Expect in 2027 2 Scattered Spider-Linked Hackers Plead Guilty Over £39M TfL Cyberattack Beats Studio Buds Flaw Could Let Nearby Attackers Eavesdrop on Users Texas Parks and Wildlife Data Breach Affects Over 3M License Customers Threat Hunting Beyond Alerts: Finding the Activity Detection Misses Scammers Use Fake GitHub Stars, VirusTotal Reviews to Spread Crypto Clipper Salesforce Disables Klue Integration After OAuth Token Theft Hits Customer Data MDR Provider Comparison: Time to Discover and Respond to Threats Meteor 3.0 Migration Helped Rocket.Chat Move Off End-of-Life Node.js Runtime Gcore Helps Ucom Safeguard Public Live Broadcast Infrastructure During Armenia’s Parliamentary Elections eFAQ Publishes Investigation Into Alleged Scam Activity and Coordinated Reputation Attacks FIFA World Cup 2026: Hackers Target Football Fans With Fake Tickets Sites MacBook Neo vs Windows Laptops for Cybersecurity Tasks Operation Endgame Disrupts SocGholish Malware Infrastructure What Businesses Should Know Before Migrating Their CMS DragonForce Ransomware Abused Microsoft Teams to Hide Malware Activity Agentjacking: Researchers Show How One Fake Bug Report Can Hijack AI Coding Agents FortiBleed Attack Exposes Fortinet Firewall Credentials in 194 Countries SpyCloud Report Finds Phishing Attacks Surge as Employee Data Is Exposed at 86% of Fortune 100 Companies 152 Chrome Live Wallpaper Extensions Hid Ad Tracking and Fake Search Clicks Heimdal Survey: Executives Four Times More Confident About AI Risk Than the Teams Managing It
Nintendo America Employee Data Exposed After Shadowbyt3$ ...
Deeba Ahmed · 2026-06-19 · via Hackread – Cybersecurity News, Data Breaches, AI and More

A third-party human resources platform called TinyPulse has become the victim of a supply-chain attack that resulted in the exfiltration of records belonging to Nintendo of America employees. The breach was confirmed by Nintendo following claims from the notorious Shadowbyt3 extortion group.

The attackers, reportedly, didn’t compromise Nintendo’s own network perimeter, but accessed the cloud environment of TinyPulse. For your information, this is an employee survey, feedback, and workforce analytics platform owned by WebMD Health Services. Since TinyPulse aggregates workforce metrics and personnel details of its client base, the infrastructure contained a large volume of identifiable employee data.
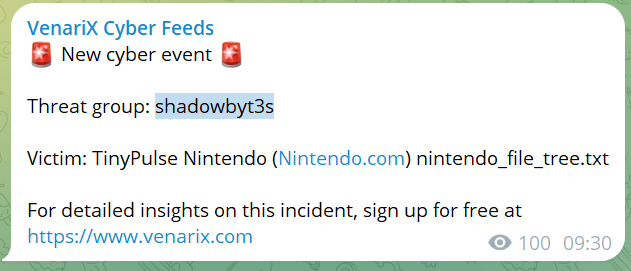
Cyberattack on Nintendo Vendor TinyPulse Allegedly Exposes Decade of Employee Records
Alert from VenariX Cyber Feeds on Telegram after SHADOWBYT3$ claims

Breach Details and Attribution

Shadowbyt3$, which emerged in October 2025 and operates as an extortion-as-a-service group, published this claim in the attack on 12 June 2026, and demanded a ransom payment of 2 million USD from Nintendo to prevent public data exposure. The group gave a 48-hour deadline to Nintendo for ransom payment, but the gaming giant declined to negotiate with them.

Following Nintendo’s refusal, Shadowbyt3$ shifted its financial demands directly to TinyPulse, setting a secondary deadline of 16 June. When this deadline passed without payment, they started leaking data samples onto their dark web platform.

Shadowbyt3$ claims to have stolen an 859-megabyte dataset comprising records from 2016 to early 2026, whereas according to Nintendo’s official statement, the exposed data is limited to a small subset of internal employee survey responses from previous years. Hackers still allege the files contain:

  • Bank statement PDFs
  • Employee names and corporate email addresses
  • W-9 tax forms containing employee identification numbers
  • Private messages and internal chat logs between staff members
  • Workforce progress plans and human resources analytics reports

Security experts have reviewed the published sample files and verified that multiple named individuals are active Nintendo of America employees.
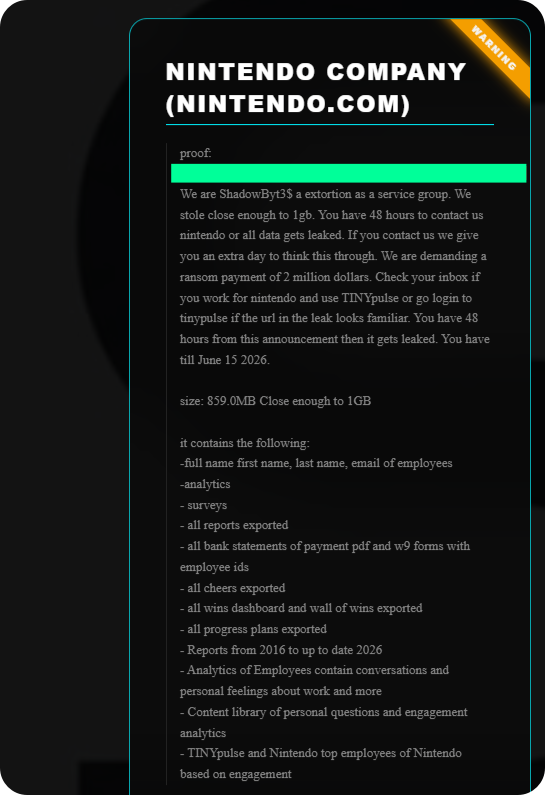
Cyberattack on Nintendo Vendor TinyPulse Allegedly Exposes Decade of Employee Records
Screenshot from SHADOWBYT3$’s dark web leak site

Ongoing Security Risks for Corporate Personnel

The exposure of W-9 tax documents and financial records introduces long-term identity theft risks because hackers routinely use this information to file fraudulent tax returns and divert financial refunds. Along with that, the exfiltrated banking details can help scammers to create targeted phishing emails using accurate corporate details to manipulate victims.

However, since TinyPulse operates a multi-tenant software architecture serving hundreds of corporate clients, other businesses using the platform may face similar data exposure risks.

Nintendo confirmed that the scope of the incident is restricted to Nintendo of America personnel. It is still recommended that any employee who uses the TinyPulse platform must implement credit freezes with reliable credit bureaus like Equifax, Experian, and TransUnion. They must also carefully monitor their tax filings for unauthorized changes.