



惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

Cyber Security Advisories - MS-ISAC
月光博客
月光博客
MyScale Blog
MyScale Blog
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
爱范儿
爱范儿
P
Proofpoint News Feed
人人都是产品经理
人人都是产品经理
Last Week in AI
Last Week in AI
罗磊的独立博客
G
Google Developers Blog
Y
Y Combinator Blog
博客园 - 【当耐特】
WordPress大学
WordPress大学
大猫的无限游戏
大猫的无限游戏
博客园 - 叶小钗
J
Java Code Geeks
酷 壳 – CoolShell
酷 壳 – CoolShell
V
Visual Studio Blog
美团技术团队
宝玉的分享
宝玉的分享
Jina AI
Jina AI
小众软件
小众软件
T
Tailwind CSS Blog
A
About on SuperTechFans

Ubuntu blog

Bring Zenoh to ROS 2 with snaps | Ubuntu Evolution of the RISC-V ISA. What next after RVA23? | Ubuntu Cut bloat, not features | Ubuntu Ubuntu now certified on Qualcomm Dragonwing™ IQ-8275 | Ubuntu Grace on the currents: Stonking Stingray | Ubuntu How we create a Canonical Academy exam | Ubuntu Surviving the uncharted: when dedicated OpenStack expertise is your best ally in disaster recovery  | Ubuntu Canonical joins the Open Secure AI Alliance | Ubuntu AI harnesses for telco autonomous networks | Ubuntu Arduino® VENTUNO™ Q is available for pre-order with Ubuntu pre-installed | Ubuntu Advantech AOM-2721 is now Ubuntu Certified | Ubuntu Canonical integrates NVIDIA Nemotron 3.5 Lightning with Ubuntu for always-on AI agents | Ubuntu Ubuntu’s virtualization hardware enablement (HWE) stack: a new model for confidential computing enablement | Ubuntu Confidential computing and the new regulatory focus on data in use | Ubuntu A day in the life of an Android developer with Anbox Cloud | Ubuntu Canonical announces the Enterprise Store as part of Ubuntu Pro | Ubuntu Tracing a memory leak bug in PID 1 and contributing an upstream fix: a Linux support story | Ubuntu MAAS installation: bare metal provisioning is easier than ever | Ubuntu Januscape vulnerability CVE-2026-53359 mitigations available | Ubuntu Managing Ubuntu on bare metal at scale | Ubuntu Ubuntu Server: a platform made for enterprise scale | Ubuntu Beyond safety and security: Why automotive open source demands dependability  | Ubuntu DirtyClone Linux kernel local privilege escalation vulnerability fixes available | Ubuntu pedit COW kernel local privilege escalation vulnerability mitigations | Ubuntu Canonical becomes Gold Sponsor of Trifecta Tech Foundation | Ubuntu Challenges designers face in open source (and how to fix them) | Ubuntu Hunting a 16-year-old SQLite bug with TLA+: is dqlite affected? | Ubuntu Anbox Cloud on C4A metal: Android, at scale, without friction | Ubuntu Canonical announces live kernel patching for Arm64 | Ubuntu How to use RISC-V custom instructions with Ubuntu | Ubuntu
Building an open source chain of trust: new research unco...
Canonical (C · 2026-07-06 · via Ubuntu blog

Canonical is pleased to share its latest research report, “The open source chain of trust.” Based on a survey of 500 DevOps professionals, the report highlights how organizations approach their open source software supply chains. While many companies are moving toward verifiable provenance and automated security workflows, internal misalignment and disjointed approaches remain serious challenges for most teams.

Read the report

Open source is the fabric of modern IT, but management remains fragmented

Open source powers development toolchains and underpins cloud-native platforms. It runs across on-prem, cloud, and edge environments. While organizations formalize policies and adopt security tools, many rely on fragmented processes with significant visibility gaps in CI/CD process between development and production stages. This research shows that 90% of respondents believe their organization needs to improve cross-team collaboration regarding open source software.
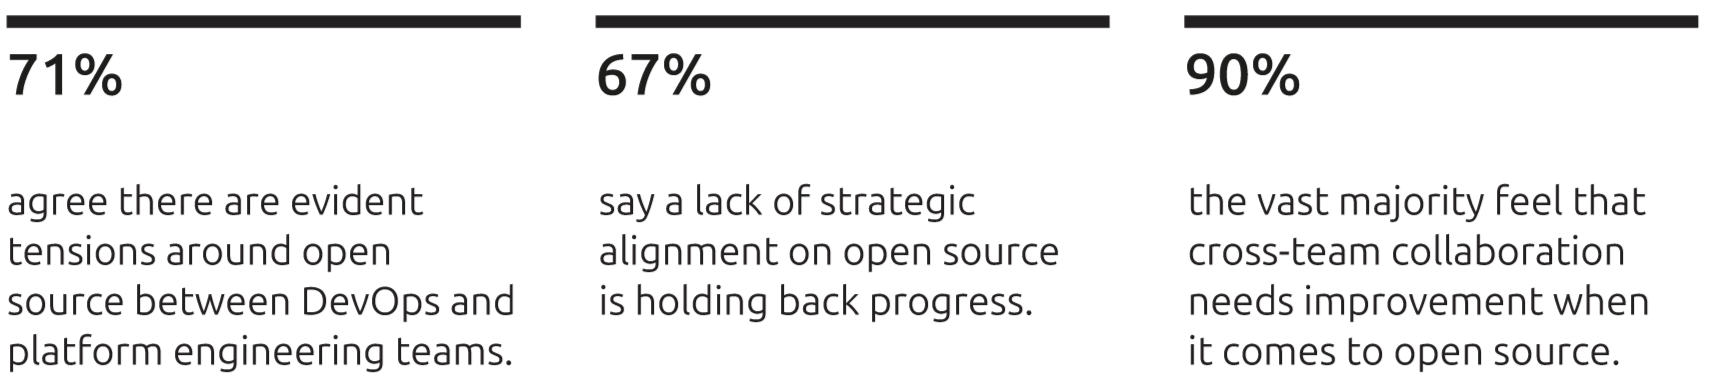
Figure 1: overview of key findings from the research

Organizations often stitch together components from many sources using inconsistent methods and misaligned upgrade cadences. Security teams struggle to manage transitive dependencies in this environment. Meanwhile, operations teams face constant trade-offs between stability and necessary changes.

Open source is a critical foundation of the enterprise, but managing the dependency sprawl can be an operational and security challenge. On top of these existing supply chain challenges, the cadence of software development is accelerating. Consequently, it is increasingly crucial for organizations to bring automation and cross-team collaboration into their SDLC governance.”

– Rachel Stephens, Research Director at RedMonk

Key findings from the research

The report identifies operational challenges and highlights how internal misalignment impacts software supply chains:
  • Cross-team tensions stall progress: 71% of respondents report tensions between DevOps and platform engineering teams regarding the scalable use of open source.
  • Manual processes hinder maturity: 35% of organizations still rely on manual code reviews for security. Another 21% use manual methods to track vulnerabilities.
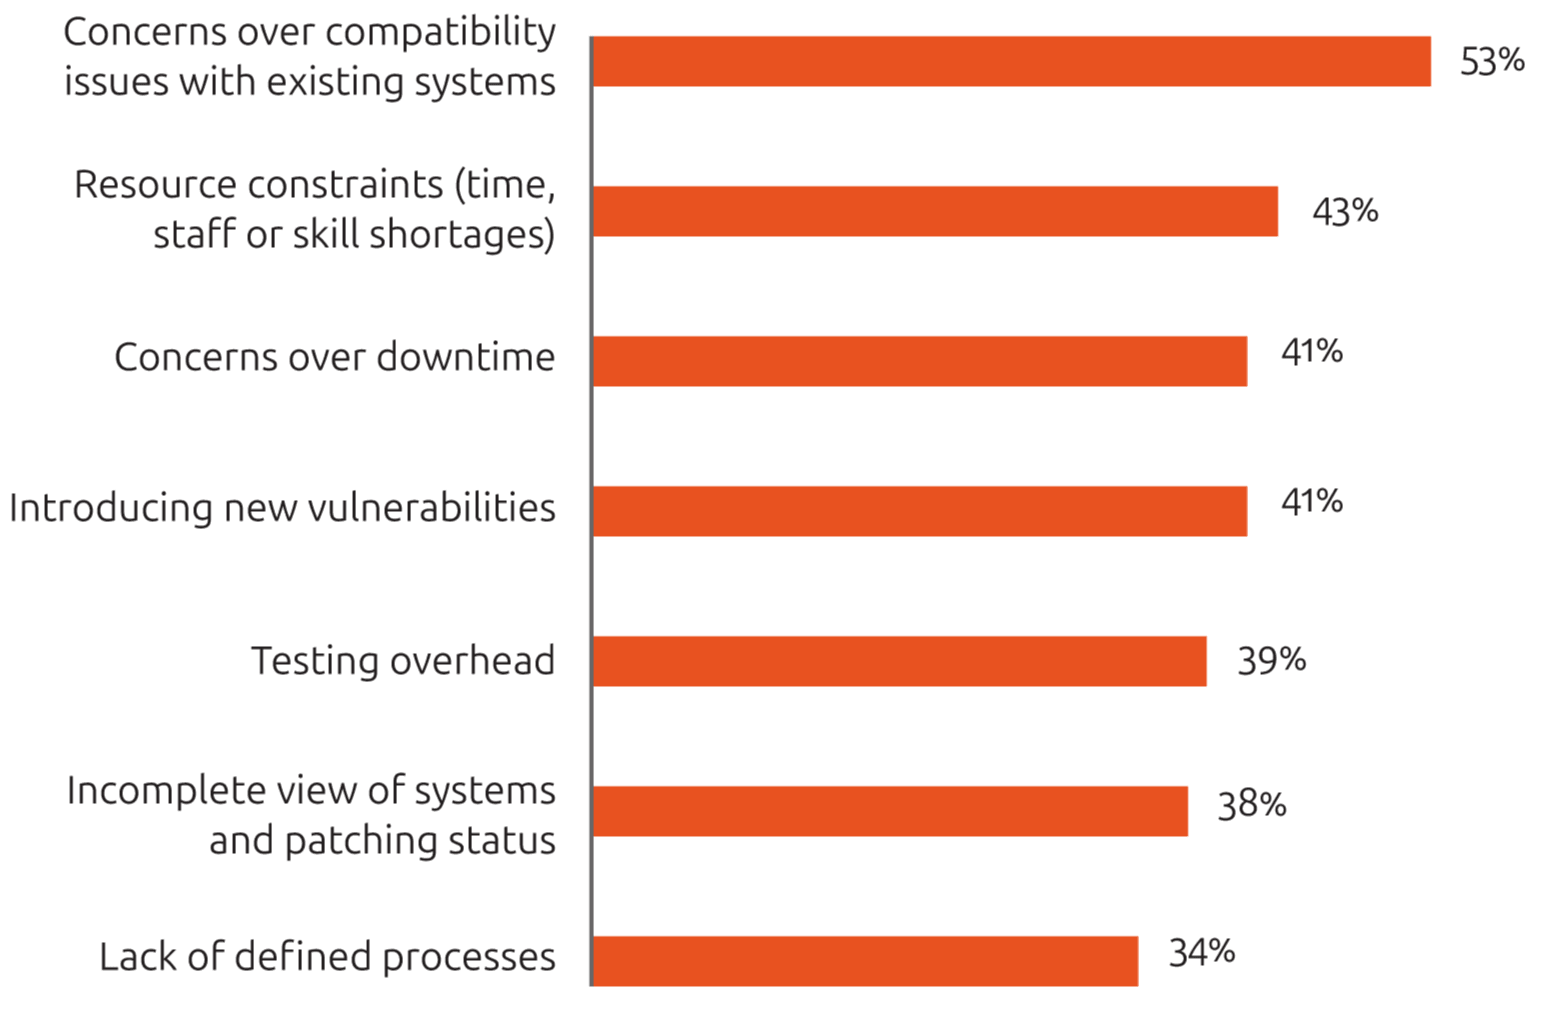
  • Operational risk drives patching delays: Primary causes for delays include system compatibility concerns (53%) and resource constraints like staff shortages (43%).

Figure 2: Most common causes of delays in organizations’ ability to patch vulnerabilities, top 3 combined answers.

Mitigating gaps through a trusted foundation

The research highlights a clear path toward more predictable and secure operations:

  • Rely on the operating system as a strategic control plane: 98% of respondents describe the OS as extremely or very important for detecting and applying updates to open source components, suggesting it can serve as a central layer to govern supply chain hygiene.
  • Establish verifiable provenance: 48% of respondents state that tracked packages would improve their confidence in software supply chain security.
  • Strengthening collaboration: Choosing the right platform as a foundation brings consistent governance and strengthens the working relationship between DevOps, security, and operations.

Discover all the insights from the research

“This new research highlights that scaling open source innovation requires organizations to move beyond fragmented workflows to adopt a stable foundation that can help fast-track security and compliance. At Canonical, we help our customers achieve exactly this by simplifying vulnerability management and providing a single, verifiable stack with trusted end-to-end provenance.”

– Lech Sandecki, Product Manager at Canonical

Trusted open source with Canonical

Maturing processes and improving internal alignment are critical for addressing security concerns. Through Ubuntu Pro, Canonical delivers consistent security maintenance for the operating system and thousands of upstream open source packages.

By streamlining vulnerability management and committing to up to 15 years of platform stability through backporting, Canonical helps resolve the inherent tension between rigorous security and operational uptime. This shift moves organizations from a state of fragmented visibility and complex management to one of securely designed architecture, ensuring the open source fabric they depend on remains a source of innovation and not of risk.

About the research

The report is based on a global survey of 500 IT professionals conducted by Vanson Bourne. Respondents represent organizations across the Americas, EMEA, and APAC.

Further resources on open source security

Read our latest research into software supply chains. Canonical offers in-depth guides to help you secure open source ecosystems and navigate supply chain complexities.

  • The state of software supply chains: Explore IDC research detailing why software supply security remains a challenge despite greater patching efforts, and how AI is making the compliance landscape more challenging. Download the research report  
  • A guide to open source vulnerability management: Discover the main challenges with open source security vulnerabilities, best practices for effective vulnerability management and how to apply cybersecurity frameworks like the NIST framework with Ubuntu Pro. Download the guide