

Senior Product Marketing Manager






Following the precedent set by Executive Order 14028, security and compliance teams increasingly request software bills of materials (SBOMs) to identify the open source components of their software projects, assess their vulnerability to emerging threats, and verify alignment with license policies. So, we asked ourselves, how do we make SBOMs easier to generate and share?
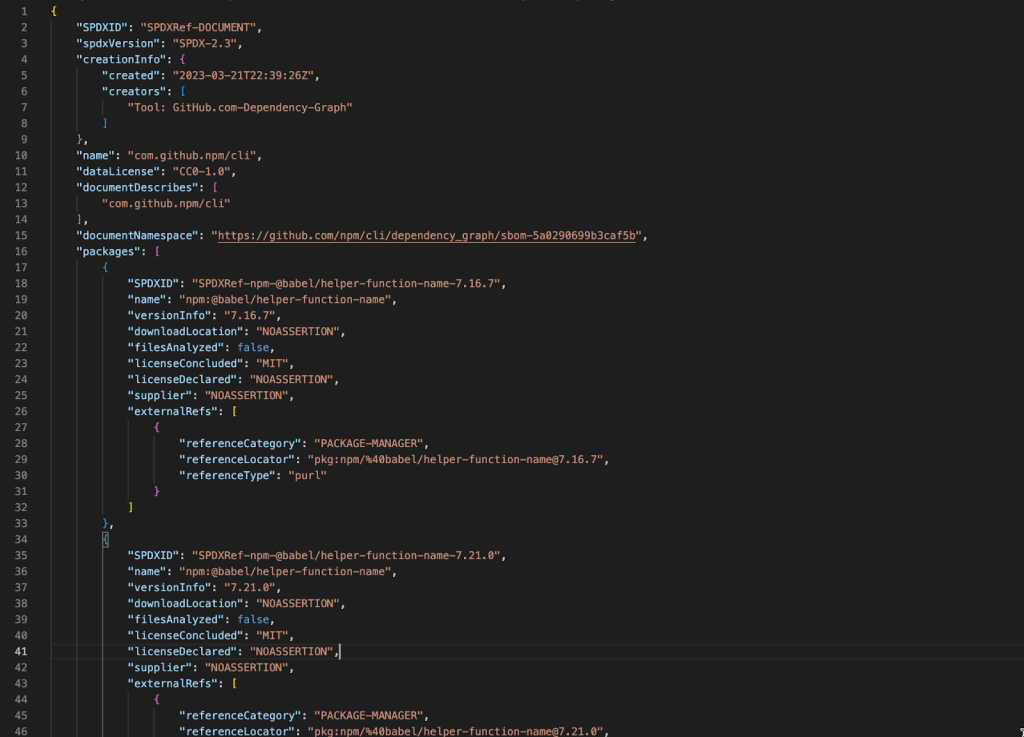
Today, we’re happy to announce a new Export SBOM function that allows anyone with read access to a GitHub cloud repository to generate an NTIA-compliant SBOM with a single click. The resulting JSON file saves project dependencies and metadata, like versions and licenses in the industry standard SPDX format, which can then be used with security and compliance workflows and tools, or reviewed in Microsoft Excel (use a JSON-to-CSV converter for compatibility with Google Sheets).
While this new self-service capability makes it easy to generate SBOMs on-demand, developers can also make SBOM generation a regular step of their development workflow. First, if you already have an SBOM for your project, you can upload it to the dependency graph to receive Dependabot alerts on any dependencies with known vulnerabilities. Next, use GitHub’s SBOM gh CLI extension to programmatically generate SBOMs from your repository’s dependency graph, or use a third-party GitHub Action to generate SBOMs at build time. A REST API for generating an SBOM from your dependency graph is coming soon.
As part of GitHub’s supply chain security solution, self-service SBOMs are free for all cloud repositories on GitHub.
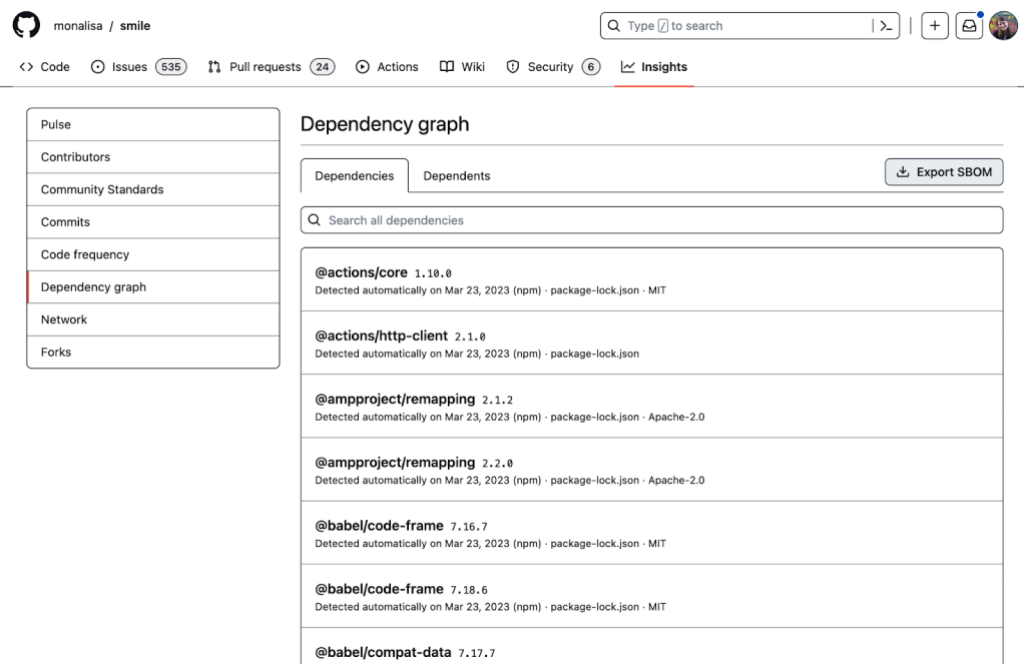
To generate an SBOM, simply click the new Export SBOM button on a repository’s dependency graph:
This creates a machine-readable JSON file in the SPDX format.
Senior Product Marketing Manager

此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。


