




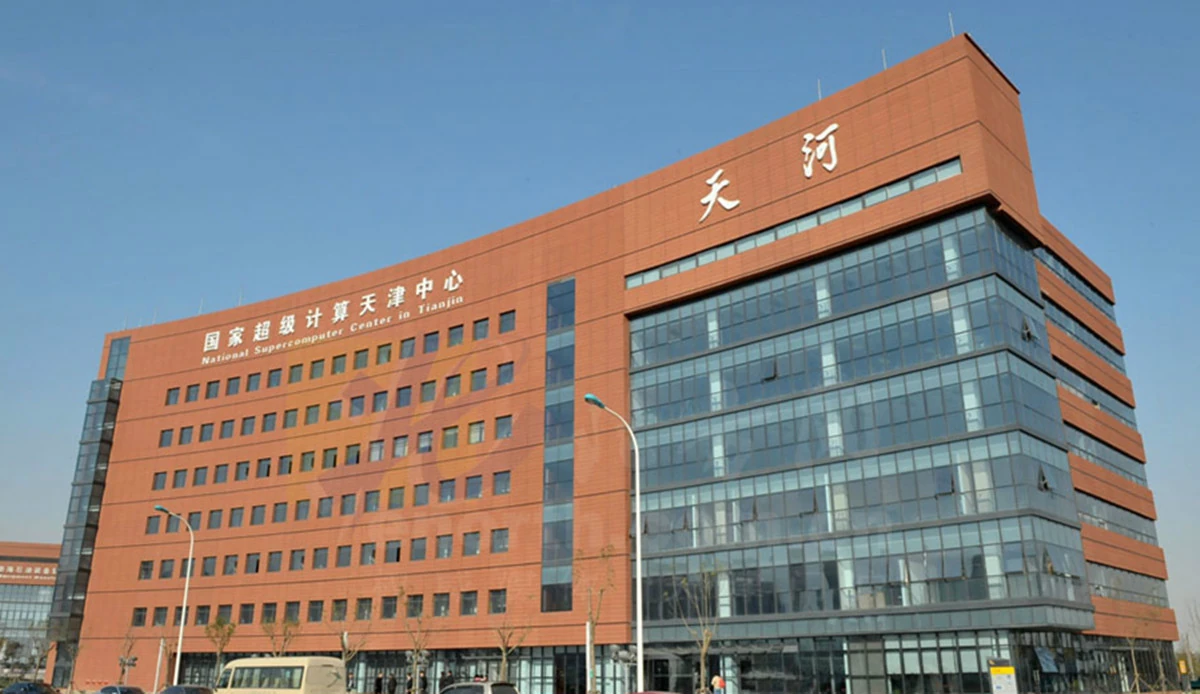
A massive alleged breach has hit China’s National Supercomputing Center (NSCC) in Tianjin. A hacker claims to have exfiltrated over 10 petabytes of highly sensitive data, including military, aerospace, and missile-related information. The facility supports around 6,000 clients, including scientific and defense organizations, raising serious concerns about national security and data exposure.
Cyber experts reviewing leaked samples say the attacker breached the system with relative ease and quietly exfiltrated massive volumes of data over several months without being detected. A group calling itself “FlamingChina” shared samples on Telegram, claiming the dataset includes sensitive research in aerospace, military, bioinformatics, and fusion.

The data is allegedly linked to major organizations such as Aviation Industry Corporation of China, Commercial Aircraft Corporation of China, and National University of Defense Technology. Chinese authorities have not yet commented.
CNN reported that cybersecurity experts say the group is selling limited samples of the stolen data for thousands of dollars, with full access costing hundreds of thousands, payable in cryptocurrency.
The alleged breach of the National Supercomputing Center in Tianjin could have major geopolitical consequences. Exposure of sensitive military and research data may give rival states valuable intelligence, increasing strategic pressure on China. The incident could escalate cyber tensions, fuel retaliation, and accelerate the global cyber arms race. It may also erode trust in Chinese infrastructure, impact international partnerships, and push governments to strengthen cybersecurity and control over critical technologies.
“Because the stolen data apparently includes military and aerospace research such as data from fighter jets and hypersonic missile testing, it could give China’s geopolitical rivals visibility of some of China’s most covert activity.” reported the CNN. “It may also cause questions to be asked about a policy which has seen vast resources channelled into China-owned and developed supercomputing specifically to reduce dependence on technology (mainly chips) manufactured in the West – a policy which would have seemed more important in light of Trump’s changeable policy of chip export controls.”
CNN could not independently verify the breach, but multiple experts who reviewed the leaked samples believe the data is likely genuine. The files reportedly include “secret”-marked documents, technical data, and simulations of weapons systems, consistent with the type of workloads handled by supercomputing centers.
The National Supercomputing Center in Tianjin is a major high-performance computing hub launched in 2009. It provides advanced processing power to universities, research institutes, and government agencies, supporting fields like aerospace, defense, AI, and weather forecasting. It hosts systems such as Tianhe-1A and enables large-scale simulations and data analysis.
According to the media, the attacker allegedly gained access via a compromised VPN and used a botnet to quietly extract data over six months, distributing traffic to avoid detection. Analysts say the method was effective but not especially sophisticated, highlighting systemic weaknesses. If confirmed, the incident would underscore longstanding cybersecurity gaps in China’s infrastructure, despite ongoing efforts to improve defenses.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, newsletter)
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。