


惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

让小产品的独立变现更简单 - ezindie.com
月光博客
月光博客
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
T
Tailwind CSS Blog
大猫的无限游戏
大猫的无限游戏
The Cloudflare Blog
博客园_首页
Jina AI
Jina AI
WordPress大学
WordPress大学
小众软件
小众软件
阮一峰的网络日志
阮一峰的网络日志
Apple Machine Learning Research
博客园 - 三生石上(FineUI控件)
酷 壳 – CoolShell
酷 壳 – CoolShell
博客园 - 叶小钗
美团技术团队
IT之家
IT之家
爱范儿
爱范儿
有赞技术团队
有赞技术团队
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
量子位
博客园 - 聂微东
人人都是产品经理
人人都是产品经理
博客园 - 【当耐特】

www.infosecurity-magazine.com

Just Three Ransomware Gangs Accounted for 40% of Attacks Last Month Google Chrome Rolls Out Protection Against Infostealers Targeting Session Cookies STX RAT Targets Finance Sector With Advanced Stealth Tactics Bitcoin Depot Reports $3.6m Crypto Theft After System Breach Atomic Stealer MacOS ClickFix Attack Bypasses Apple Security Warnings Middle East Hack-for-Hire Operation Traced to South Asian Cyber Espionage Group Governance Gaps Emerge as AI Agents Drive 76% Increase in NHIs Google Warns of New Threat Group Targeting BPOs and Helpdesks Google API Keys Quietly Gain Access to Gemini on Android Devices Critical Vulnerability in Ninja Forms Exposes WordPress Sites Anthropic Launches Project Glasswing to Use AI to Find and Fix Critical Software Vulnerabilities US Thwarts DNS Hijacking Network Controlled by Russian APT28 Hackers Claude Discovers Apache ActiveMQ Bug Hidden for 13 Years Iran‑Backed Threat Actors Hit US CNI Providers via Internet‑Facing OT Assets Russian APT28 Hackers Hijack Routers to Steal Credentials, UK Security Agency Warns GPU Rowhammer Attack Enables Privilege Escalation and Full System Compromise GrafanaGhost Exploit Bypasses AI Guardrails for Silent Data Exfiltration Over $17bn Lost to Cyber Fraud in the Last Year, Warns FBI Storm-1175 Exploits Flaws in High-Velocity Medusa Attacks Fortinet Releases Emergency Patch After FortiClient EMS Bug Is Exploited New Phishing Platform Used in Credential Theft Campaigns Against C-Suite Execs New 'Storm' Infostealer Remotely Decrypts Stolen Credentials NCSC Issues Security Alert Over Hackers Targeting WhatsApp and Signal Accounts Apple Expands iOS 18 Security Updates Amid DarkSword Threat Researchers Observe Sub-One-Hour Ransomware Attacks GitHub Used as Covert Channel in Multi-Stage Malware Campaign Most CNI Firms Face Up to £5m in Downtime from OT Attacks Google Introduces Android Dev Verification Amid Openness Debate New Venom Stealer MaaS Platform Automates Continuous Data Theft Chinese Hackers Target European Governments in Espionage Campaigns
RSA Conference: UK NCSC Head Urges Industry to Develop Vi...
Kevin Poireault · 2026-03-25 · via www.infosecurity-magazine.com

The head of the UK’s national cybersecurity agency is calling for security professionals to “seize the disruptive vibe coding opportunity” to make software more secure.

However, this must be coupled with the rapid development of vibe coding safeguards for AI code-generation tools to become “a net positive for security”.

Delivering a keynote speech during the RSA Conference in San Francisco on March 24, Richard Horne chief executive of the UK’s National Cyber Security Centre (NCSC), said the cybersecurity industry should leverage the exploding use of AI-assisted software development – also known as vibe coding – to reduce the collective vulnerability to cyber-attacks.
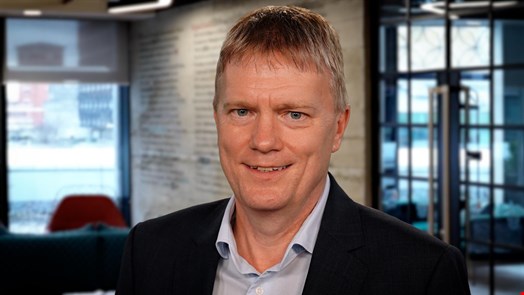
Richard Horne. Source: UK's National Cyber Security Centre

Whilst software produced without human review could potentially propagate vulnerabilities, well-trained AI tooling writing software which is secure by design could transform cybersecurity outcomes.

“The attractions of vibe coding are clear. Disrupting the status quo of manually produced software that is consistently vulnerable is a huge opportunity, but not without risk of its own,” he said.

“The AI tools we use to develop code must be designed and trained from the outset so that they do not introduce or propagate unintended vulnerabilities.”

NCSC’s Secure Vibe Coding Commandments

In parallel, Dave Chismon, CTO for architecture at NCSC, published a blog on March 24 arguing that, while AI-generated code currently poses intolerable risks for many organizations, vibe coding shows “glimpses of a new paradigm” allowing “experienced developers to massively increase their productivity.”

Chismon predicted the business benefits of using AI to write code will drive up adoption. He argued it is vital that security professionals start engaging with the risks now and embed core security principles that will make software less vulnerable to attack.

His suggested commandments for securing vibe coding include:

  • Integrate secure by default coding practices into vibe coding tools: AI models must generate safe, hardened code out of the box
  • Adopt a ‘trust but verify’ approach: demand provable model provenance to ensure no malicious backdoors in AI-generated code
  • Perform AI-powered code reviews: use AI to audit all code (human-written and AI-generated) and scan for vulnerabilities
  • Implement deterministic guardrails: enforce strict, rule-based controls to limit what code can do, even if it’s compromised
  • Secure hosting platforms: build environments that sandbox and protect against bad code, AI-generated or not
  • Automate security hygiene: let AI handle docs, tests, fuzzing, and threat modeling for every piece of software

The NCSC CTO emphasized the need to start implementing some of these guardrails now, “without waiting five years for the vibe future.”

“As just one example, the ability to use AI to harden the hosting or code of a legacy (even end-of-life) critical application would pay off a lot of technical and security debt carried by an organization,” Chismon said.

He also highlighted that AI could help with securing coding practices, from the smallest tasks, like maintaining the allow-list of URLs an application is permitted to talk to, to bigger tasks, like rewriting critical components in a framework that protects from common security issues by default, or in a memory safe language.

Chismon envisaged “a possible future” where AI code ends up far more restricted and locked down by default than the best on-premises or software-as-a-service (SaaS) product.

“Ironically, it may even present a solution to organizations still worried about the old concerns with cloud services, who have avoided migrating in all these years,” he added.

Read now: Palo Alto Networks Introduces New Vibe Coding Security Governance Framework