








A rapidly expanding ransomware-as-a-service (RaaS) operation has claimed more than 320 victims, with the bulk of attacks occurring in early 2026.
According to researchers at Check Point, the group, known as The Gentlemen, has gained traction among affiliates and is increasingly targeting enterprise environments using a mix of modular tooling and cross-platform payloads.
First identified in mid-2025, the operation promotes its services on underground forums and recruits technically skilled partners.
Affiliates are provided with ransomware variants written in the Go programming language that support Windows, Linux, NAS and BSD systems, along with a separate ESXi encryptor developed in C.
The ransomware toolkit includes features designed to streamline large-scale intrusions. Affiliates can leverage built-in lateral movement capabilities, credential reuse and Group Policy-based deployment to trigger simultaneous encryption across domain environments.
In one observed case, attackers achieved domain controller access before deploying payloads across multiple systems. The activity included credential harvesting, remote execution via administrative shares and widespread reconnaissance.
The attackers also disabled endpoint protections and used scheduled tasks, services and registry changes to maintain persistence.
Key capabilities observed in the attacks include:
Cross-platform encryption covering endpoints, servers and virtualized environments
Automated lateral movement using stolen domain credentials
Group Policy deployment for rapid, domain-wide execution
Defense evasion through disabling antivirus and firewall protections
The ransomware also terminates processes linked to databases, backup tools and virtual machines to maximize impact, while deleting shadow copies and logs to hinder recovery and forensic analysis.
During incident response, Check Point researchers identified the use of SystemBC, a proxy malware commonly associated with human-operated ransomware campaigns. The tool enables covert communication via SOCKS5 tunnels and can deliver additional payloads directly into memory.
Telemetry from a related command-and-control (C2) server revealed more than 1570 infected systems globally. The distribution, heavily concentrated in the US, UK and Germany, suggests a focus on organizational targets rather than opportunistic consumer infections.
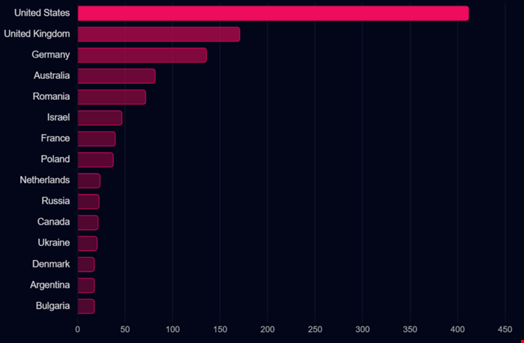
Check Point researchers noted that it remains unclear whether SystemBC is fully integrated into The Gentlemen ecosystem or simply used by certain affiliates. However, its presence alongside tools such as Cobalt Strike suggests a modular attack chain.
The intrusion also showed adaptability. When SystemBC deployment was blocked, attackers shifted to alternative C2 channels and established persistence using remote desktop and remote access software.
CPR emphasized that the combination of scalable affiliate recruitment, enterprise-focused tooling and integration with established post-exploitation frameworks increases the threat level.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。