


惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

S
SegmentFault 最新的问题
MongoDB | Blog
MongoDB | Blog
J
Java Code Geeks
Stack Overflow Blog
Stack Overflow Blog
The GitHub Blog
The GitHub Blog
博客园 - Franky
博客园 - 叶小钗
大猫的无限游戏
大猫的无限游戏
V
Visual Studio Blog
IT之家
IT之家
美团技术团队
博客园 - 司徒正美
Martin Fowler
Martin Fowler
Last Week in AI
Last Week in AI
酷 壳 – CoolShell
酷 壳 – CoolShell
Vercel News
Vercel News
雷峰网
雷峰网
B
Blog
WordPress大学
WordPress大学
aimingoo的专栏
aimingoo的专栏
D
Docker
P
Proofpoint News Feed
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
爱范儿
爱范儿

www.infosecurity-magazine.com

Just Three Ransomware Gangs Accounted for 40% of Attacks Last Month Google Chrome Rolls Out Protection Against Infostealers Targeting Session Cookies STX RAT Targets Finance Sector With Advanced Stealth Tactics Bitcoin Depot Reports $3.6m Crypto Theft After System Breach Atomic Stealer MacOS ClickFix Attack Bypasses Apple Security Warnings Middle East Hack-for-Hire Operation Traced to South Asian Cyber Espionage Group Governance Gaps Emerge as AI Agents Drive 76% Increase in NHIs Google Warns of New Threat Group Targeting BPOs and Helpdesks Google API Keys Quietly Gain Access to Gemini on Android Devices Critical Vulnerability in Ninja Forms Exposes WordPress Sites Anthropic Launches Project Glasswing to Use AI to Find and Fix Critical Software Vulnerabilities US Thwarts DNS Hijacking Network Controlled by Russian APT28 Hackers Claude Discovers Apache ActiveMQ Bug Hidden for 13 Years Iran‑Backed Threat Actors Hit US CNI Providers via Internet‑Facing OT Assets Russian APT28 Hackers Hijack Routers to Steal Credentials, UK Security Agency Warns GPU Rowhammer Attack Enables Privilege Escalation and Full System Compromise GrafanaGhost Exploit Bypasses AI Guardrails for Silent Data Exfiltration Over $17bn Lost to Cyber Fraud in the Last Year, Warns FBI Storm-1175 Exploits Flaws in High-Velocity Medusa Attacks Fortinet Releases Emergency Patch After FortiClient EMS Bug Is Exploited New Phishing Platform Used in Credential Theft Campaigns Against C-Suite Execs New 'Storm' Infostealer Remotely Decrypts Stolen Credentials NCSC Issues Security Alert Over Hackers Targeting WhatsApp and Signal Accounts Apple Expands iOS 18 Security Updates Amid DarkSword Threat Researchers Observe Sub-One-Hour Ransomware Attacks GitHub Used as Covert Channel in Multi-Stage Malware Campaign Most CNI Firms Face Up to £5m in Downtime from OT Attacks Google Introduces Android Dev Verification Amid Openness Debate New Venom Stealer MaaS Platform Automates Continuous Data Theft Chinese Hackers Target European Governments in Espionage Campaigns
44% Surge in App Exploits as AI Speeds Up Cyber-Attacks, ...
2026-02-25 · via www.infosecurity-magazine.com

Written by

Photo of Alessandro  Mascellino

There has been a 44% increase in cyber-attacks exploiting public-facing applications, IBM X-Force has warned.

The newly published the 2026 IBM X-Force Threat Intelligence Index report points to missing authentication controls and AI-enabled vulnerability scanning as major drivers behind the spike.

Vulnerability exploitation emerged as the leading cause of incidents in 2025, accounting for 40% of cases observed by IBM X-Force. At the same time, active ransomware and extortion groups grew 49% year over year, signalling a more fragmented ecosystem. Publicly disclosed victim counts rose by roughly 12%.

"Attackers aren't reinventing playbooks, they're speeding them up with AI," said Mark Hughes, global managing partner for cybersecurity services at IBM. "The core issue is the same: businesses are overwhelmed by software vulnerabilities. The difference now is speed."
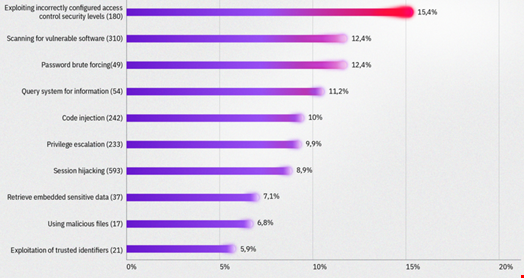
Top 10 attack patterns discovered by X-Force Red in 2025. Source:  IBM X-Force.
Top 10 attack patterns discovered by X-Force Red in 2025. Source: IBM X-Force.

IBM found that large supply chain and third-party compromises have nearly quadrupled since 2020. Attackers are increasingly targeting software build and deployment environments, along with SaaS integrations, exploiting trusted relationships and CI/CD automation in development workflows.
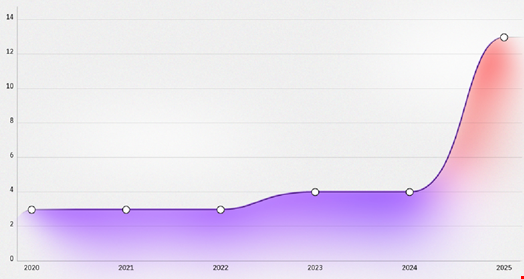
The growth of major supply chain or third-party compromises since 2015. Source: IBM X-Force.

The report attributed part of this growth to the blurring line between nation-state and financially motivated threat actors, as tactics circulate on underground forums and AI streamlines reconnaissance and exploitation.

Additional findings from the report include:

  • Infostealer malware exposed over 300,000 ChatGPT credentials in 2025

  • Manufacturing accounted for 27.7% of incidents, marking its fifth consecutive year as the most targeted sector

  • North America represented 29% of observed cases, up from 24% in 2024, becoming the most attacked region for the first time in 6 years
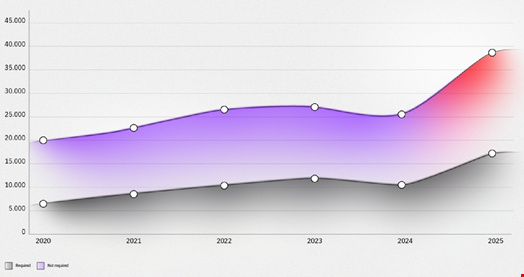
Most vulnerabilities tracked in 2025 did not require authentication to exploit. Source: IBM X-Force.

AI Lowers Barriers And Expands Risk

The research also describes how leaked tooling and AI capabilities are lowering barriers to entry for ransomware actors.

Read more about AI in cyber-attacks: AI-powered Cyber-Attacks Up Significantly in the Last Year, Warns CrowdStrike

Smaller, transient groups are reusing established playbooks and automating parts of their operations. As multimodal AI models mature, IBM expects adversaries to automate more complex tasks, including reconnaissance and advanced ransomware attacks.

AI is also accelerating the attacker lifecycle more broadly. IBM observed threat actors using AI to conduct research, analyse large data sets and refine attack paths in real time. In one example, North Korean IT worker schemes employed AI-driven image manipulation to create synthetic identities and translation tools to engage across global marketplaces.

The findings suggest that while techniques may be familiar, the pace and scale of exploitation are shifting rapidly as AI becomes embedded in the cybercrime ecosystem.