







Welcome to this week’s edition of the Threat Source newsletter.
Howdy friends, and hello from Cisco Live U.S., here in sunny (and very hot) Las Vegas!
An interesting quirk of being sent to one of these events is you learn to understand your limits as a person. Cisco Live is a three-day event, and it encompasses so many people, partners, workshops, CTFs (!!), and symposiums. I can confidently say that here on day three, I’ve had rarely a moment’s rest and, as they say, my dogs are barking.
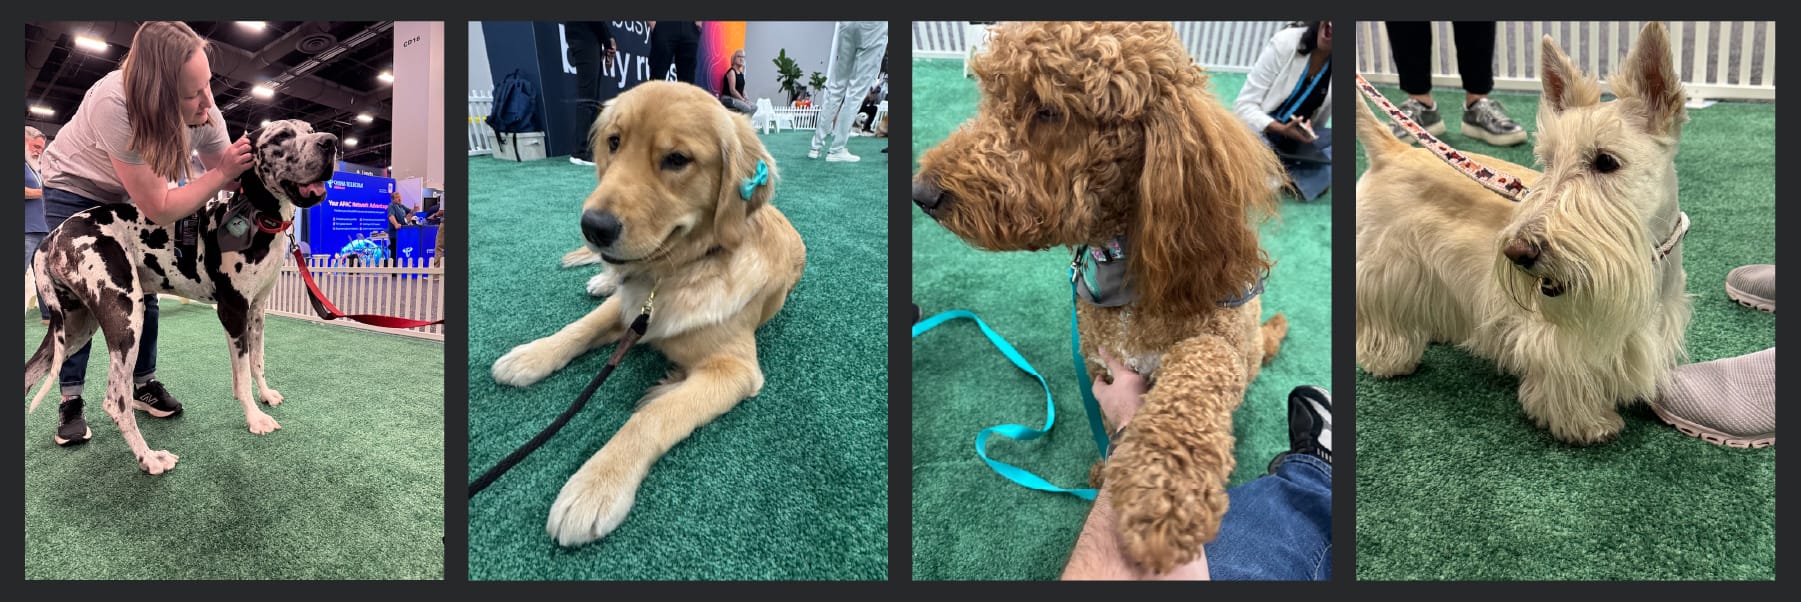
Speaking of dogs, did you know that at Cisco Live we have therapy dogs? Healing Hounds is a local Las Vegas therapy dog volunteer group, and Splunk sponsored them this year. Every two hours, the goodest boys and girls rotate in and you can stop what you are doing to immediately go give them pets. Look at these cute faces. LOOK AT THEM.
Back to limits. One thing I’ve discovered is that conferences like this can be loud. I don’t mind loud. Loud is fine. But eight hours of noise at high levels is stressful. So, I use my Apple AirPods in noise cancelling mode, and it keeps even a massive conference like CLUS to a very manageable dull roar. If you own a pair, or any earplugs, trust me. Use them. It’s not going to shut out the world, but it will give you more stamina in an environment with bright lights and loud noises.
With that much stimuli for an extended period, you must create some space for yourself. Conferences that have quiet or chill spaces, shout out to you! A place for humans to find a moment of rest in the endurance contest that is a technology convention is a wonderful thing.
So what is the vibe at CLUS? AI. All the AI. Not from a product perspective, but from an infrastructure and security perspective. How do folks plan to move and manage that much data, especially in an agentic world? It’s a hot debate, given what I’ve listened to so far. Every business is struggling with it in their own ways, and conferences like CLUS are good opportunities to put those companies in the same room and ideate on ways to process and defend in an AI world. We’re talking many hundreds of zettabytes of data daily, the kind of data pipelines the entire world runs on. At that scale, the challenge is just wild and almost incomprehensible. I’m glad I could help and be a part of those discussions.
As the summer starts, the great patchening is coming as vendors start issuing rapid patches and CVE advisories. This is the quiet before the storm, so enjoy these cute dog photos! Black Hat and DEF CON are around the corner, as well! And always find time during these fire drills to take care of yourself, and if you can, pet some dogs.
The one big thing
Cisco Talos is expanding our Threat Hunting program to proactively track down advanced adversaries who deliberately slip past traditional detection thresholds. By combining AI-driven telemetry analysis with human expert validation, we continuously hunt for hidden threats across endpoint, network, and identity data. This hypothesis-driven approach allows us to identify complex intrusions — like a recent KongTuke command-and-control (C2) discovery — before a formal detection signature even exists.
Why do I care?
Most security tools operate on a simple principle: If a known-bad pattern appears, fire an alert. But as threat actors increasingly leverage AI to move faster and intentionally stay under the radar, relying solely on automated alerts leaves massive blind spots. Hypothesis-driven hunting addresses this gap by correlating weak signals across an environment, allowing defenders to piece together ambiguous anomalies and uncover sophisticated intrusions that would otherwise go unnoticed.
So now what?
If your team lacks the dedicated headcount for continuous hunting, Cisco Talos Threat Hunting can bridge the gap. Reach out to your Cisco account team, explore our new dedicated portal in Cisco Security Cloud Control, and read the full blog for a detailed breakdown of our recent KongTuke C2 investigation.
Top security headlines of the week
Global stock exchange hit by monthslong email campaign
A threat actor got a near-continuous view into an influential finance executive's email inbox, thanks to clever use of legitimate, native Windows tools. (Dark Reading)
One-click GitHub dev attack lets attackers steal full GitHub OAuth tokens
The vulnerability allows attackers to install malicious VS Code extensions that steal GitHub OAuth tokens when they are passed to GitHub.dev by exploiting a message-passing mechanism between the main VS Code window and webviews. (The Hacker News)
FBI-flagged phishing kit “Kali365” expands its reach
Once targeting just Microsoft 365, the phishing-as-a-service platform now aims at AWS, Okta, and Russian platforms, while relying on device code phishing. (Dark Reading)
Dozens of Red Hat packages backdoored through its official NPM channel
Official Red Hat NPM accounts have been compromised and used to push a malicious worm that spreads from machine to machine, where it pilfers sensitive credentials in hopes of stealing yet more confidential data, researchers said. (Ars Technica)
“HTTP/2 Bomb” exploit knocks web servers offline in seconds
The attack potentially affects over 880,000 websites that support HTTP/2 and run default NGINX, Apache HTTPD, Microsoft IIS, Envoy, or Cloudflare Pingora configurations. (SecurityWeek)
Can’t get enough Talos?
Winning the cyber marathon with Tony Giandomenico
In the high-speed world of cybersecurity, the difference between a breach and a breakthrough often comes down to endurance. Tony Giandomenico, Senior Director of Product Management with Cisco Talos, joins me to discuss Talos Threat Hunting, the challenges of leading major product launches, and the grueling discipline of Ironman triathlons.
When synthetic logs don’t lie: Generating coherent attack stories for better detection
Are your detection rules failing because your test data lacks the nuance of a real-world network? In this episode of Talos Takes, Amy sits down with David Bianco to discuss why traditional synthetic data often falls short and how his new open-source project, EvidenceForge, is changing the game.
Upcoming events where you can find Talos
- Cisco Live U.S. (May 31 – June 4) Las Vegas, Nevada
- Black Hat USA (Aug. 1 – 6) Las Vegas, Nevada
Most prevalent malware files from Talos telemetry over the past week
SHA256: 9f1f11a708d393e0a4109ae189bc64f1f3e312653dcf317a2bd406f18ffcc507
MD5: 2915b3f8b703eb744fc54c81f4a9c67f
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=9f1f11a708d393e0a4109ae189bc64f1f3e312653dcf317a2bd406f18ffcc507
Example Filename: VID001.exe
Detection Name: Win.Worm.Coinminer::1201
SHA256: 9896a6fcb9bb5ac1ec5297b4a65be3f647589adf7c37b45f3f7466decd6a4a7f
MD5: 38de5b216c33833af710e88f7f64fc98
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=9896a6fcb9bb5ac1ec5297b4a65be3f647589adf7c37b45f3f7466decd6a4a7f
Example Filename: sample.exe
Detection Name: Win.Tool.Procpatcher::1201
SHA256: c0ad494457dcd9e964378760fb6aca86a23622045bca851d8f3ab49ec33978fe
MD5: bf9672ec85283fdf002d83662f0b08b7
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=c0ad494457dcd9e964378760fb6aca86a23622045bca851d8f3ab49ec33978fe
Example Filename: f_000b97.html
Detection Name: W32.C0AD494457-95.SBX.TG
SHA256: afc8a00883a4ea07df2dc1d4ed02f8a23b35c9456413b438a2d9ce3ae5076638
MD5: cc4d231df34e57f59eb970353c7d9de2
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=afc8a00883a4ea07df2dc1d4ed02f8a23b35c9456413b438a2d9ce3ae5076638
Example Filename: AutoPico.exe
Detection Name: PUA.Win.Tool.Kmsactivator::
SHA256: a31f222fc283227f5e7988d1ad9c0aecd66d58bb7b4d8518ae23e110308dbf91
MD5: 7bdbd180c081fa63ca94f9c22c457376
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=a31f222fc283227f5e7988d1ad9c0aecd66d58bb7b4d8518ae23e110308dbf91
Example Filename: d4aa3e7010220ad1b458fac17039c274_62_Exe.exe
Detection Name: Win.Dropper.Miner::95.sbx.tg**