Scale data protection with automated governance in Unity Catalog
As data estates grow, every organization that manages sensitive data at scale faces the same question: how do you ensure that sensitive data is protected consistently across every table, whether it contains PII, financial records, health data, or anything else subject to compliance requirements?
AI further heightens this problem. Users can access data in more ways than before, through Genie, agents, APIs and more. Protection has to keep pace with the demand for data, or access controls end up limiting the empowerment that technology has created.
The answer cannot be manual configuration per table. It has to be a system where governance teams define the rules once, and protection follows the data automatically across the entire data estate as it is created and classified. That way, users and agents can be granted broad access to the platform without being granted broad access to sensitive data.
Today, we are excited to announce the General Availability of three complementary capabilities in Unity Catalog that make this possible: Attribute-Based Access Control (ABAC) policies for row filtering and column masking, Governed Tags, and automated Data Classification.
Why manual data governance and access controls don’t scale
Three problems stand in the way of sensitive data protection at scale.
- Access rules configured per object are repetitive and prone to inconsistency. When every table requires its own row filter or column mask, subtle differences creep in: different masking logic for the same column type, outdated rules on older tables, conflicting definitions across teams.
- Enforcement that depends on coordination with object owners leaves gaps. Data producers are experts at creating data, but there’s significant overhead to ensure all columns are classified and no sensitive data slips in. Enforcement steps get missed or stall on people who have other work to do, and gaps only surface during audits or compliance checks.
- Manual identification of sensitive data can't keep pace with growth. New tables and data records arrive continuously, and the business expects to use them right away. If detection relies on humans, or on detection logic hand-coded into individual pipelines for every type of data that comes in, it will lag behind both the data and the demand.
These challenges require a shift away from manual, per-object governance.
How Unity Catalog enables high leverage data governance with ABAC, tags, and classification
Access rules need to apply dynamically based on attributes, sensitive data needs to be detected as it appears, and responsibilities need to spread across specialized roles so no single person is a bottleneck. Unity Catalog brings this together through three complementary capabilities, paired with a permission model that enables separation of duties: attribute-based access control (ABAC) policies, governed tags, and agentic data classification.
- ABAC policies are Unity Catalog's dynamic access control model. It controls access based on the attributes of the data, so a single policy can cover many matching tables instead of each one being configured individually. An ABAC policy evaluates tag-based conditions and applies row filters, which control which rows a user sees, and column masks, which control what values a user sees for specific columns, automatically to every matching object across entire catalogs and schemas. A governance admin defines the policy once, and new data picks up protection as soon as the right tags are in place.
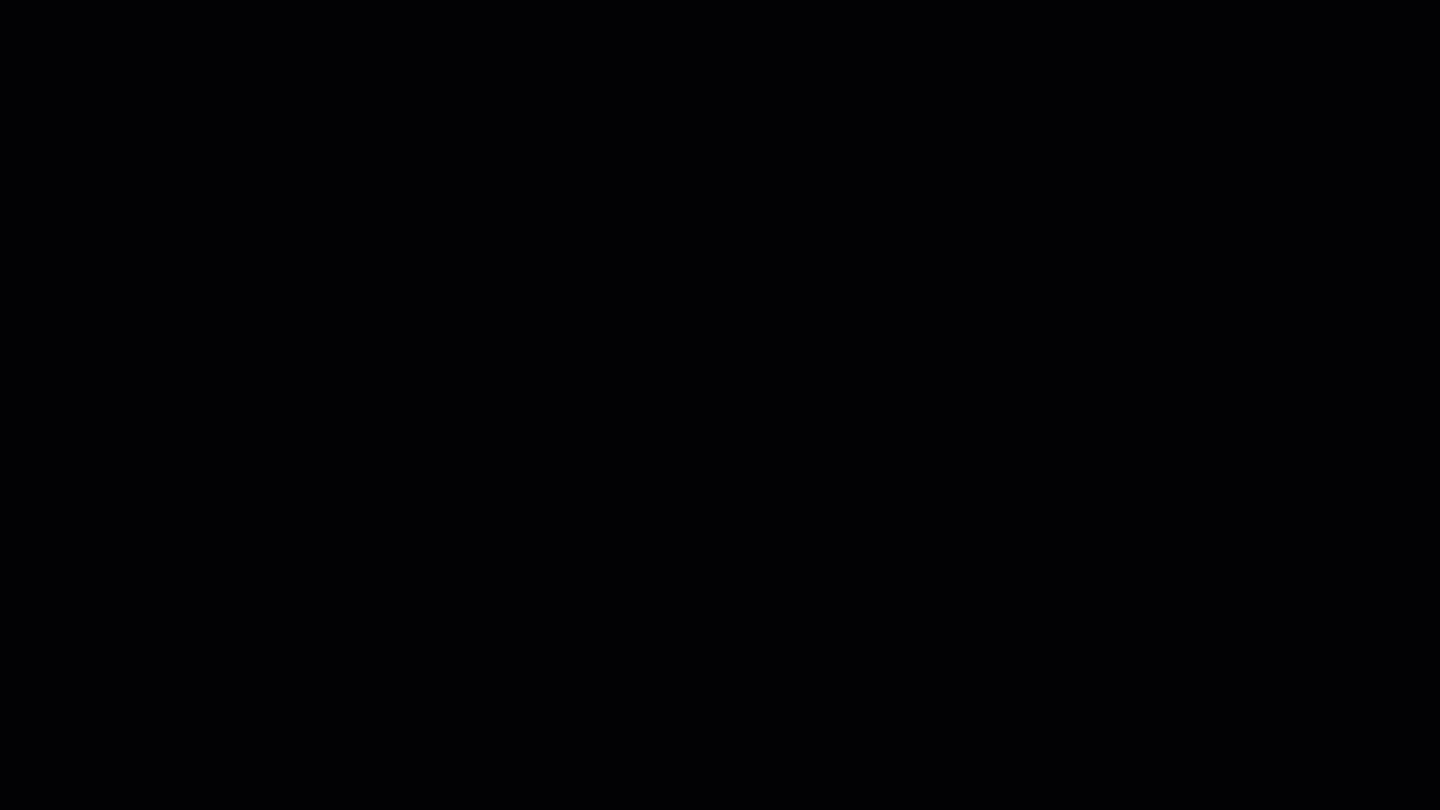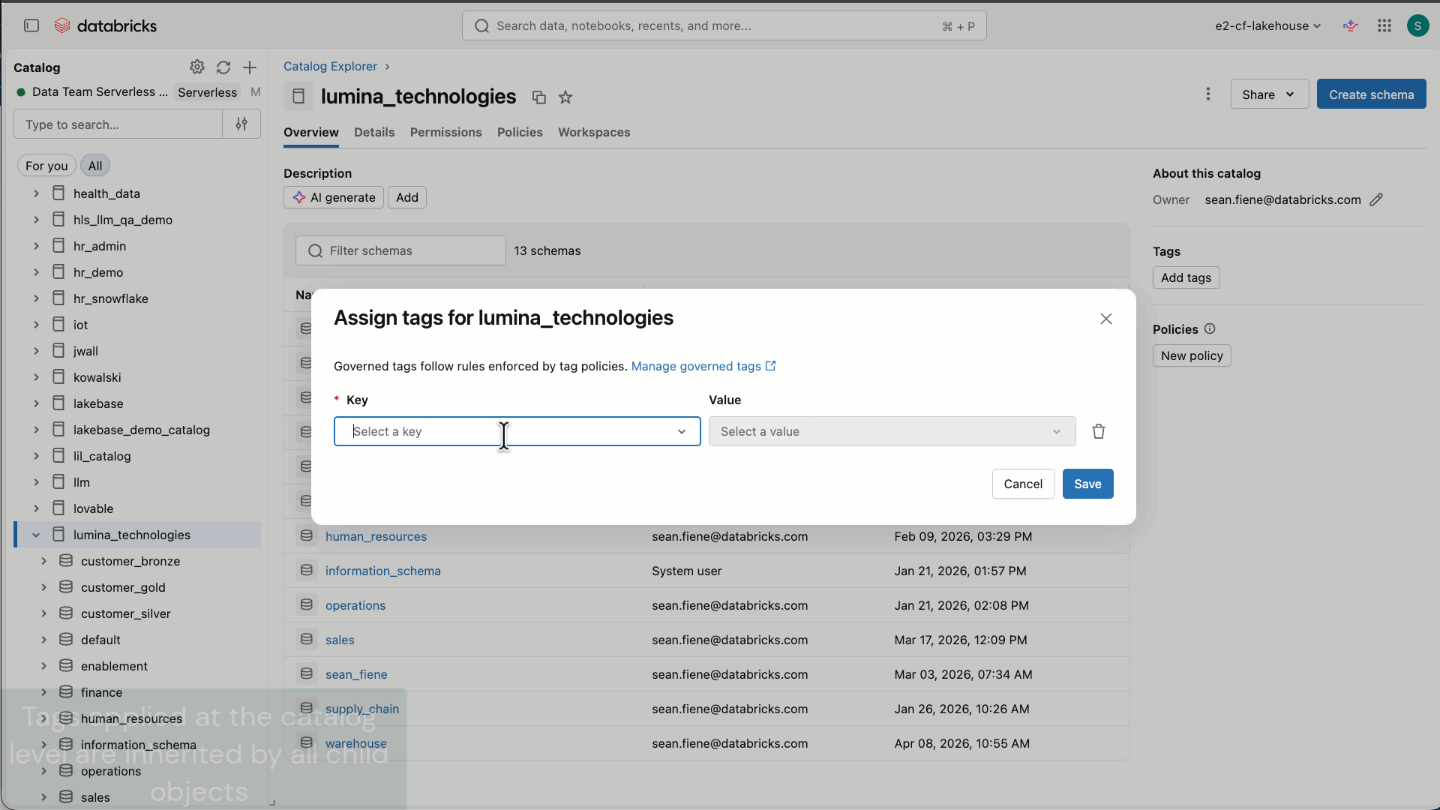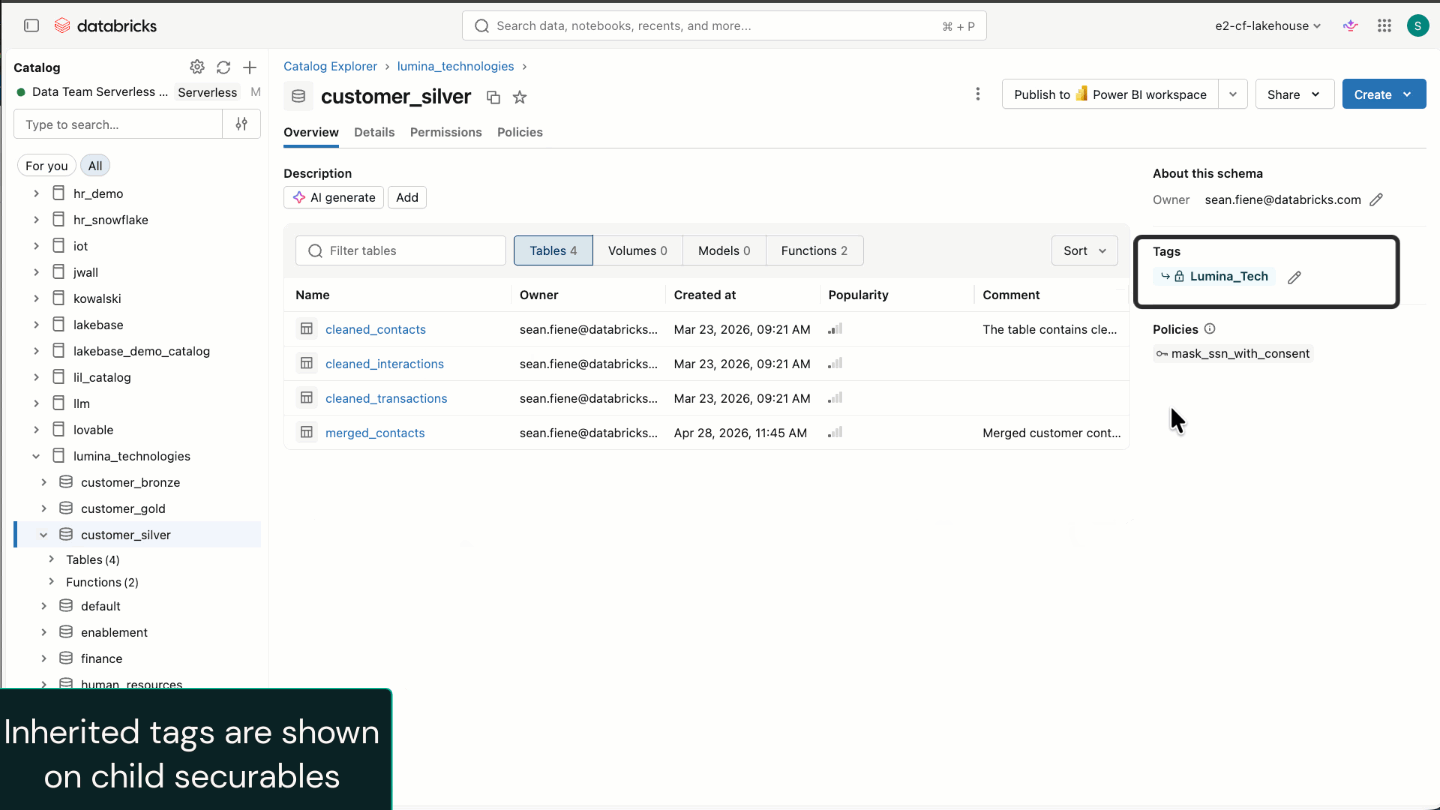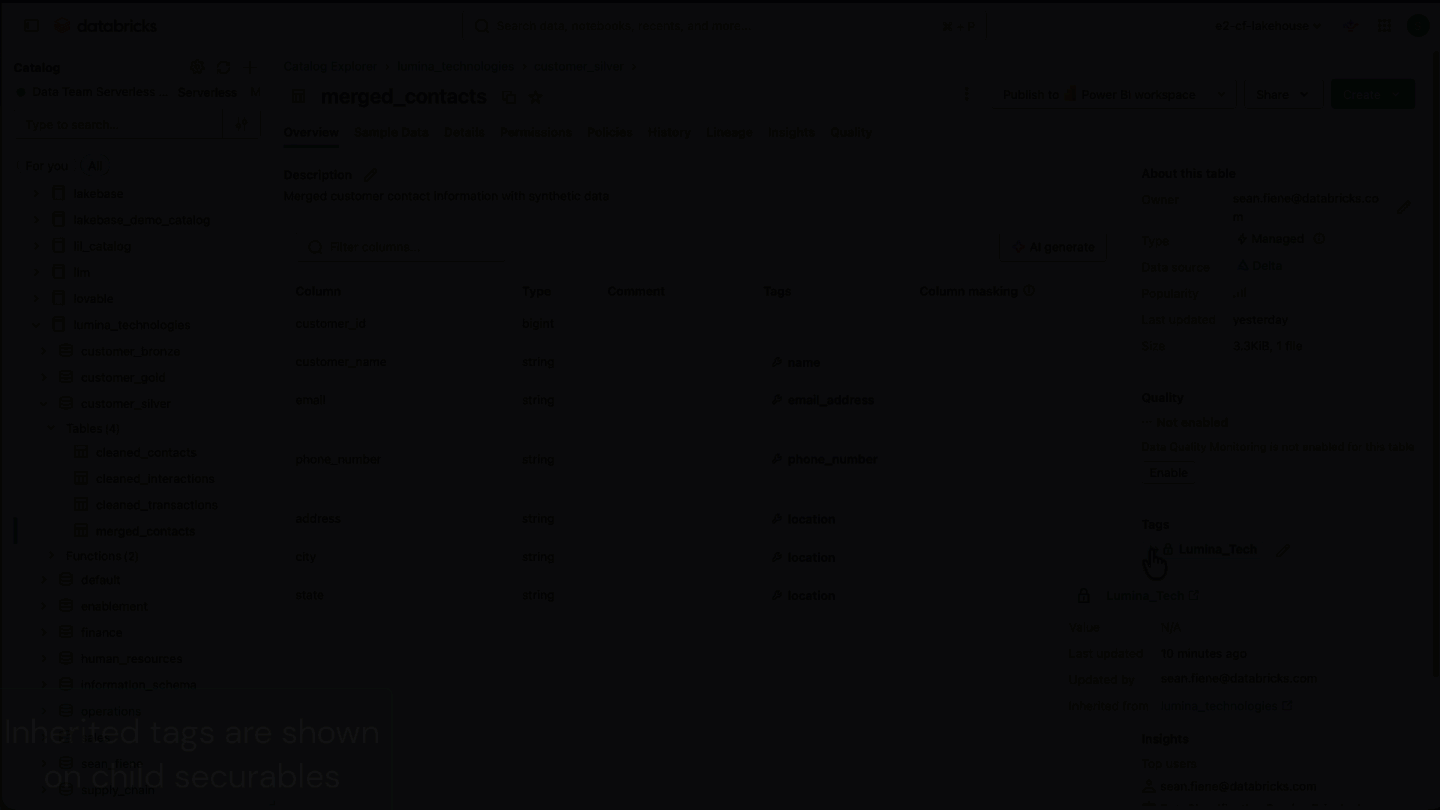
- Governed tags are the attribute foundation that ABAC policies build on: an account-level vocabulary of keys and values that standardizes how data is described across an account, with permissions that control who can apply which tags to which objects. Tags are key or key-value pairs (like sensitivity:confidential or pii:ssn) that attach to catalogs, schemas, tables, and columns, and inherit from parent to child objects.
- Agentic data classification automatically identifies sensitive data (PII, PHI, etc.) for governance and compliance. Built-in classifiers cover standards such as GDPR and HIPAA, while custom classifiers extend detection to business-specific patterns learned from already-tagged columns. Using proven pattern recognition, metadata, and large language models, it delivers higher accuracy than manual or regex-only tools. New data is automatically scanned to ensure any sensitive data introduced is caught. Combined with ABAC policies protecting data with matching tags, these capabilities ensure automatic and scalable protection of sensitive data.
Together, these three capabilities enable a governance model that supports separation of duties. Governance shouldn't rely on a single person or a single role. Instead, responsibilities can be distributed across specialized groups that are experts in their area and don't have to depend on others to do their work. Unity Catalog supports this with the appropriate permissions and boundaries across all three capabilities, so each group can only perform the actions it is responsible for.
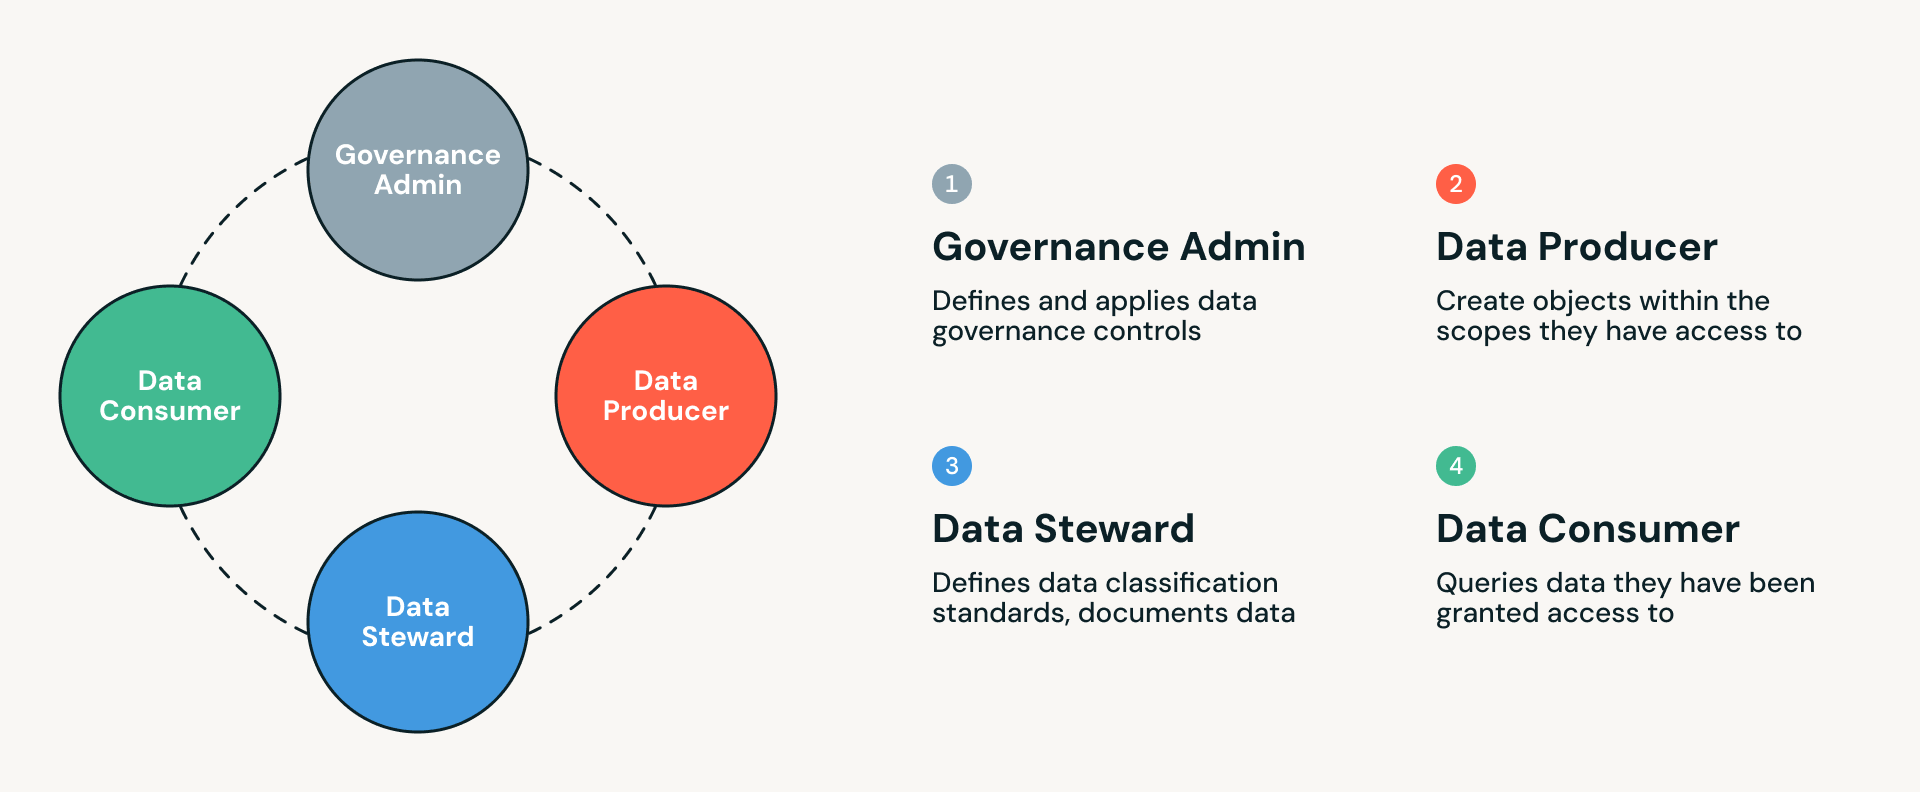
Separation of duties in practice
The three capabilities are designed to work together. Because the policies, tag taxonomy, permissions, and classification all operate within Unity Catalog, there is no handoff between systems, and no manual step between discovery and protection.
In practice, the workflow looks like this:
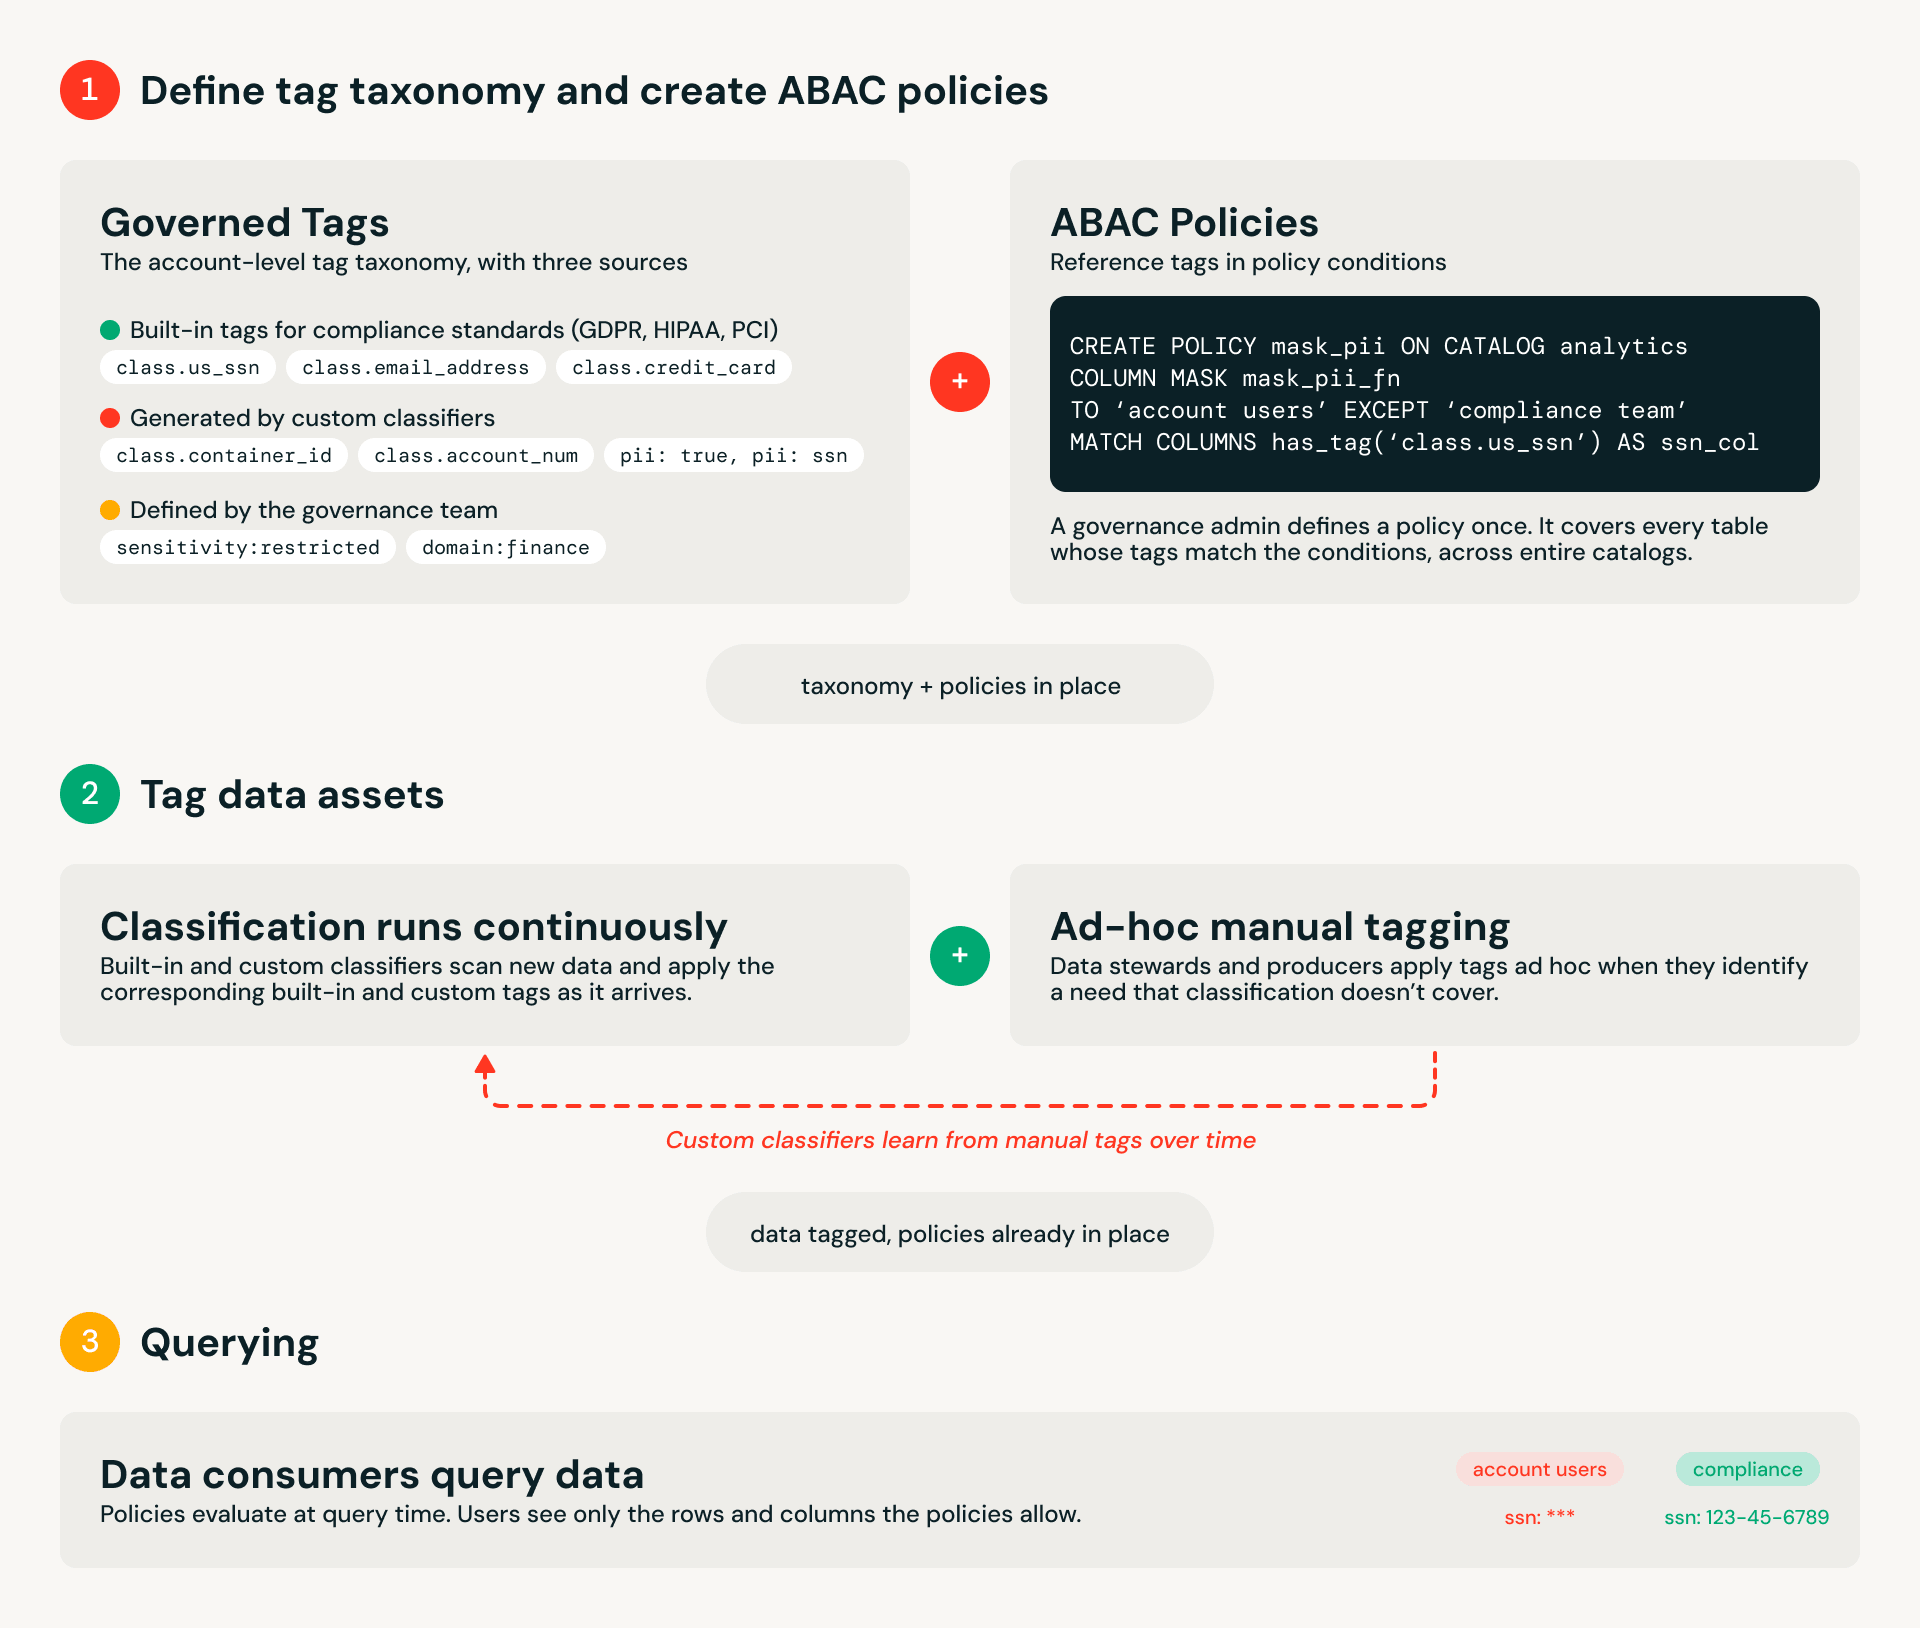
- Define the taxonomy: Governance teams establish the governed tag taxonomy, combining built-in classifiers (aligned to standards like GDPR, HIPAA, PCI), custom classifiers for repeatable patterns, and metadata tags for business context like domains or sensitivity tiers.
- Create ABAC policies: Governance admins define policies that reference these tags to control access based on data attributes.
- Automatically classify and protect data: Classification runs continuously, tagging new data as it arrives. Stewards can apply tags as needed which the system learns from over time, reducing manual effort. As a result, newly tagged data is protected immediately.
- Enable governed data access: Data producers create tables within governed scopes, and data consumers query results, seeing only the rows and columns they’re permitted to access.
“At Atlassian, governing data access and compliance across thousands of users and datasets was becoming increasingly complex with traditional role-based models. ABAC in Unity Catalog has allowed us to define fine-grained access policies based on data attributes, significantly reducing the operational overhead of managing permissions at scale. What used to require extensive manual permission management now happens dynamically, letting our teams focus on delivering insights rather than managing access.” — Gerald Nakhle, Software Engineer, Atlassian
What’s new: General Availability for ABAC policies, governed tags, and data classification
All three capabilities are now generally available, with improvements that address the most common customer feedback.
ABAC policies GA: attribute-based access control across the data estate
At GA, ABAC scales to the largest enterprise data estates and adds enhancements to policy evaluation and authoring. GA highlights include:
- Built for enterprise-scale deployments. Policy limits grew 10x across every scope, with support for 10,000+ policies per metastore and 100+ per catalog and schema.
- Session identity evaluation for views and functions. ABAC policies now evaluate against the identity of the user running the query. Users see exactly what their own permissions allow them to see, even when they query through a view or function.
- One masking function for many column types. A single UDF that accepts and returns VARIANT can mask INT, DOUBLE, DECIMAL, and other numeric types at once, and the same approach extends to STRUCT columns. This cuts down on the number of policies organizations need to maintain.
"Fewer policies, lower costs, surgical precision. ABAC transformed Udemy's data governance from brute-force to elegance." — Rajit Saha | Director, Data & AI Platform, Udemy
Governed tags GA: standardize data classification with tags
At GA, governed tags add full lifecycle management across SQL, APIs, and the UI, plus stronger admin controls and clearer visibility. GA highlights include:
- Full lifecycle management with SQL, APIS, and UI. Admins can create, modify, and inspect tags using SQL (CREATE, ALTER, DROP, SHOW, DESCRIBE GOVERNED TAG) as well as the UI, REST API, and Terraform. This enables easy automation and integration into existing workflows.
- Workspace admin controls. Workspace admins receive CREATE by default (configurable) while account admins receive MANAGE and CREATE, allowing flexible control over tag governance.
- Improved visibility into tag coverage and inheritance: UI and APIs provide clearer insight into how tags are applied and inherited, helping teams track coverage, trace classification decisions, and audit changes.
Agentic data classification GA: Automatically detect and tag data at scale
At GA, classification expands compliance coverage, adds accuracy controls, and unlocks custom classifiers for business-specific patterns. In addition to its current capabilities, GA highlights include:
- Complete visibility of sensitive data in one place: View all classifications detected across a workspace and drill down into where they were found, who has access, and where ABAC policies need to be created for protection.
- Human-in-the-loop validation that continuously improves detection accuracy. Customer feedback and quality evaluations have further improved detection accuracy. Additionally, users can exclude any false positive detections from being tagged, which continuously improves precision of future scans.
- Expanded compliance coverage. New classifiers cover GDPR, HIPAA, GLBA, DPDPA, and PCI, alongside regional support across the UK, Germany, Australia, and Brazil. Additional classifiers for India and Canada will be coming this month. The full list can be found here.
- Custom classifiers in Beta. Business-specific categories are now supported. Give Data Classification any Governed Tag and the system will automatically identify matching columns. Detection patterns are learned from existing tagged columns and surrounding Unity Catalog metadata, automatically fitting to your data.
“As our company grows, manual approaches to data identification and protection become increasingly difficult to sustain. Databricks' agentic Data Classification replaces manual overhead with automated, high-quality results that scale cost more with value. Data Classification can help provide continuous visibility into where key data lives across our environments. Custom classifiers can adapt to our specific data patterns, helping streamline access and compliance management. Attribute-based access control (ABAC) policies can equip us to scale compliance efforts through classification with reduced manual overhead.” — Nan Wu, Software Engineer, Superhuman

Getting started with ABAC, governed tags, and data classification in Unity Catalog
ABAC policies, governed tags, and data classification are available today in Unity Catalog.
These three capabilities represent the foundation of scalable data governance in Unity Catalog. As your data estate grows, the organize-detect-protect pipeline grows with it.
Learn more at Data and AI Summit
Join us in San Francisco, June 15–18, 2026, to see how Data + AI Summit is shaping the future of attribute-based access control and data governance.



