








The U.S. Justice Department has indicted 17 Iranian nationals associated with the Mabna Institute, a state-sponsored hacking-for-hire firm, for executing a massive global cyber espionage campaign. Operating since 2013, the malicious network systematically targeted academic institutions, private corporations, and government agencies to harvest intellectual property. While nine defendants faced prior indictments in 2018 for targeting more than 300 universities and private firms, newly unsealed charges add eight individuals to the sweeping legal action. Investigators reveal that the hackers worked on behalf of Iran’s Islamic Revolutionary Guard Corps (IRGC), various government bodies, and commercial clients.
The campaign targeted the credentials of hundreds of thousands professors worldwide, compromising roughly 80,000 of them. By exploiting these accounts, the actors exfiltrated over 31 terabytes of sensitive academic data, including journals, dissertations, and ebooks valued at $3.4 billion. The intrusions affected 178 universities, including 144 in the United States, alongside 53 private firms, two non-governmental organizations, and 10 state agencies. Beyond academic espionage, the defendants targeted private entities, including an extortion scheme against entertainment network HBO for $6 million dollars in Bitcoin.
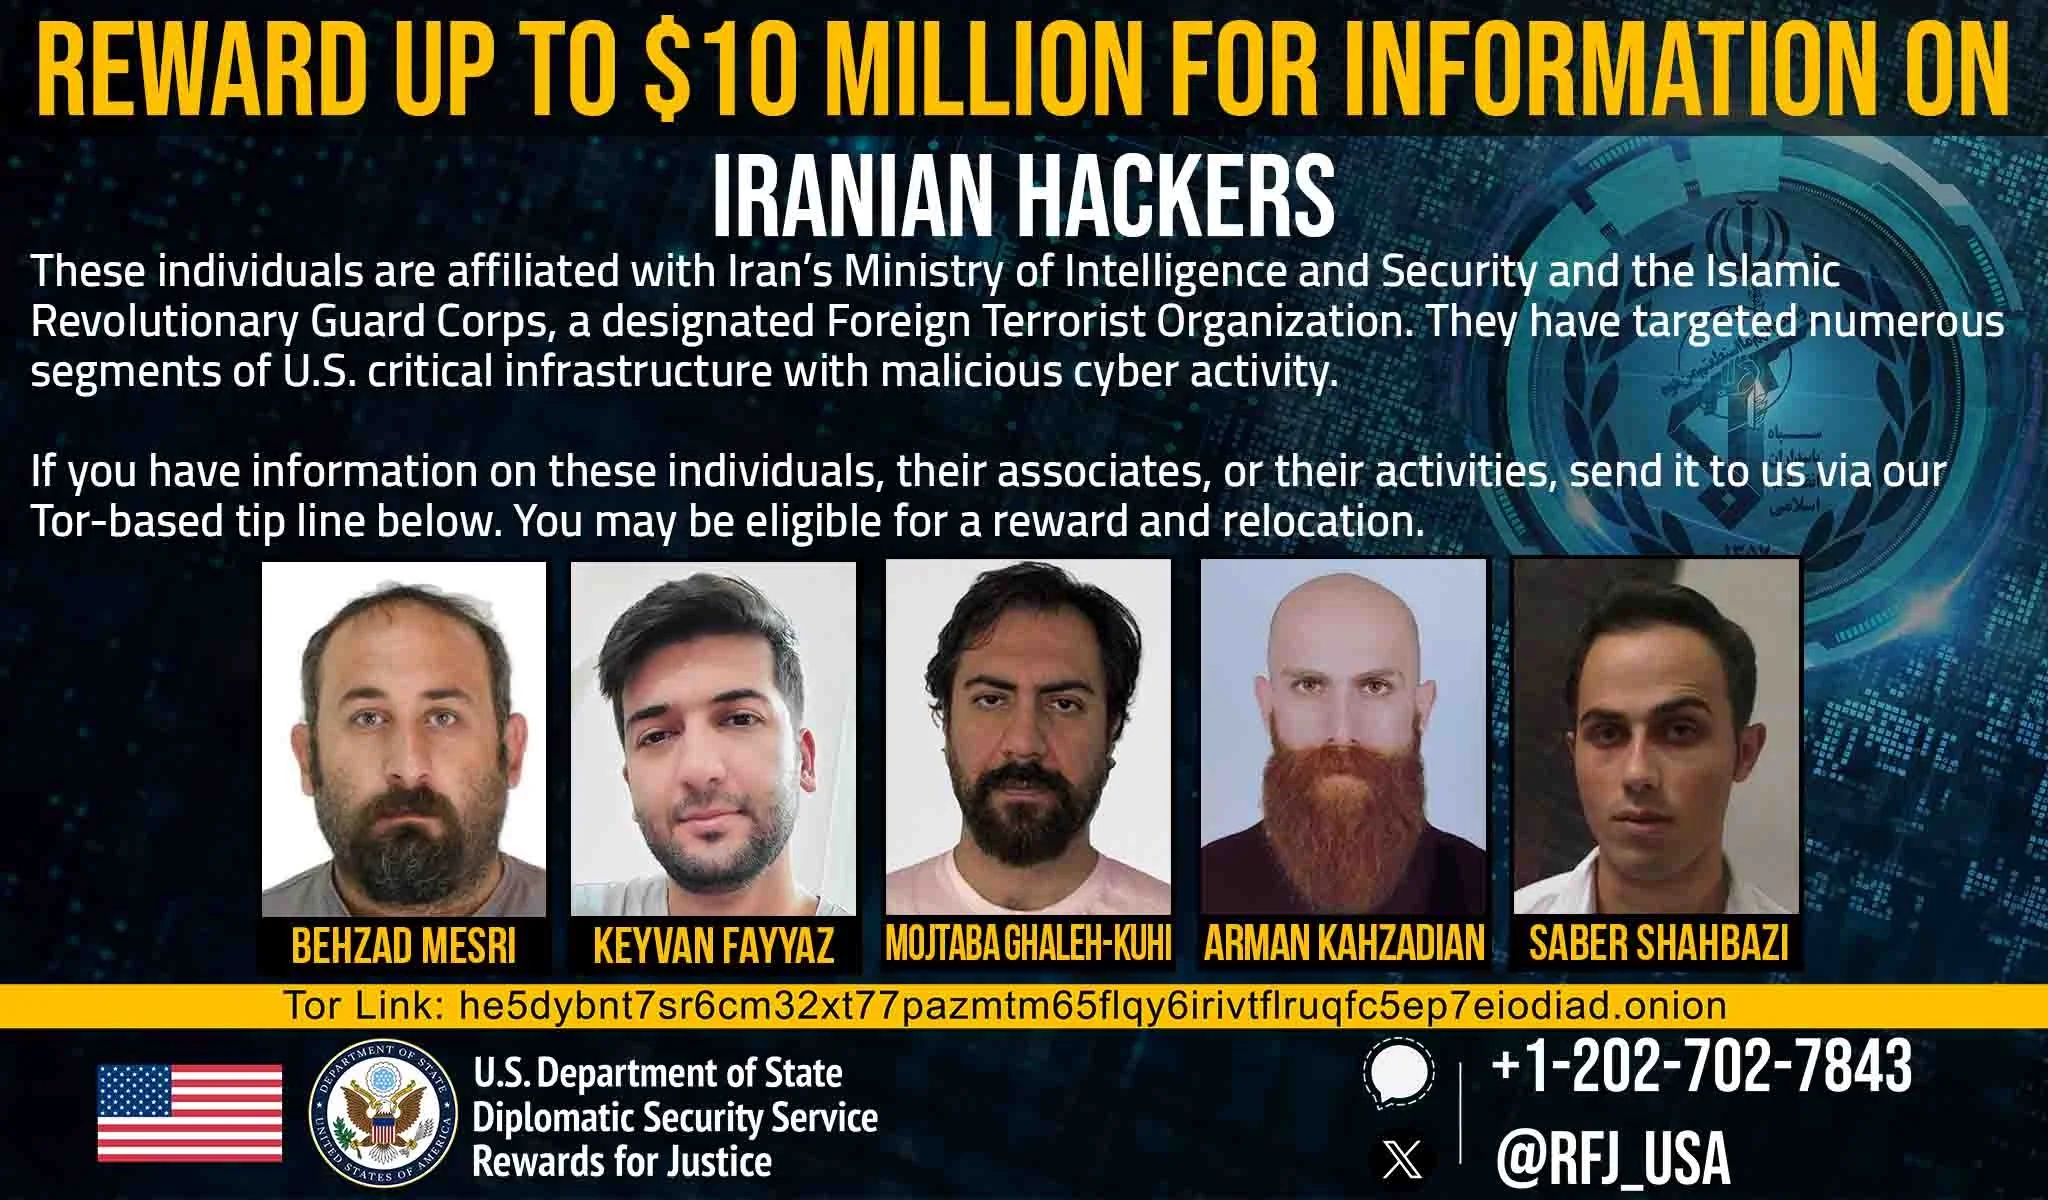
The State Department announced rewards of up to $10 million for information leading to the apprehension of five key defendants and established an anonymous Tor network link to receive tips. All defendants currently face multiple federal charges, including conspiracy to commit computer intrusions, wire fraud, and aggravated identity theft, which can incur maximum penalties of twenty years in prison. This prosecution reinforces the government’s long-term commitment to pursuing foreign threat actors who target domestic organizations, regardless of how much time passes.
A joint advisory issued by federal agencies warns that the Medusa ransomware syndicate has systematically breached over 500 critical infrastructure organizations in the United States since June 2021. Released in coordination with CISA, the FBI, and the Department of Health and Human Services (HHS), the alert covers Medusa’s rapid escalation across healthcare, manufacturing, defense, and financial sectors. This release is an update to a March 2025 assessment, which previously estimated the victim count at just over 300 entities. Other targeted areas include education, medical, legal, and insurance systems.
While the threat actors have been active since January 2021, they experienced a massive surge in their operations in 2023 following the launch of the “Medusa Blog” leak site. Operators leverage this portal to publish stolen files, applying double extortion tactics to coerce non-paying victims. Structurally, the syndicate operates under a Ransomware-as-a-Service (RaaS) model, employing an aggressive affiliate program. Developers actively recruit initial access brokers on dark web forums, offering payments ranging from $100 to $1 million dollars for exclusive access. Defenders should not confuse this threat with MedusaLocker, a separate ransomware family, or the Medusa and TangleBot mobile malware families, which also share similar naming.
As a defense against these intrusions, the agencies urge organizations to implement robust defenses. Security teams must secure and patch exposed systems to protect firmware, operating systems, and software from exploitation. Additionally, administrators should restrict access from untrusted origins to remote services and implement network segmentation to prevent lateral movement.
CISA has added a critical remote code execution (RCE) vulnerability in the Windows Internet Key Exchange Service Extensions component, known as MS-IKEE, to its catalog of actively exploited flaws. Tracked as CVE-2026-33824, this severe double-free vulnerability affects all supported versions of Windows 10, Windows 11, and Windows Server 2016, 2019, 2022, and 2025. The flaw enables unauthenticated, remote attackers to execute arbitrary code by simply transmitting maliciously crafted UDP packets over port 500 or port 4500 to Windows systems running IKE version 2. Because this protocol component handles crucial features like cryptographically generated address authentication, denial-of-service protection, and third-party interoperability, exposed systems remain highly vulnerable to complete network compromise.
Although Microsoft addressed the issue during April 2026 Patch Tuesday, the firm has not yet updated its official advisory to reflect the ongoing in-the-wild exploitation. Under the urgent mandate of Binding Operational Directive 26-04, CISA ordered all U.S. Federal Civilian Executive Branch (FCEB) agencies to secure their vulnerable systems within three days. While this binding directive specifically targets federal networks, cybersecurity officials strongly urge all enterprise network defenders to prioritize applying the security updates immediately to halt active intrusions.
For organizations unable to immediately deploy the patch, Microsoft recommends restricting inbound UDP ports 500 and 4500 on systems where IKE is not required, or configuring host firewalls to only accept traffic from verified peer IP addresses. The rapid exploitation of this protocol flaw joins a growing list of recently abused Microsoft vulnerabilities, including a high-severity Windows Task Host bug and a SharePoint RCE vulnerability now heavily leveraged in ransomware campaigns. Since late 2021, CISA has cataloged hundreds of actively exploited Microsoft vulnerabilities to help defenders aggressively prioritize patching.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。