







Threat hunting is meant to uncover malicious activity before it becomes an incident. In reality, it can easily turn into a long expedition through noisy logs, vague indicators, and detection rules that lack the context needed to separate real risk from routine activity.
The issue is rarely the analyst’s skill. The real bottleneck is intelligence quality. A standalone IP address, domain, or hash may be useful for blocking, but it does not explain the campaign behind it, the behaviors it leaves on endpoints, or the infrastructure likely to appear next.
Effective hunting requires behavioral context: the ability to connect artifacts such as mutexes, file paths, network traffic, processes, and detection tags into a fuller picture of an attack. It also requires validating hypotheses and rules against real-world malicious activity, not only abstract technique descriptions.
Below are the practical examples of how this approach works.
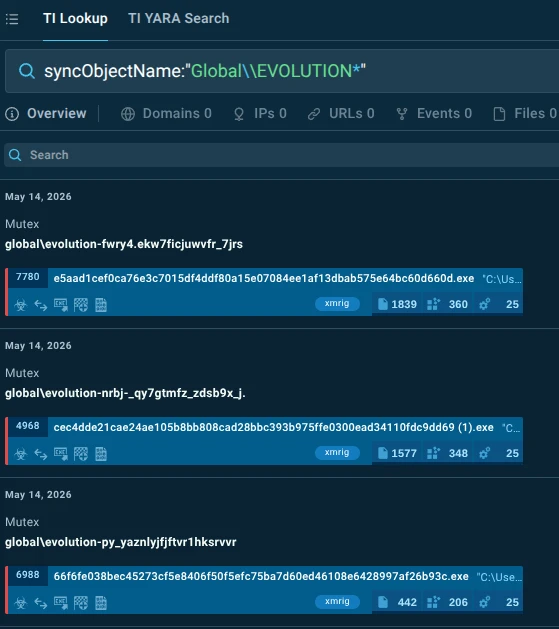
An analyst investigates a suspicious executable identified as a stealer and notices a mutex beginning with Global\EVOLUTION, followed by a randomized suffix.
A full mutex value is not a durable indicator. Searching for it would miss variants using different random endings, while traditional feeds may not include the artifact at all. But the stable prefix may reveal a family-level behavior.
Using a wildcard search in ANY.RUN’s Threat Intelligence Lookup, the analyst searches for mutexes matching Global\EVOLUTION*. The results reveal multiple samples with the same hardcoded prefix and different suffixes, confirming that the pattern is associated with a broader malware family rather than a one-off sample.
syncObjectName:”Global\\EVOLUTION*”
The analyst then pivots to other artifacts found in these executions. The samples consistently create archives following a pattern such as: C:\Users\admin\AppData\Local\Temp\evo_\stolen.zip.
This is a second independent behavioral indicator that definitely looks like a stealer. Now, instead of relying on one fragile IOC, the team has a behavioral profile that combines mutex creation and archive generation.
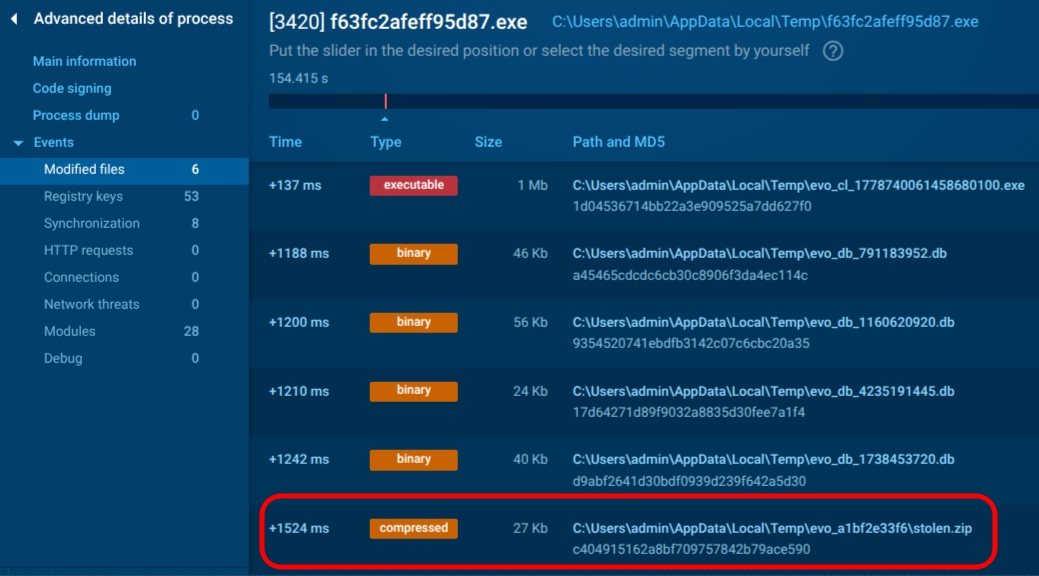
Combining both indicators with OR/AND logic lets the hunter tune for either maximum reach or high-confidence, low-noise detection, building a multi-indicator profile from a single mutex, without relying on indicators that break the moment the malware updates.
Impact: one behavioral artifact expands into full campaign coverage, with detection logic validated before it ever touches production.
Threat Intelligence Lookup helps security teams investigate faster, connect weak signals, and reduce attacker dwell time.
View more threat hunting cases.
Threat hunting rules need broad coverage, but broad coverage can also catch benign activity.
Consider a rule that detects Windows hostnames transmitted in network traffic. This behavior is common among stealers and remote-access trojans, which often send hostnames as victim identifiers. It is also possible for legitimate software to transmit device information.
suricataMessage:”HUNTING Windows PC hostname observed”
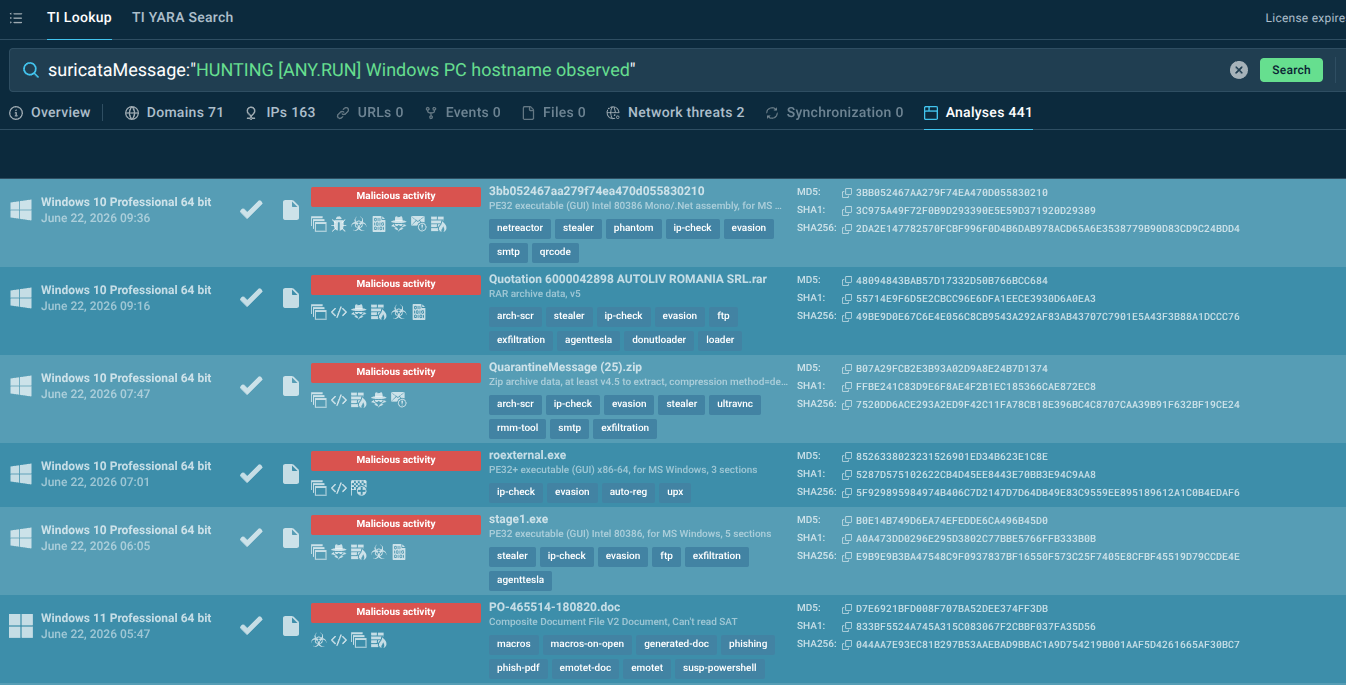
Before deploying the rule, an analyst reviews matching sandbox sessions. One alert appears to involve Outlook.exe, which initially looks suspicious. However, closer inspection shows that the destination is a legitimate Microsoft licensing endpoint. Legitimate Microsoft domain in threat detection
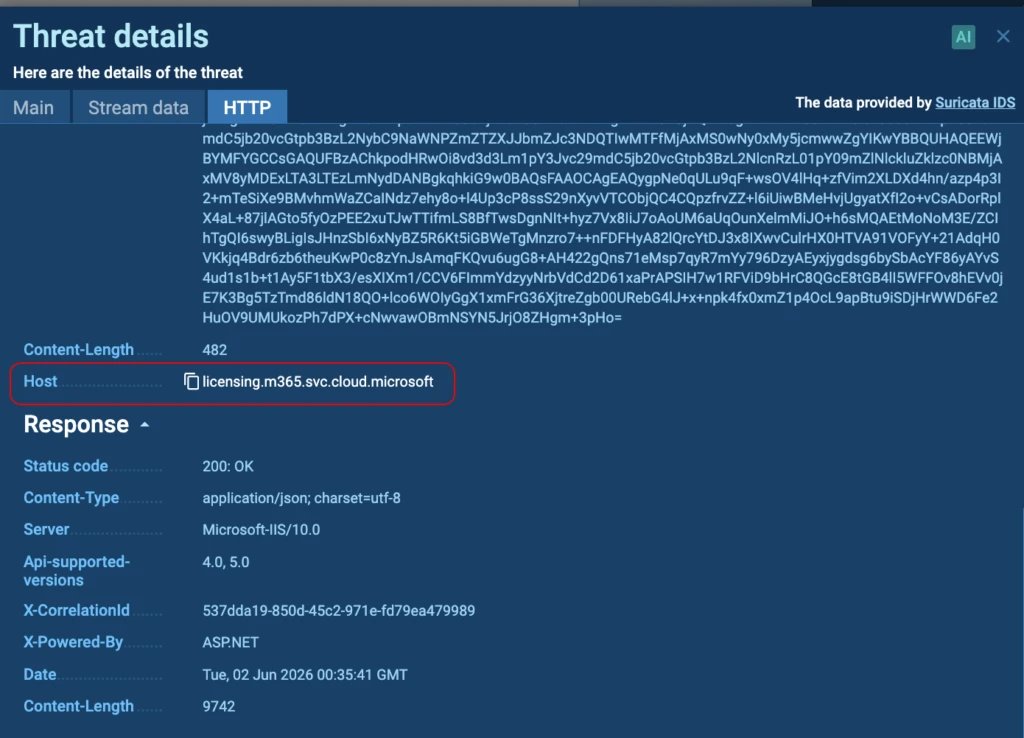
The HTTP traffic confirms that Outlook is sending device and license metadata as part of a normal Office license renewal process. There is no malicious payload, no suspicious infrastructure, and no evidence of data theft.
Rather than disabling the rule, the analyst documents the behavior as a known false positive and adds an exclusion for legitimate Microsoft licensing traffic.
This is the difference between tuning and weakening detection. The rule retains its ability to catch real hostname exfiltration while avoiding a predictable source of analyst fatigue. Over time, this process helps teams build a detection pipeline that surfaces meaningful threats instead of manufacturing queue noise.
Impact: false positives get caught and documented before reaching production, and analyst attention stays on genuinely malicious activity.
Interactive investigation is essential, but hunting also needs to scale.
ANY.RUN’s Threat Intelligence Feeds continuously deliver fresh indicators and contextual data into SIEM, EDR, XDR, SOAR, firewalls, and other security tools. This helps teams prioritize alerts involving known malicious infrastructure, correlate internal telemetry with active campaigns, automate enrichment, and reduce the manual work of collecting and maintaining IOCs.
The Interactive Sandbox adds the behavioral layer. Analysts can safely observe suspicious files, URLs, and emails in execution, then review processes, network connections, dropped files, mutexes, command lines, and other artifacts. Tier 1 Reports, AI summaries, and investigation recommendations help analysts understand the most relevant evidence faster and identify useful pivots for deeper hunting.
Together, TI Feeds keep defenses current while sandbox intelligence explains what the indicators actually mean. One supplies the stream; the other supplies the map.
Give your SOC team the context to validate suspicious activity quickly, cut false-positive effort, and focus scarce expertise on threats that can affect the business.
Threat hunting matters because attackers do not always trigger an alert. They abuse legitimate tools, rotate infrastructure, and hide within normal-looking activity. If teams rely only on automated detection, some threats will remain invisible until they cause measurable damage.
Intelligence-driven hunting helps organizations find those threats earlier, reduce dwell time, and improve the quality of detection engineering. It also makes better use of scarce analyst time by reducing manual research and false-positive investigations.
For the business, that means lower incident response costs, stronger resilience, and a security operation that can focus on genuine risk rather than endless log archaeology.
With fresh threat intelligence, behavioral evidence, and tools for rapid validation, threat hunting becomes less of a guessing game and more of a repeatable process for reducing exposure.
(Photo by Moritz Erken on Unsplash)
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。