


A deceptive trojan is outsmarting Android’s built-in defences to bombard users with unstoppable background advertisements. Security analysts at Doctor Web recently found Android.MagicAd.1, a trojan malware that manipulates legitimate phone systems to force-feed ads even when all app windows are closed.
This is a frustrating trick, proving that ad-delivering threats are no longer just a minor nuisance but highly engineered tools designed to break safety rules.
Android.MagicAd.1 first appeared in 2025, but researchers say it is now being pushed through more than 50 infected games and utility apps. The malicious apps were not limited to shady download sites either. They were distributed through official app stores, including Samsung Galaxy Store and Xiaomi’s GetApps catalogue.
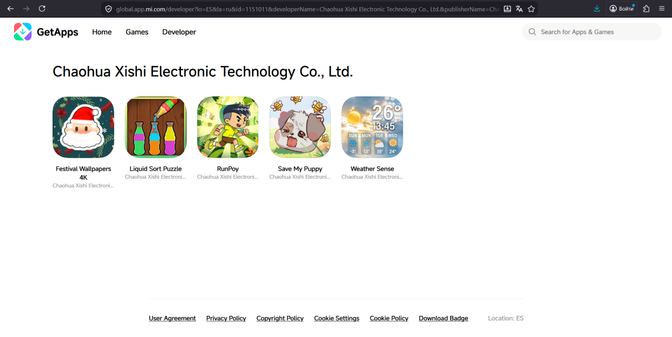
To evade early detection by security scanners, the hackers rotated their apps, keeping them online for less than a month before swapping them with new versions. However, once downloaded, the trojan remained active on user devices.
The attack chain begins with hidden, encrypted components inside native code libraries. When a victim opens a compromised app, the malware decrypts these resources to extract a core component called Android.MagicAd.1.origin.
This Android malware also performs environment checks before launching its payload. It scans for virtual machines or blacklisted IP addresses to ensure it’s not being monitored by security researchers. If everything is clear, it hides its app icon from the home screen menu and schedules background tasks to keep itself running permanently.
Researchers explained in the blog post that modern Android operating systems strictly forbid background apps from launching themselves or displaying windows over other programs without explicit permissions. Android.MagicAd.1, however, can bypass this barrier simply by targeting trusted, pre-installed system applications. The way it does this depends heavily on the phone’s manufacturer.
On Xiaomi and Amazon devices, the malware sends a delayed system command called a “pending intent” to its internal component, Android.MagicAd.1.origin. It routes this command through standard system apps like Mi Browser, Miui SystemUI, or the Amazon Fire TV Home Screen launcher to wake itself up and draw transparent ad banners right over active screens.
For Vivo devices, the hackers exploit an internal communications system called Android Binder instead, sending data packages through standard tools like iManager, Phonebook, or Vivo Browser to trigger the background ads.
On other brands, the trojan program uses a clever, universal fallback. It saves a silent audio file, opens the system media player at zero volume, and simulates a physical button click using a background command. This trick fools the operating system into giving the trojan immediate priority to display its ads.
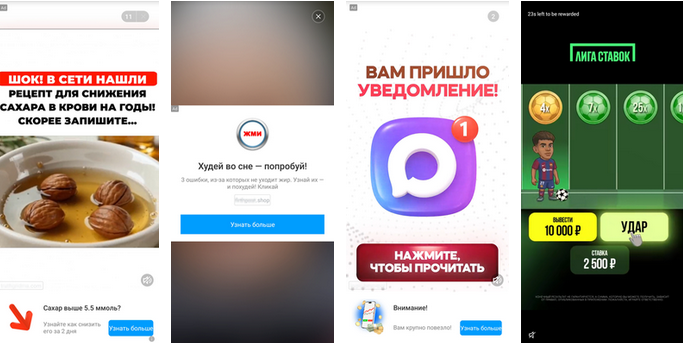
Doctor Web confirms that all identified malicious apps have now been removed from official stores. While the immediate distribution loop has been broken, this campaign shows how easily threat actors can weaponize the very software meant to protect us.
(Image by iXimus from Pixabay)
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。