


A massive wave of cyberattacks has hit more than 100 organisations globally, and universities are the main targets. Security researchers at Mandiant and the Google Threat Intelligence Group (GTIG) were notified about the threat through public reports. Further probing revealed that 68% of the victims were colleges and universities. And, most of these are based in the US.
The cybercrime group behind this wave is UNC6240 or ShinyHunters. The group’s targets were organisations using the Oracle PeopleSoft software. For your information, this software handles institutional business operations.
Reportedly, the activity occurred between 27 May and 9 June, and involved the exploitation of a critical zero-day flaw (tracked as CVE-2026-35273 CVSS 9.8) to compromise university networks. Since the group caught this flaw before Oracle released a patch, they proceeded completely unhindered.
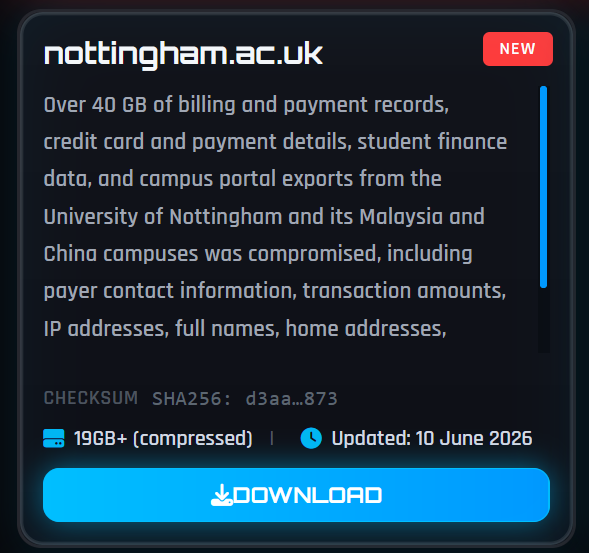
One of the group’s latest victims in the PeopleSoft-linked attack is the University of Nottingham in the United Kingdom, where the personal data of 450,000 students was leaked just a couple of days ago. The leaked data reportedly includes 40 GB of PII and financial information belonging to students and university staff.
CVE-2026-35273 is an unauthenticated remote code execution bug that exists in the Oracle PeopleSoft PeopleTools (mainly versions 8.61 and 8.62) Environment Management Hub (PSEMHUB) component. According to GTIG’s blog post, this bug allowed hackers to bypass authentication entirely or log in as privileged users.
Instead of a direct database exploit, they operated entirely inside PeopleSoft’s application logic, using legitimate APIs to access and extract records. This means standard database security monitors never noticed anything wrong. This tactic is similar to other major supply-chain software compromises we have observed in the past, like the MOVEit breaches.
— Michael R (@nahamike01) June 10, 2026ShinyHunters, (or a group impersonating them) exposed several directories revealing ongoing targeting of PeopleSoft (Enterprise Resource Planning software) environments.
Also visible were staging materials, including MeshCentral agents, and a defacement and credential spray…
Researchers found five staging IP addresses (142.11.200.186 to 142.11.200.190) running Python SimpleHTTP servers on port 8888 that the hackers used to store their malware. This toolkit contained MeshCentral remote-control binaries named meshagent32-azure-ops.exe, meshagent64-azure-ops.exe, and meshagent64-v2.exe.
These files were strategically named after safe Microsoft Azure services to bypass security filters and hide their true goal- opening a backdoor to a C2 server (wss://azurenetfiles.net:443/agent.ashx).
Once inside, the attackers read WebLogic configurations (config.xml) and process scheduler files (psappsrv.cfg) to map out the internal network blueprints. To spread quickly across university networks, they deployed a custom script called (victim_abbreviation)_fanout.sh.
This script fetched a list of internal systems from /etc/hosts and used credential spraying (which involves rapid, automated password guessing) to compromise deeper systems.
To fulfil their main objective of data theft and extortion, the hackers then planted a note named README-IF-YOU-SEE-THIS-YOUVE-BEEN-HACKED.TXT inside internal folders. This was done after full system control to threaten the victims.
The attack’s final step involved compressing the stolen files using the zstd utility tools so that data packages became easier to move and exfiltrating the archives to their public leak site mirror at 176.120.22.24.
Oracle released an out-of-band Security Advisory on 10 June 2026, announcing that fixes will be arriving soon. The company warned users to quickly apply remediation measures, meanwhile:
“We consider implementation of the recommended mitigations to be a high-priority risk reduction measure and strongly recommend immediate action to address the identified exposure.”
To stop the attacks, security teams need to isolate the /PSEMHUB/* and /PSIGW/HttpListeningConnector network points right away. They should also watch out for Server-Side Request Forgery (SSRF) in their access logs and block unusual port 445 SMB traffic leaving their systems.
“The Oracle PeopleSoft breach is an example of the new kind of attacks every ERP will face in today’s new agentic world. Companies need to reassess their ERP security and controls and adapt, because they are exposed,” said James Davison, Chief Strategy Officer at Pathlock, an identity and access security provider.
This attack shows that traditional perimeter security and IdP-level authentication are necessary, but not sufficient. Modern ERP security requires a layered approach that combines preventive controls, continuous monitoring, and visibility into user activity. The visibility into user activity is key here; behavioral monitoring to spot exceptions isn’t a nice-to-have anymore,” James explained.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。