




Two young hackers, reportedly the members of the Scattered Spider hacking group, pleaded guilty under the Computer Misuse Act for their involvement in a £39 million cyberattack on Transport for London (TfL). Specifically, they admitted to conspiring to commit unauthorised acts against TfL’s computer systems, a charge carrying a severe warning that the attack created a serious risk of damage to human welfare.
The hackers, Thalha Jubair, 20, and Owen Flowers, 18, were to stand trial at Woolwich Crown Court on 22 June, but they changed their pleas to guilty on the very first day of their trial.
“The profile of offenders like Flowers and Jubair demonstrates the increasing threat from cyber criminals based in the UK and other English-speaking countries, epitomised by Scattered Spider,” NCA’s deputy director and NCA’s National Cyber Crime Unit, Paul Foster, stated in an official press release.
Jubair and Flowers are accused of a cyberattack on TFL between 31 August and 3 September 2024 that completely shook the capital’s transport network, causing a 3-month-long service disruption, even forcing all 28,000 TfL staff members to physically walk into an office just to reset their computer passwords.
The attack hit everyday passengers harder because the hackers also targeted the Oyster card refund system. This forced people to wait much longer to get their money back. Also, the hackers completely shut down the online application system for children’s discount Oyster cards. The British Transport Police and West Midlands officers collaborated to arrest the hackers after a “lengthy, highly complex and painstaking investigation,” the NCA’s official statement read.
As per Hackread.com’s past coverage of the incident in September 2024, while core train and bus services remained running, the hackers did access the personal details, names, and bank information of 10 million customers.
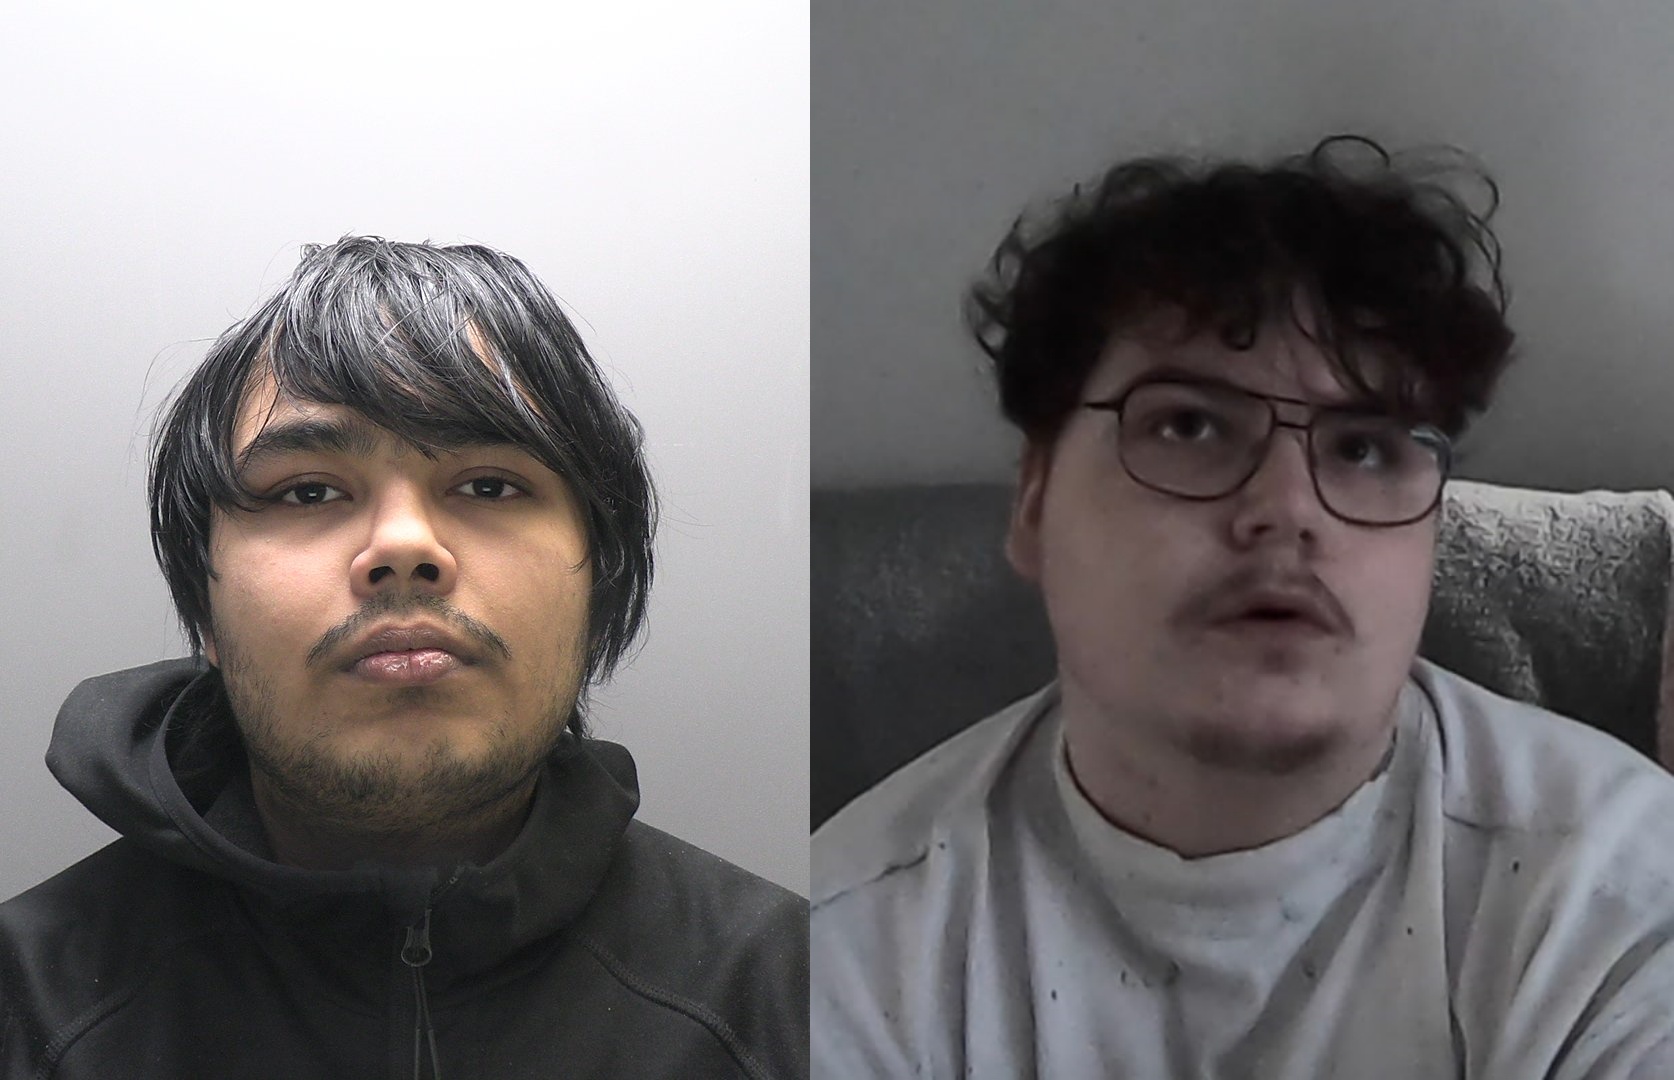
The National Crime Agency (NCA) and City of London Police raided the hackers’ homes on 16 September 2024, seizing tower computers, laptops, USB sticks, and hard drives containing crucial evidence linking the duo to the attack.
One laptop had video clips of Jubair actually using TfL systems while the two discussed the attack on Telegram and a shared online workspace. Flowers also looked at data, selling stolen login details online, and broke his bail rules twice in 2025. He even targeted US hospitals, breaking into networks belonging to SSM Health Care and Sutter Health.
This case highlights the consistent, disturbing rise in the youth’s involvement in such crimes, as they don’t understand the legal dangers of cyberattacks. NCA earlier reported that one in five UK children between 10 and 16 have broken the law online and engaged in hacking.
“A recent survey of children aged 10-16 showed that 20% engage in behaviours that violate the Computer Misuse Act, which criminalises unauthorised access to computer systems and data. The figure is higher for those who game, standing at 25%,” NCA reported in 2024.
The case against Jubair and Flowers actually shows what happens when authorities catch these young hackers, and it must be taken as an example. Now that they have pleaded guilty, both will remain in custody. They will face the legal consequences together during a two-day sentencing hearing scheduled for 15 and 16 July 2026.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。