







In a collective operation, Group-IB, INTERPOL, and the Algerian National Police have dismantled SniperDZ, an online Phishing-as-a-Service (PhaaS) network that helped hackers steal user data for nearly ten years.
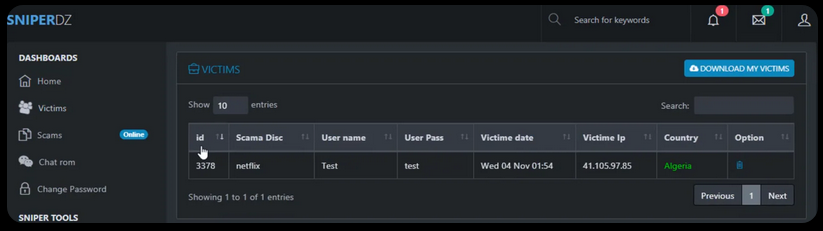
Operating via Telegram and Facebook channels, SniperDz allowed anyone, even novice hackers, to use its toolkit of 80 ready-made phishing templates for free to create fake login pages and trick people into giving away their login credentials (usernames – passwords) and other personal data.
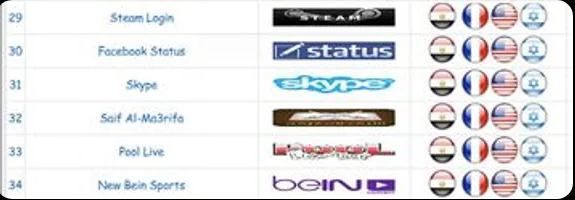
The phishing platform allowed scammers to target users on around 30 popular platforms, including PayPal, Facebook, Instagram, Netflix, and Steam, via more than 20,000 domains.
As per the details shared by INTERPOL and Group-IB, this PhaaS network was launched in 2015 but evaded detection for so long because the admins constantly changed its name. The platform was also known as JokerDz, StormDz, and SpamDz.
In 2024, Group-IB cybersecurity researchers detected fake Facebook accounts of politicians in the Middle East and North Africa delivering malicious links. These accounts lured users into clicking those links by promising free internet access and gifts.
With the support of INTERPOL, slowly, information started emerging; the code’s developer turned out to be a threat actor known online as Guedz. The hacker created a massive vulnerability for himself by producing video tutorials to train affiliate scammers.
In those recordings, Guedz failed to mask his active administrator panel and personal backend email addresses, and Group-IB’s analysts used data correlation to trace him using these clues.
Group-IB compiled and shared this data with INTERPOL and the Algerian National Police. This helped Algerian authorities arrest Guedz and seize active hardware containing phishing code and malicious scripts.
This raid was part of a broader threat mitigation initiative called Operation Ramz that ran between October 2025 and 28 February 2026. INTERPOL shared its results in a press release on 18 May but didn’t explicitly name the SniperDz network at the time. Group-IB is the first to name the network and share more details on this network in a report published today.
“For nearly ten years, SniperDz served as quiet criminal infrastructure, available to anyone with the motivation to use it. The scale of its reach became concrete in 2016, when the platform published statistics showing that campaigns run through its service had already collected more than 45,000 victim records. That figure represented only the activity captured at a single point in time, years before the operation was dismantled,” Group-IB revealed.
According to INTERPOL’s press release, Operation Ramz covered 13 nations, including Egypt, Morocco, Jordan, and Qatar, leading to 201 arrests and the seizure of 53 malicious servers. Over 3,867 compromised endpoints and victims were identified.
During the mitigation process in Jordan, investigators tracked an investment scam platform run by 15 forced workers. These individuals were victims of human trafficking who had their travel documents withheld and were forced to run the scam scripts.
Authorities arrested the two primary operators running that facility. This coordinated shutdown proves that even the most long-standing scam networks eventually fall when international threat intelligence and local law enforcement align.
“In a world where cybercriminals exploit the digital landscape without borders, Operation Ramz demonstrates the effectiveness of global collaboration. INTERPOL is dedicated to working with its member countries and private sector partners to take down malicious infrastructure, disrupt criminal groups, and bring perpetrators to justice,” stated INTERPOL’s Director of Cybercrime, Neal Jetton.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。