












A major software supply chain vulnerability has been discovered across the open-source network that can allow cybercriminals to hijack build pipelines and compromise corporate networks. Cybersecurity research firm Novee discovered this structural flaw, which they named Cordyceps after a body-snatching parasitic fungus, and shared its findings with Hackread.com.
According to the company, Cordyceps is a systemic class of Continuous Integration and Continuous Deployment (CI/CD) vulnerabilities, and the flaw exists within GitHub Actions workflows (specifically in .yml configuration files).
Researchers found that an unauthenticated user wouldn’t even need special organisation privileges to launch an attack because a free, anonymous online account is enough to forge approvals, inject malicious code, or steal permanent credentials.
Standard automated scanners miss this risk because they only look at single files in isolation. In contrast, Cordyceps relies on multi-step exploit chains where untrusted data tricks the system by crossing a security boundary.
In a hypothetical command injection and artifact poisoning attack, an unauthorised user leaves an anonymous comment or submits a malicious code update, called a pull request. A low-privilege workflow treats this input as a trusted command, running hidden code to compromise the final software package or artifact.
From there, privilege escalation occurs when that tainted data flows into a high-privilege workflow and exposes high-level authentication keys. This entire process could allow an external threat actor to gain full administrative permissions over a company’s cloud network.
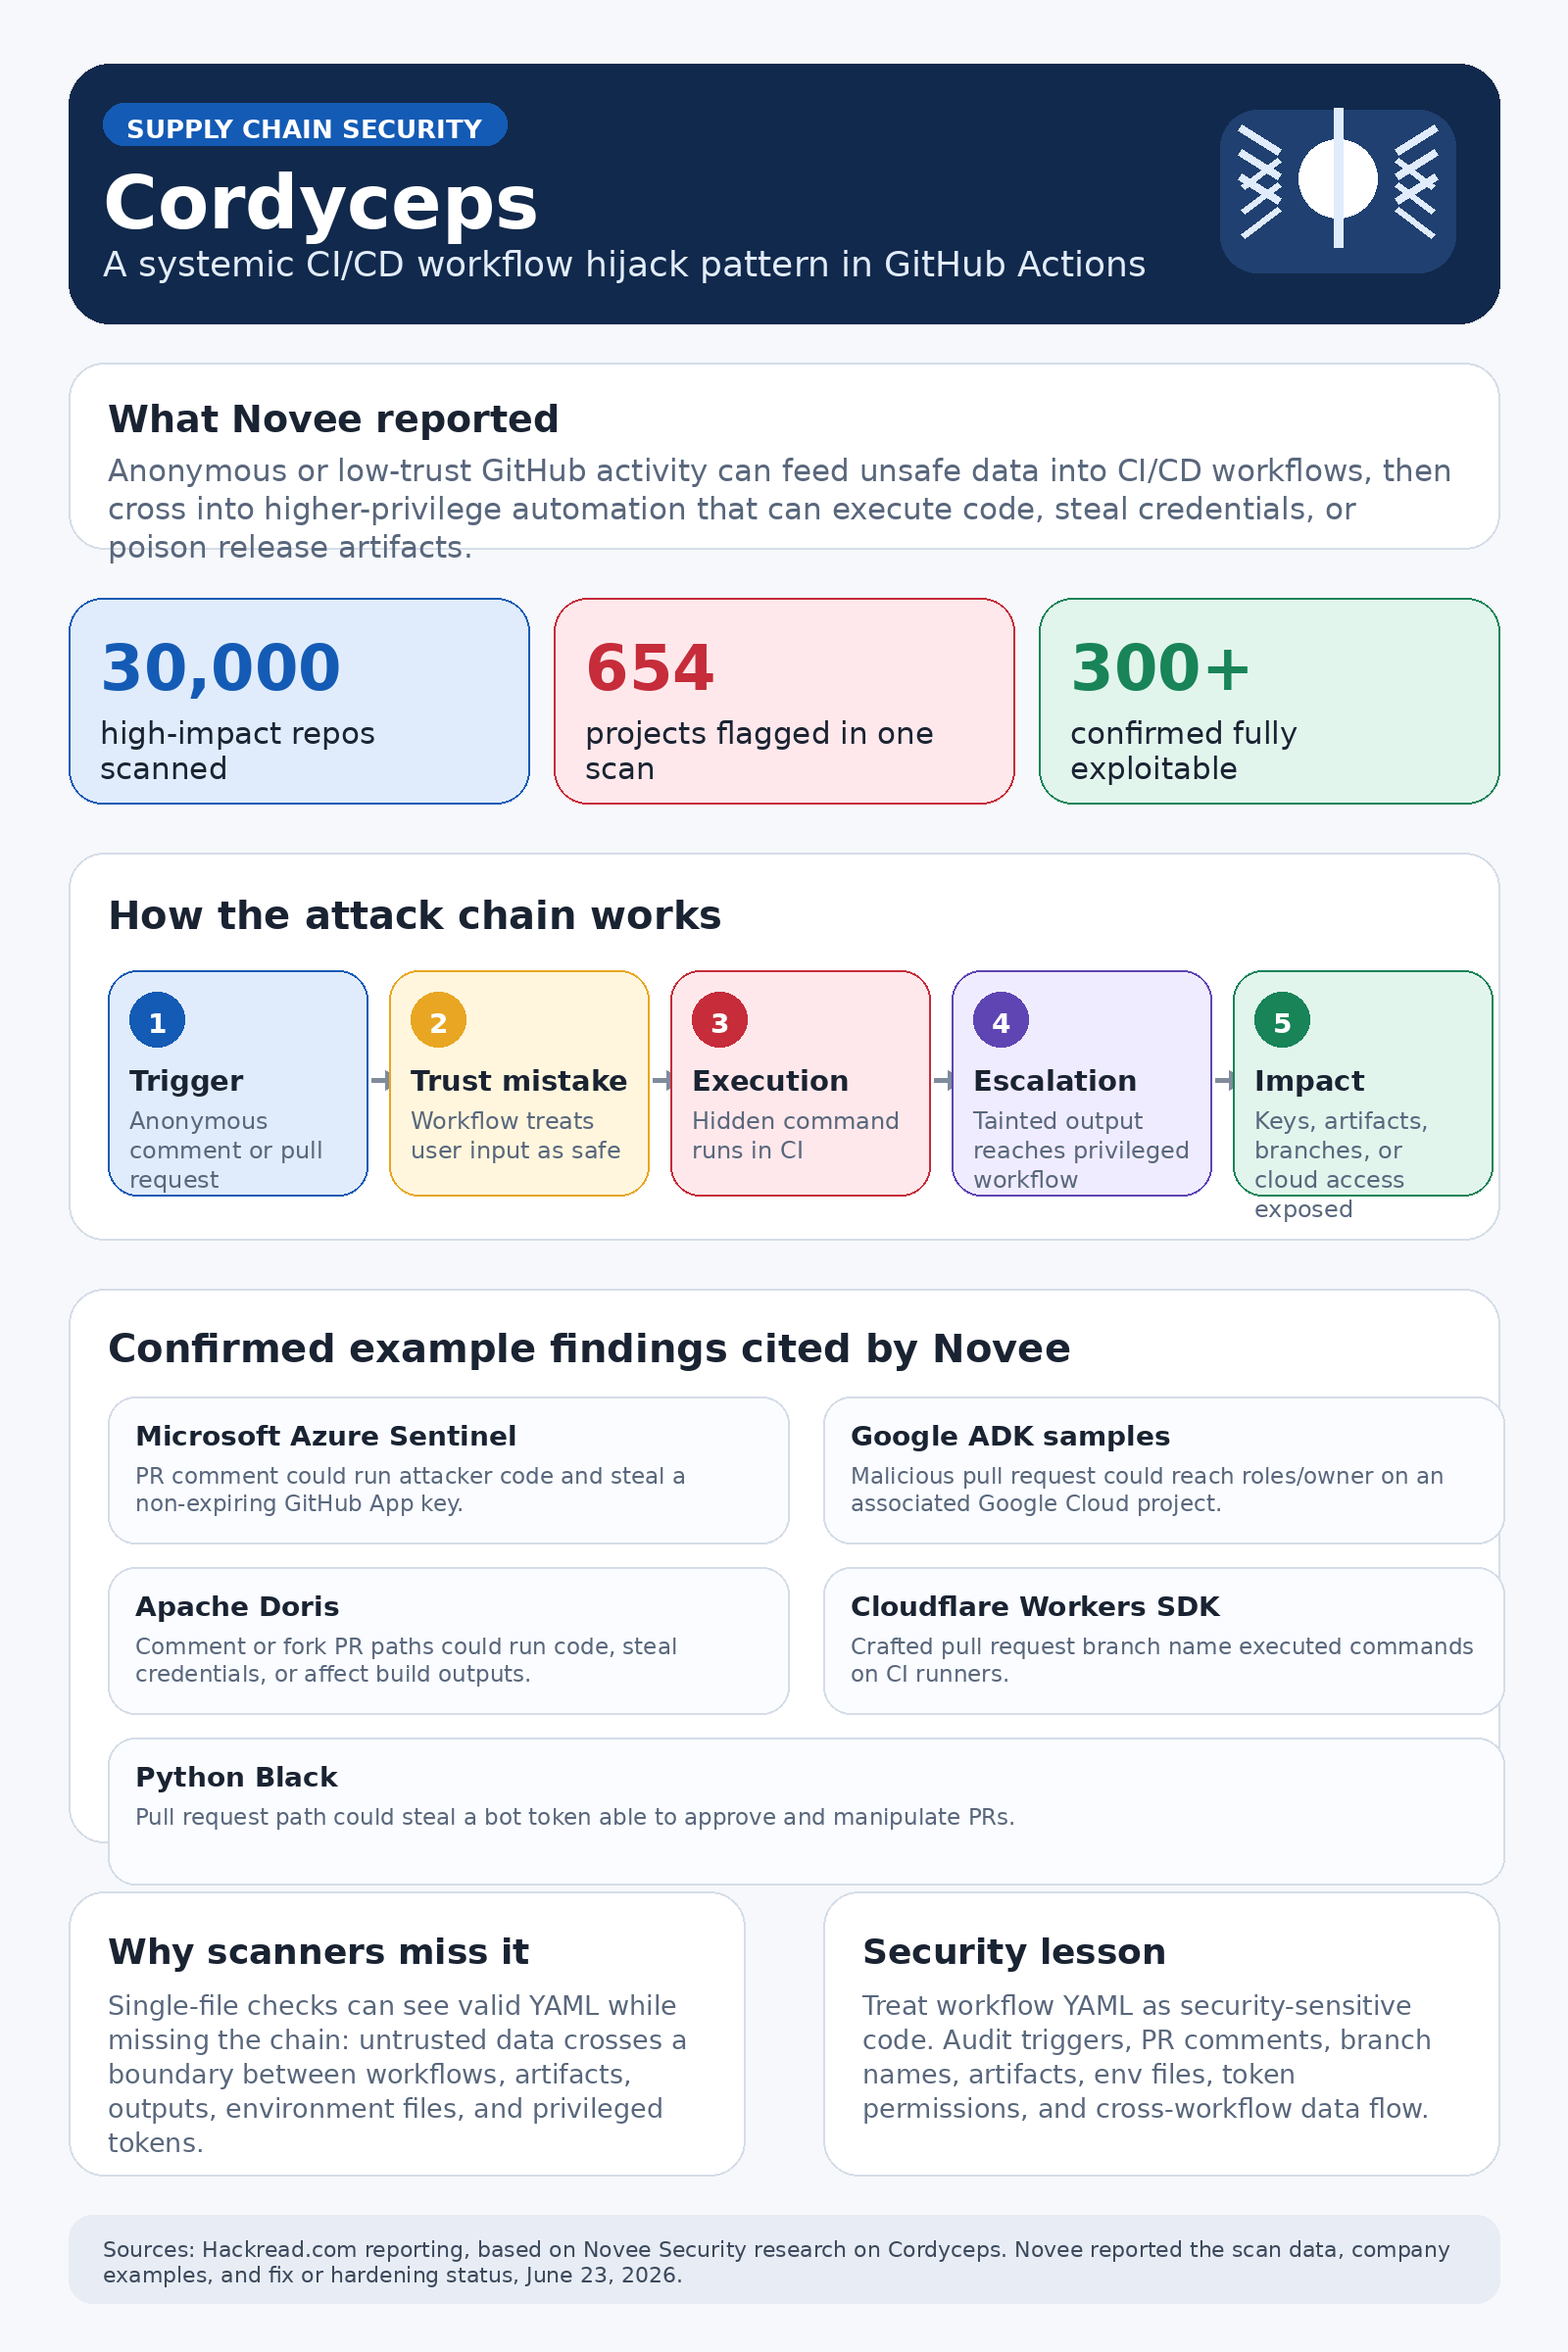
Novee scanned roughly 30,000 high-impact open-source repositories, flagged 654 projects in a single scan, and verified that over 300 were fully exploitable to test the risk. Novee’s security team also confirmed the flaws across major infrastructure systems, impacting companies such as Microsoft, Google, Apache, Cloudflare, and the Python Software Foundation.
In one confirmed finding inside Microsoft Azure Sentinel, researchers proved that an anonymous comment on a pull request could allow an attacker to execute code and steal a non-expiring GitHub App key. This would grant write access to security content deployed directly to customer workspaces via the Azure Marketplace.
Similarly, researchers targeted Google’s AI Agent Development Kit sample repository (adk-samples), where a single malicious pull request was shown to grant full ownership roles (roles/owner) over the associated Google Cloud project.
Further investigation, as per Novee’s blog post, published today, revealed that an attacker could also run unauthorized commands on Cloudflare’s Workers SDK toolchain (using the Wrangler CLI tool), steal saved login credentials from the Apache Doris database, and snatch automation tokens from Black- a popular Python code tool that handles 130 million downloads a month. All tested vulnerabilities have since been reported and fixed.
Researchers noted that such flaws are rapidly rising because while AI coding agents are generating configuration files at an exponential pace, these persistently reproduce the same insecure structural patterns, thus multiplying the vulnerability across millions of untested repositories.
Since anonymous users can exploit these flawed pipelines to manipulate major corporate platforms without authorization, researchers described the risk as “puppeteering the repositories of some of the world’s biggest companies, silently manipulating their workflows.”
Photo by Steve A Johnson on Unsplash
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。