



惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
酷 壳 – CoolShell
酷 壳 – CoolShell
博客园_首页
Engineering at Meta
Engineering at Meta
量子位
A
About on SuperTechFans
阮一峰的网络日志
阮一峰的网络日志
Recent Announcements
博客园 - 司徒正美
V
Visual Studio Blog
H
Hackread – Cybersecurity News, Data Breaches, AI and More
The GitHub Blog
The GitHub Blog
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
F
Fortinet All Blogs
Martin Fowler
Martin Fowler
腾讯CDC
Jina AI
Jina AI
C
Check Point Blog
H
Help Net Security
罗磊的独立博客
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
V
V2EX
爱范儿
爱范儿
I
InfoQ

Hackread – Cybersecurity News, Data Breaches, AI and More

Operation Endgame Disrupts StealC, Amadey and SocGholish Malware Networks Fake npm Packages Impersonate PostCSS Tool to Steal Chrome Passwords Best Crypto Payment Solutions for E-Commerce Businesses Internet Society Foundation Opens Global Call for Common Good Cyber Fund to Strengthen Cybersecurity LastPass Confirms Customer Data Breach After Klue OAuth Token Theft ‘Cordyceps’ CI/CD Flaw Exposes Microsoft, Google, Apache Repos to Pipeline Hijacking The Rise of AI-Powered Academic Fraud: Beyond Traditional Plagiarism New CryptoBandits Malware Uses USB Drives and Tor to Steal Crypto The Evolution of iGaming Fraud: What Security Teams Should Expect in 2027 2 Scattered Spider-Linked Hackers Plead Guilty Over £39M TfL Cyberattack Beats Studio Buds Flaw Could Let Nearby Attackers Eavesdrop on Users Texas Parks and Wildlife Data Breach Affects Over 3M License Customers Threat Hunting Beyond Alerts: Finding the Activity Detection Misses Scammers Use Fake GitHub Stars, VirusTotal Reviews to Spread Crypto Clipper Salesforce Disables Klue Integration After OAuth Token Theft Hits Customer Data MDR Provider Comparison: Time to Discover and Respond to Threats Meteor 3.0 Migration Helped Rocket.Chat Move Off End-of-Life Node.js Runtime Gcore Helps Ucom Safeguard Public Live Broadcast Infrastructure During Armenia’s Parliamentary Elections Nintendo America Employee Data Exposed After Shadowbyt3$ Targets TinyPulse eFAQ Publishes Investigation Into Alleged Scam Activity and Coordinated Reputation Attacks FIFA World Cup 2026: Hackers Target Football Fans With Fake Tickets Sites MacBook Neo vs Windows Laptops for Cybersecurity Tasks Operation Endgame Disrupts SocGholish Malware Infrastructure What Businesses Should Know Before Migrating Their CMS DragonForce Ransomware Abused Microsoft Teams to Hide Malware Activity Agentjacking: Researchers Show How One Fake Bug Report Can Hijack AI Coding Agents FortiBleed Attack Exposes Fortinet Firewall Credentials in 194 Countries SpyCloud Report Finds Phishing Attacks Surge as Employee Data Is Exposed at 86% of Fortune 100 Companies 152 Chrome Live Wallpaper Extensions Hid Ad Tracking and Fake Search Clicks Heimdal Survey: Executives Four Times More Confident About AI Risk Than the Teams Managing It
New GhostShell Hacking Group Targets Ukraine’s Drone Defe...
Deeba Ahmed · 2026-06-24 · via Hackread – Cybersecurity News, Data Breaches, AI and More

A new cyberattack campaign has been discovered targeting Ukraine’s drone sector, including military units, supply chains, and volunteer groups. Security researchers at Synaptic Systems recently analysed the activity and named the new group behind it GhostShell and the tracking label MB-0009. Reportedly, it has been active since at least February 2026.


How the Attack Works

GhostShell uses a trick called a decoy document to trap its targets. They sent a malicious compressed folder named Besomar_documentation.rar. When opened, this archive secretly copies a hidden script into the Windows Startup folder. This step allows the malware to run every time the computer turns on.

At the same time, the victim sees harmless-looking PDF documents. These docs are written in Ukrainian and pretend to be from Besomar, a real Ukrainian company that makes defense drones. These fake documents include titles about drone configurations and charging stations to make the trap look believable.
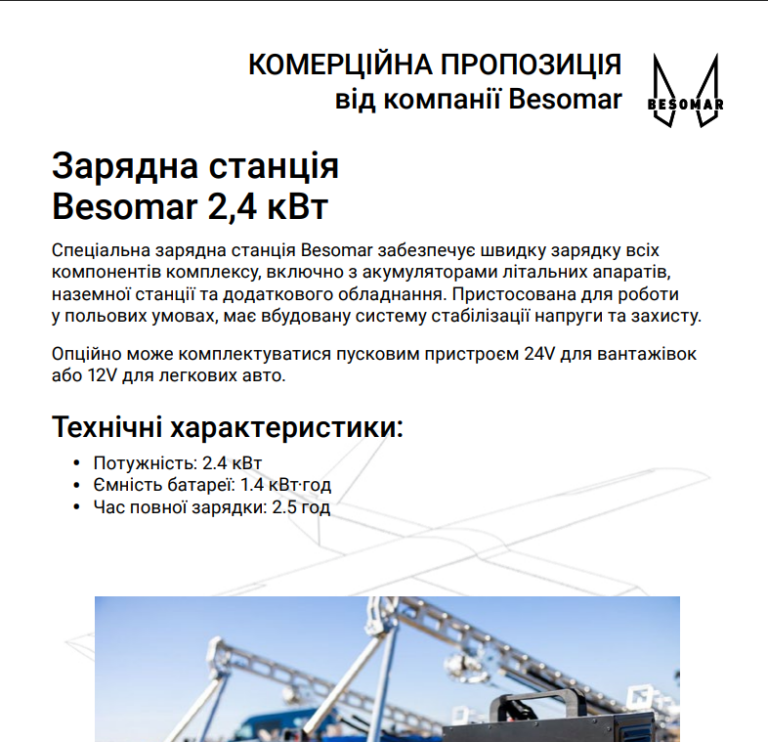
Decoy PDF sample (Source: Synaptic Systems)


Stealing Information in the Background

Once the trap is sprung, the hidden script contacts a website called cloudaxiscc to download more malicious programs. Synaptic Systems found three specific harmful files linked to this setup: 122.exe, 22.exe, and update.exe.

These files are listed with their unique digital fingerprints as shown in the image below.
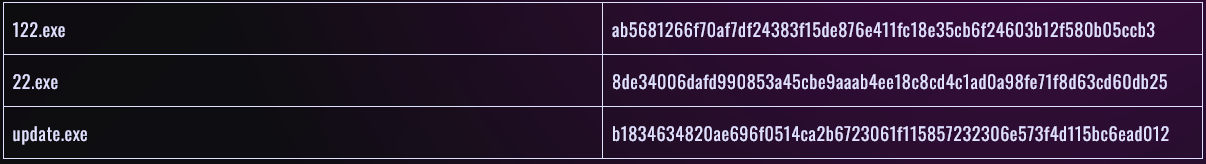
Credit: Synaptic Systems

The main file, 122.exe, acts as a spy program. It takes screenshots of the victim’s desktop, gathers computer names, and sends this data back to a server named cdnexpress.cc. Another file, update.exe, hides by pretending to be an official Windows security service. It even uses a Telegram page link to find its command server.

Alongside this, there’s a third file titled 22.exe. This is the file that drops a well-known data-stealing program called Vidar v2. The malware now starts collecting saved internet passwords, history, and cryptocurrency wallet information from the infected machine.

Researchers noted in their technical report that this campaign, although it aims to disrupt Ukrainian defense networks, would exercise caution before blaming a specific country. Using their specialised evaluation method, called the SOLBIT model, Synaptic Systems explained that surface details like language are easy for hackers to fake.

For now, GhostShell is being tracked as an independent, highly organised group of cybercriminals, and researchers are continuing to monitor their activities for any new threats.

Photo by Yulii Shtel on Unsplash